
Skip to content
KitploitKITPLOIT
ToolsExploitsBlog
Log in
Submit
ToolsExploitsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

FeedsContactPrivacy© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories

Tools

AllAndroid SecurityAuthentication & AuthorizationCloud Infrastructure SecurityDefensive ToolsDisk ForensicsEmbedded Systems SecurityGeneral Purpose UtilitiesIndicator of Compromise (IOC) ManagementOSINT (Open Source Intelligence)Packet Sniffing & AnalysisPassword CrackingPenetration Testing FrameworksPhishing ToolsPrivilege EscalationReconnaissanceStatic AnalysisVulnerability ScannersWeb Vulnerability ScannersWi-Fi AuditingBluetooth SecurityContainer SecurityDynamic Analysis (Sandboxing)Encryption/Decryption ToolsExploit FrameworksIdentity ManagementiOS SecurityIoT SecurityMemory ForensicsNetwork MappingOSINT for Social EngineeringPassword AttacksPayload GenerationPersistence MechanismsPort ScanningStatic Code Analysis (SAST)Threat Feeds & AggregatorsVulnerability AnalysisWeb Proxies & InterceptionCode AnalysisDNS & Subdomain EnumerationDynamic Code Analysis (DAST)ExploitationHash AnalysisIDS/IPS EvasionImpersonation ToolsLateral MovementMobile App PentestingNetwork ForensicsReverse EngineeringRFID/NFC ToolsSCADA/ICS SecurityScripting & AutomationServerless SecurityShellcodeWeb Application ExploitationAPI Security TestingConfiguration AuditingData ExfiltrationDebuggersForensicsInformation GatheringMobile ForensicsNetwork Access ControlPost-ExploitationSecurity VirtualizationPhishingWAF BypassWeb SecurityFuzzingNetwork SecuritySteganographyWireless SecurityData RecoveryMalware AnalysisDigital ForensicsHardware HackingCryptographyCTFPenetration TestingCloud SecurityDevSecOpsMobile SecurityPrivacyCommand and ControlSocial EngineeringHardware SecurityUtilities & FrameworksHardware & IoT SecuritySecret DetectionBinary AnalysisThreat IntelligenceIdentity & Access Management (IAM)Supply Chain SecurityAuthenticationMachine LearningIntrusion DetectionPapers & ResearchMisconfigurationSubdomain EnumerationEmail HarvestingLearning & EducationAI-Assisted ReversingDNS FuzzingRed TeamingIncident ResponseCrawlerCurated ResourcesRemote Access ToolShellcode GenerationPayload DevelopmentRemote Access TrojanAPI SecurityAnti-BotFingerprint SpoofingCAPTCHA BypassEmail SecurityDNS AnalysisChaos EngineeringLearning Paths & CoursesContainer EscapeAI SecurityDatabase SecurityFirmware AnalysisAnomaly DetectionLog AnalysisAdversarial AttackBinary ExploitationLabs & Practice
NewestRelevanceMost popularRecently updated
39 results
excelpeek preview

excelpeek

GitHubslaughterjames/excelpeek

Static analysis tool for investigating potentially malicious Microsoft Excel files, extracting metadata, macros, and embedded objects to aid digital…
digital-forensicsforensicsmalware-analysis+1
38
4 years ago
ForensiX-Studio preview

ForensiX-Studio

GitHubaquibpro/forensix-studio

Forensic intelligence platform that analyzes files, correlates threat indicators, maps behavior to MITRE ATT&CK, and generates actionable security…
anomaly-detectiondigital-forensicsforensics+4
16 months ago
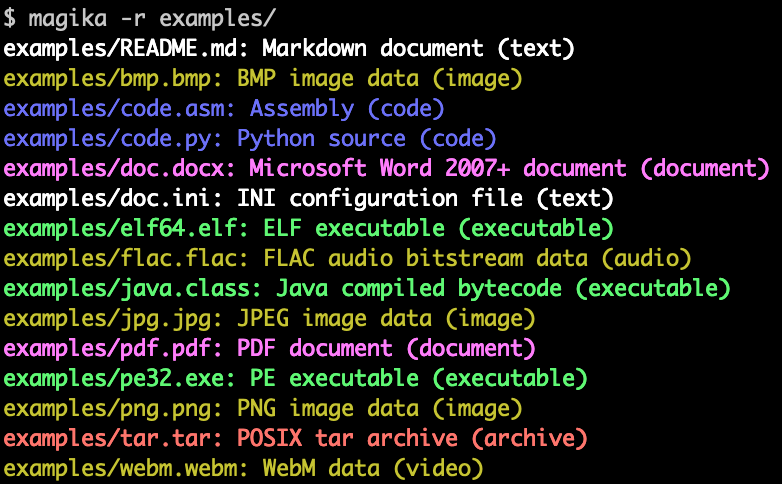
magika preview

magika

GitHubgoogle/magika

Fast and accurate AI powered file content types detection
code-analysisforensicsgeneral-purpose-utilities+3
18.7k5h 42m ago
yara preview

yara

GitHubvirustotal/yara

The pattern matching swiss knife

forensicsmalware-analysisstatic-analysis+2
10.0k1 day ago
pe-bear preview

pe-bear

GitHubhasherezade/pe-bear

Portable Executable reversing tool with a friendly GUI

binary-analysisforensicsmalware-analysis+3
3.9k13 days ago
pefile preview

pefile

GitHuberocarrera/pefile

pefile is a Python module to read and work with PE (Portable Executable) files
binary-analysisforensicsmalware-analysis+3
2.1k12h 24m ago
oletools preview

oletools

GitHubdecalage2/oletools

Python toolkit for analyzing MS OLE2 and Office documents, extracting VBA macros, detecting exploits, and performing forensic analysis of structured…
code-analysisdigital-forensicsforensics+3
3.4k9 months ago
PortEx preview

PortEx

GitHubstruppigel/portex

Java library to analyse Portable Executable files with a special focus on malware analysis and PE malformation robustness

anomaly-detectionbinary-analysisforensics+3
5437 days ago
IPA preview

IPA

GitHubseekbytes/ipa

GUI analyzer for deep-diving into PDF files. Detect malicious payloads, understand object relationships, and extract key information for threat…
binary-analysisdefensive-toolsdigital-forensics+6
8842 years ago
peframe preview

peframe

GitHubguelfoweb/peframe

PEframe is a open source tool to perform static analysis on Portable Executable malware and malicious MS Office documents.
forensicsmalware-analysisreverse-engineering+2
6285 years ago
SSMA preview

SSMA

GitHubsecrary/ssma

SSMA - Simple Static Malware Analyzer [This project is not maintained anymore by me]
forensicsmalware-analysisstatic-analysis+1
4146 years ago
PEpper preview

PEpper

GitHub0x0be/pepper

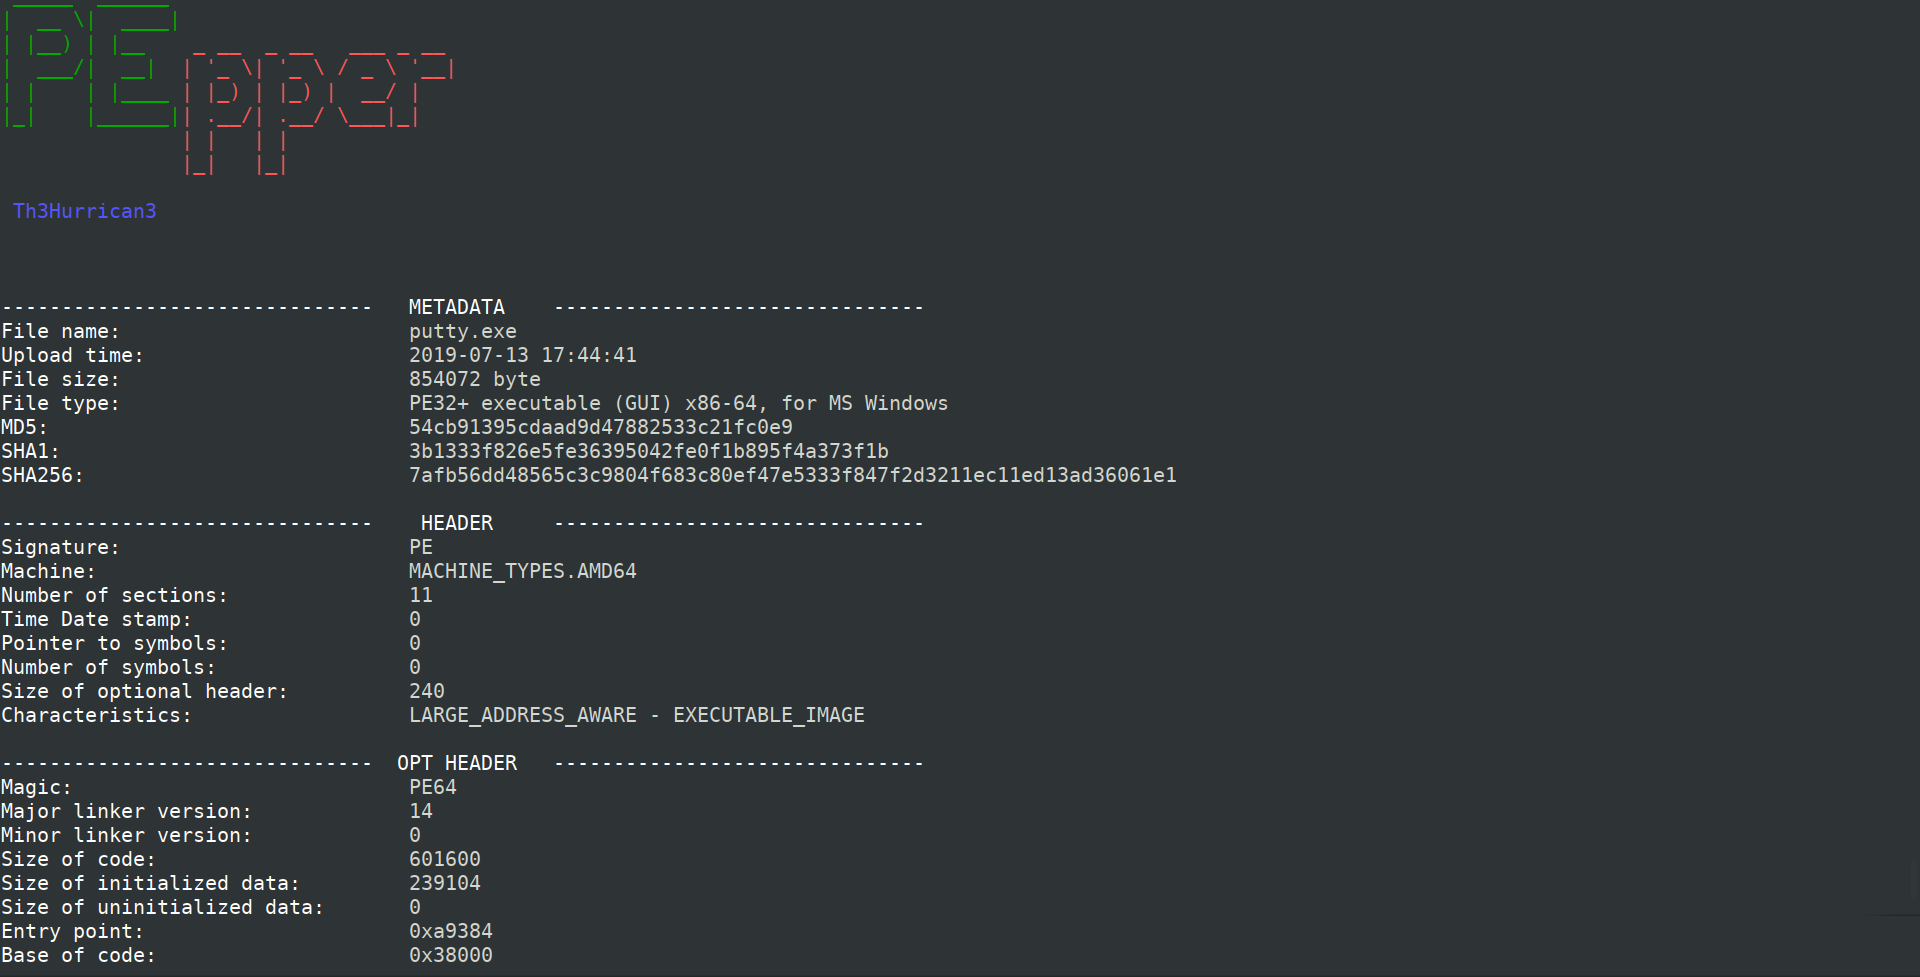
An open source script to perform malware static analysis on Portable Executable
binary-analysisforensicsmalware-analysis+1
3334 years ago
PortexAnalyzerGUI preview

PortexAnalyzerGUI

GitHubstruppigel/portexanalyzergui

Graphical interface for PortEx, a Portable Executable and Malware Analysis Library
binary-analysisforensicshash-analysis+3
1937 days ago
inhale preview

inhale

GitHubnetspooky/inhale

A malware analysis and classification tool.
binary-analysisforensicshash-analysis+3
1905 years ago
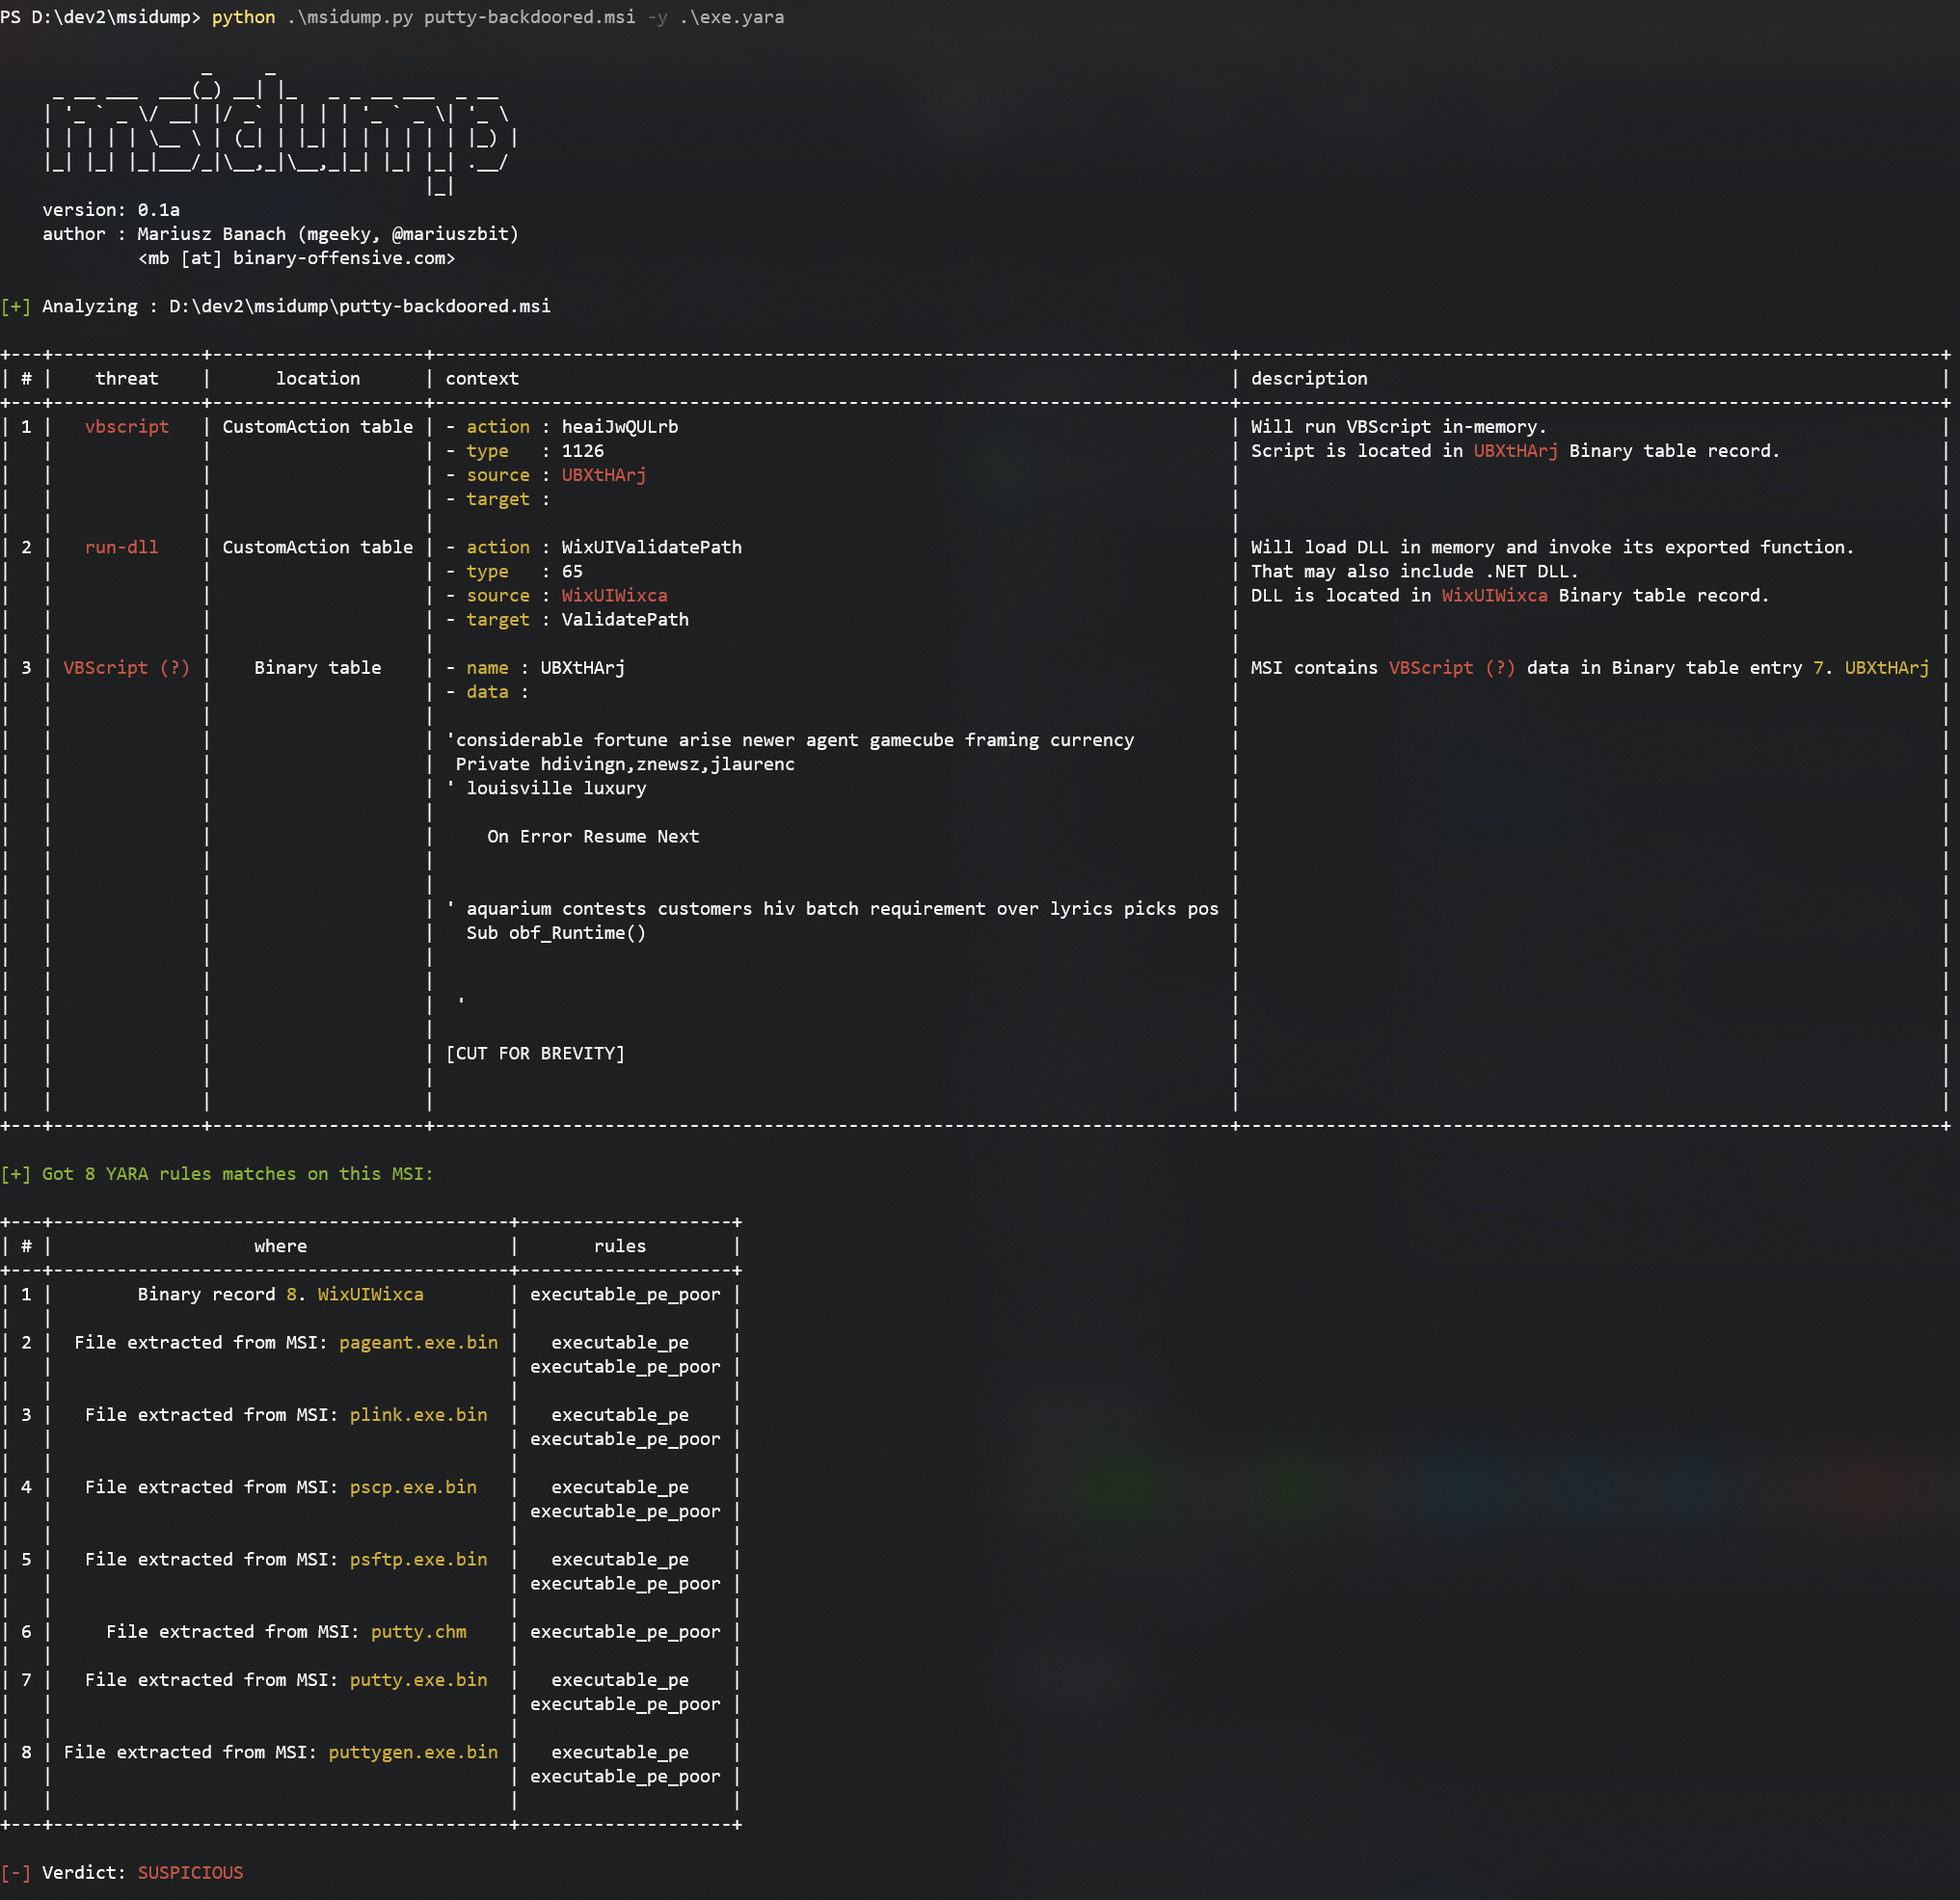
msidump preview

msidump

GitHubmgeeky/msidump

MSI Dump - a tool that analyzes malicious MSI installation packages, extracts files, streams, binary data and incorporates YARA scanner.
binary-analysisforensicsmalware-analysis+1
2343 years ago
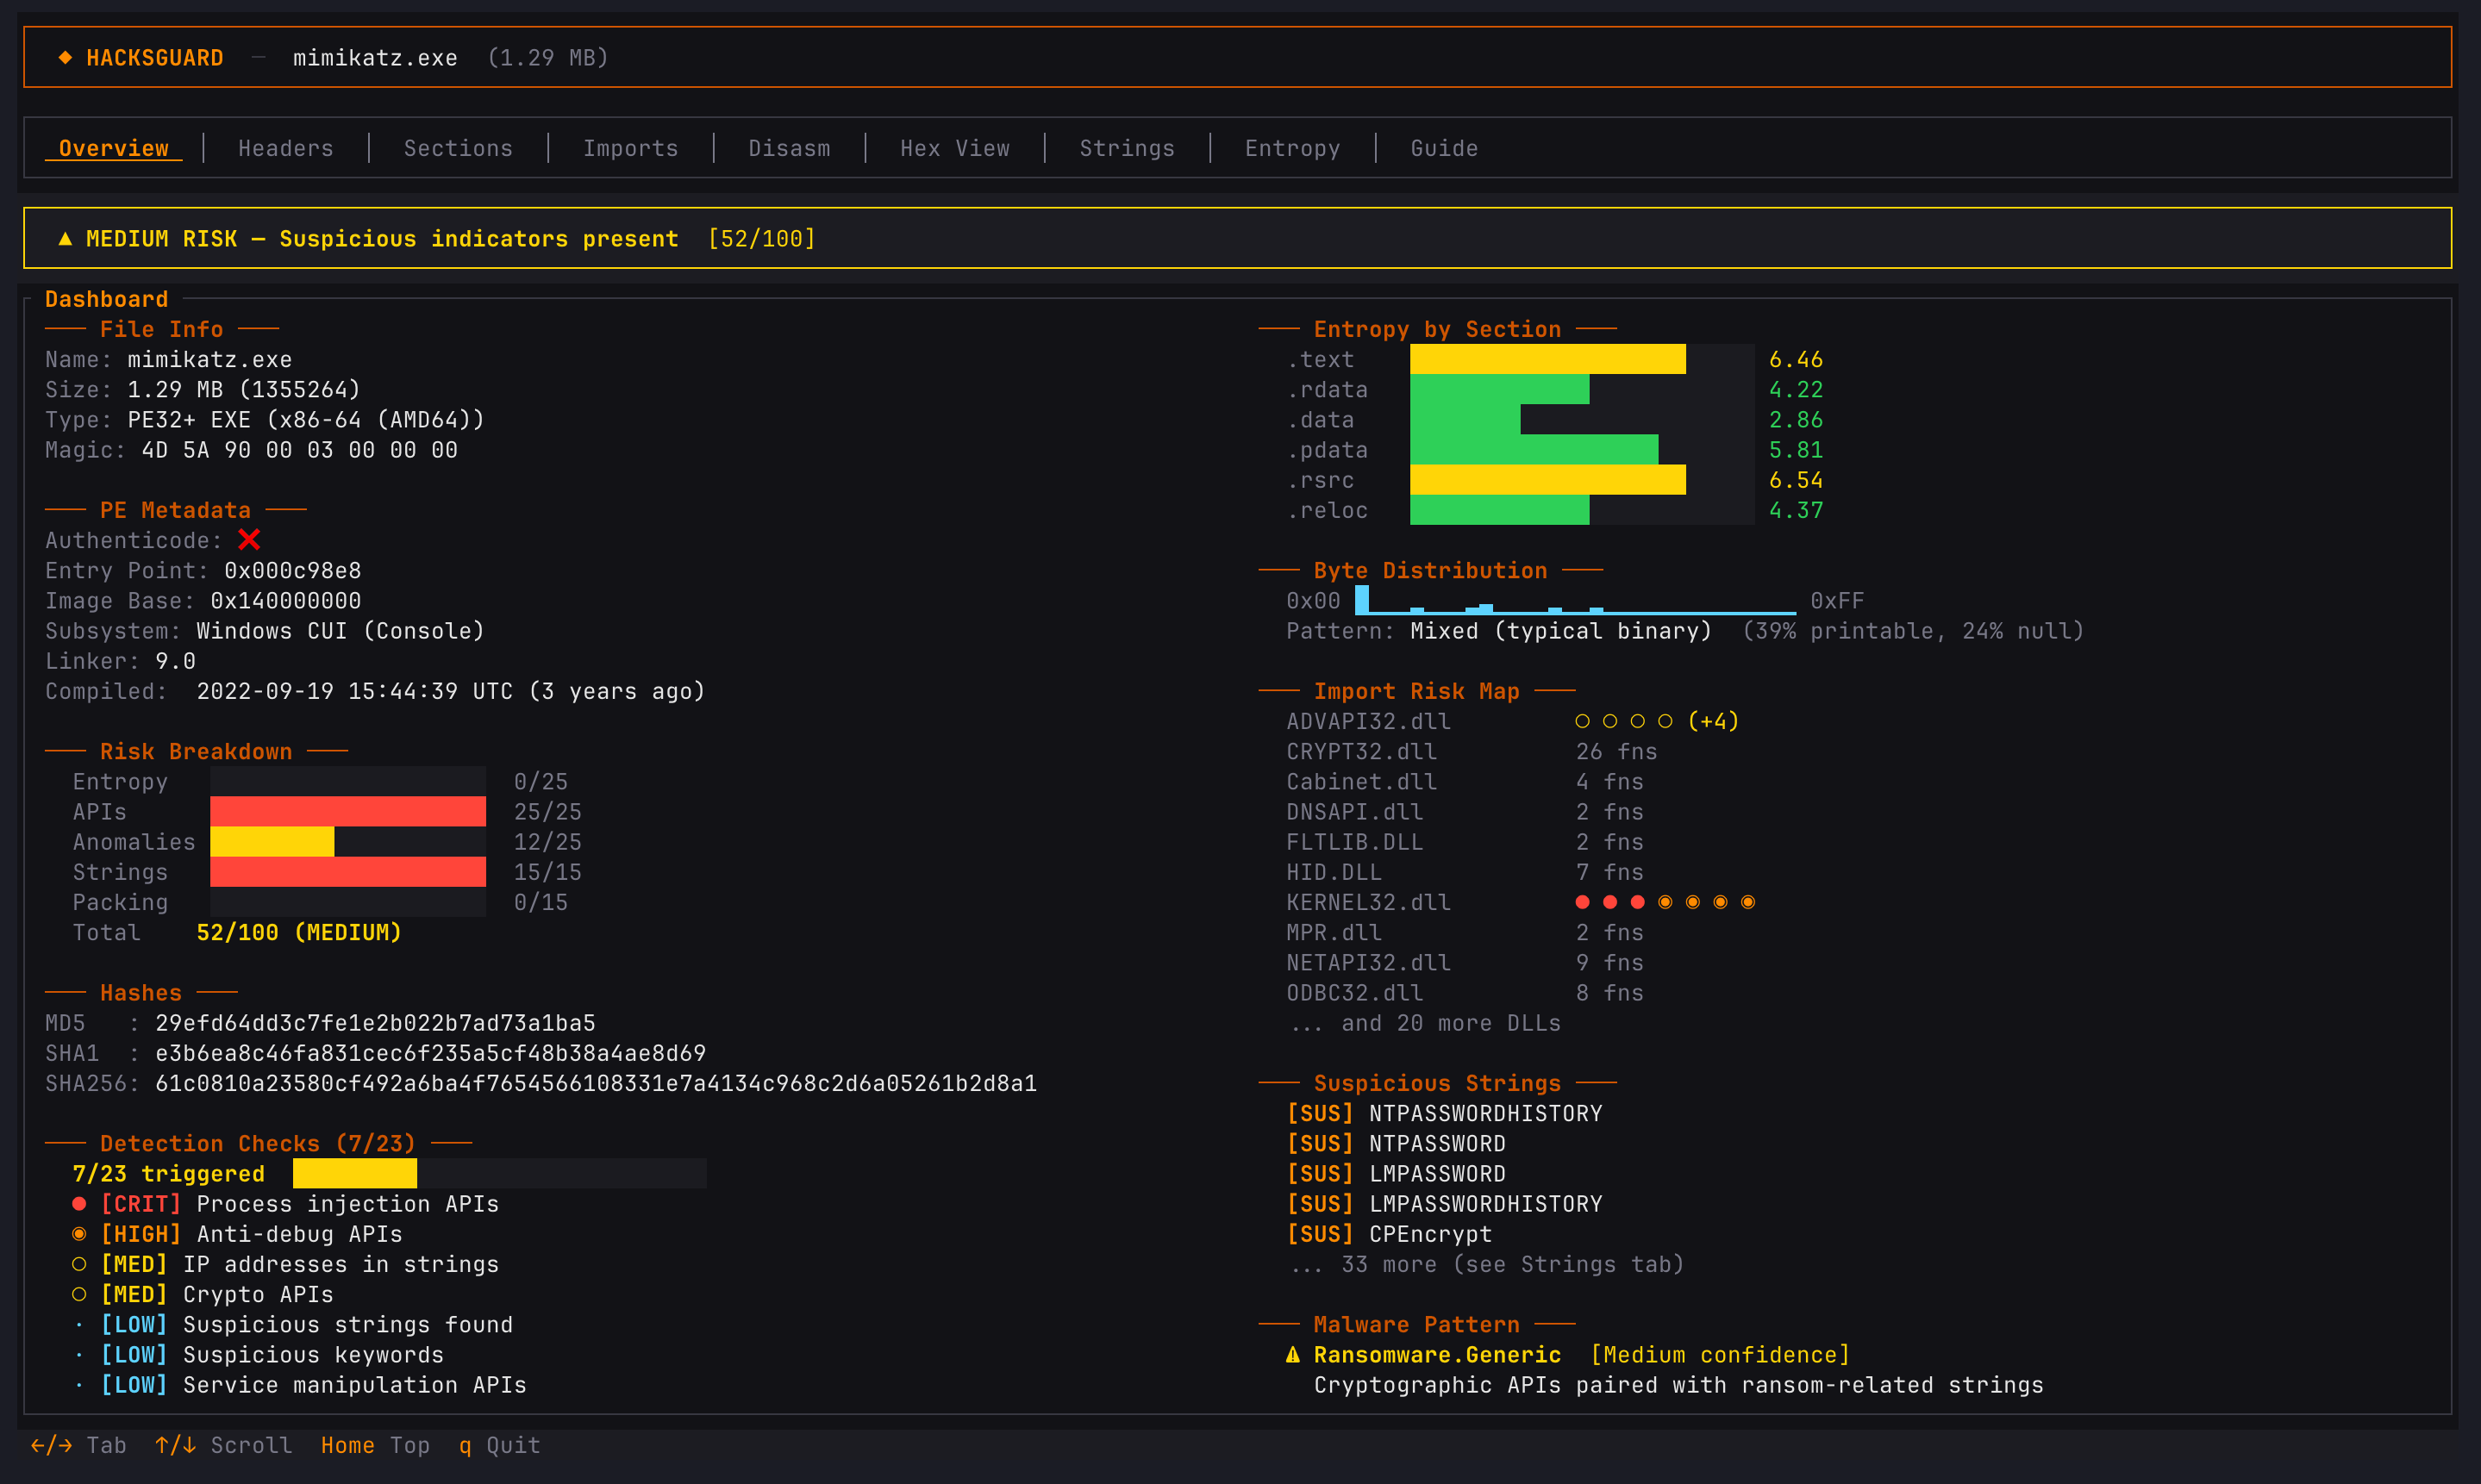
hacksguard preview

hacksguard

GitHubrhacknarok/hacksguard

A blazingly fast, multi-threaded TUI malware analysis tool built in Rust. Features deep PE parsing, YARA scanning, and heuristic risk scoring.
binary-analysisforensicsmalware-analysis+2
2161 month ago
nuitka-static-unpacker preview

nuitka-static-unpacker

GitHubdimareverse/nuitka-static-unpacker

Static-first research tool for unpacking Nuitka-compiled binaries: extracts constants, modules, recovers .pyc files, and generates analysis reports.
binary-analysisdata-recoveryforensics+3
1372 months ago
webshell-analyzer preview

webshell-analyzer

GitHubtstillz/webshell-analyzer

Web shell scanner and analyzer.

forensicsmalware-analysisstatic-analysis+2
1143 years ago
Previous123Next