msf_shellcode_analysis

Static analysis walkthrough of a Metasploit Windows shellcode: PowerShell payload decoding, XOR obfuscation, PEB walking, and Export Address Table…

Static analysis walkthrough of a Metasploit Windows shellcode: PowerShell payload decoding, XOR obfuscation, PEB walking, and Export Address Table…

Ghidra is a software reverse engineering (SRE) framework

A powerful and user-friendly binary analysis platform!

Tool to look for several security related Android application vulnerabilities

A byte code analyzer for finding deserialization gadget chains in Java applications

BARF : A multiplatform open source Binary Analysis and Reverse engineering Framework

A reverse engineering framework written in Python.

Autonomous white-hat security auditor for AI-driven code review, bug bounty research, exploit construction, and execution-grounded verification.

A tool that is used to hunt vulnerabilities in x64 WDM drivers

MCP server for reverse engineering Windows executables and binary formats. Combines static triage, Ghidra-assisted function recovery, plugin-driven…

MCP server packaging a three-tier penetration-testing methodology: attack-surface reconnaissance, source-to-sink static analysis, and live finding…

Scanning tool for identifying local privilege escalation issues in vulnerable MSI installers

Model Context Protocol server for autonomous vulnerability discovery

Vimana is a modular security framework for auditing Python APIs and Web applications. The plugin-based architecture enables security professionals to…

Android deeplink misconfiguration detector and exploitation tool

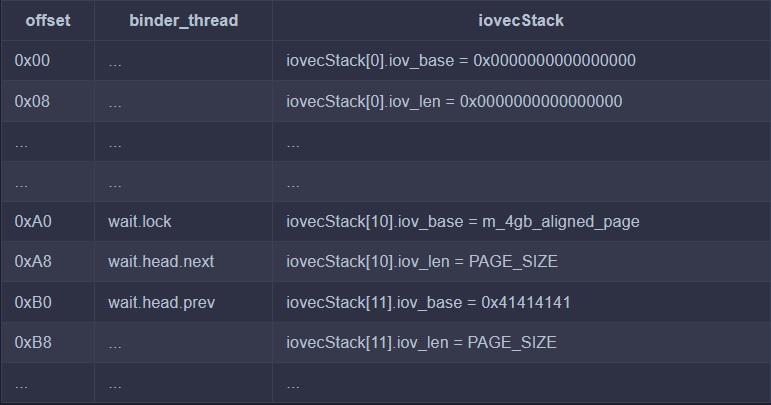
Triggering and Analyzing Android Kernel Vulnerability CVE-2019-2215

Adaptix C2 service plugin that drives LitterBox payload analysis from the operator UI.

AI Smart Contract Security Analysis and PoC Generation Framework