
oletools
 decalage2/oletools
Python toolkit for analyzing MS OLE2 and Office documents, extracting VBA macros, detecting exploits, and performing forensic analysis of structured…
code-analysisdigital-forensicsforensics+3
3.4k
decalage2/oletoolsPython toolkit for analyzing MS OLE2 and Office documents, extracting VBA macros, detecting exploits, and performing forensic analysis of structured…
 seekbytes/ipa
GUI analyzer for deep-diving into PDF files. Detect malicious payloads, understand object relationships, and extract key information for threat…
 warpedatom/offsetinspect
PowerShell toolkit for AMSI/Defender detection-boundary analysis and static malware triage maps byte offsets to detection triggers, plus YARA,…
 sh1n0g1/z9
Detects PowerShell-based malware artifacts from event logs and performs static analysis on PowerShell scripts to identify malicious activity.
 bytespulse-oe/wp2shell-hestia-scanner
Read-only WordPress security scanner for HestiaCP servers. Detects wp2shell compromise indicators (CVE-2026-63030 / CVE-2026-60137) across all hosted…
 aquibpro/forensix-studio
Forensic intelligence platform that analyzes files, correlates threat indicators, maps behavior to MITRE ATT&CK, and generates actionable security…
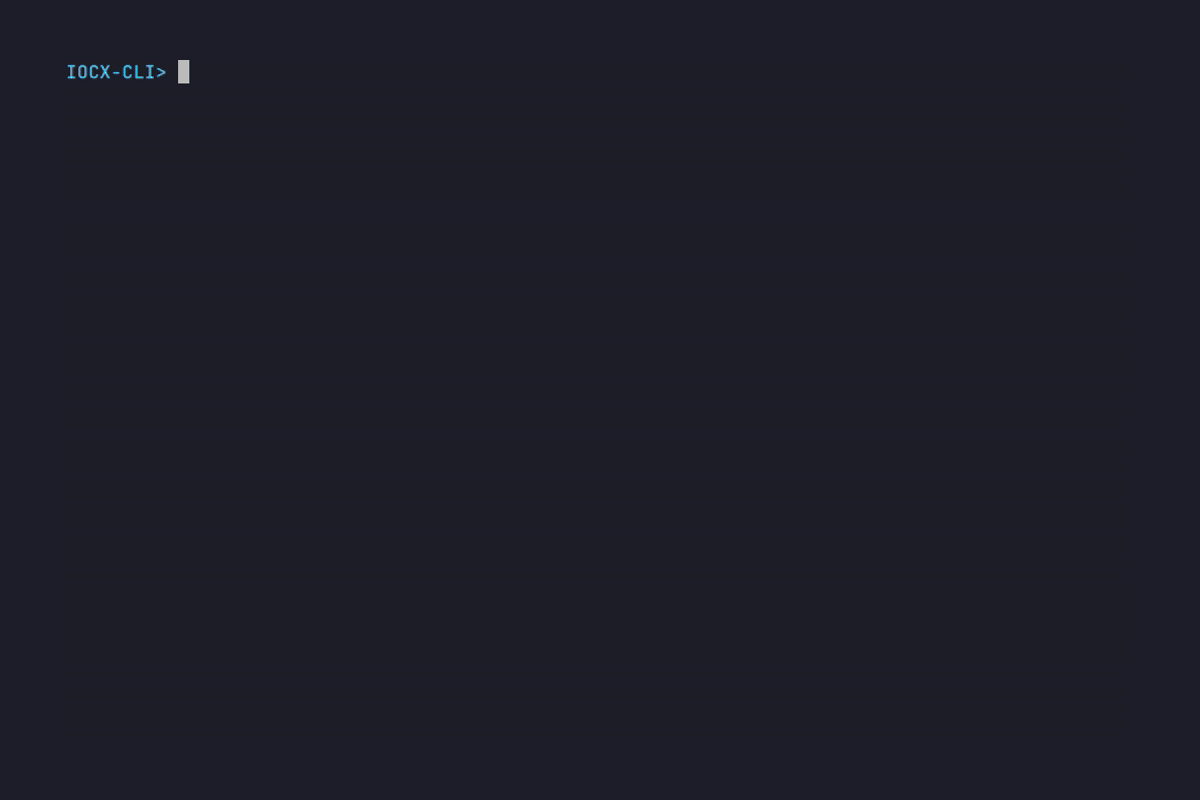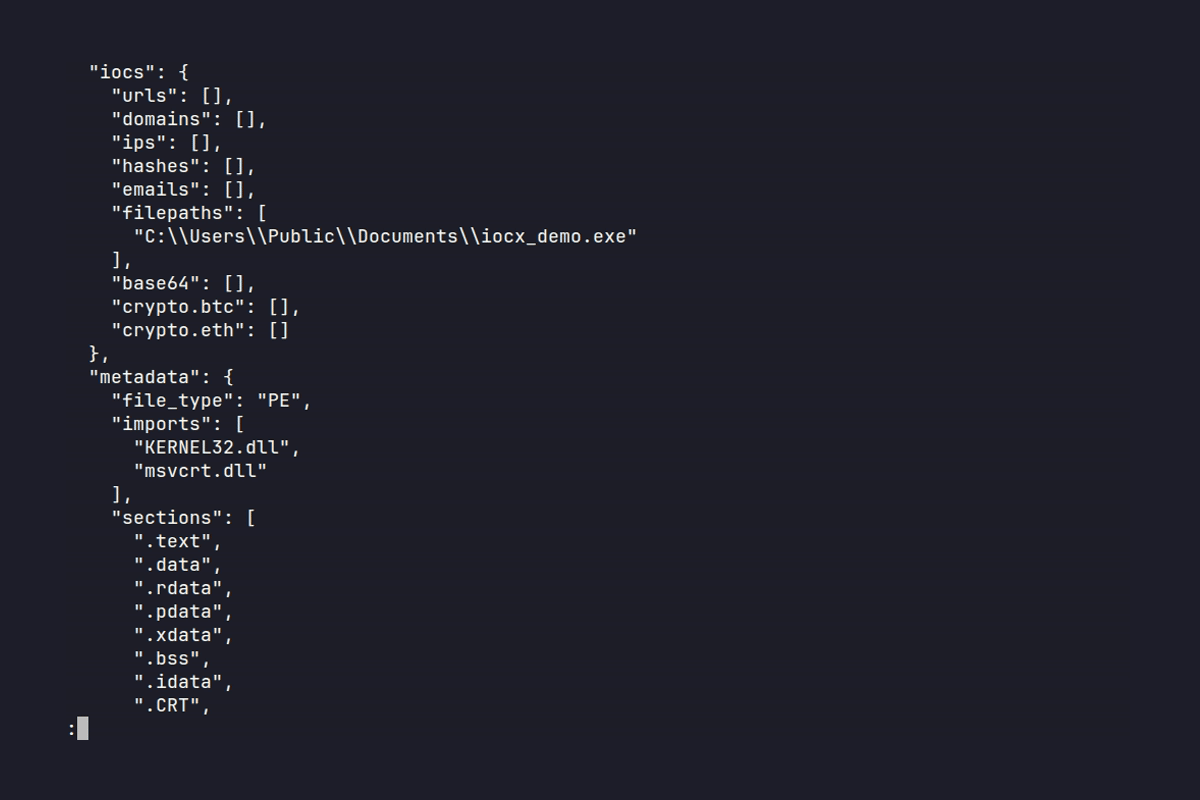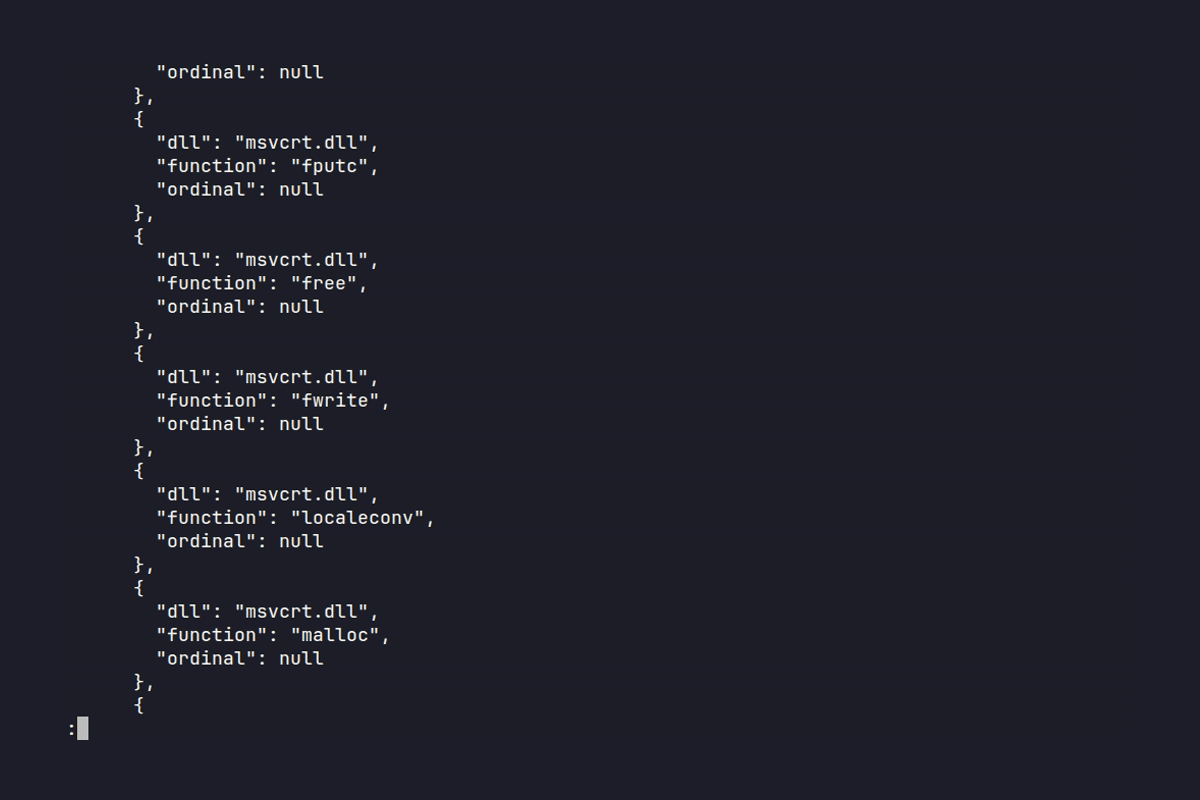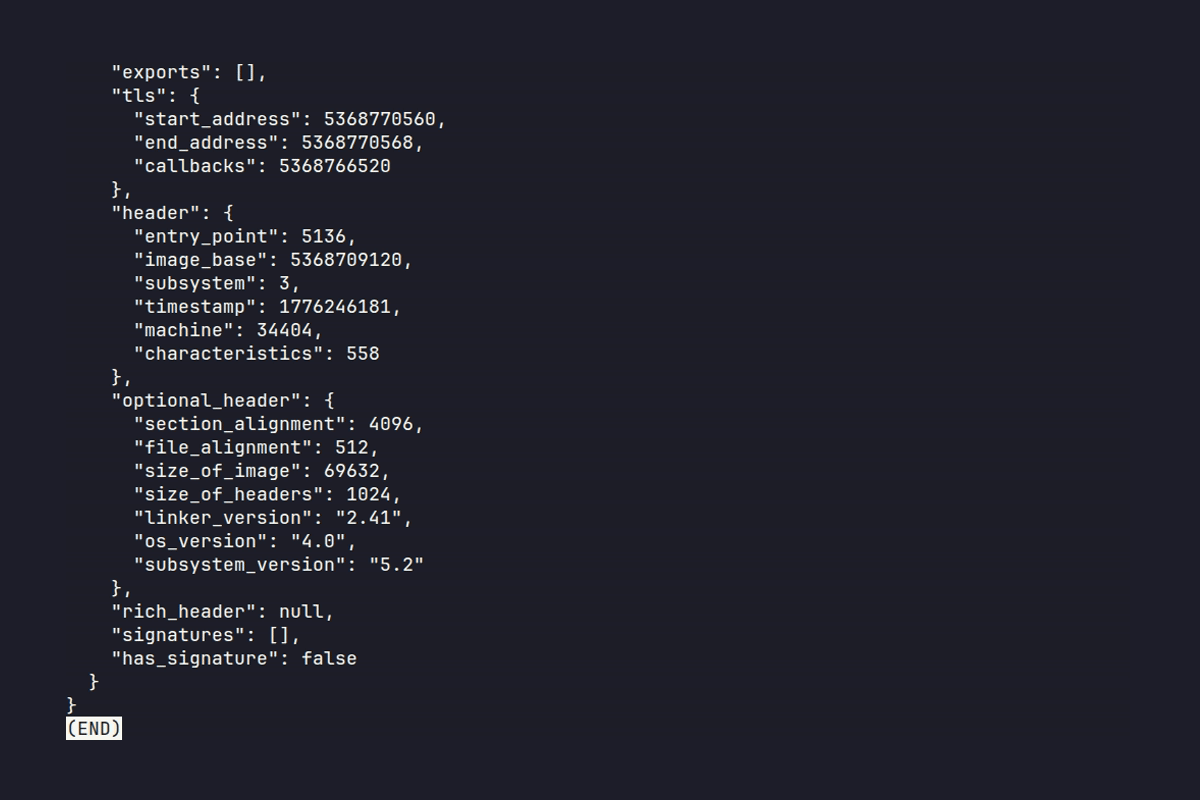 iocx-dev/iocx
An extensible, deterministic static‑analysis engine that extracts high‑signal IOCs from PE binaries and text, built for SOC automation and modern…
 forentfraps/pe-signgen
Universal signature generation for any system function from all Windows Builds using Winbindex
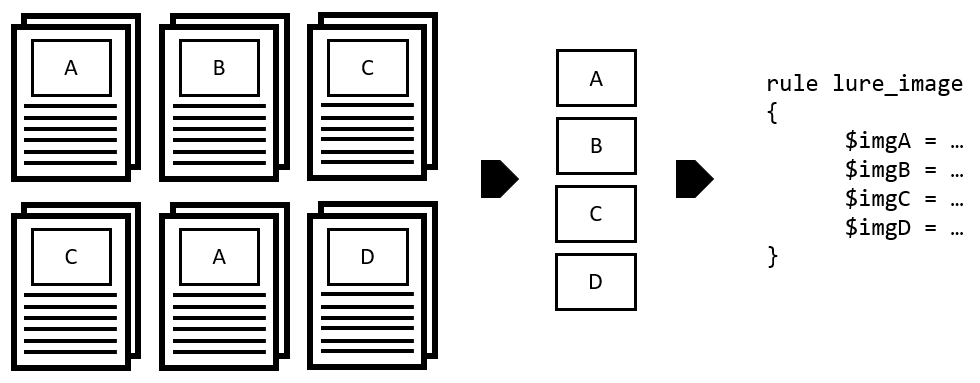 target/halogen
Automatically create YARA rules from malicious documents.
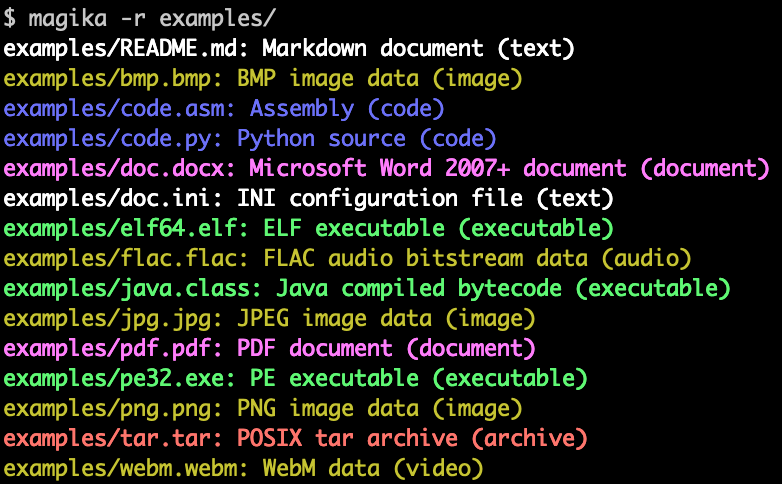 google/magika
Fast and accurate AI powered file content types detection
 ilhamrzr/rar-anomaly-inspector
Defensive PowerShell tool for static inspection of RAR archives and detection of CVE-2025-8088 path traversal anomalies.
 dwexi/entropystrip
Algorithmic PE de-obfuscator, Shannon entropy radar, and incident triage engine
 sumidcyber/zeroscout
🦅 ZeroScout: The Autonomous Local & Cloud Threat Hunter. Visualize attacks in a live War Room, identify APT groups via Genetic Analysis, and…
 chpratik/cve-2026-9830
Threat intelligence report repository for CVE-2026-9830, an authentication bypass vulnerability in BookingPress Pro WordPress plugin, with detailed…
 codeshield-security/log4jshell-bytecode-detector
Local Bytecode Scanner for the Log4JShell Vulnerability (CVE-2021-44228)
 threatlabz/iocs
This repository is for Indicators of Compromise (IOCs) from Zscaler ThreatLabz public reports
 dbzoo/log4j_scanner
Filesystem scanner for Log4Shell (CVE-2021-44228) and related CVEs. Detects vulnerable JAR files via hash matching and class presence. Runs…
 corelight/quipu
A desktop workbench for writing, validating, compiling, and testing YARA rules.