
http-desync-guardian
 aws/http-desync-guardian
Analyze HTTP requests to minimize risks of HTTP Desync attacks (precursor for HTTP request smuggling/splitting).
api-security-testingstatic-analysisvulnerability-analysis+1
273
aws/http-desync-guardianAnalyze HTTP requests to minimize risks of HTTP Desync attacks (precursor for HTTP request smuggling/splitting).
 sirredbeard/cve-2025-60876
Behavior-preserving fix for CVE-2025-60876 HTTP header injection in BusyBox wget, with proof-of-concept, percent-encoding patch, and upstream…
 lfi-project/lfi
Top-level repository for LFI: Practical, Efficient, and Secure Software-based Sandboxing
 cellebrite-labs/ida_kcpp
An IDAPython module for enhancing c++ support on top of ida_kernelcache
 owasp/appsec-agent
A TypeScript package that provides AI-powered agents for Application Security (AppSec) tasks, built on top of the frontier models.
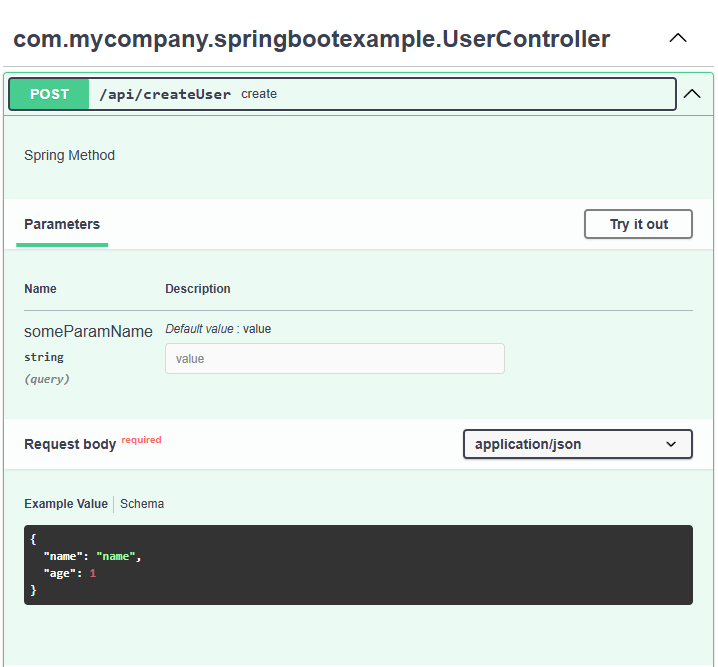 blackfan/bfscan
Tool for finding URLs, paths, secrets and generating raw HTTP requests and OpenApi specifications from config files and annotations used in JAR / WAR…
 mcp-shark/mcp-shark
Wireshark-like forensic analysis for Model Context Protocol communications Capture, inspect, and investigate all HTTP requests and responses between…
 aniketkarne/aco-prompt-shield
Stop prompt injection attacks before they reach your LLM — zero API costs, runs entirely locally, integrates in 2 minutes. Prompt injection is the…
 simoneavogadro/android-reverse-engineering-skill
Decompiles Android APK/XAPK/JAR/AAR files and extracts HTTP APIs, authentication patterns, and call flows using jadx, with R8-resistant Kotlin name…
 hashgraph-online/hol-guard
Open-source antivirus for AI agents: block risky tools, secret access, prompt injection, malicious packages, MCP servers, plugins, and skills at…
 byezero/nginx-cve-2026-42945-check
Local read-only scanner for CVE-2026-42945 (NGINX Rift) that checks NGINX, OpenResty, and Tengine instances for vulnerable rewrite configurations…
 shoucheng3/cov-int
XWiki Commons CVE-2023-31126 v14.10.3 for Coverity analysis
 shoucheng3/xwiki__xwiki-commons_cve-2023-31126_14-10-3
Java library providing technical commons for XWiki projects, with a focus on vulnerability analysis and static code inspection for security testing.
 shoucheng3/xwiki__xwiki-commons_cve-2023-36471_14-10-5
Technical Java libraries providing common utilities and components for the XWiki platform, including security vulnerability fixes and code analysis…
 shoucheng3/xwiki__xwiki-commons_cve-2023-29201_14-5
Technical libraries for XWiki projects, providing reusable components for vulnerability analysis, code analysis, and static analysis across…
 traceforce/mcp-xray
Unified security scanner for MCP servers with config, pentest, and repo-scan modes. Generates SARIF reports for CI/CD integration, detects secrets,…
 d0rb/cve-2024-4323
Critical heap buffer overflow vulnerability in the handle_trace_request and parse_trace_request functions of the Fluent Bit HTTP server.
 renio-wow/cve-2026-51416
Analyzes a specific CVE in WeChat OAuth handler, identifying unbounded HTTP response reads leading to denial of service, with remediation guidance.