
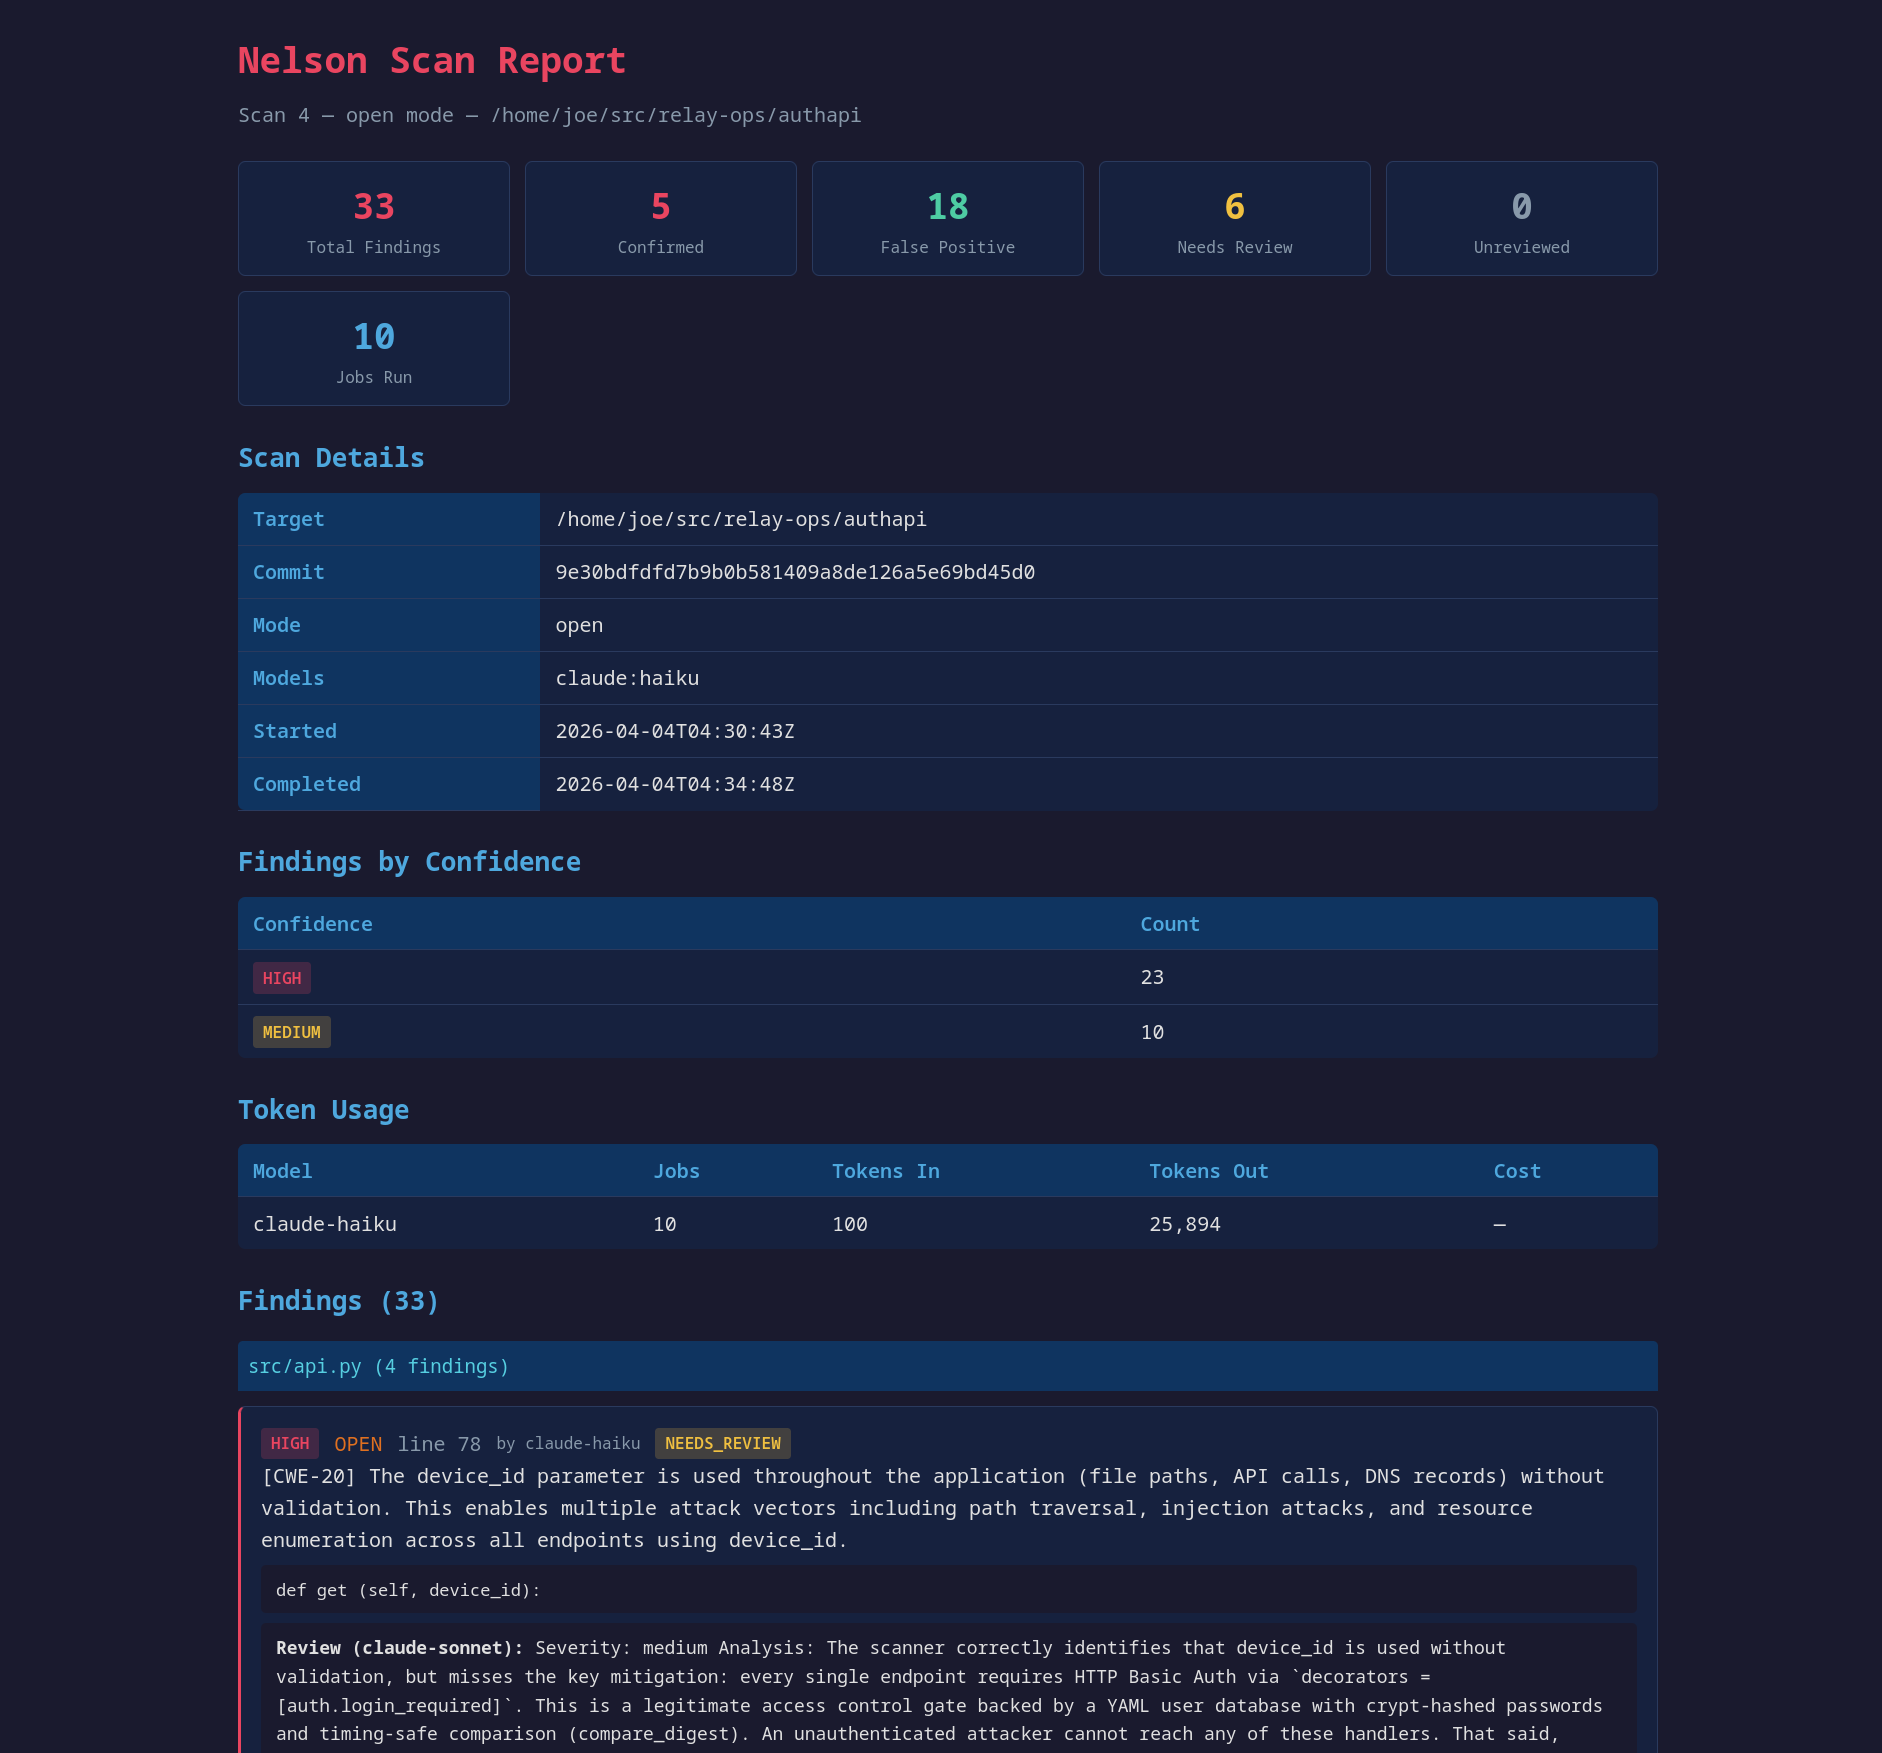
nelson
 swelljoe/nelson
Finding vulnerabilities through dumb brute force
ai-securitycode-analysiseducation+3
swelljoe/nelsonFinding vulnerabilities through dumb brute force
 oalabs/hashdb
Assortment of hashing algorithms used in malware
 pan-unit42/dotnetfile
Python library for parsing CLR/PE metadata in .NET assemblies, exposing streams and hash fingerprints to support malware analysis and threat hunting.
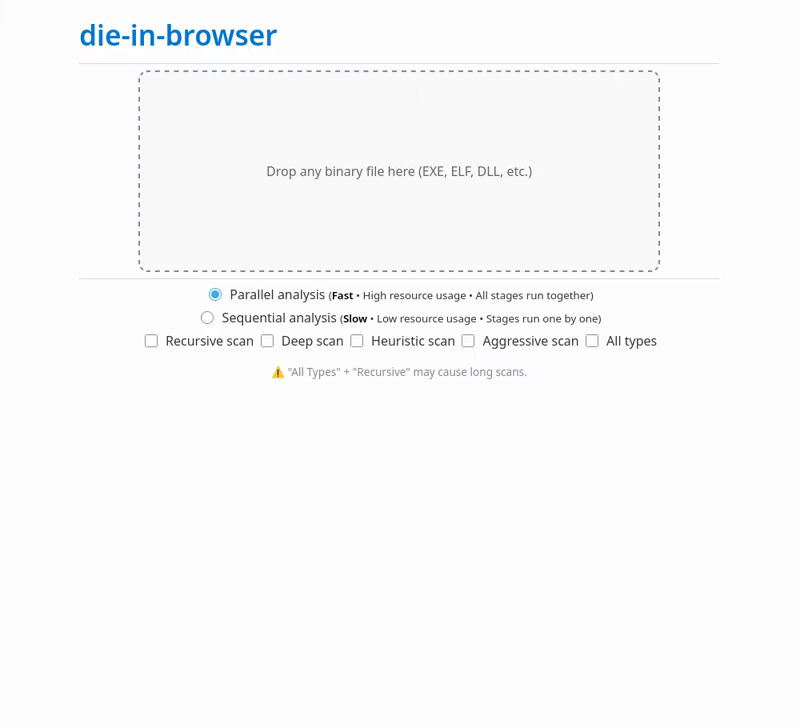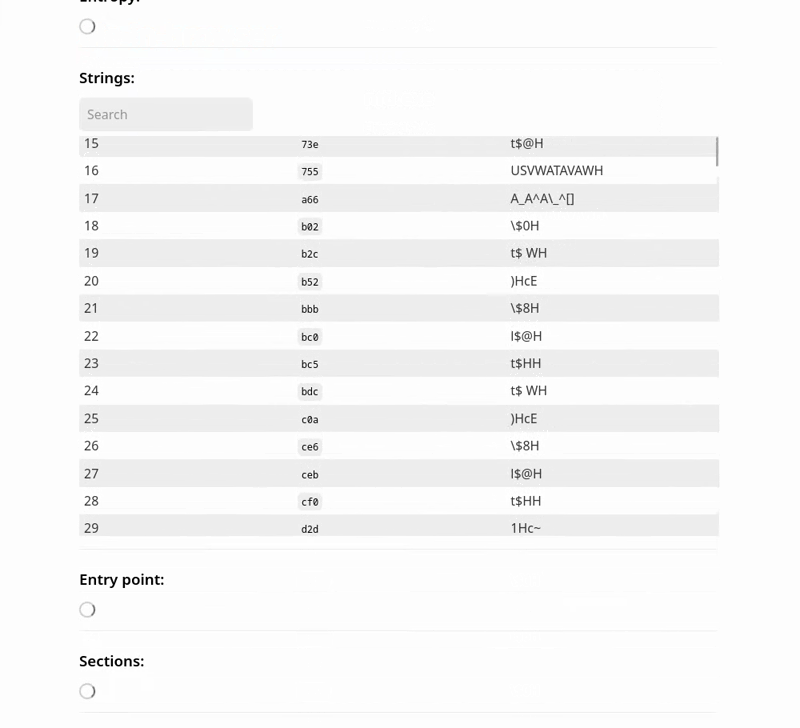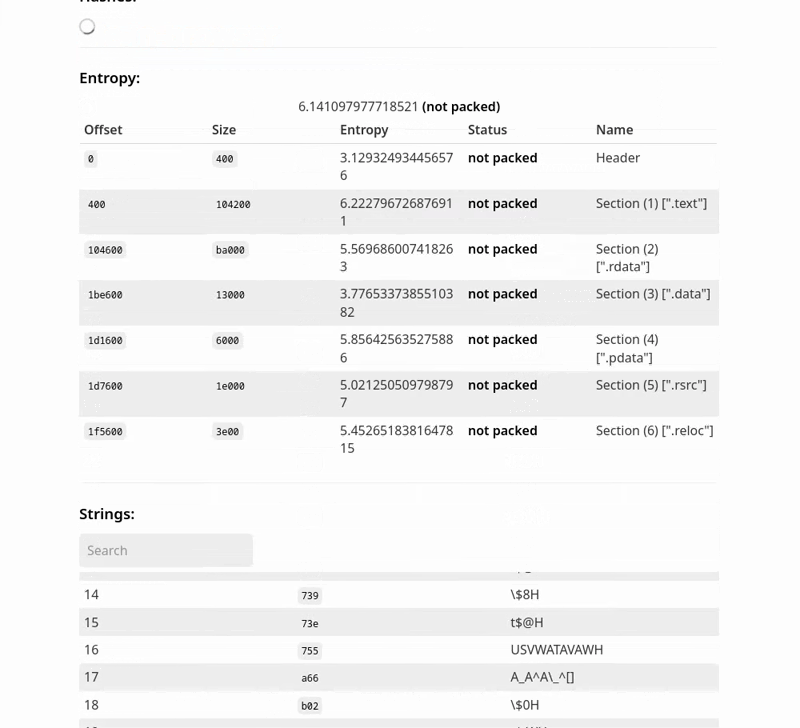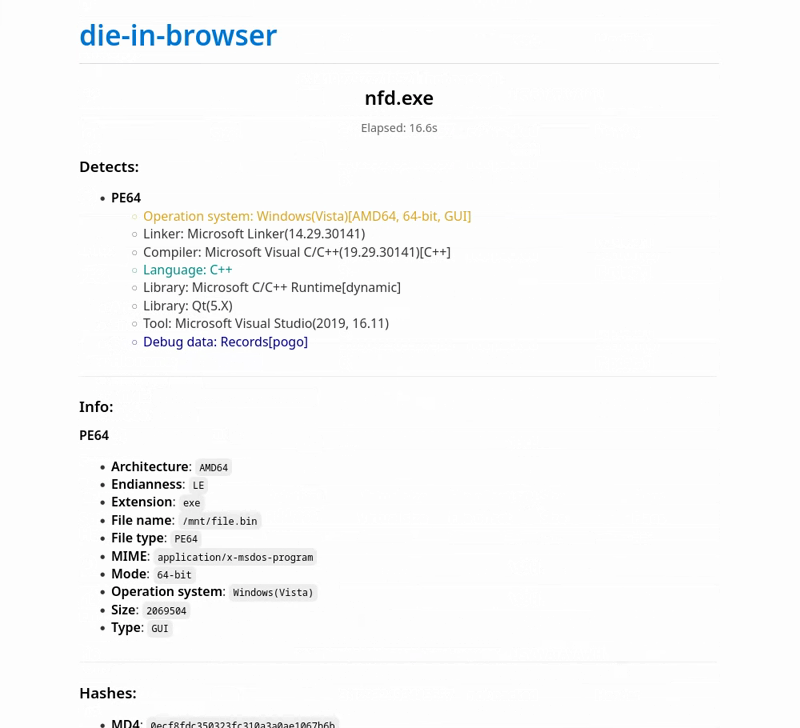 xoreaxlmbdx/die-in-browser
Static binary analysis with Detect It Easy — 100% in your browser, no uploads.