IntelOwl
Scalable threat intelligence platform that enriches observables and files using 200+ analyzers, with built-in GUI, REST API, and automated workflows…

Scalable threat intelligence platform that enriches observables and files using 200+ analyzers, with built-in GUI, REST API, and automated workflows…

Plugin for JADX to integrate MCP server

Malware detection using learning and information retrieval for Android

Python script using r2pipe to detect CVE-2017-13208 in Android libnetutils.so by checking for missing dhcp_size validation via static binary analysis.

Rule-based Android malware scoring engine that analyzes APKs using static and dynamic analysis to detect vulnerabilities, identify malware families,…

Static taint analysis platform for Android apps that detects vulnerabilities and compliance issues using customizable rule-based scanning and…

Decompiles Android APK/XAPK/JAR/AAR files and extracts HTTP APIs, authentication patterns, and call flows using jadx, with R8-resistant Kotlin name…

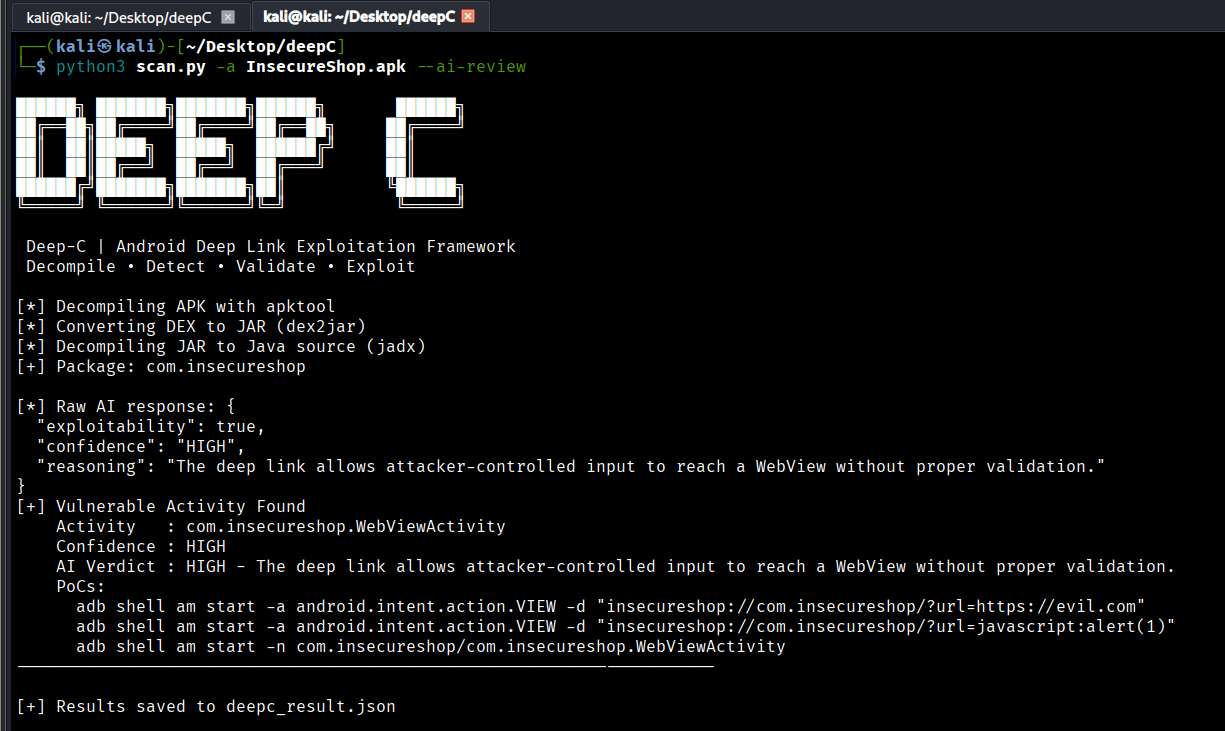
Android deeplink misconfiguration detector and exploitation tool

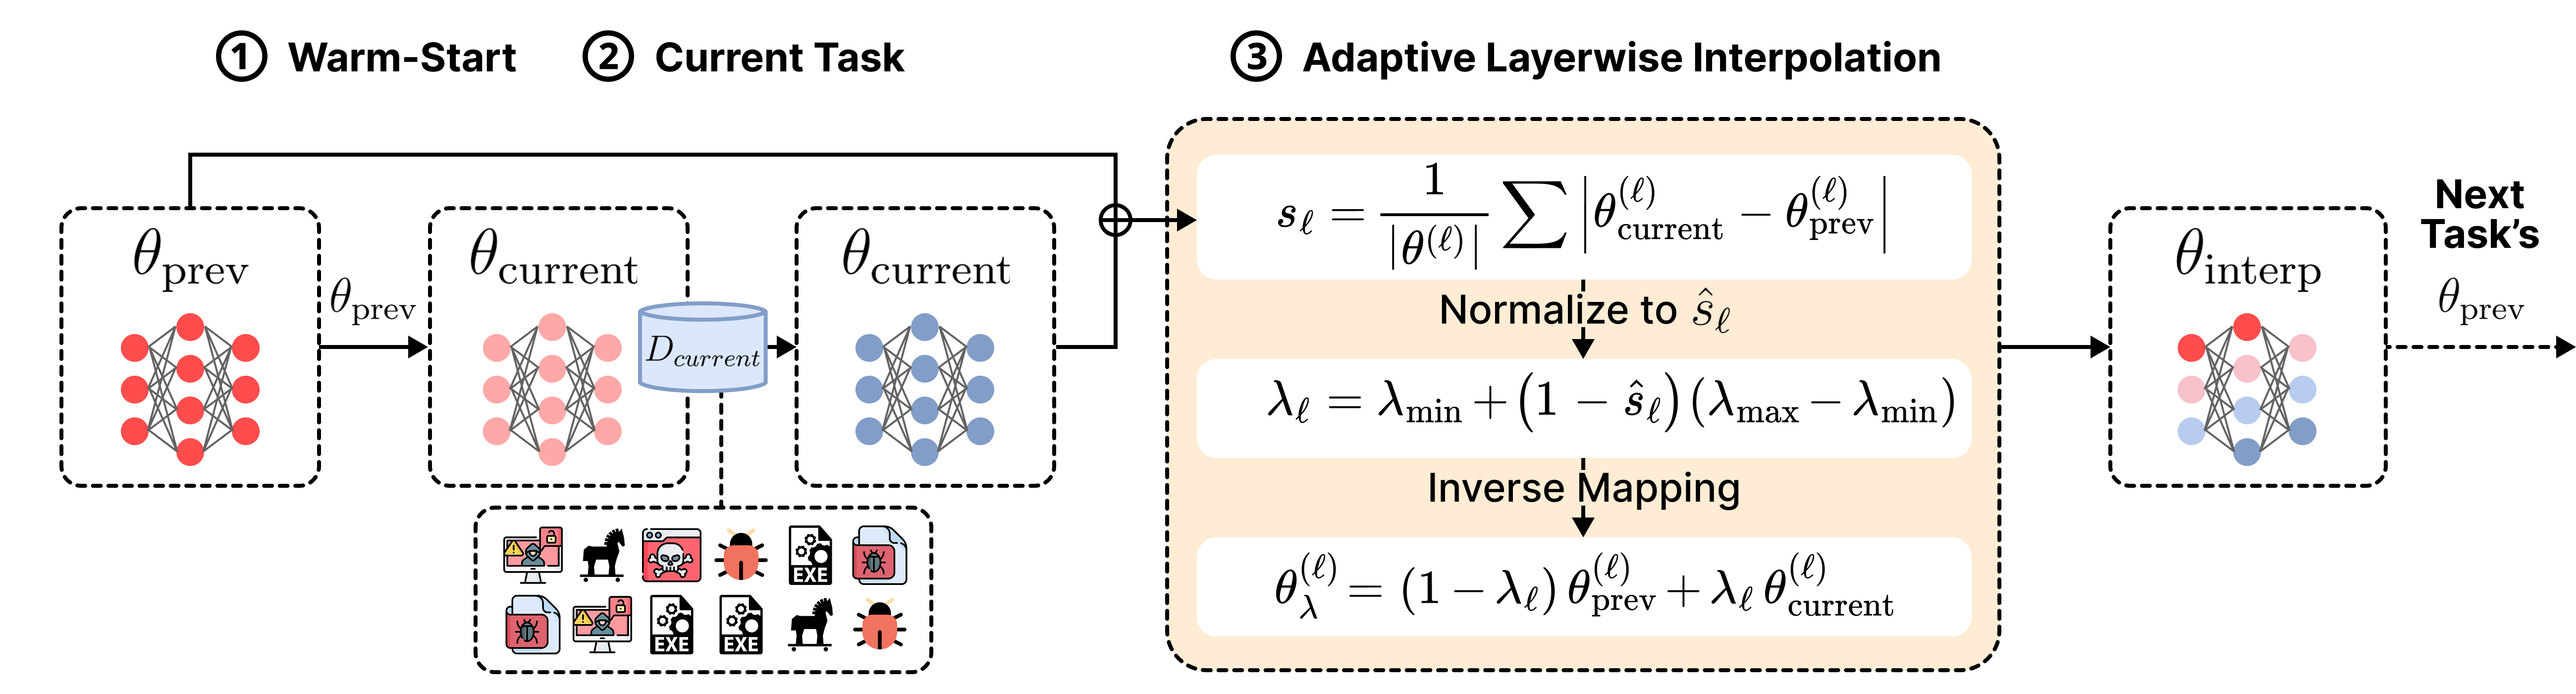
Memory-free continual learning framework for malware classification using mode connectivity-based interpolation. Supports class-incremental and…

Ghidra is a software reverse engineering (SRE) framework

Radare2 and Frida better together.