
Archived
anchore-engine
 anchore/anchore-engine
A service that analyzes docker images and scans for vulnerabilities
cloud-securitycontainer-securitydevsecops+3
1.6k
anchore/anchore-engineA service that analyzes docker images and scans for vulnerabilities
 otsmane-ahmed/ci-supplychain-guard
Static analysis tool that detects malicious dependencies in CI/CD pipelines using pattern matching and AST analysis, with a traffic-light risk…
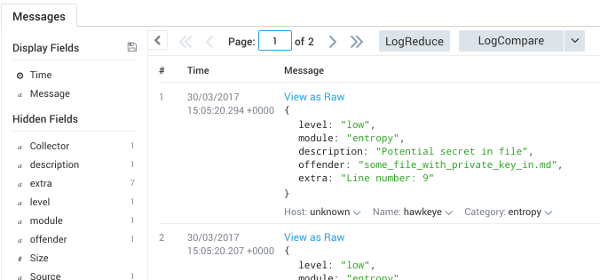 hawkeyesec/scanner-cli
A project security/vulnerability/risk scanning tool
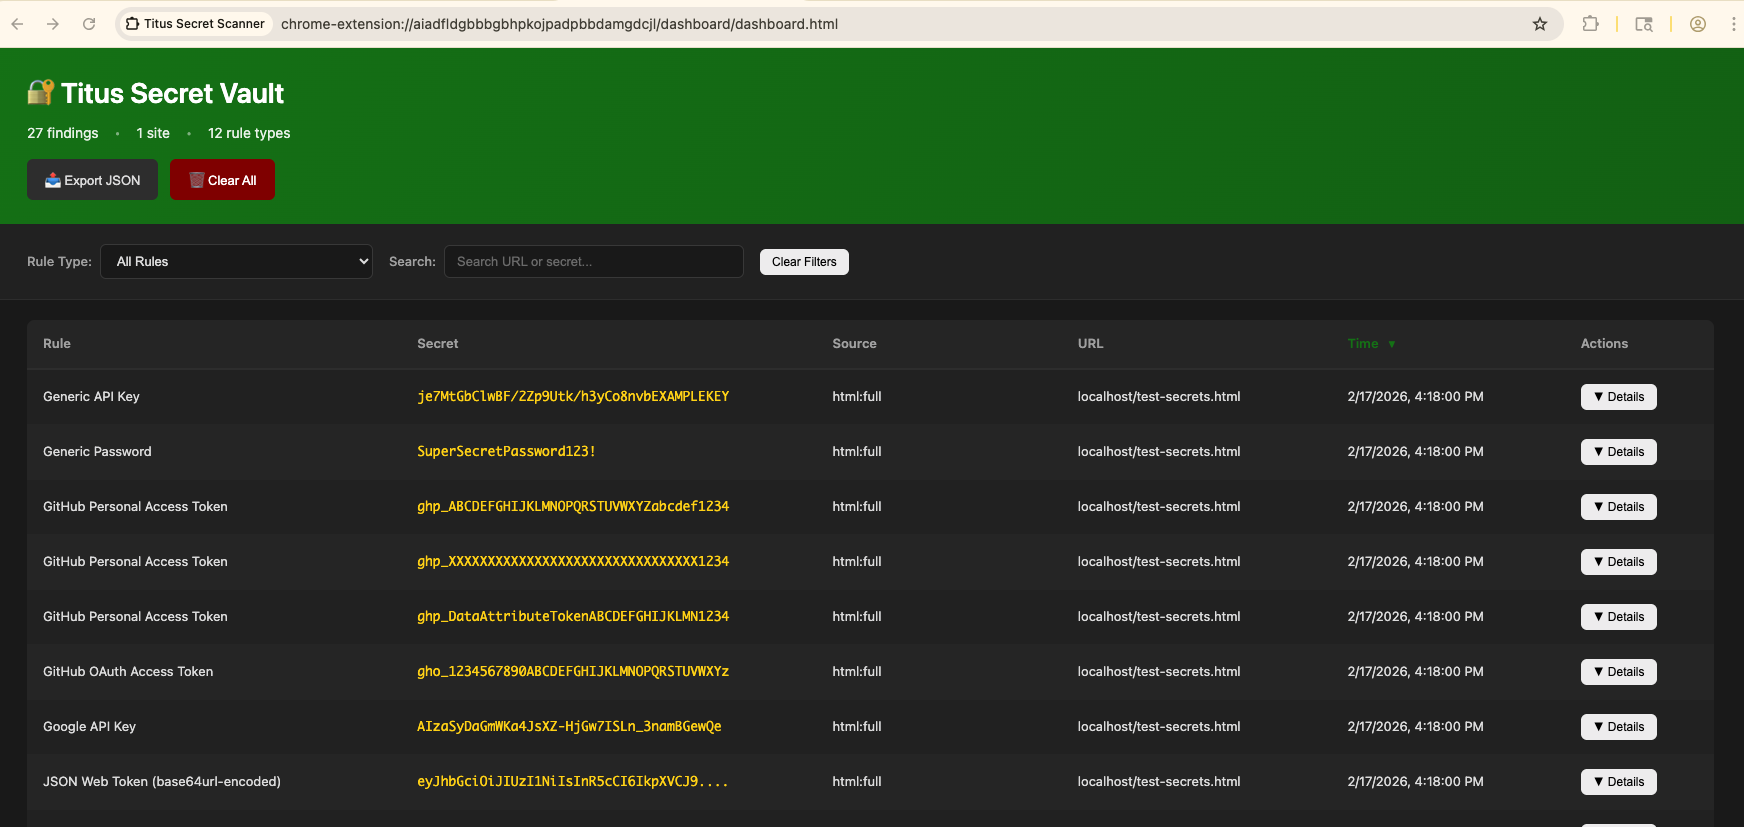 praetorian-inc/titus
High-performance secrets scanner. CLI, Go library, Burp Suite extension, and Chrome extension. 487 detection rules with live credential validation.
 aquasecurity/trivy-module-wordpress
Trivy example module for WordPress
 phanhoangkhang/react2shell
Isolated Docker lab and static scanner for CVE-2025-55182, with vulnerable/patched Next.js builds and PoC validation of RSC Flight deserialization.
 vesjolyjd/kaspersky_cve-2024-3094
Security review of CVE-2024-3094 (XZ Utils backdoor) including threat modeling, static/dynamic code analysis, fuzzing with AFL++, and a…
 cristianzsh/freki
Open-source malware analysis platform with static PE analysis, YARA pattern matching, VirusTotal integration, REST API, and Docker deployment for…
 bogdanticu88/threatmap
IaC threat modeler with STRIDE, MITRE ATT&CK, and PASTA frameworks. REST API, GraphQL, and Docker support for Terraform, CloudFormation, and…
 maweil/bidi_char_detector
Checks your files for existence of Unicode BIDI characters which can be misused for supply chain attacks. See CVE-2021-42574
 dinosn/fastjson-jsontype-rce-lab
Docker labs + defensive scanner for fastjson remote-class-load RCE. fastjson 1.2.66-1.2.83: @JSONType resource probe (CVE-2026-16723). fastjson2…
 gach0ng/agentstalker
End-to-end security audit framework for LLM agents: static AST and taint modeling, attack synthesis, Docker sandbox replay, and deterministic verdict…
 apaonum/brotli-cve-check
Agent skill + script to scan projects for CVE-2026-111497 (Brotli), rate criticality and suggest fixes
 aquasecurity/scan-cve-2018-8115
CLI tool that verifies Docker images for CVE-2018-8115 by checking layers for malicious files, helping ensure safe pulls from Docker Hub.
 shcesama/cve-2023-4863-analysis
Educational analysis of CVE-2023-4863 (libwebp heap buffer overflow) with Blue Team detection tools, static WebP scanner, defensive Java validator,…
 nccgroup/mtk_bp
Tools for analyzing and reverse engineering MediaTek baseband firmware, including file extraction, symbol parsing, and Ghidra integration for modem…
 praetorian-inc/capability-sdk
Shared Go SDK defining a standard capability interface for security scanners, with multi-format finding output (terminal, JSON, NDJSON, Markdown,…
 liamg/extrude
:detective: Analyse binaries for missing security features, information disclosure and more...