CVE-2024-51132-POC
Proof-of-concept exploit for CVE-2024-51132, an XML External Entity (XXE) injection vulnerability in HAPI FHIR core libraries, enabling SSRF and…

Proof-of-concept exploit for CVE-2024-51132, an XML External Entity (XXE) injection vulnerability in HAPI FHIR core libraries, enabling SSRF and…

The Mobile App Pentest cheat sheet was created to provide concise collection of high value information on specific mobile application penetration…

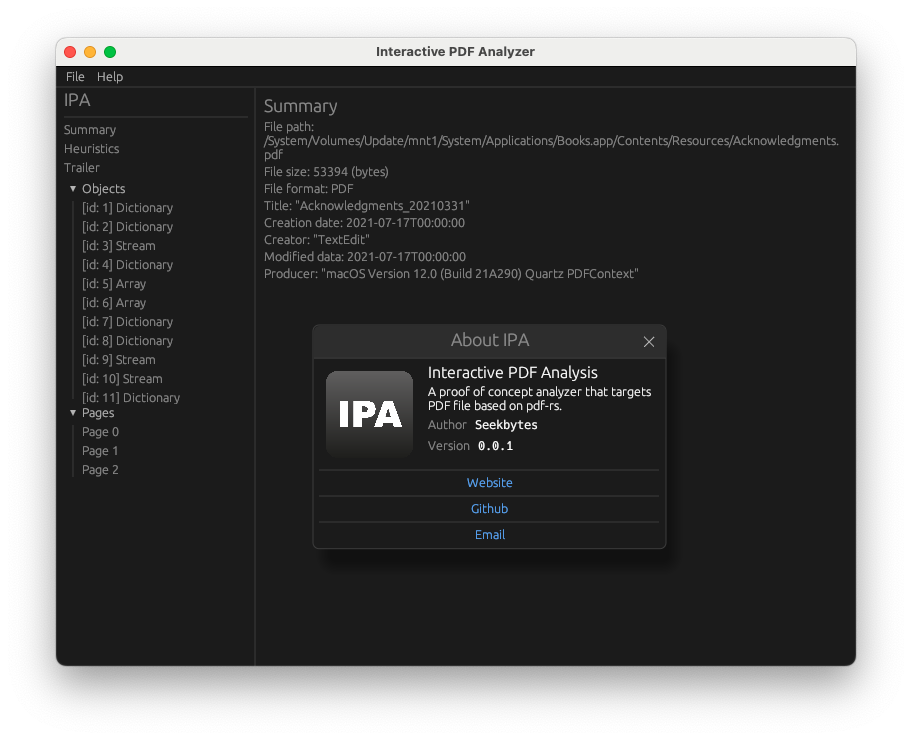
GUI analyzer for deep-diving into PDF files. Detect malicious payloads, understand object relationships, and extract key information for threat…

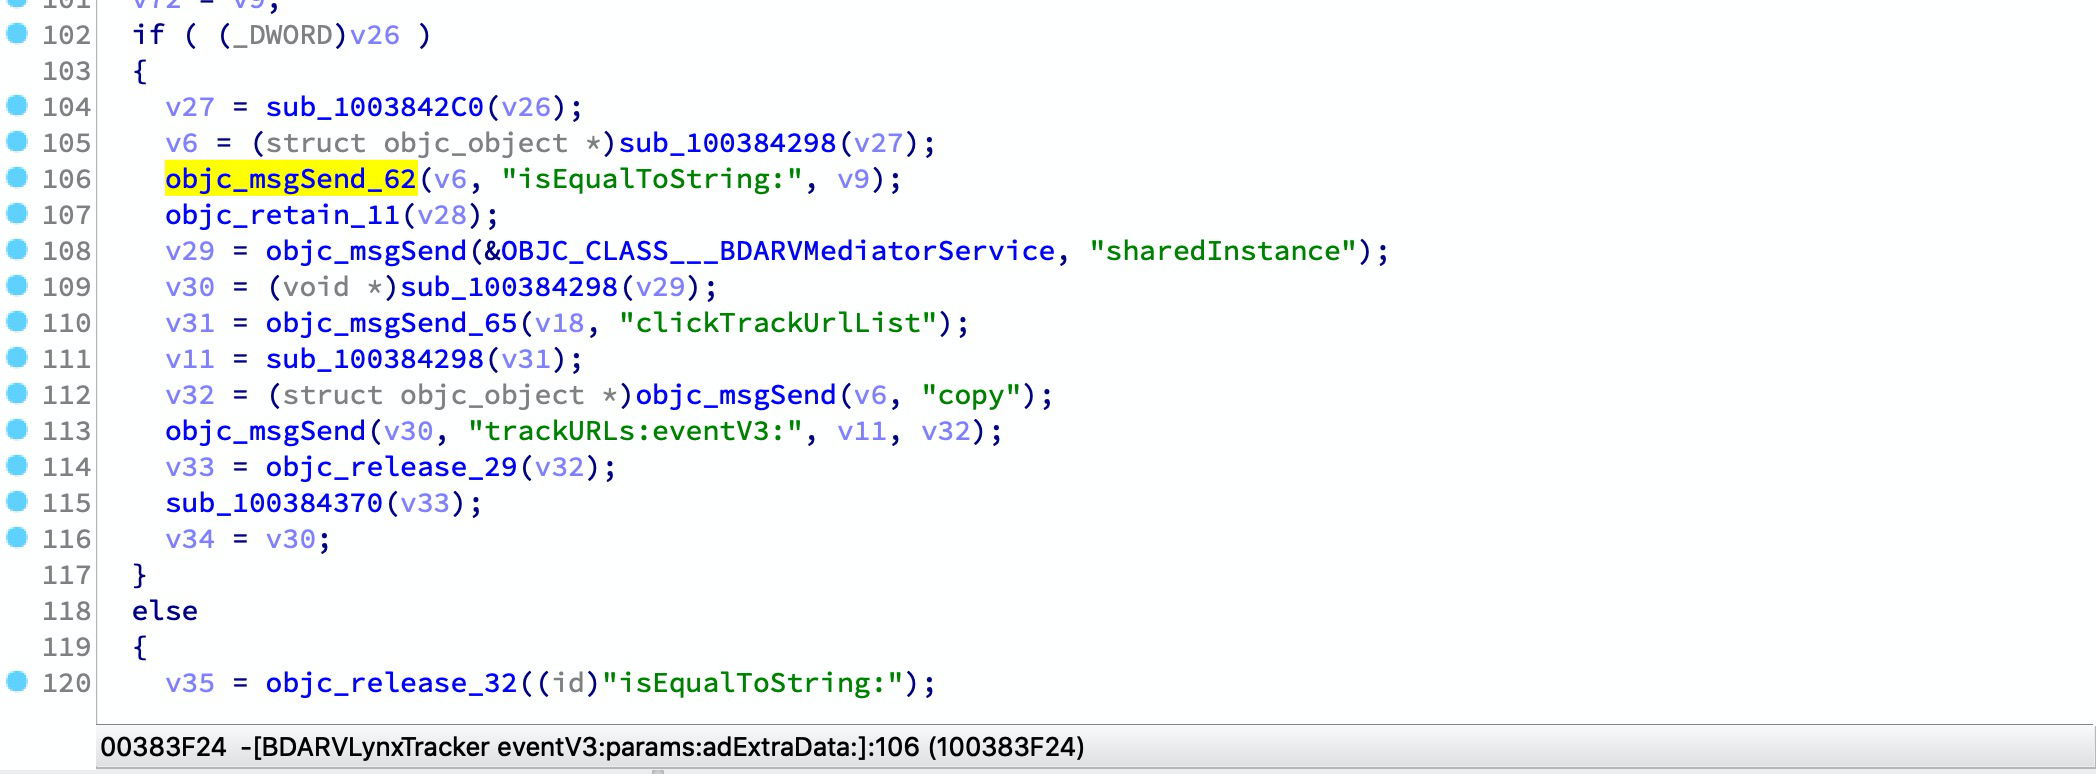
iblessing is an iOS security exploiting toolkit, it mainly includes application information gathering, static analysis and dynamic analysis. It can…

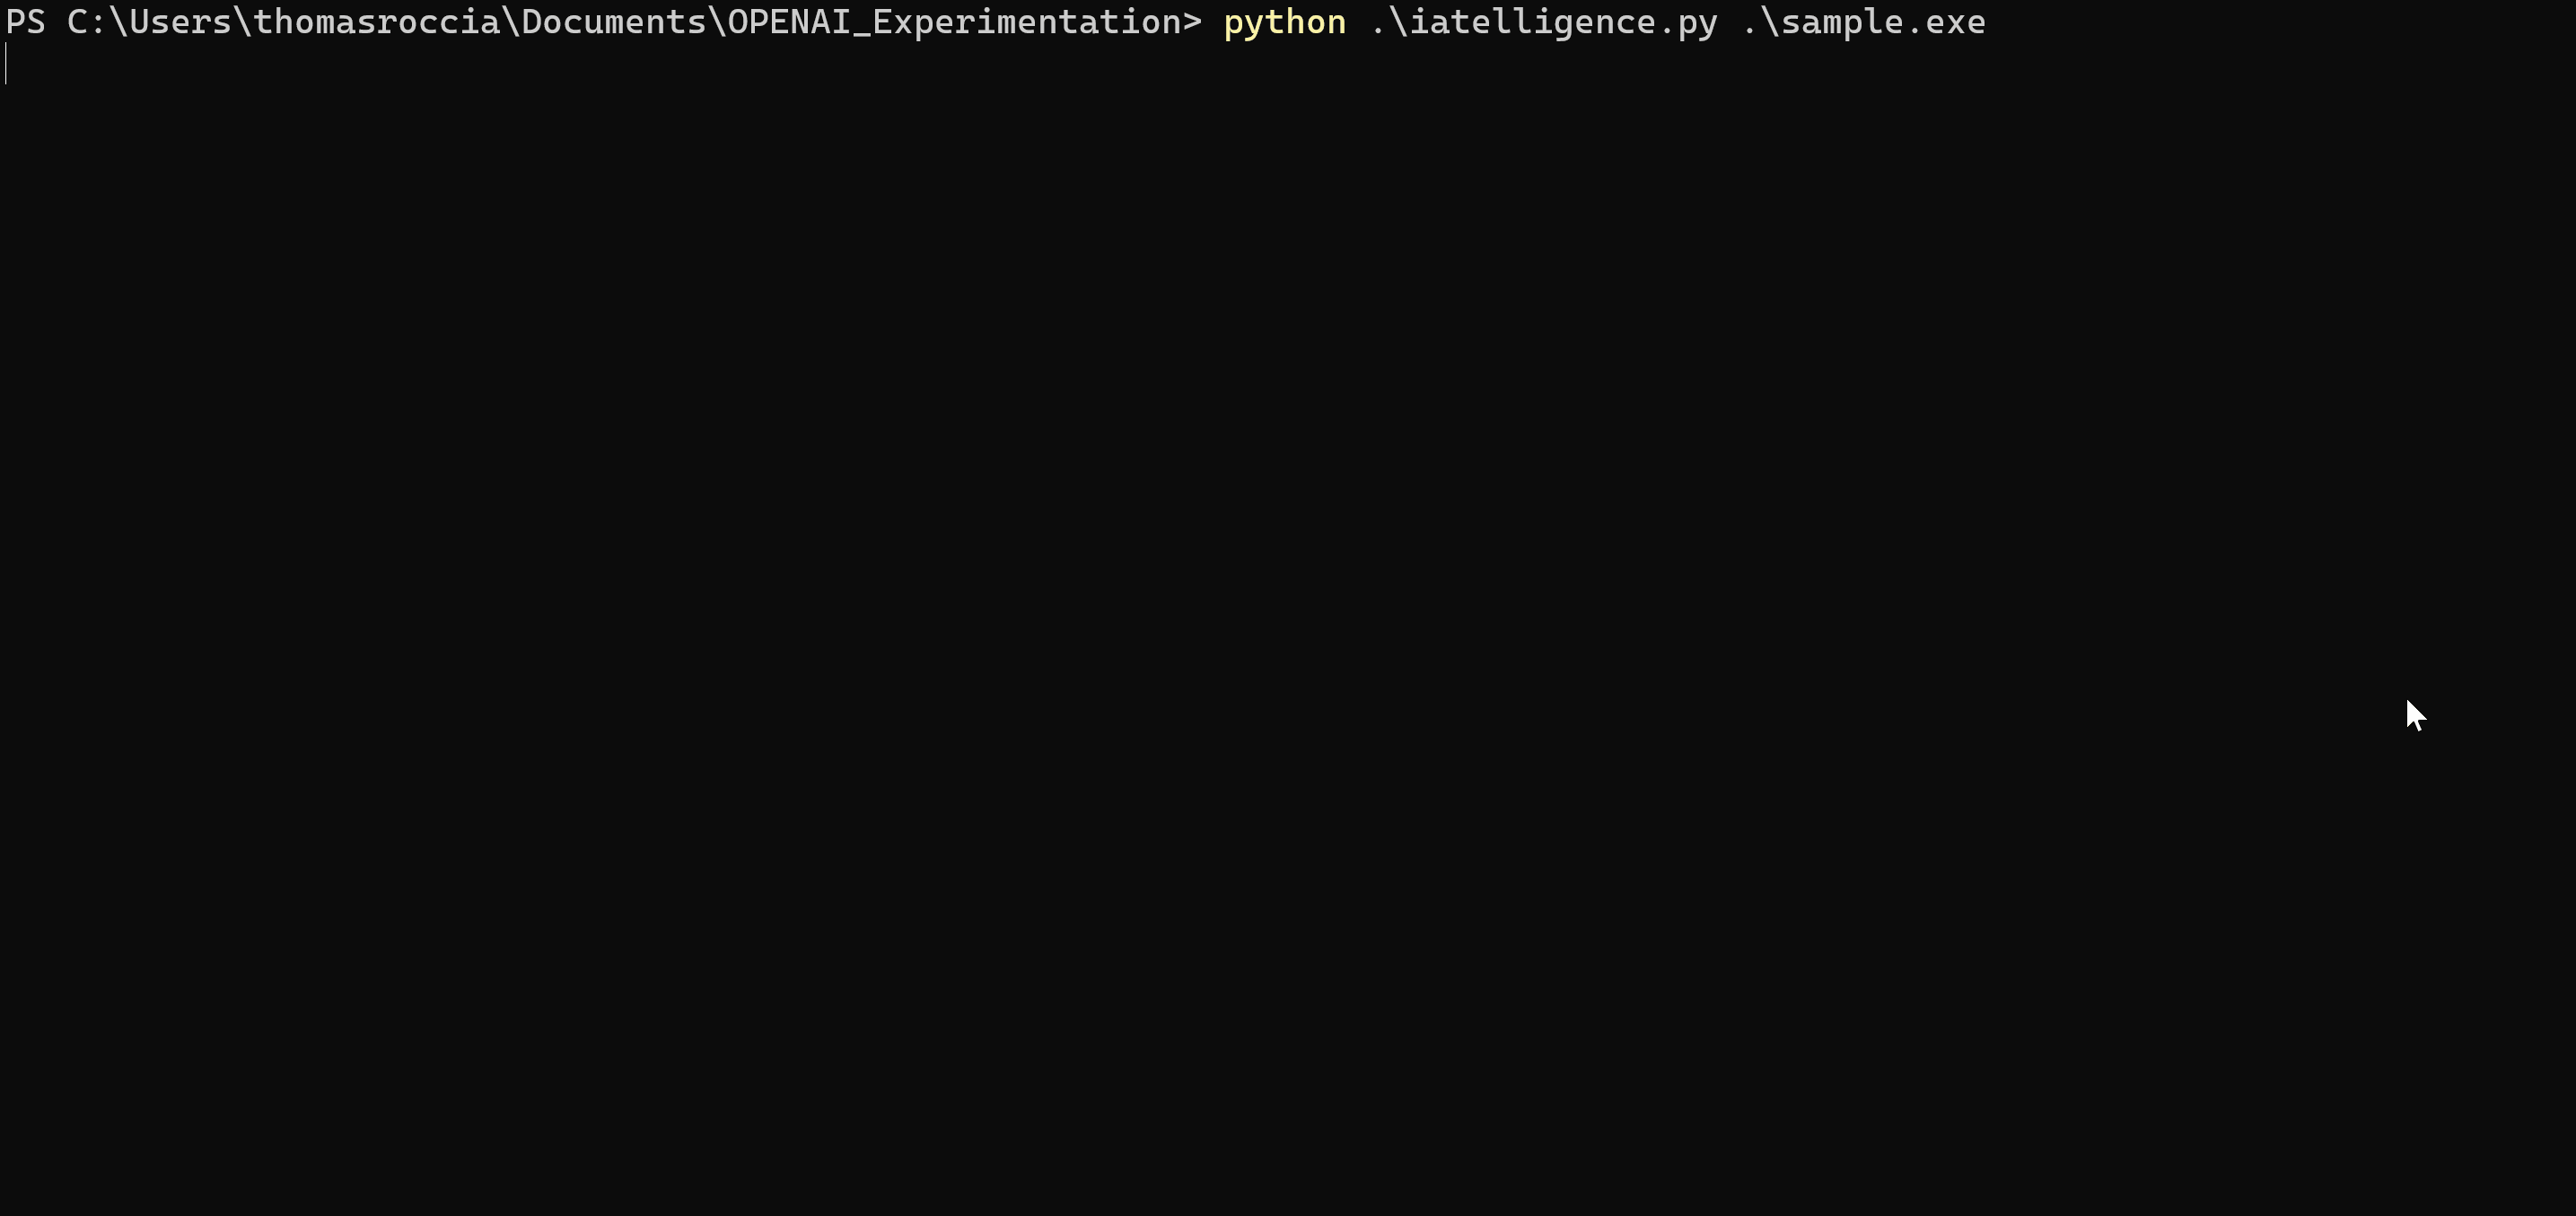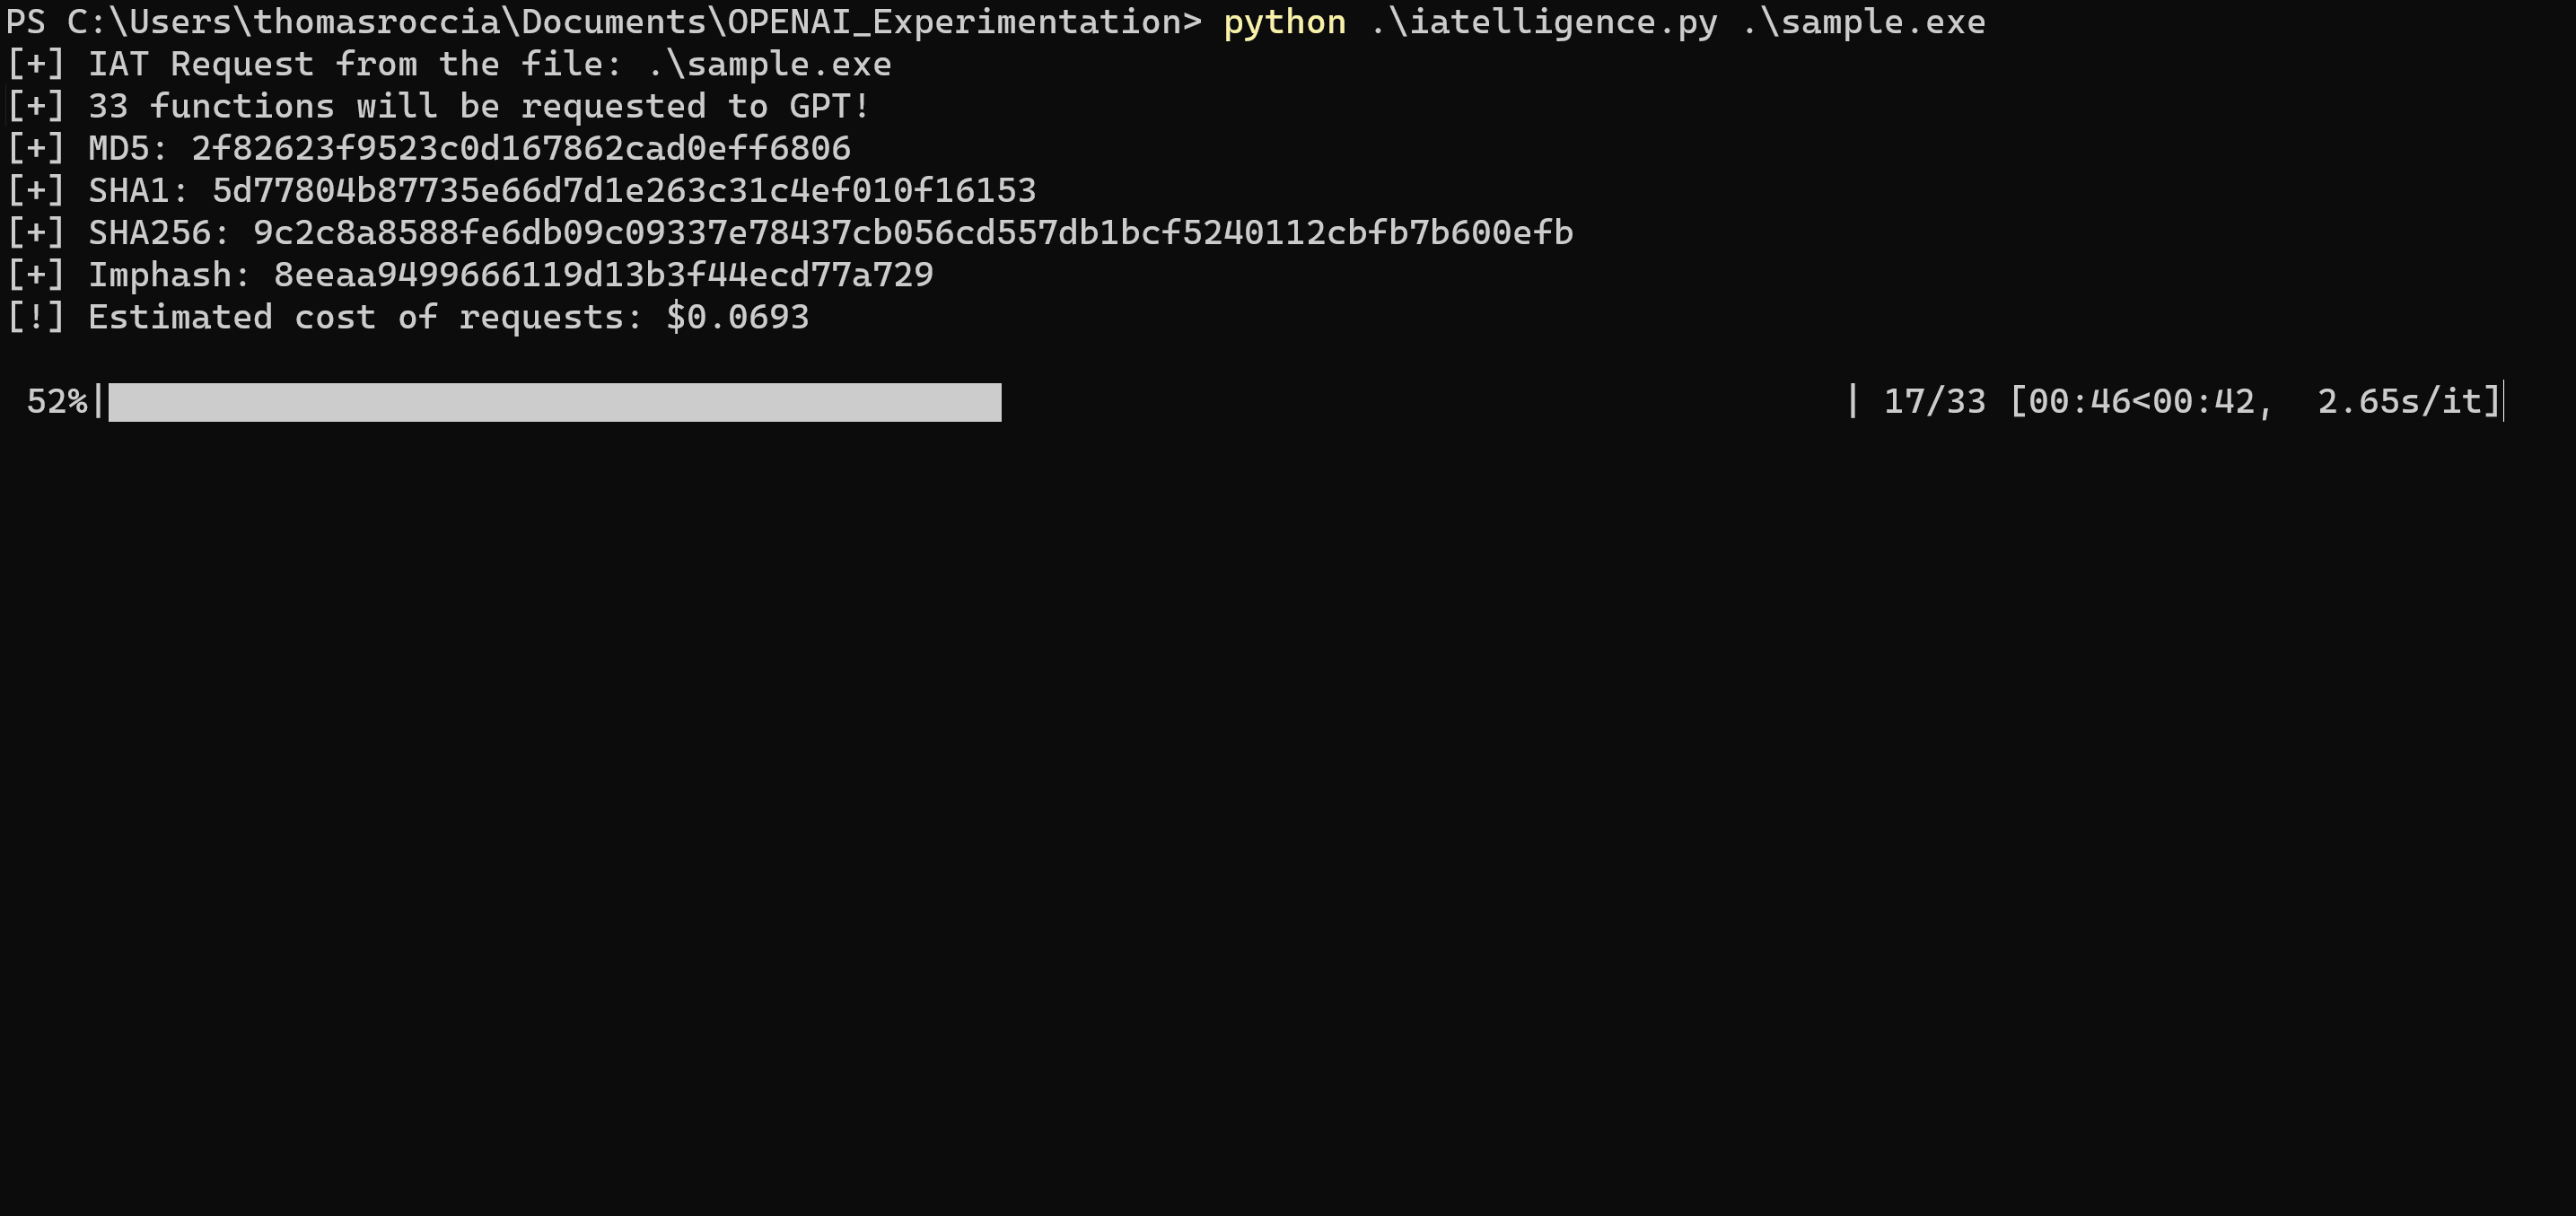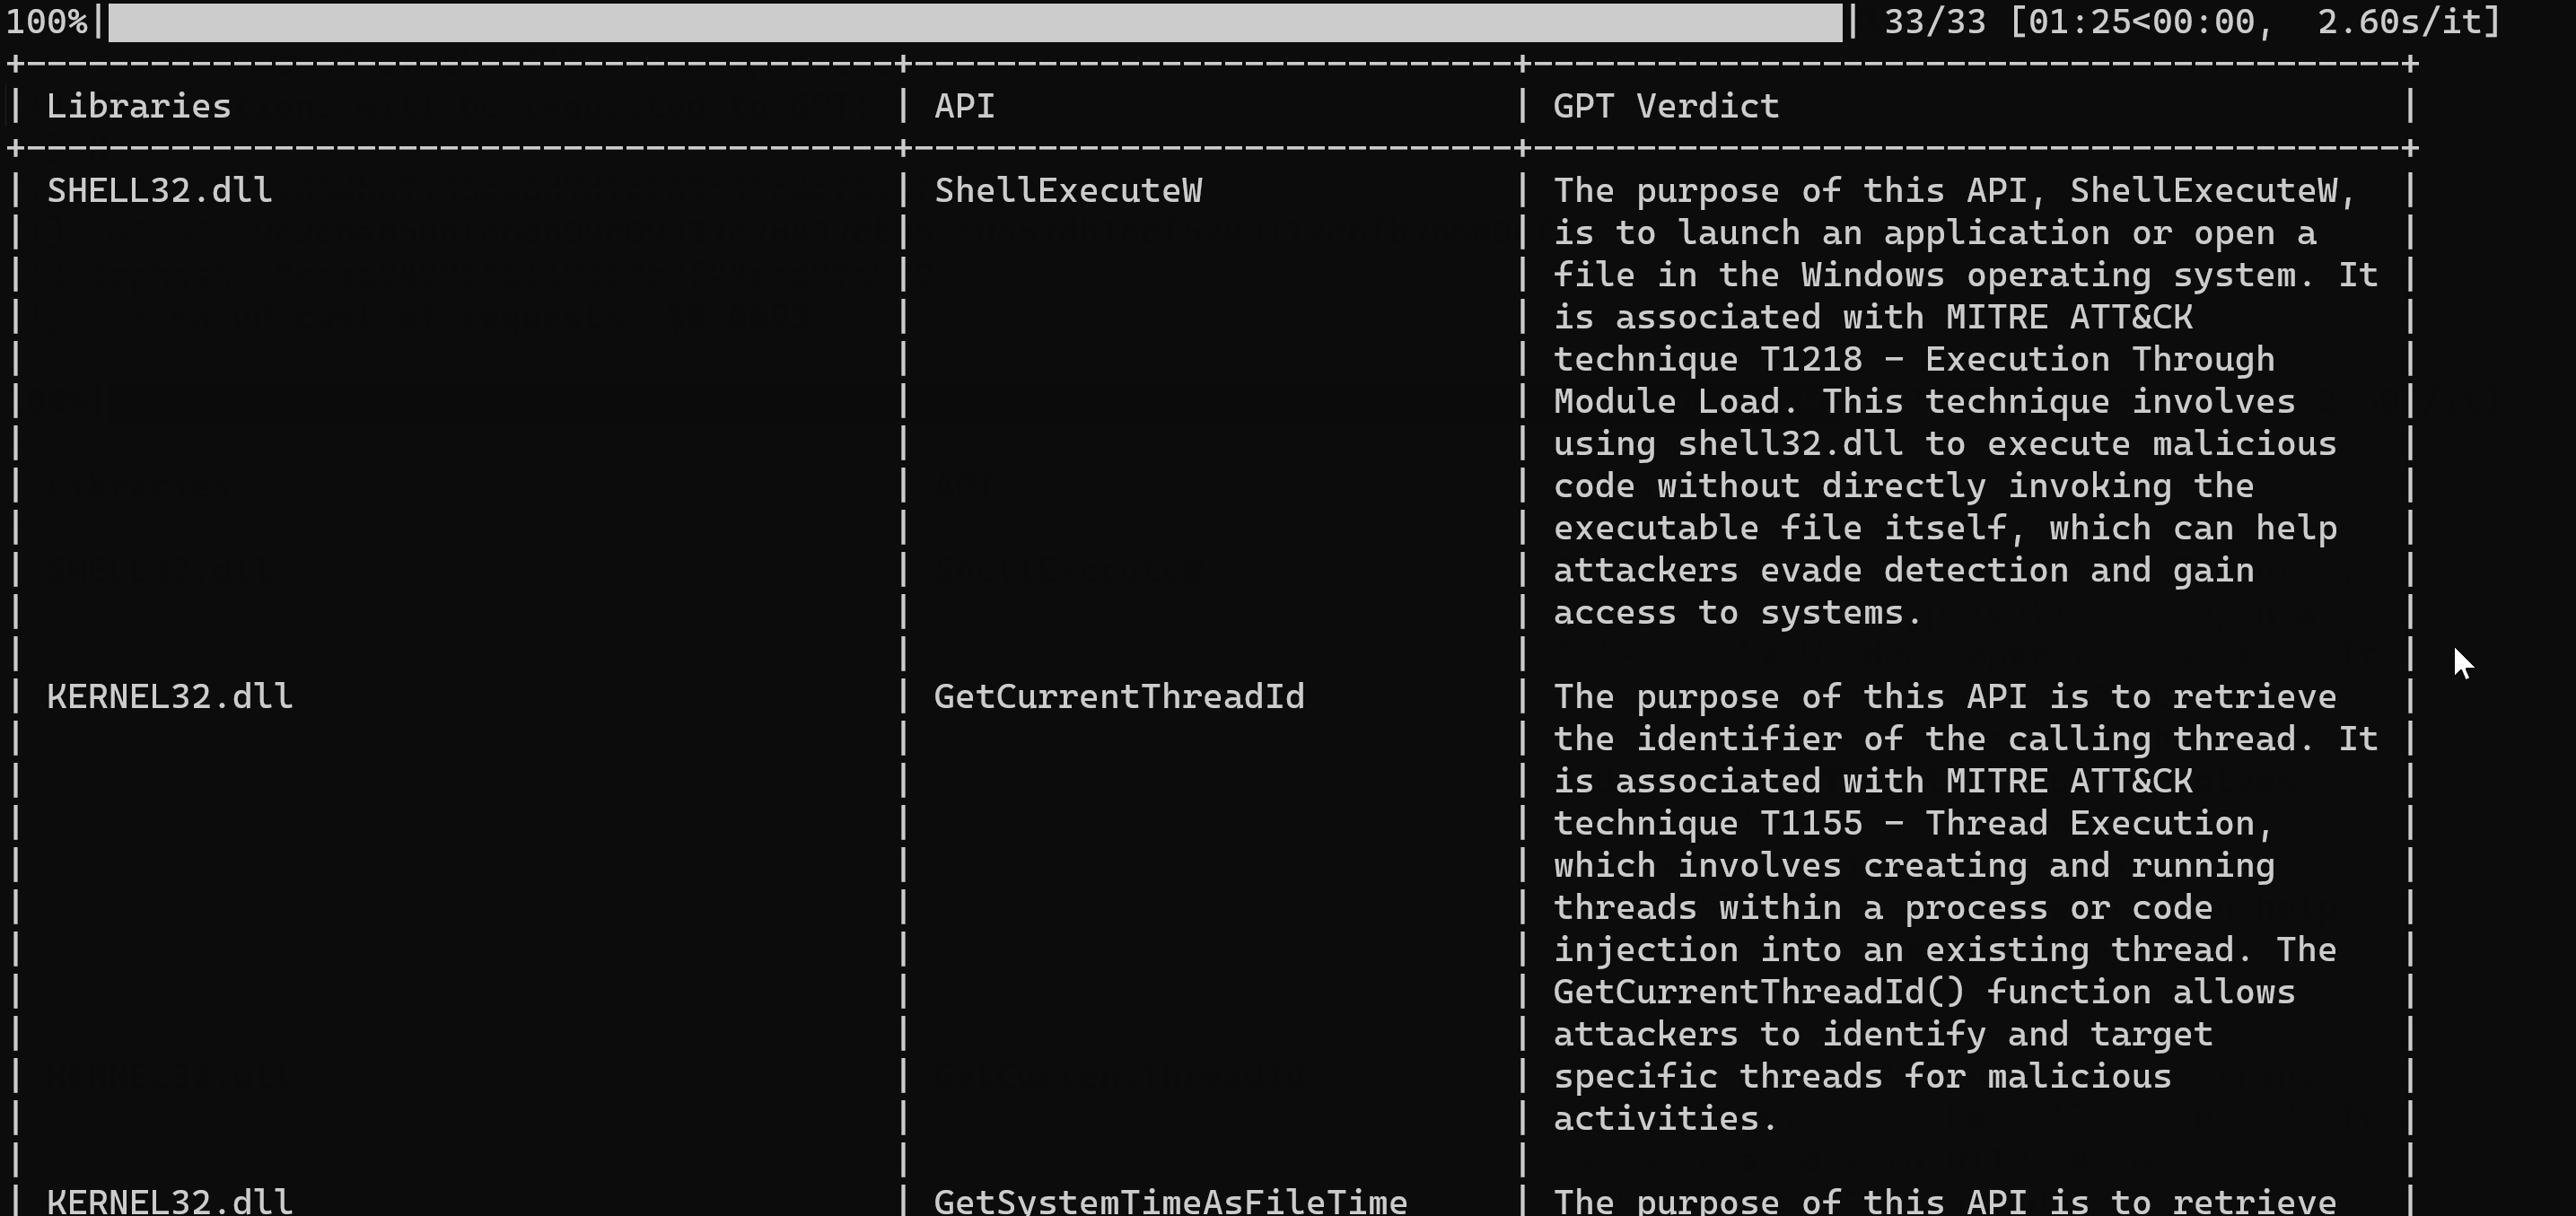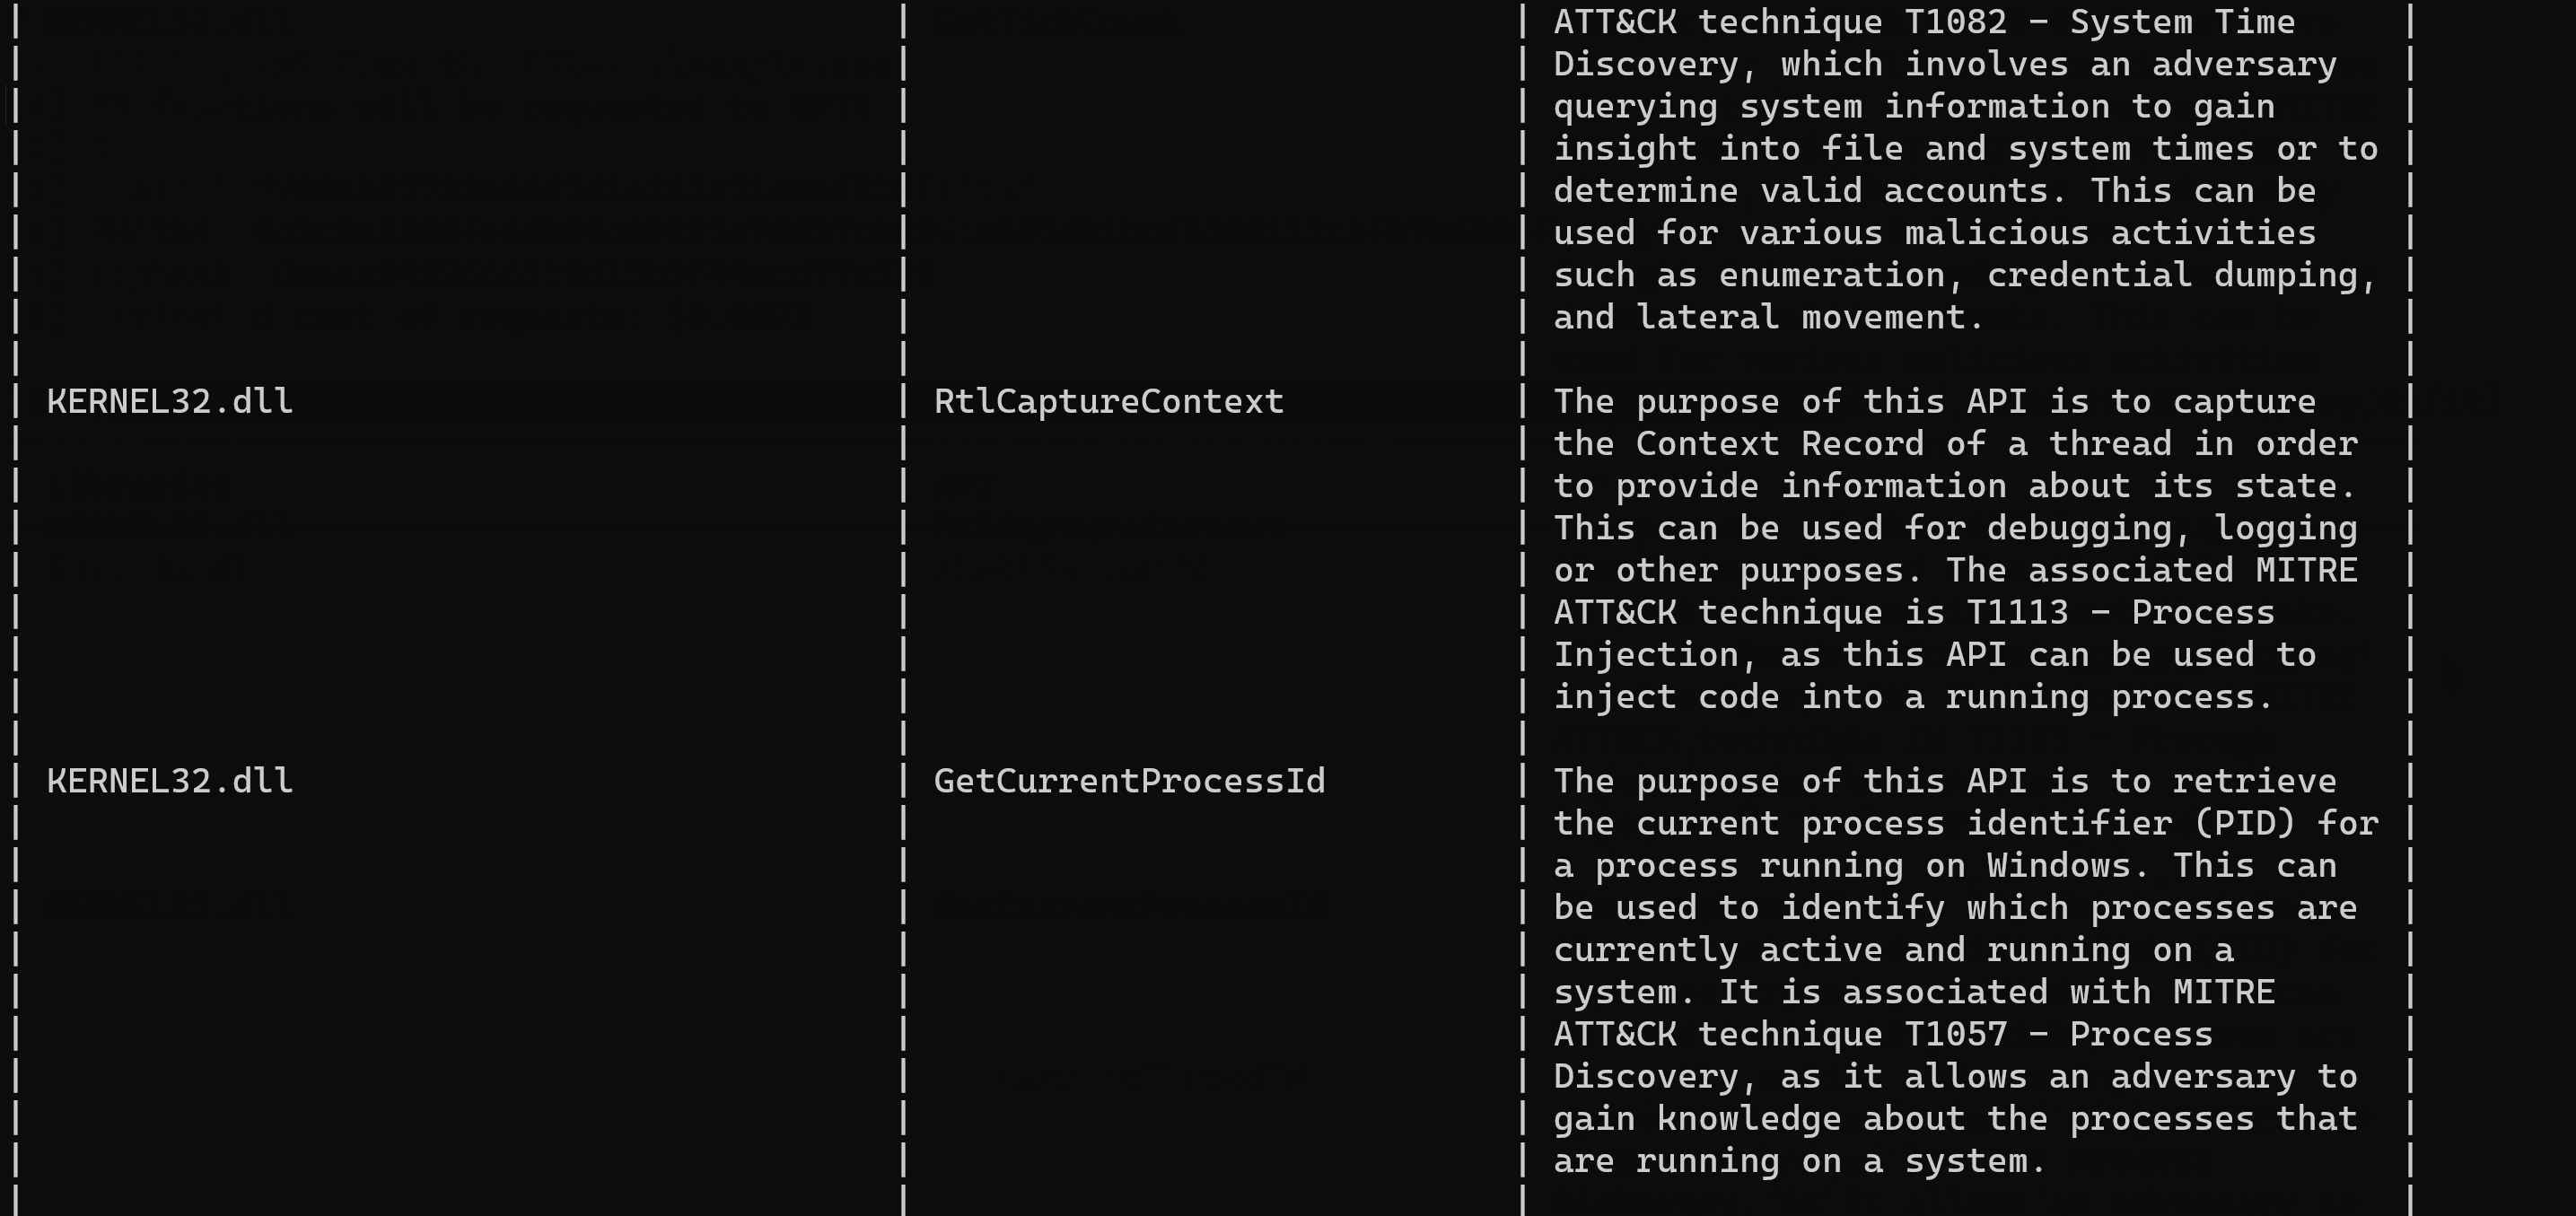
IATelligence is a Python script that will extract the IAT of a PE file and request GPT to get more information about the API and the ATT&CK matrix…

Malware detection using learning and information retrieval for Android

Mobile Reconnaissance Framework is a powerful, lightweight and platform-independent offensive mobile security tool designed to help hackers and…

:detective: Analyse binaries for missing security features, information disclosure and more...

Mobile Helper Framework (mhf) is a tool that automates the process of identifying the framework/technology used to create a mobile application.…

Information flow analysis tool for Android applications

A comprehensive browser extension (.xpi) malware scanner which checks for many common malware tricks like:, credential-stealers obfuscation tactics,…

**HashEye** is a powerful Python CLI tool for instantly detecting and analyzing hash types. It provides detailed information about hash formats,…

Extracts and exports certificate information from digitally signed PE files using Python and pefile, enabling forensic analysis of code-signing…

Proof-of-concept and technical analysis of CVE-2023-25813, a SQL injection vulnerability in Sequelize ORM versions prior to 6.19.1, including…

Static analysis tool for iOS applications that extracts links, API keys, subdomains, binary info, linked libraries, and strings to aid mobile…

Android Application Identifier for Packers, Protectors, Obfuscators and Oddities - PEiD for Android

x64 PE bin2bin obfuscator which doesn't add a section to the binary

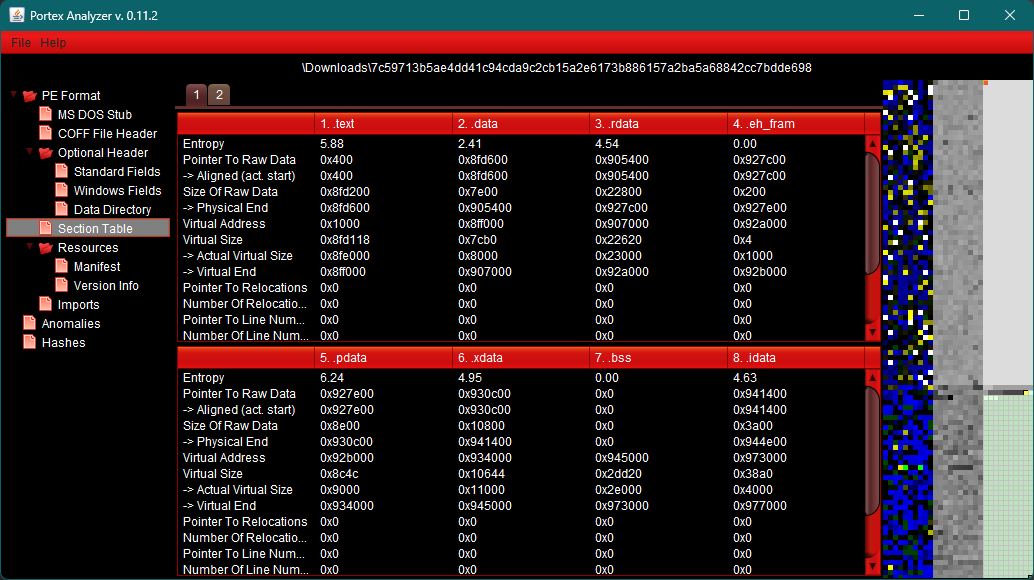
Graphical interface for PortEx, a Portable Executable and Malware Analysis Library