

dexcalibur
 reversenseorg/dexcalibur
[Official] Android reverse engineering tool focused on dynamic instrumentation automation leveraging Frida. It disassembles dex, analyzes it…
android-securitybinary-analysisdebuggers+5
1.2k
reversenseorg/dexcalibur[Official] Android reverse engineering tool focused on dynamic instrumentation automation leveraging Frida. It disassembles dex, analyzes it…
 0xpwny/apkatshu
Apkatshu is a Tool for extracting urls , emails , ip address , and interesting data from APK files
 maldroid/maldrolyzer
Simple framework to extract "actionable" data from Android malware (C&Cs, phone numbers etc.)
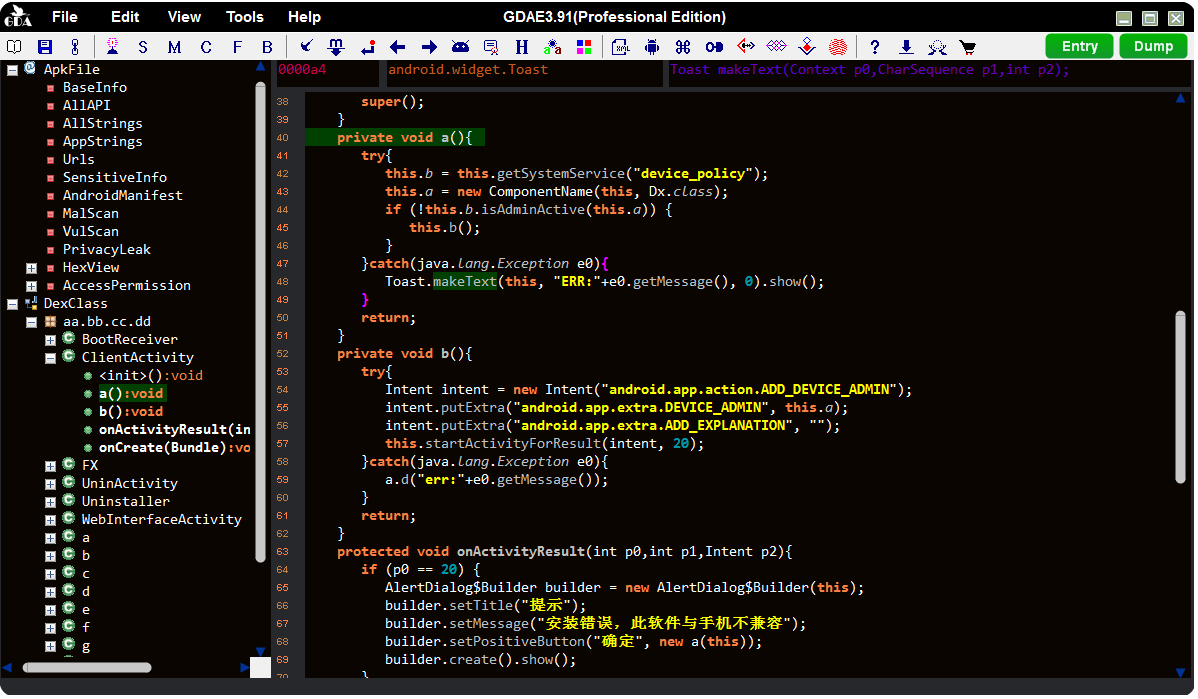 charles2gan/gda-android-reversing-tool
the fastest and most powerful android decompiler(native tool working without Java VM) for the APK, DEX, ODEX, OAT, JAR, AAR, and CLASS file. which…
 tls456/cve-2026-43805-poc
CVE-2026-43805 IOKit IODMACommand race analysis and proof of concept