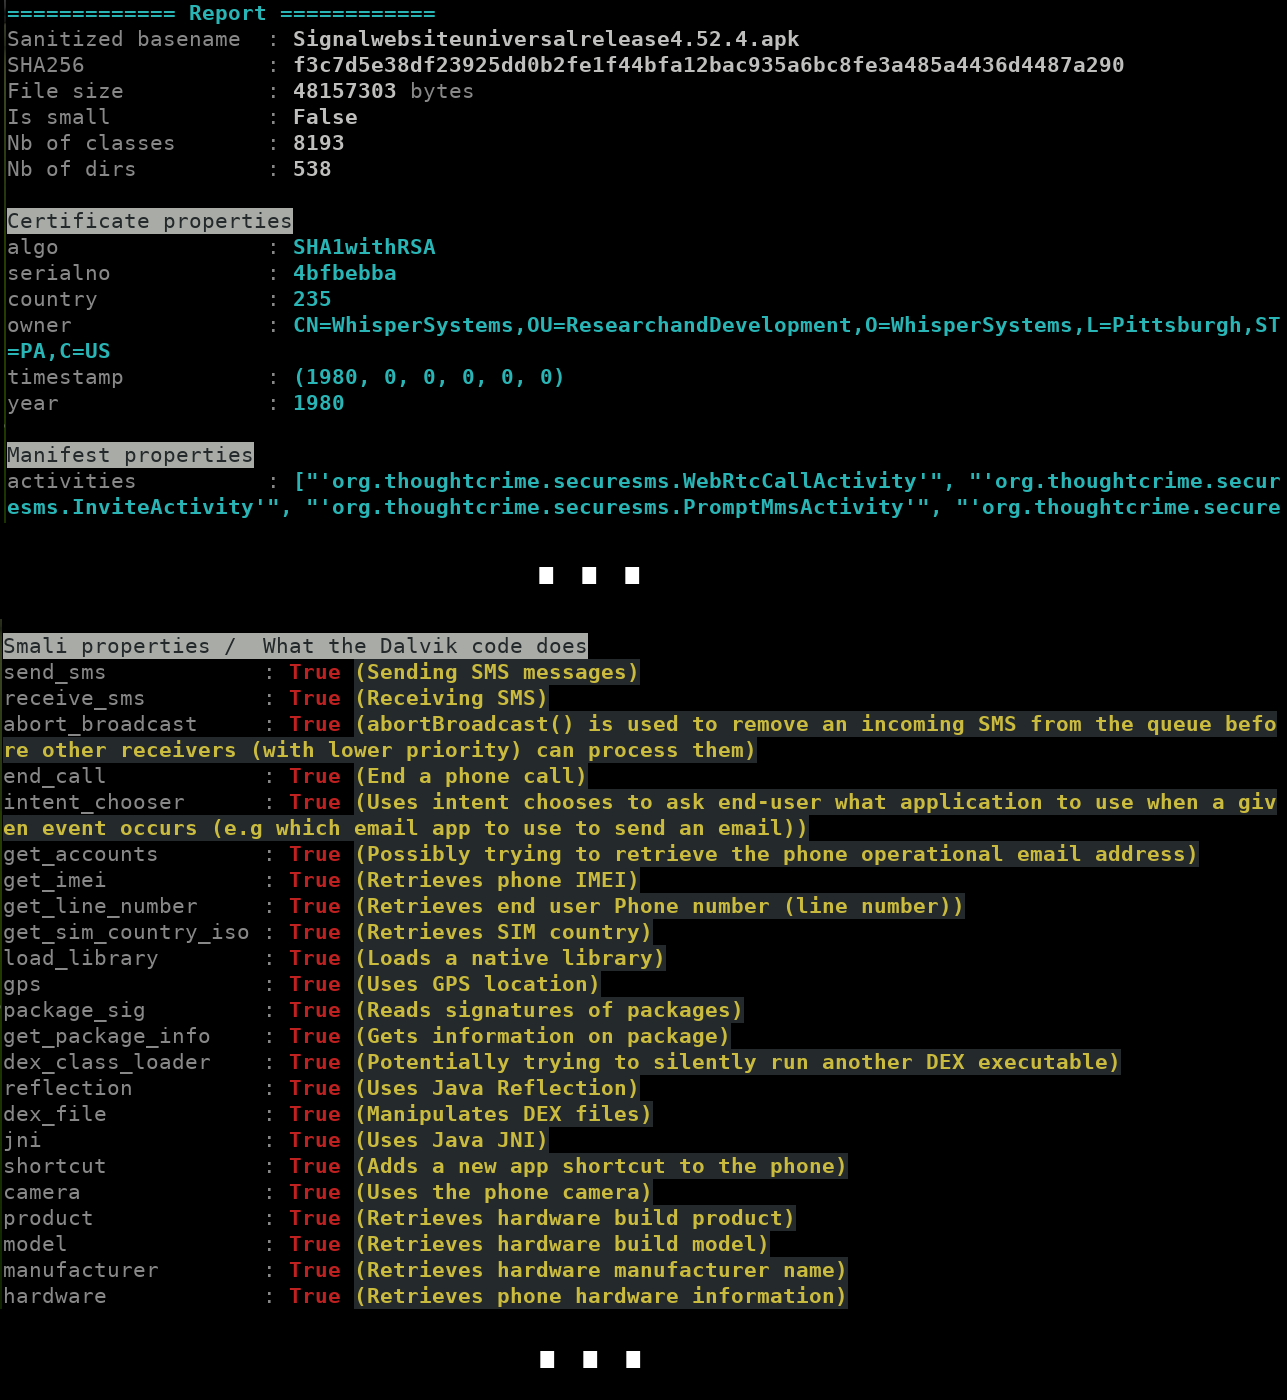
droidlysis
 cryptax/droidlysis
Automated pre-analysis tool for Android apps that disassembles samples, extracts properties via configurable pattern matching, and organizes output…
android-securityinformation-gatheringmalware-analysis+3
311
cryptax/droidlysisAutomated pre-analysis tool for Android apps that disassembles samples, extracts properties via configurable pattern matching, and organizes output…
 coffeeandsecurity/dakshscra
Framework-aware static code analysis tool for automated source code review with platform-specific rules, taint analysis, effort estimation, and…
 baiduxlab/sgxray
Automated reasoning tool based on the SMACK verifier that detects SGX enclave bugs from trusted boundary violations, including invalid pointer…
 trustedsec/ts_llmlib
Python library for local LLM-powered security analysis with Ghidra binary analysis, C/C++ vulnerability scanning, and MCP tool integration for…
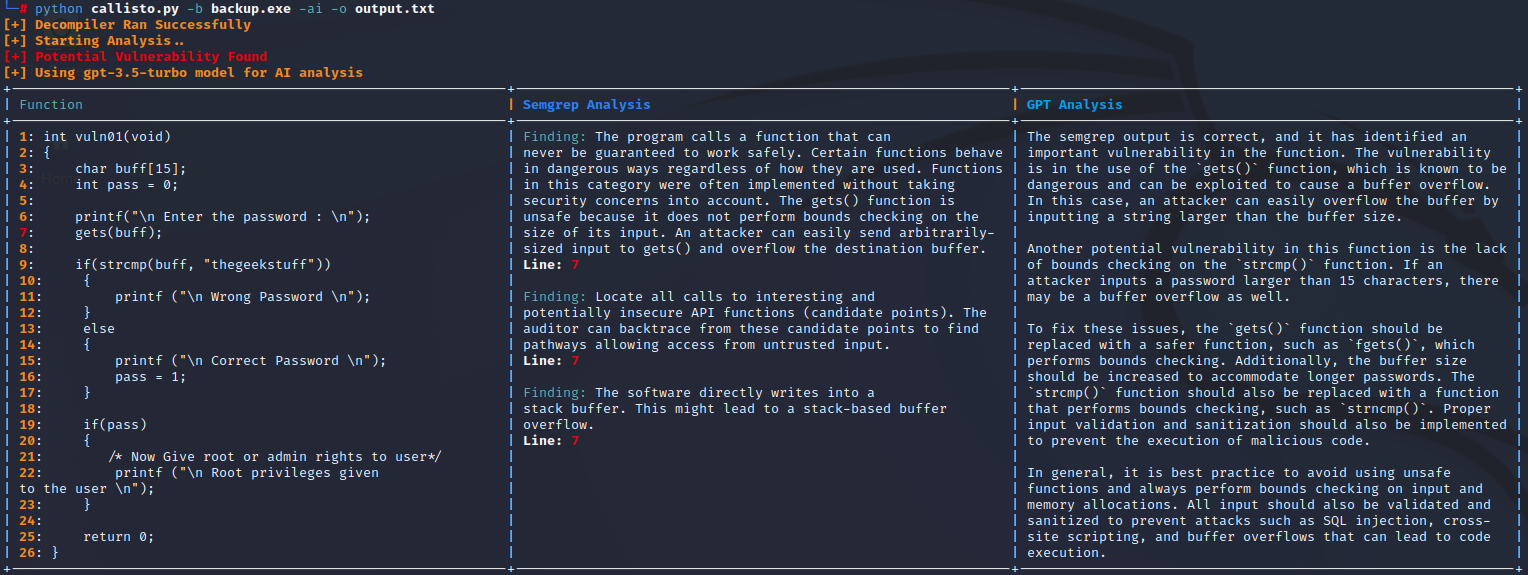 jetp1ane/callisto
Automated binary vulnerability analysis tool that decompiles executables via Ghidra, scans pseudo-C code with Semgrep, and validates findings using…
 iilegacyyii/exportdumper
A small tool I made to dump the export table of PE files. The primary use case was intended for use within DLL proxying.
 x86rc/unthemidator
An automated Themida / Code Virtualizer / WinLicense (v3.0-v4) unpacker and dump fixer tool
 cmu-sei/pharos
Automated static analysis tools for binary programs
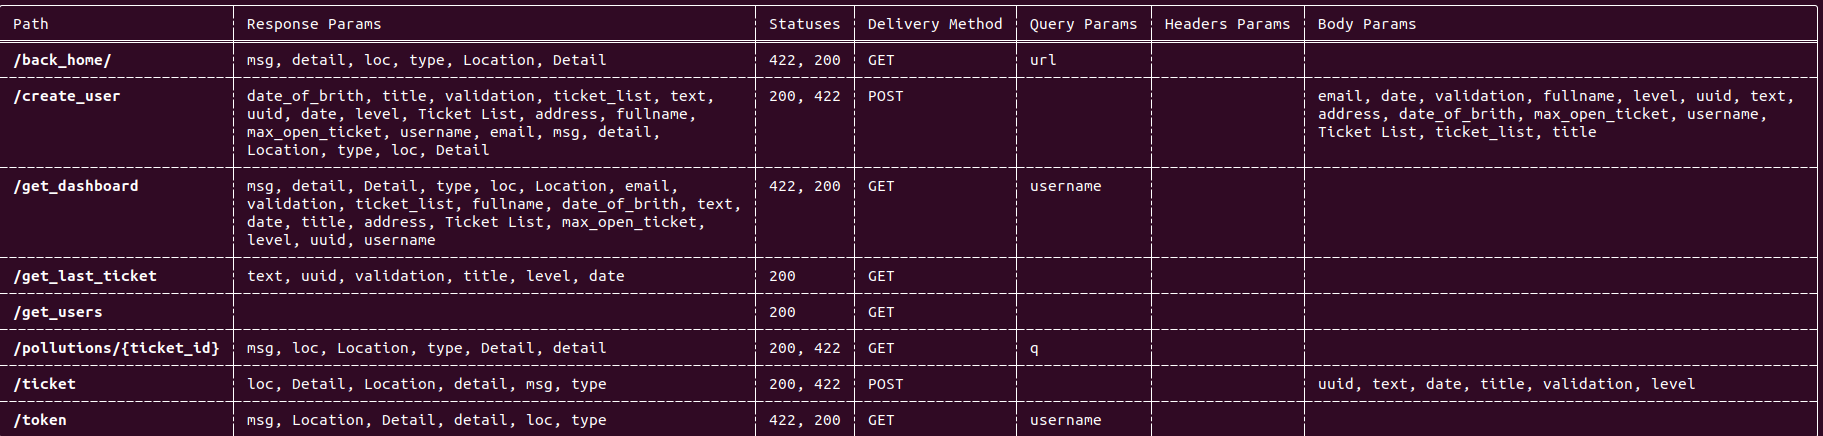 blst-security/cherrybomb
CLI tool that audits OpenAPI specifications, validates them against best practices, and runs automated security tests to detect vulnerabilities and…
 pr0me/xtride
N-gram-based type recovery tool for binaries, recovering structures and function signatures from decompiled code with high throughput and actionable…
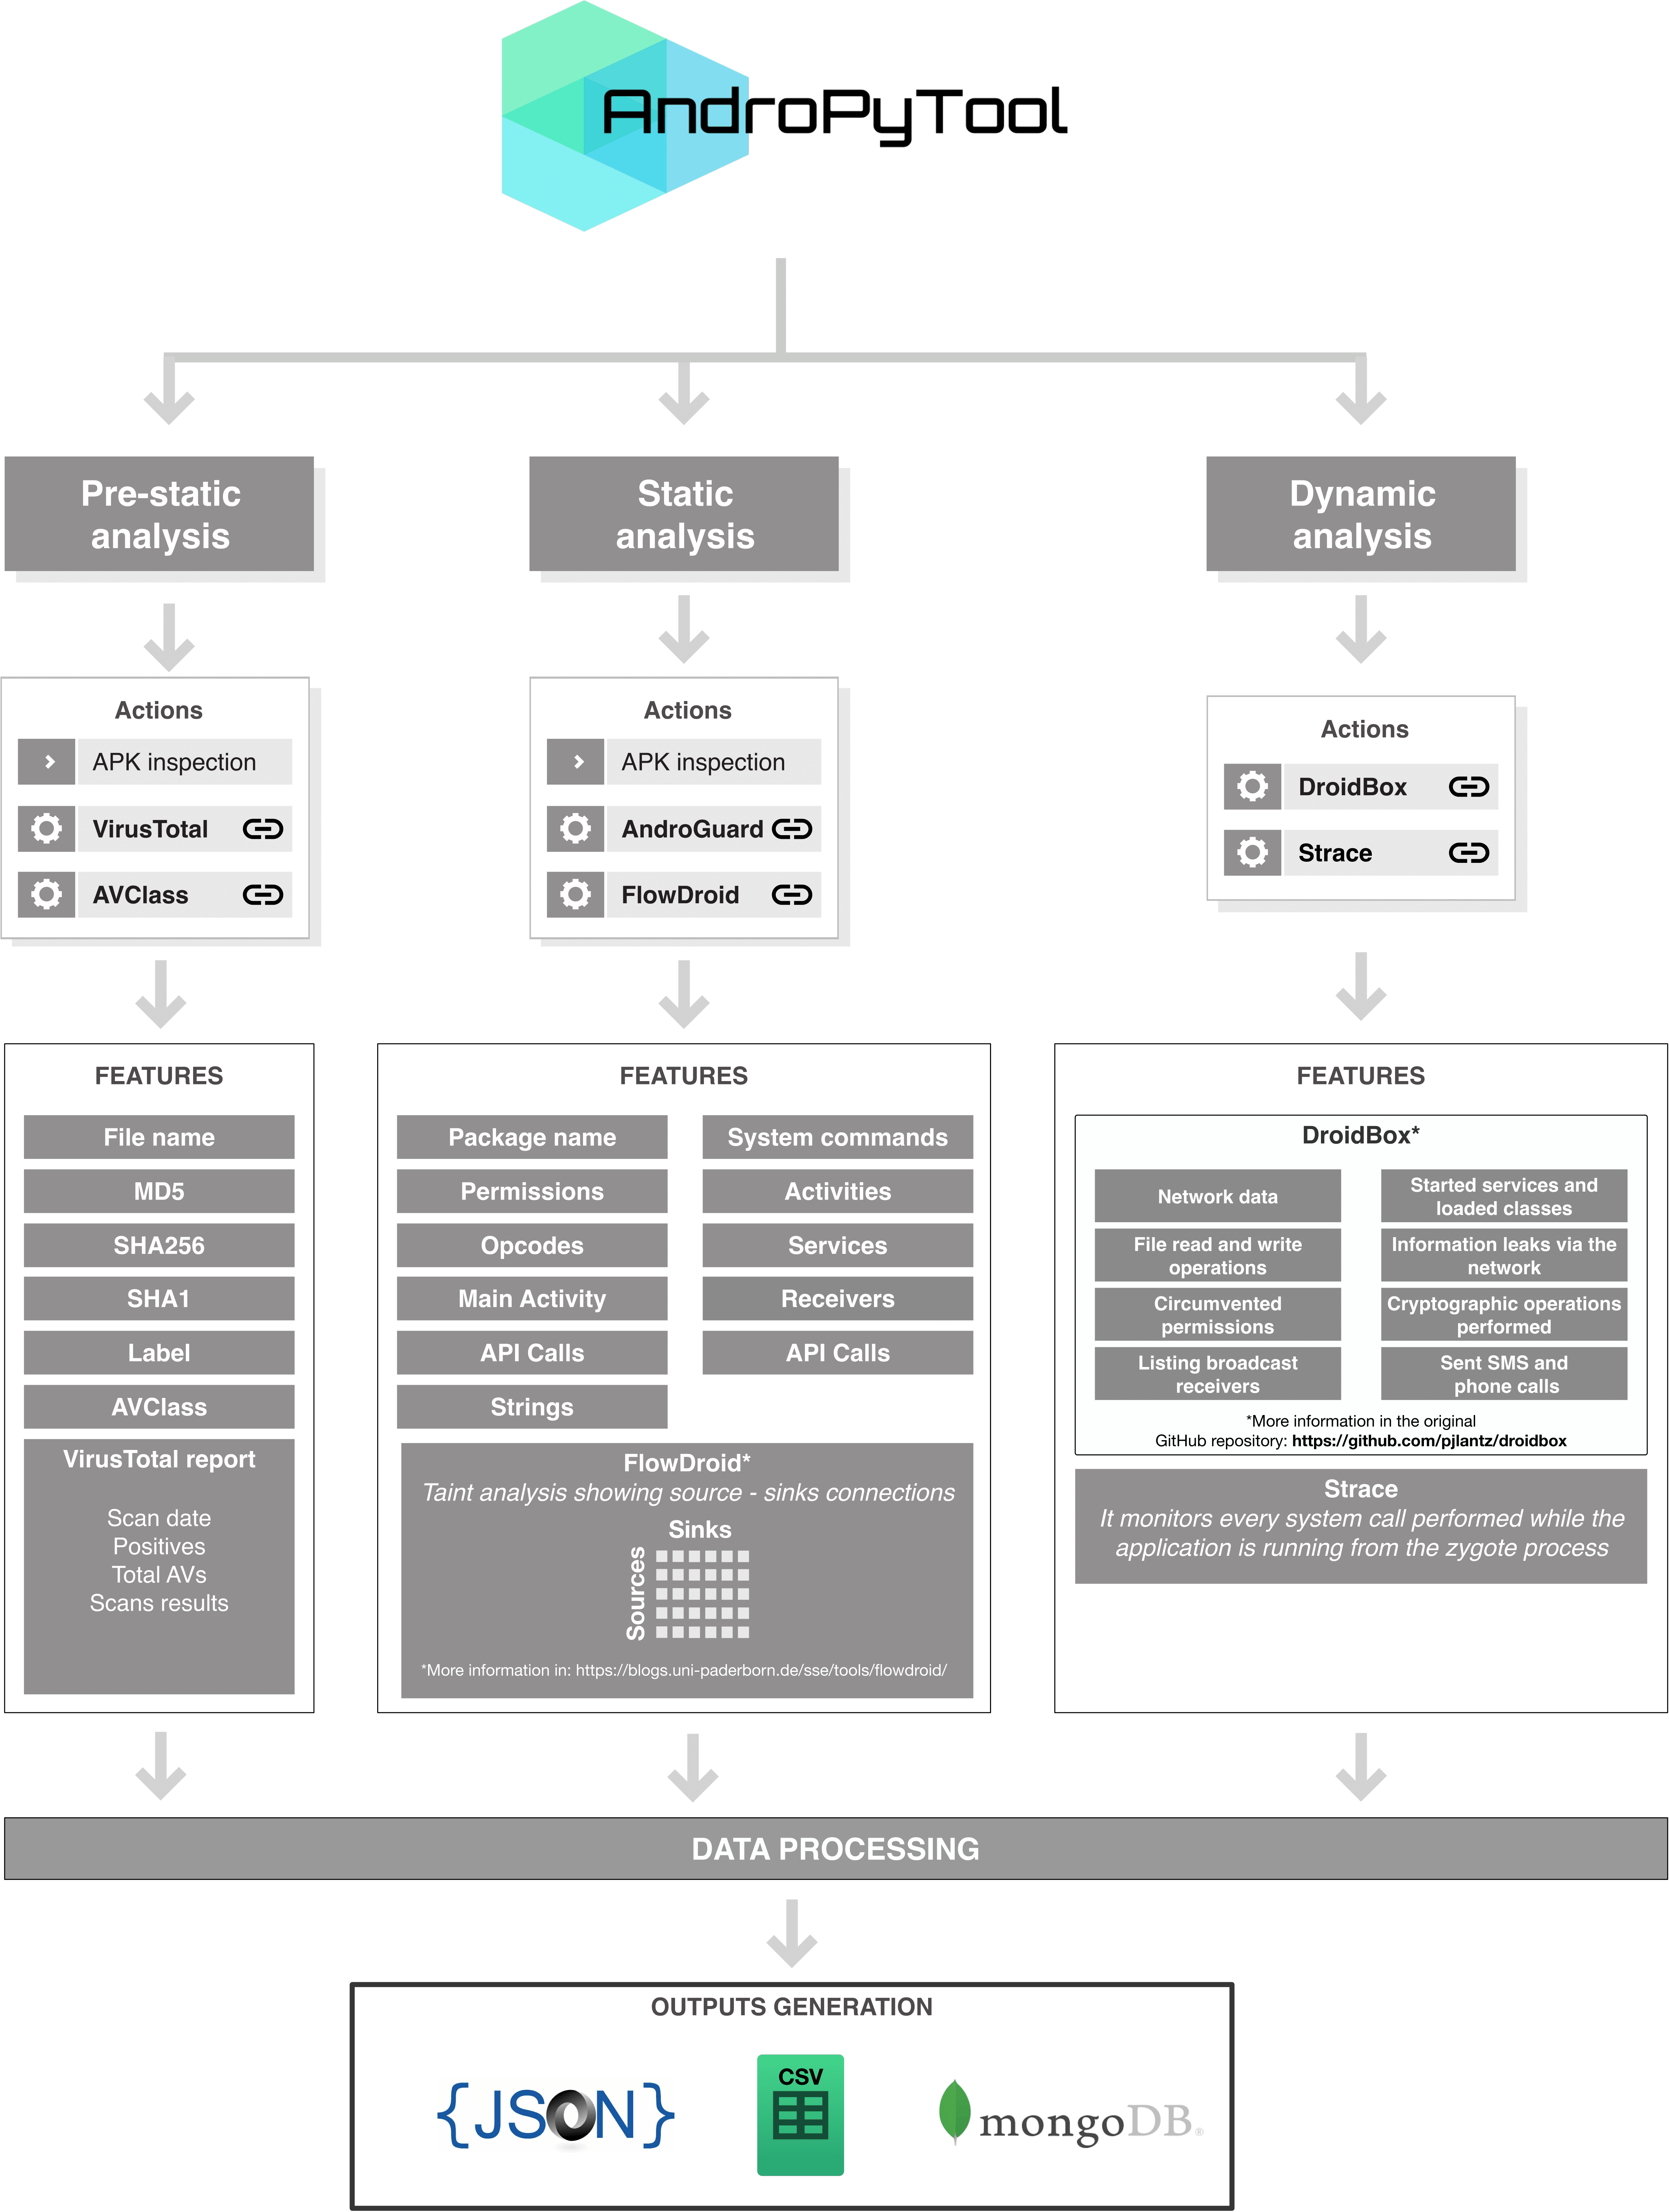 alexmyg/andropytool
A framework for automated extraction of static and dynamic features from Android applications
 mandiant/route-sixty-sink
Link sources to sinks in C# applications.
 spamscanner/spamscanner
Spam Scanner is a Node.js anti-spam, email filtering, and phishing prevention tool and service. Built for @ladjs, @forwardemail, @cabinjs, @breejs,…
 affolter-engineering/xssearch
Rust-based XSS scanner with context-aware payload selection, WAF detection and bypass, crawling, blind XSS callbacks, and static DOM sink analysis.
 ght657/work1-secure-api
HDU IS Work 1 - Secure REST API (Flask) with CI/CD (pytest + bandit + pip-audit) and CVE-2018-17246 analysis
 anchore/syft
CLI tool and library for generating a Software Bill of Materials from container images and filesystems
 anchore/grype
A vulnerability scanner for container images and filesystems