
ioctlance
 zeze-zeze/ioctlance
A tool that is used to hunt vulnerabilities in x64 WDM drivers
binary-analysisdynamic-analysis-sandboxingexploit-frameworks+4
4784 months ago
zeze-zeze/ioctlanceA tool that is used to hunt vulnerabilities in x64 WDM drivers
 gherardofiori/maliciousbrowserextensions
This Repository is created after my own research into malicious browser extensions, by brining the work of many others and news articles into one…
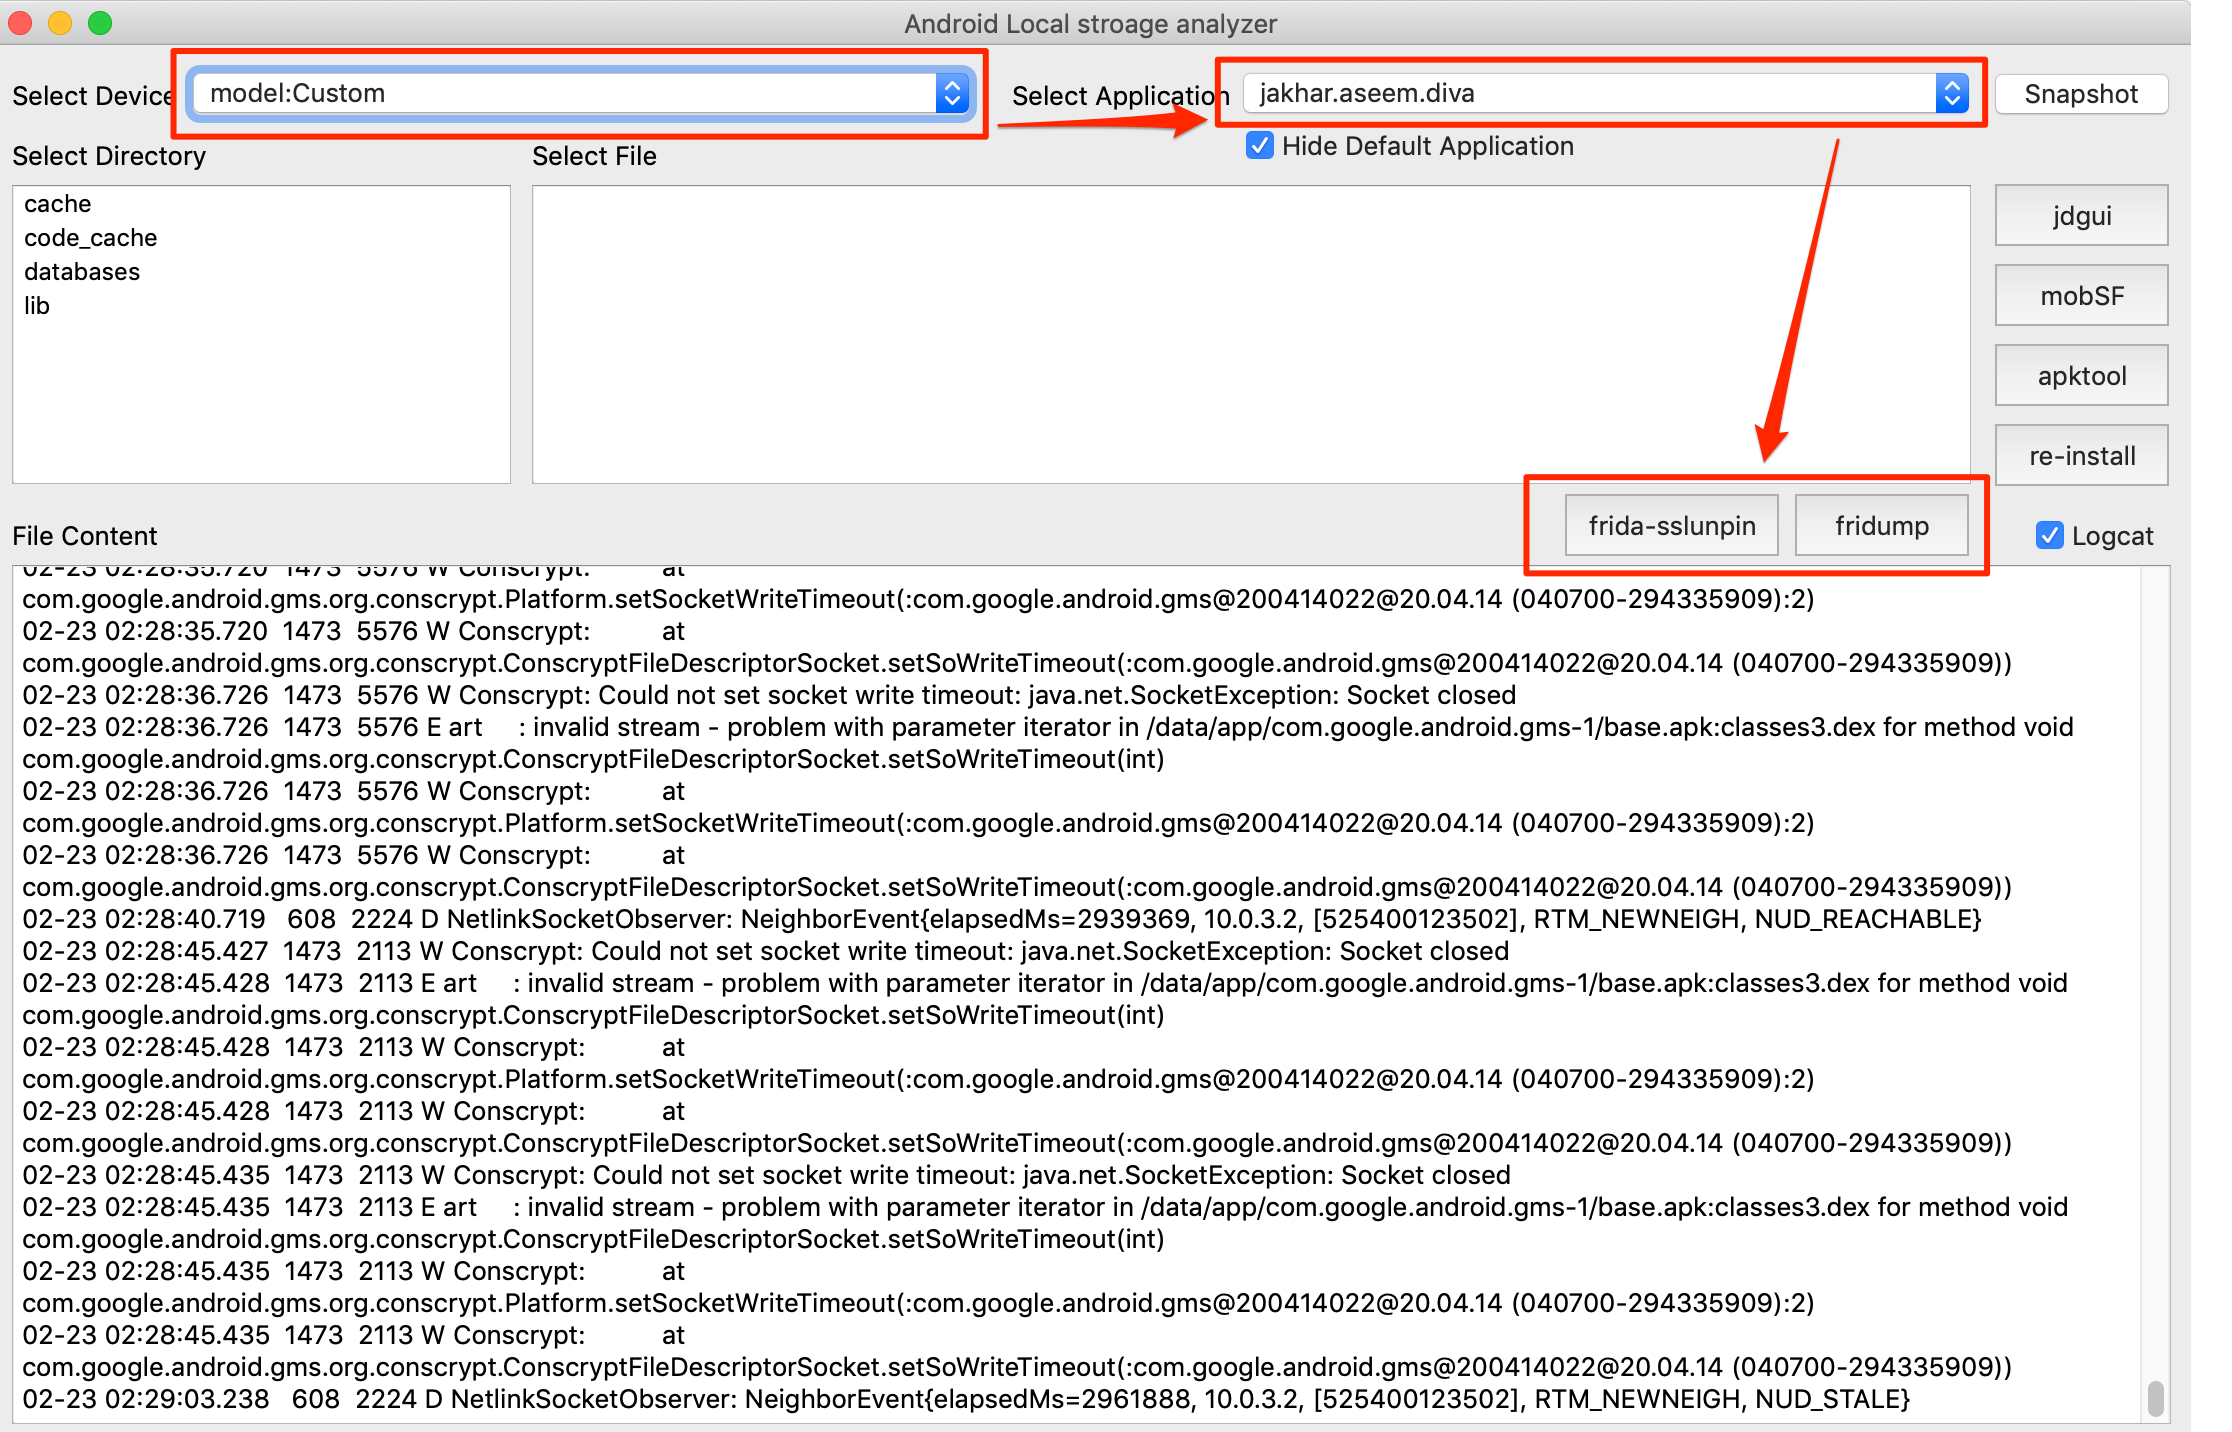 notsosecure/android_application_analyzer
The tool is used to analyze the content of the android application in local storage.
 stuxctf/mhf
Mobile Helper Framework (mhf) is a tool that automates the process of identifying the framework/technology used to create a mobile application.…
 0x11dfe/file-unpumper
Tool that can be used to trim useless things from a PE file such as the things a file pumper would add.
 gitlab-da/tutorials/security-and-governance/custom-scanner-integration/fern-pattern-scanner
Scans selected files for patterns stated in rules. This is used in order to find secrets you may have accidentally written to a file. This scanner is…
 maoabc/nmmp
dex-vm used to protect the android classes.dex file
 kevthehermit/ratdecoders
Python Decoders for Common Remote Access Trojans
 dissectmalware/xlmmacrodeobfuscator
Extract and Deobfuscate XLM macros (a.k.a Excel 4.0 Macros)
 lifting-bits/sleigh
CMake build of Ghidra's SLEIGH processor specification library, providing standalone disassembly and p-code lifting engines for reverse engineering…
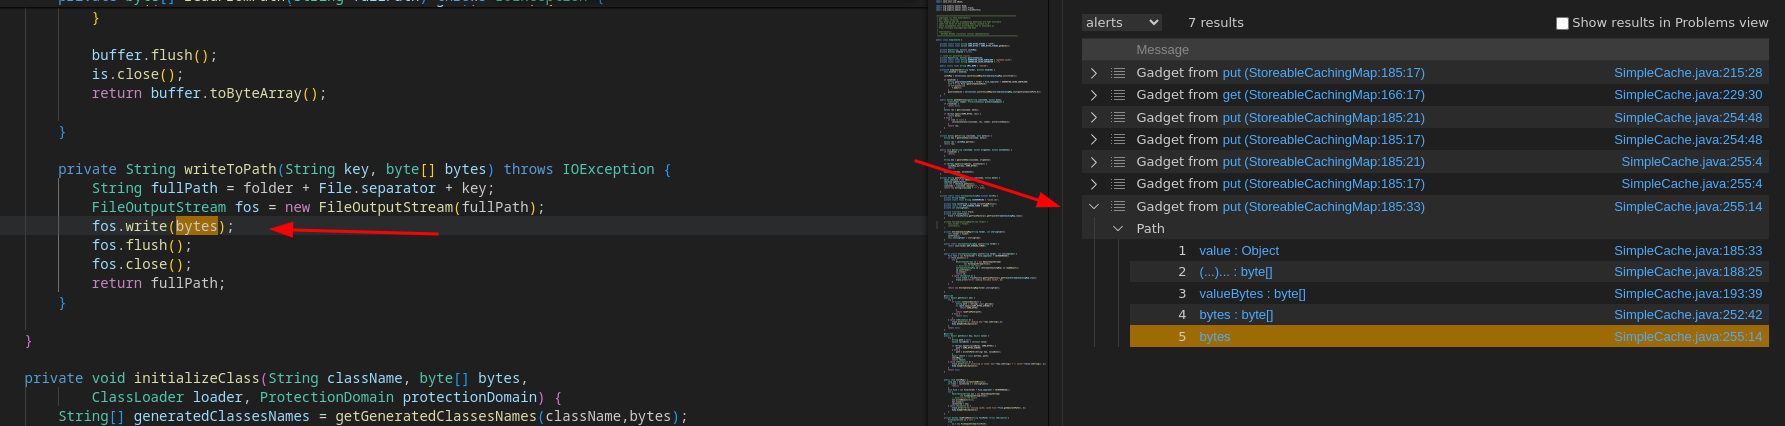 synacktiv/qlinspector
Finding Java/C# gadget chains with CodeQL
 neurosaki987/qvm-tool
Static analysis and structure recovery toolkit for ACE .qvm0-protected PE images
 hillu/local-log4j-vuln-scanner
[Moved to Codeberg] Simple local scanner for vulnerable log4j instances
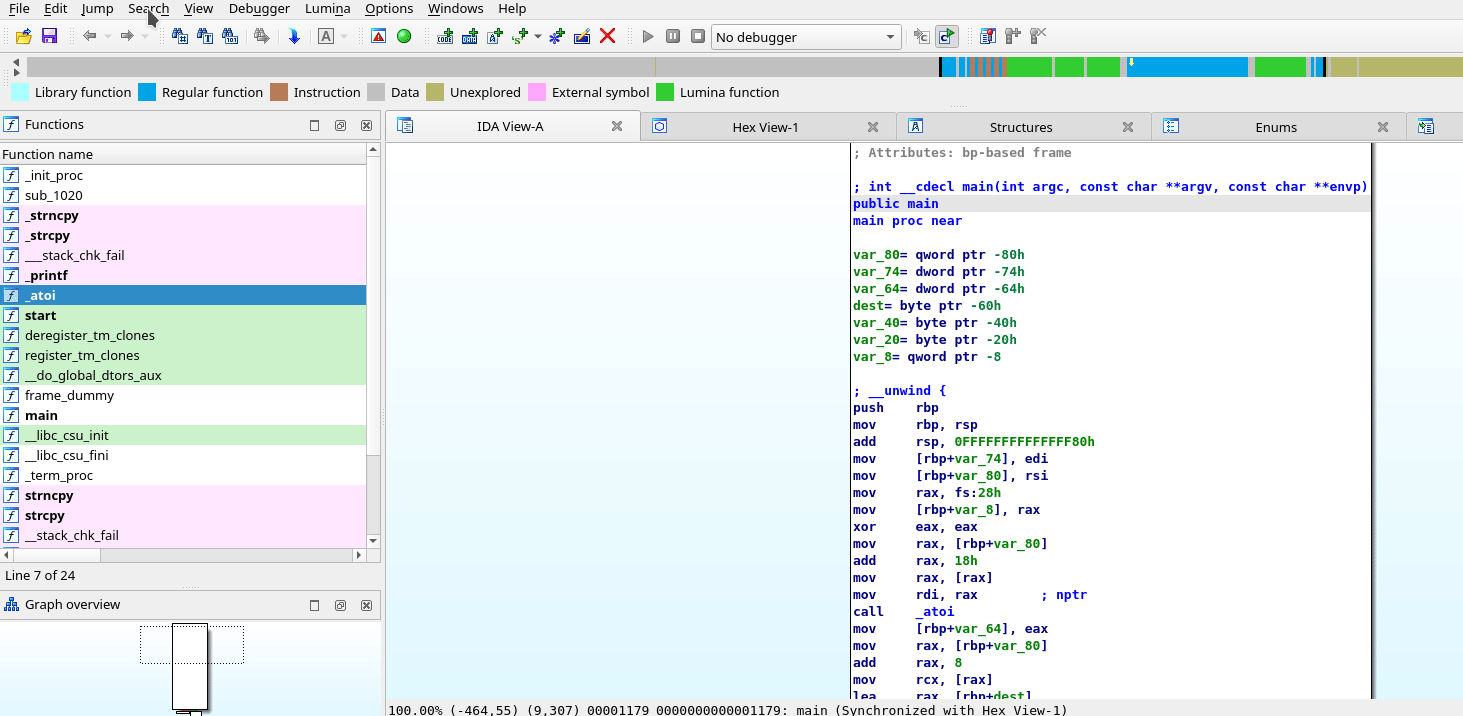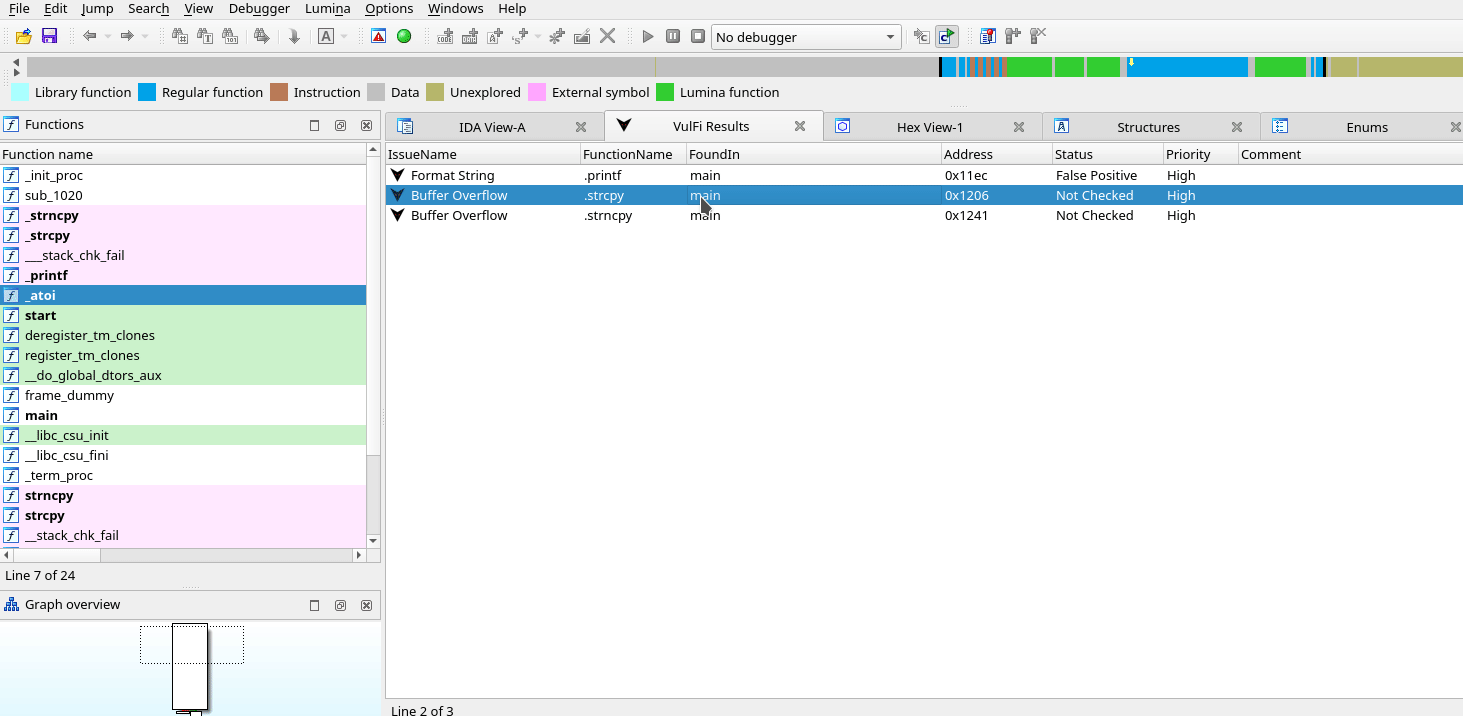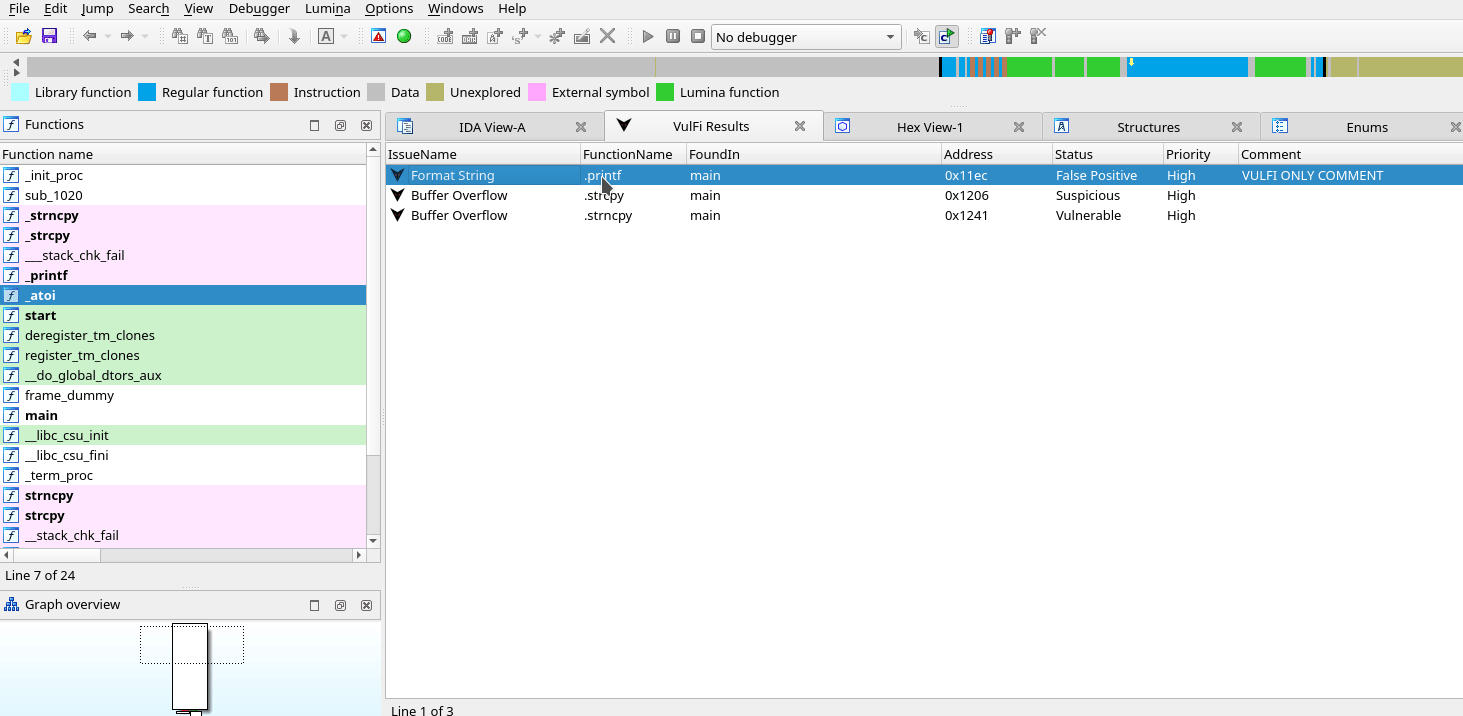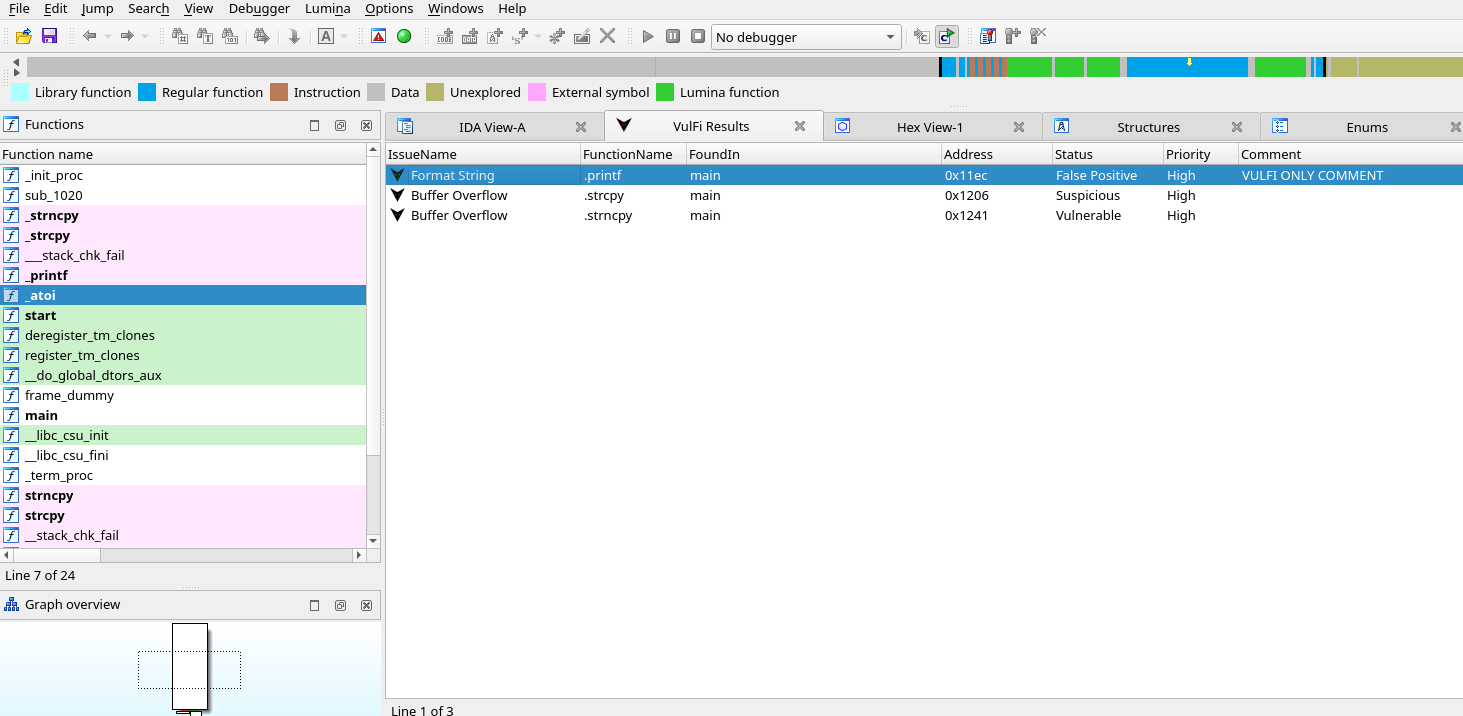 accenture/vulfi
IDA Pro plugin for query based searching within the binary useful mainly for vulnerability research.
 malgamy/yara_rules
Curated signature-rule collection for detecting and classifying malicious files via pattern matching, with CLI instructions for scanning files and…
 jetbrains/fernflower
Decompiler from Java bytecode to Java, used in IntelliJ IDEA.
 maweil/bidi_char_detector
Checks your files for existence of Unicode BIDI characters which can be misused for supply chain attacks. See CVE-2021-42574
 epicosy/xstream-1
Java library for XML serialization and deserialization, with a focus on CVE-2020-26217 exploitation. Enables converting Java objects to XML and back,…