React-Router-CVE-2025-61686-

Detailed analysis of CVE-2025-61686, a path traversal vulnerability in React Router's file session storage, including root cause, attack scenarios,…

Detailed analysis of CVE-2025-61686, a path traversal vulnerability in React Router's file session storage, including root cause, attack scenarios,…

A lightweight security auditor and sandbox for shell scripts. Oversight combines a Static Analysis engine (Rust) with Dynamic Enforcement (Linux…

AI Smart Contract Security Analysis and PoC Generation Framework

Trail of Bits Claude Code skills for security research, vulnerability detection, and audit workflows

A Rust CLI tool that recursively discovers Git repositories, captures state changes, generates diffs, extracts code elements with full snippets, and…

Fast, configurable secrets scanner for filesystems, git history, containers, and cloud sources, with Expr-based filtering, credential validation, and…

Security scanner auditing Claude Code environments for CVE-2026-21852 pre-trust execution, hook hijacking, and eBPF lockdown.

Autonomous white-hat security auditor for AI-driven code review, bug bounty research, exploit construction, and execution-grounded verification.

100% Free & Open Source • Privacy-First Security Scanning and AI Code Review CLI

Collection of Solidity snippets and Foundry scripts for smart contract security audits

Scan is a free & Open Source DevSecOps tool for performing static analysis based security testing of your applications and its dependencies. CI and…

A fast universal code security scanner, written in Rust. Batteries included: supports 14 languages, TUI for triage, secrets, post-quantum audits,…

A multi-platform CI/CD vulnerability detection and attack automation tool for identifying security weaknesses in pipeline configurations.

Find credentials and secret with 170+ rules covering across source code, Web URL, and CI/CD, verifies them against vendor APIs, and generates SARIF,…

End-to-end security audit framework for LLM agents: static AST and taint modeling, attack synthesis, Docker sandbox replay, and deterministic verdict…

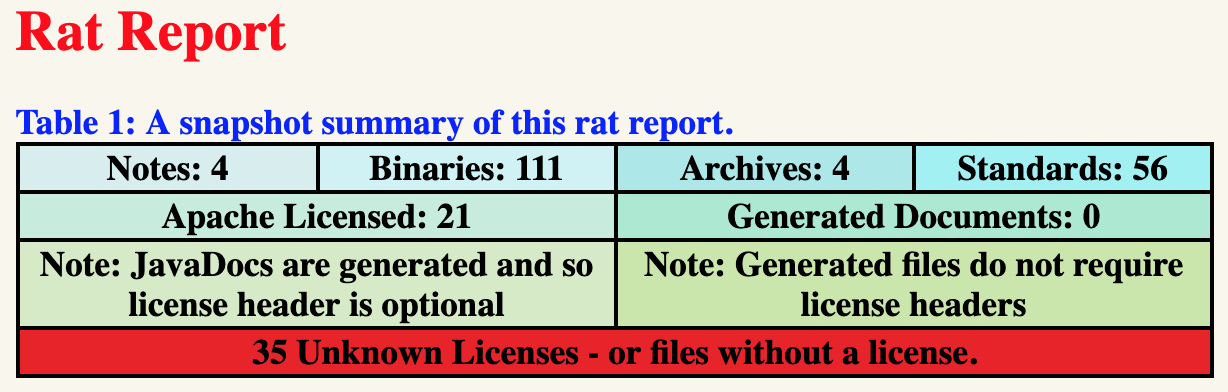
Apache RAT (Release Audit Tool) Gradle Plugin

Rule-based linter for OpenSSH client config files that detects duplicate hosts, missing identity files, weak algorithms, wildcard ordering issues,…

Cross-check the views of your attack surface and find the endpoints that cannot corroborate each other.