
brakeman
 presidentbeef/brakeman
A static analysis security vulnerability scanner for Ruby on Rails applications
code-analysisdevsecopsstatic-analysis+2
7.3k20 days ago
presidentbeef/brakemanA static analysis security vulnerability scanner for Ruby on Rails applications
 microcosm-cc/bluemonday
bluemonday: a fast golang HTML sanitizer (inspired by the OWASP Java HTML Sanitizer) to scrub user generated content of XSS
 c2sp/c2sp
Community Cryptography Specification Project
 corgea/sighthound
Tree-sitter based static vulnerability scanner with pattern matching and taint-flow analysis for multi-language source code. Outputs findings as…
 nstarke/egodeath
A JavaScript Obfuscator based on Cryptographic Indistinguishability Obfuscation techniques
 jstrosch/subparse
Modular malware analysis artifact collection and correlation framework
 bogdanticu88/threatmap
IaC threat modeler with STRIDE, MITRE ATT&CK, and PASTA frameworks. REST API, GraphQL, and Docker support for Terraform, CloudFormation, and…
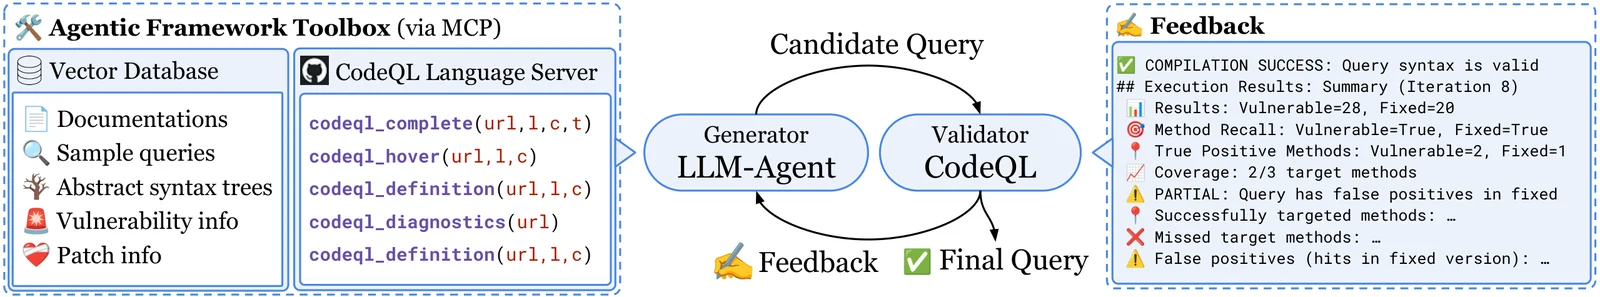 neuralprogram/qlcoder
Agentic Framework for Synthesizing CodeQL Queries
 gwroblew/detectxsslib
C++ library for detecting cross-site scripting (XSS) vulnerabilities in URLs through pattern analysis, with server modules and command-line tools for…
 wspr-ncsu/mininode
Static analysis CLI tool that reduces Node.js application attack surface by constructing dependency graphs and removing unused modules and functions…
 zihxs/check-react-rce-cve-2025-55182
Security scanner to detect CVE-2025-55182 & CVE-2025-66478 vulnerabilities in React Server Components (RSC) projects
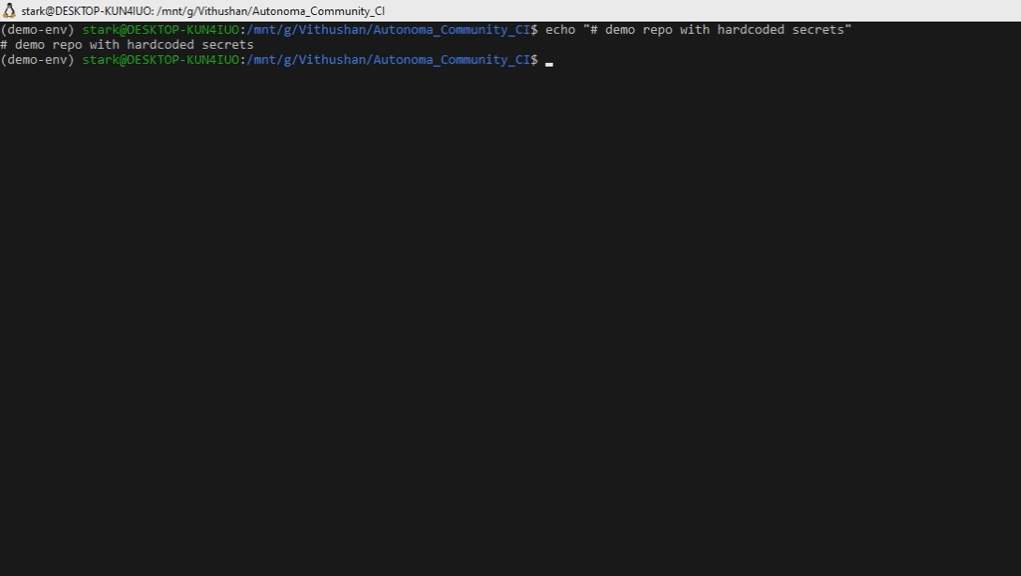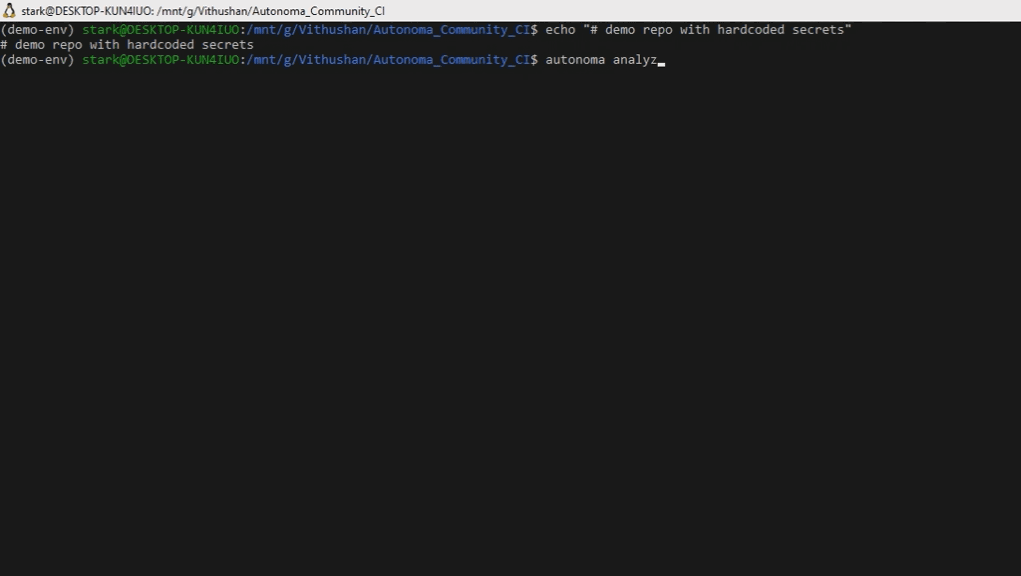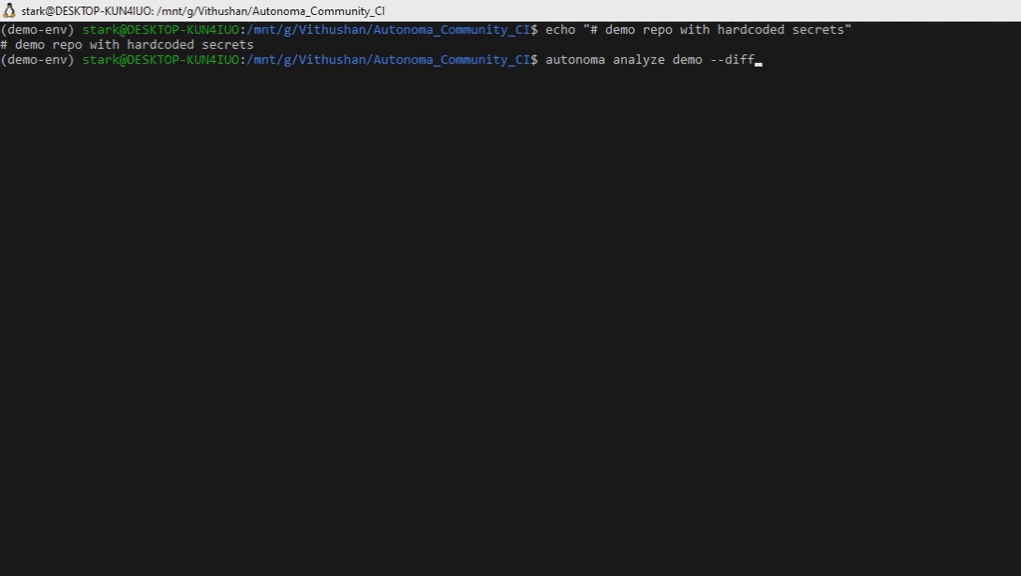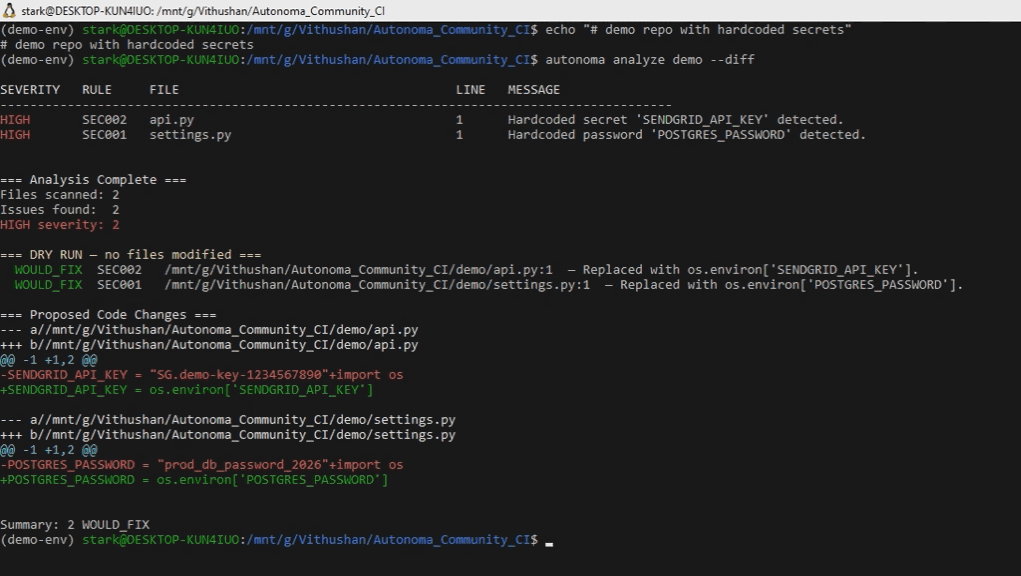 vihaaninnovations/autonoma
Detects and auto-fixes hardcoded secrets in Python repos — refuses when the fix could break your code
 filipsedivy/cve-2020-15227
Python-based checker for CVE-2020-15227 that tests Nette applications for remote code execution vulnerabilities via file_put_contents and shell_exec…
 gmh5225/evmbench-certora-agent-harness
Iterative agent harness that uses LLMs and Certora Prover to generate and refine smart-contract CVL specs, feeding verifier output back until success…
 cucumberanorsncompany/sealsecurityassignment
Researching on the vulnrability CVE-2023-26136
 morrisel/cve-2023-26136
This repository contains a solution for the CVE-2023-26136 vulnerability.
 samaujs/cve-2011-1475
Check with Maven on CVE-2011-1475