

FIASSE
 owasp/fiasse
A Framework for Integrating Application Security into Software Engineering (FIASSE) using the Securable Software Engineering Model (SSEM)
code-analysiscurated-resourcesdevsecops+7
143 days ago
owasp/fiasseA Framework for Integrating Application Security into Software Engineering (FIASSE) using the Securable Software Engineering Model (SSEM)
 otsmane-ahmed/ci-supplychain-guard
Static analysis tool that detects malicious dependencies in CI/CD pipelines using pattern matching and AST analysis, with a traffic-light risk…
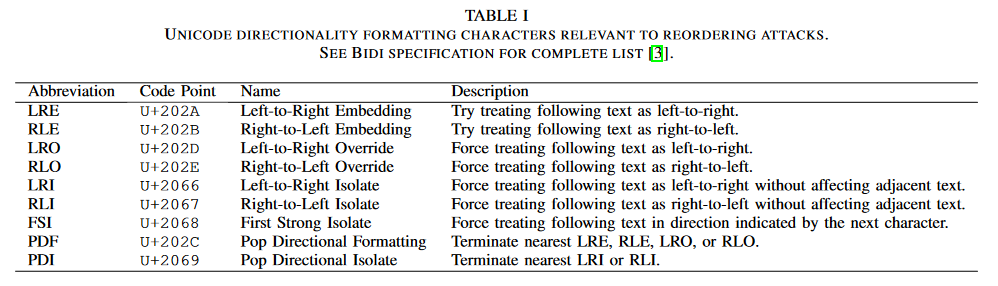 simplylu/cve-2021-42574
Generate malicious files using recently published bidi-attack (CVE-2021-42574)
 abraxas/sqlite-fj-using-auth
SQLite 3.53.4 - High - Local - Privilege leftover - FULL JOIN USING skips sqlite3AuthRead
 teycir/honeypotscan
Free honeypot token scanner for Ethereum, Polygon & Arbitrum. Detect scam tokens before you buy. Instant analysis of smart contracts using 13…
 ejfkdev/jd
Go CLI that deobfuscates javascript-obfuscator (obfuscator.io) output and unminifies JavaScript using AST transforms, static decoding, and a goja…
 mo200909/office-malware-forensics-lab-remnux-static-analysis
Static analysis of 2 malicious Office documents on REMnux using oletools; identified CVE-2017-11882 and obfuscated macros.
 mkway/cve-2025-57833
We've set up an environment to test CVE-2025-57833. This environment was built using AI, so it's subject to ongoing modification.
 nccgroup/formal_np1sec
Formalizing np1sec using Tamarin and other FM (see https://github.com/equalitie/np1sec)
 hohn/codeql-sample-polkit
All stages of exploring the polkit CVE-2021-4034 using codeql
 atlassian/bitbucket-iac-scan
Scans Infrastructure as Code files for security misconfigurations and vulnerabilities using KICS, with Bitbucket Code Insights reporting.
 shoucheng3/jeremylong__dependencycheck_cve-2018-12036_3-1-2
Software composition analysis tool that detects publicly disclosed vulnerabilities in project dependencies using CPE matching, generating detailed…
 pierdipi/unicode-control-characters-action
A GitHub Action to find Unicode control characters using the Red Hat diagnostic tool https://access.redhat.com/security/vulnerabilities/RHSB-2021-007…
 blackvectorops/semantic_firewall
Generate deterministic semantic fingerprints for Go functions. Detect xz-style backdoors and verify semantic equivalence using Static Single…
 eliavila10/win32_hash
Password hashing and verification library for Windows, written in Ada/SPARK using the Windows CNG API (bcrypt) and proved with GNATprove.
 aipeacs/sc3010-computer-security
Using Struts2 and PowerShell to recreate CVE-2017-5638 OGNL Injection vulnerability.
 monnappa22/limon
Limon is a sandbox developed as a research project written in python, which automatically collects, analyzes, and reports on the run time indicators…
 lycis/cawdog
CAWODOG is a proof-of-concept project demonstrating how to protect Python-based AI models deployed on offline industrial machines. Across three…