

pdfresurrect
 enferex/pdfresurrect
Analyze and help extract older "hidden" versions of a pdf from the current pdf.
data-recoverydigital-forensicsstatic-analysis
enferex/pdfresurrectAnalyze and help extract older "hidden" versions of a pdf from the current pdf.
 kevinbackhouse/djvulibre-poc-cve-2025-53367
Proof-of-concept exploit for CVE-2025-53367, a vulnerability in the DjVuLibre library. Demonstrates exploitation of a memory corruption bug in DjVu…
 patrickdw123/paranoidf
ParanoiDF - PDF Analysis Suite based on PeePDF by Jose Miguel Esparza (http://peepdf.eternal-todo.com/). Tools added: Password cracking, redaction…
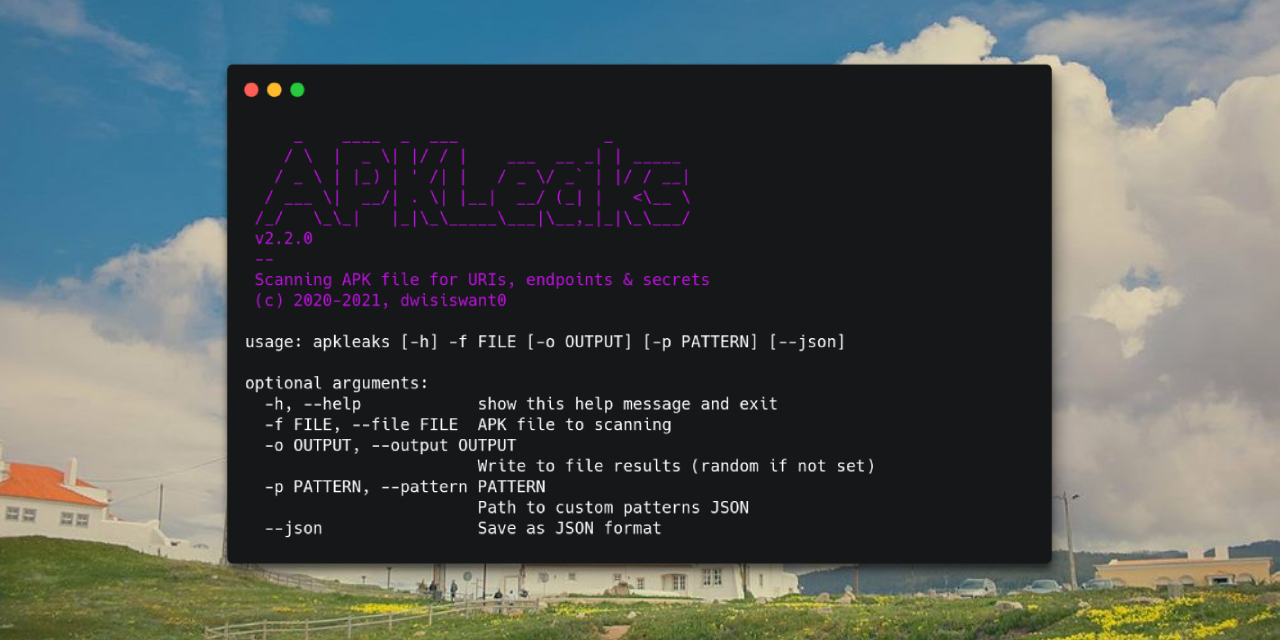 dwisiswant0/apkleaks
Scanning APK file for URIs, endpoints & secrets.
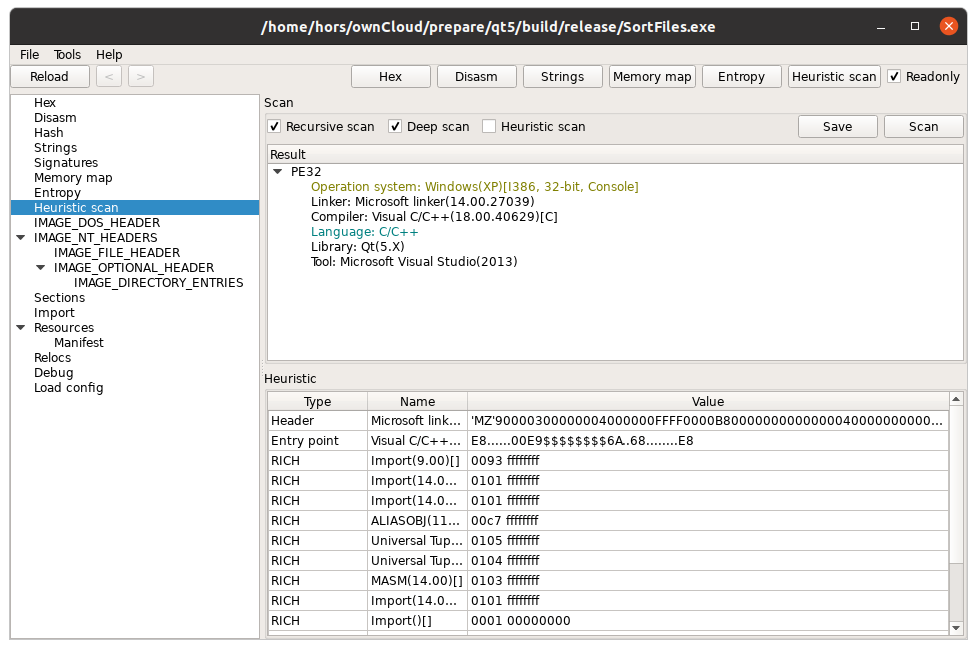 horsicq/xpeviewer
PE file viewer/editor for Windows, Linux and MacOS.
 cmu-sei/kaiju
CERT Kaiju is a binary analysis framework extension for the Ghidra software reverse engineering suite. This repository is a "mirror" -- please file…
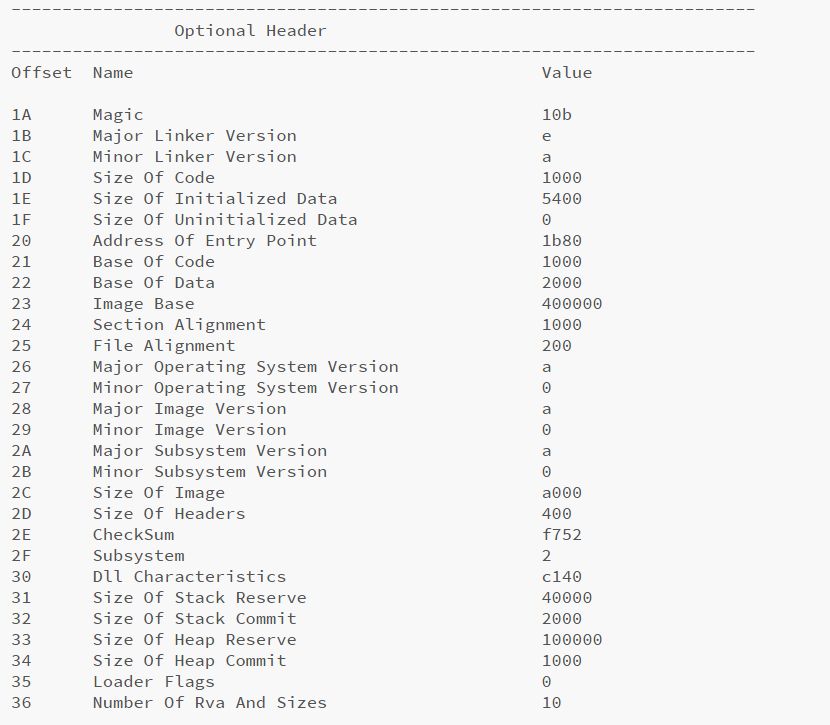 blacknbunny/peanalyzer
Advanced Portable Executable File Analyzer And Disassembler 32 & 64 Bit
 crowdstrike/xwf-yara-scanner
Native YARA scanner X-Tension for X-Ways Forensics, enabling in-snapshot file scanning with multi-threaded RVS support, report table output, and no…
 jhuapl/codecut
A Ghidra plugin for locating object file boundaries.
 firelock-ai/kin
Semantic graph-based version control for AI-written code. Tracks entities and relations instead of file diffs, enabling blast radius analysis, shadow…
 trou/cpu_rec_rs
Determine which CPU architecture is used in a binary file.
 bytespulse-oe/wp2shell-hestia-scanner
Read-only WordPress security scanner for HestiaCP servers. Detects wp2shell compromise indicators (CVE-2026-63030 / CVE-2026-60137) across all hosted…
 trerb/ai-ide-config-guard
Scan a repo for AI-IDE config files that can trigger RCE via Claude Code hooks, Cursor rules, MCP auto-registration. Detects CVE-2025-59536,…
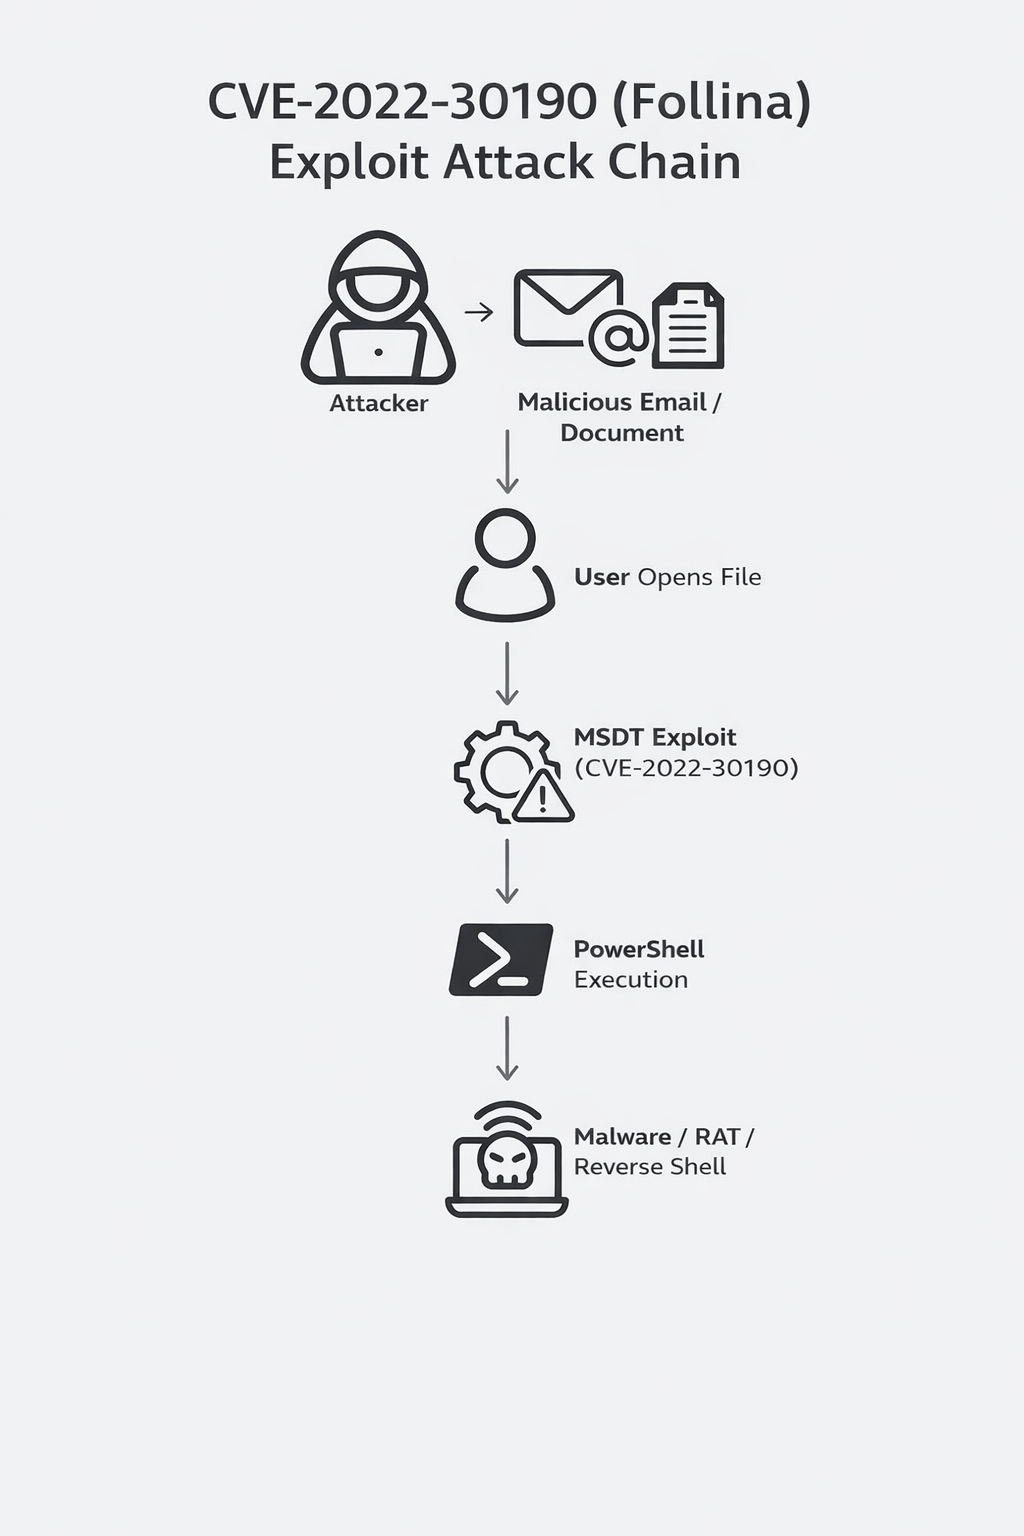 nimesh895/malware-analysis-follina-cve-2022-30190
Step-by-step static malware analysis of a Follina (CVE-2022-30190) exploit document, covering file extraction, VirusTotal correlation, MITRE ATT&CK…
 kai-one001/react-router-cve-2025-61686-
Detailed analysis of CVE-2025-61686, a path traversal vulnerability in React Router's file session storage, including root cause, attack scenarios,…
 svdwi/bluebox
Open-source threat intelligence platform for malware and observable analysis. Enriches IPs, domains, URLs, and hashes with external sources, performs…
 quarkslab/quokka
Quokka: A Fast and Accurate Binary Exporter