YaraVM
 milankovo/yaravm
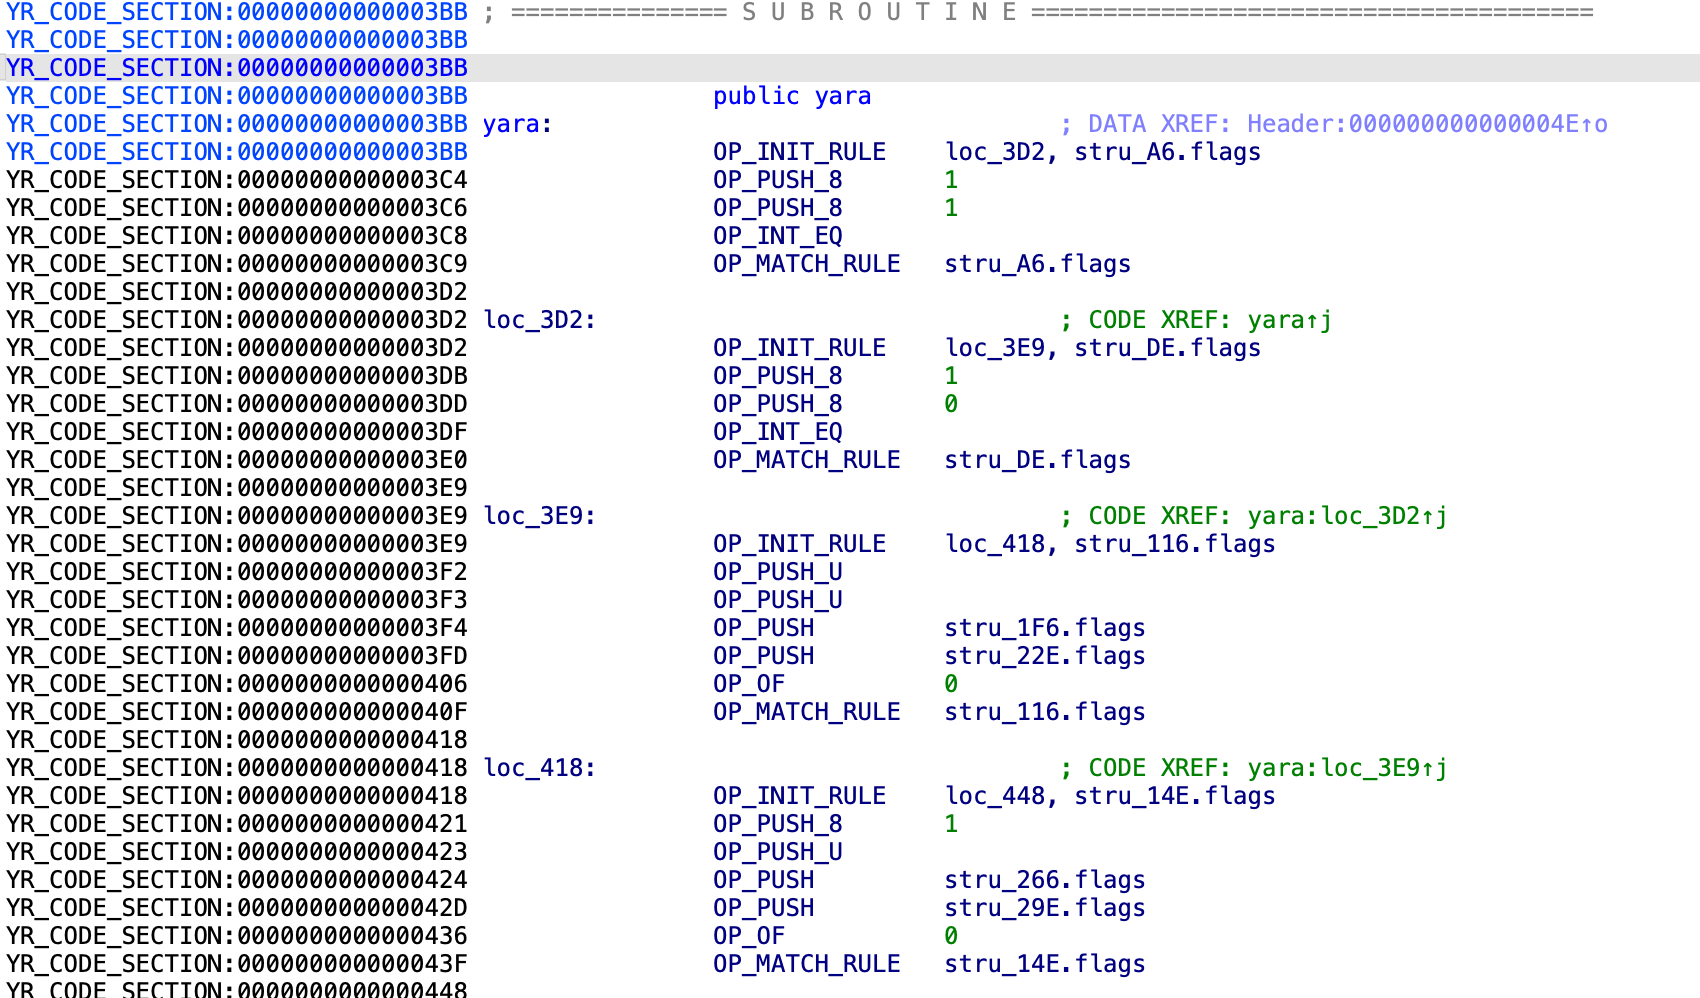
This repository contains an IDA processor for loading and disassembling compiled yara rules.
binary-analysisdebuggersmalware-analysis+2
53
milankovo/yaravmThis repository contains an IDA processor for loading and disassembling compiled yara rules.
 deepquantum/dconstruct
A disassembler & experimental decompiler for TLOU2 DC Scripts.
 otsmane-ahmed/ci-supplychain-guard
Static analysis tool that detects malicious dependencies in CI/CD pipelines using pattern matching and AST analysis, with a traffic-light risk…
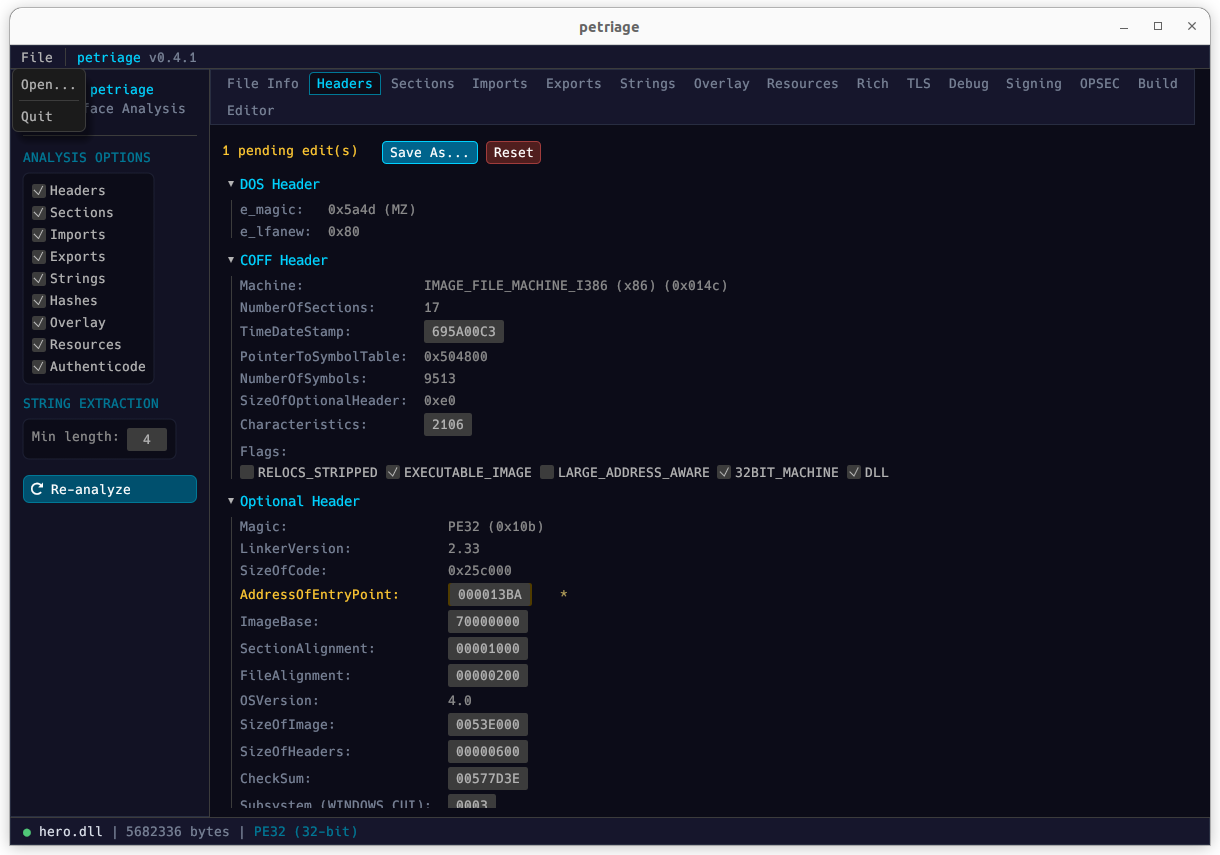 uky007/petriage
PETriage: A symbol-unified PE file reader for triage, built for multi-platform and multi-interface use.
 forentfraps/pe-signgen
Universal signature generation for any system function from all Windows Builds using Winbindex
 abhishek2512mishra/claude-code-security-audit
Security scanner auditing Claude Code environments for CVE-2026-21852 pre-trust execution, hook hijacking, and eBPF lockdown.
 cyb3rmx/qu1cksc0pe
All-in-One malware analysis tool.
 cmu-sei/pharos
Automated static analysis tools for binary programs
 bishopfox/jsluice
Extract URLs, paths, secrets, and other interesting bits from JavaScript
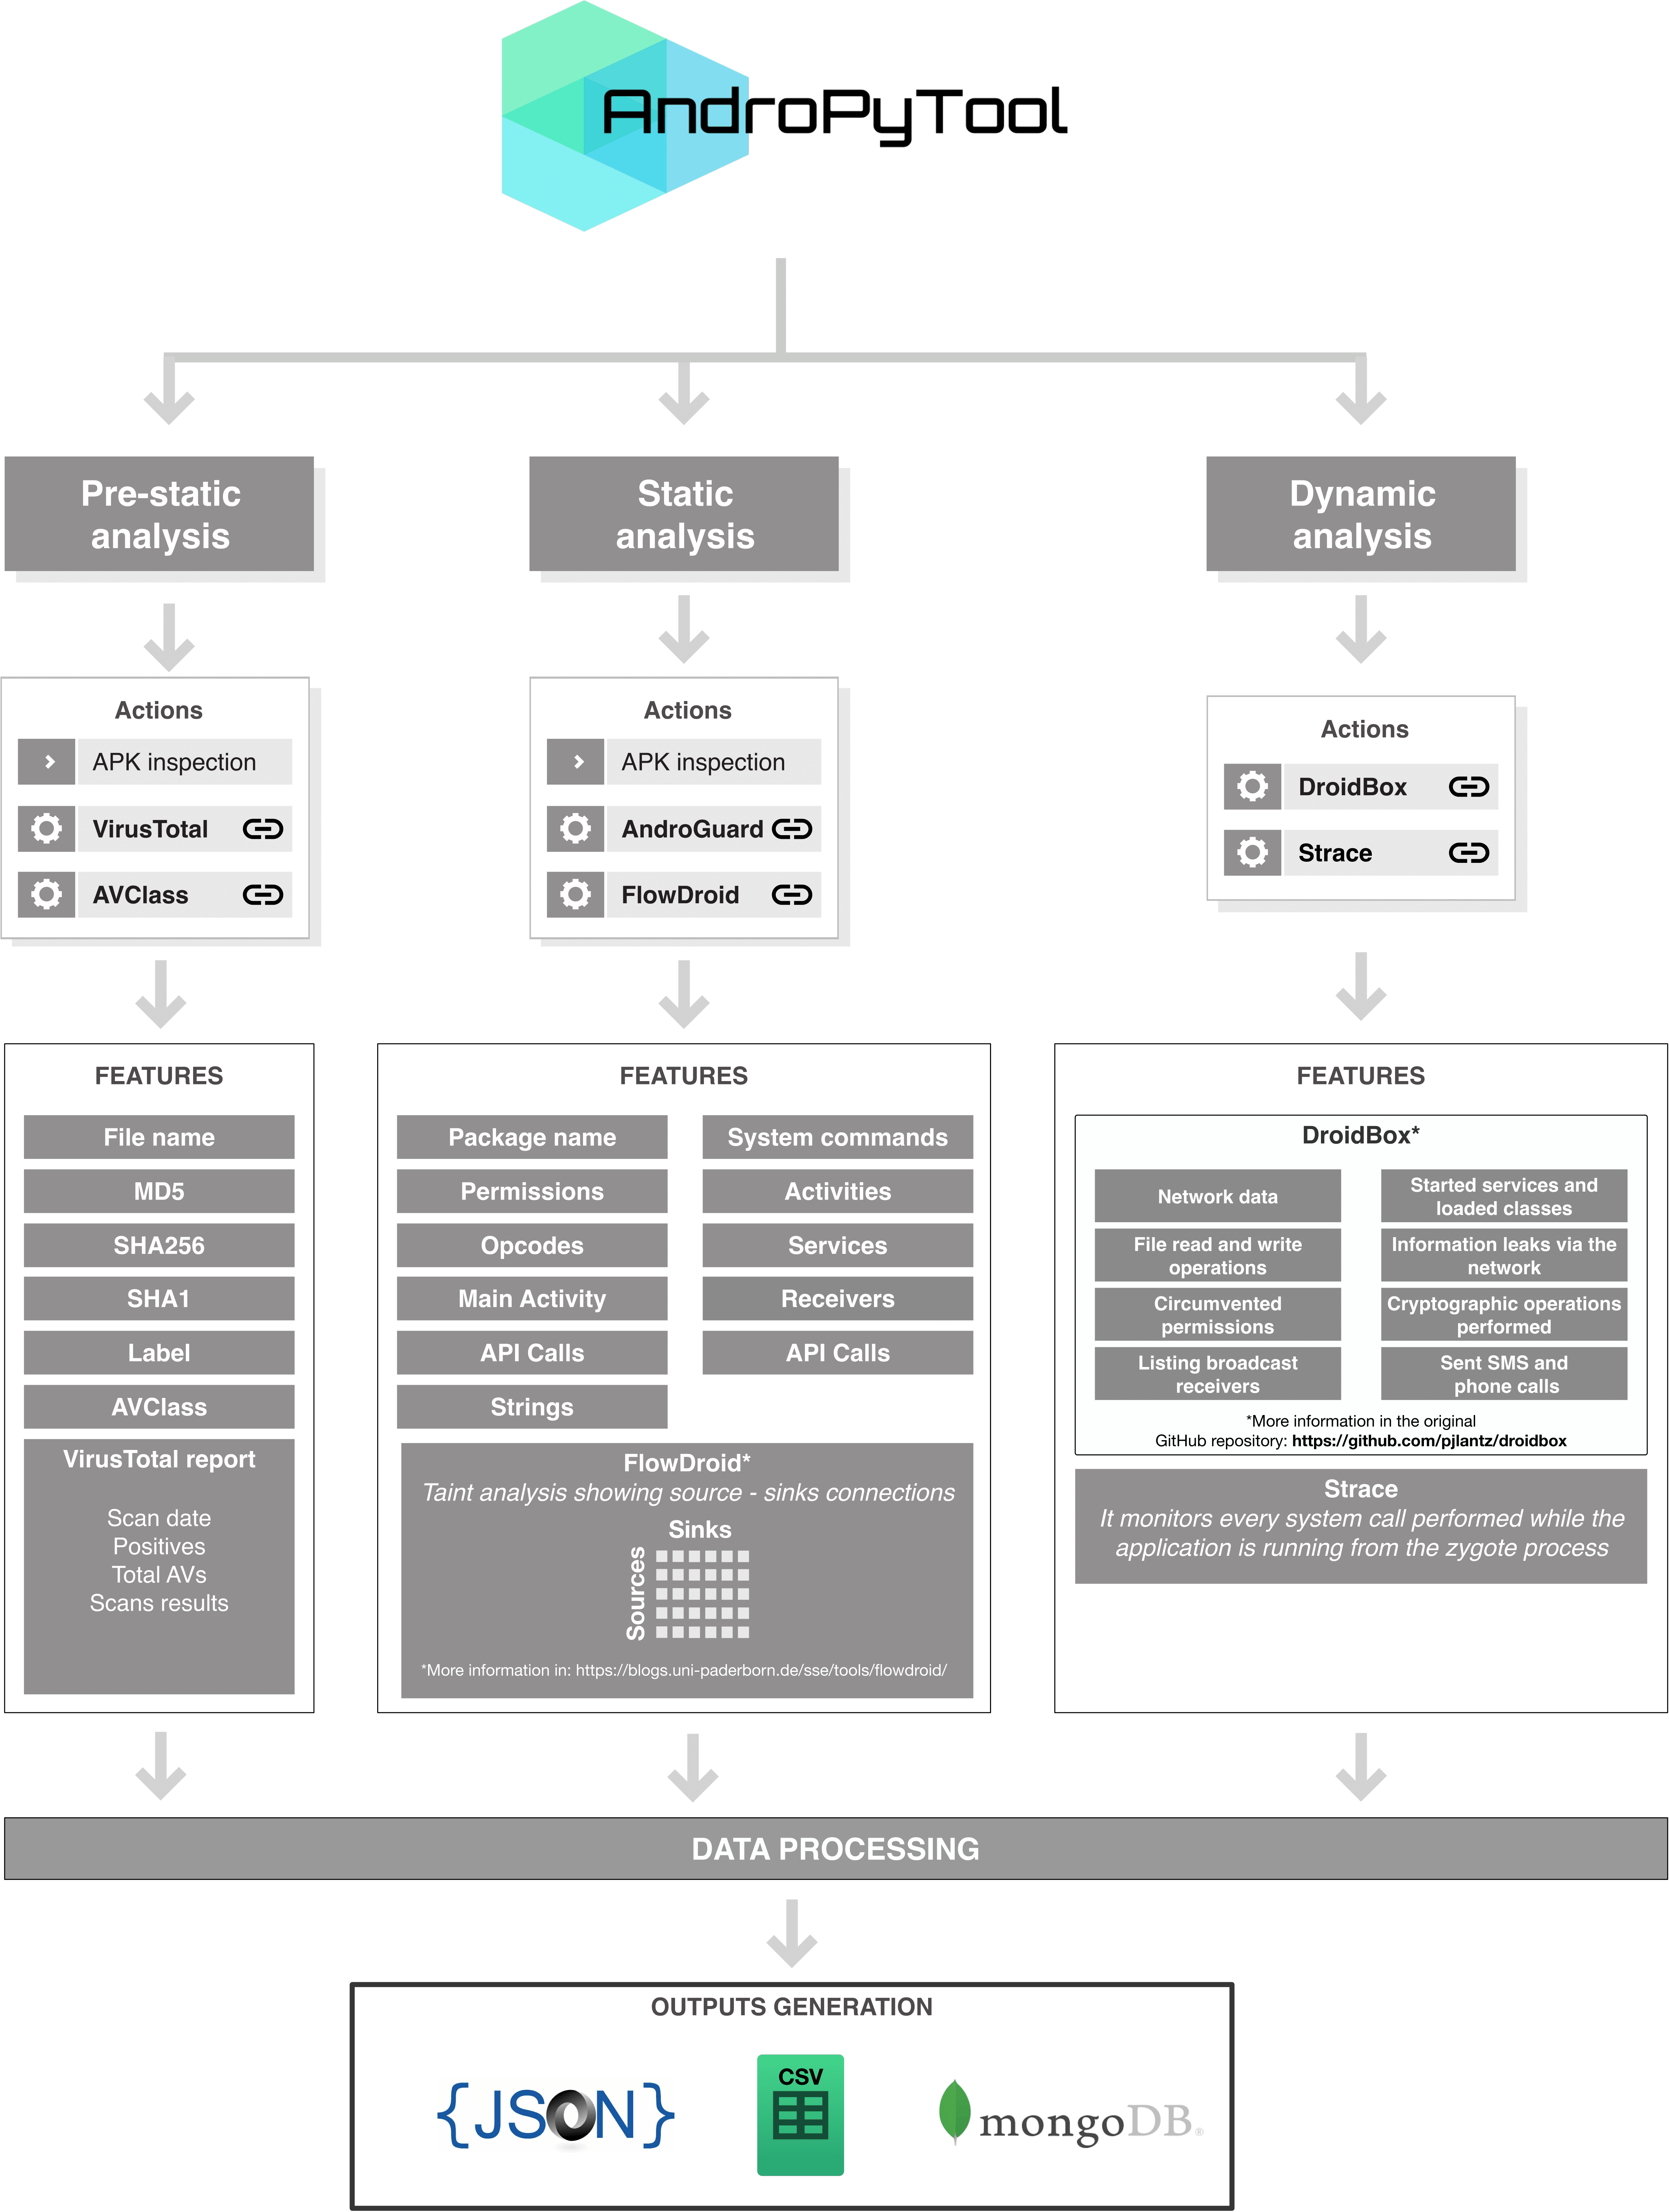 alexmyg/andropytool
A framework for automated extraction of static and dynamic features from Android applications
 dkhuuthe/madlira
Malware detection using learning and information retrieval for Android
 coinbase/salus
We would like to request that all contributors please clone a *fresh copy* of this repository since the September 21st maintenance.
 xoreaxeaxeax/hexcymatix
Visualizes repeated byte sequences in binary files to reveal hidden structure, supporting reverse engineering and pattern discovery without…
 gradiant/faro
FARO - Document Sensitivity Detector
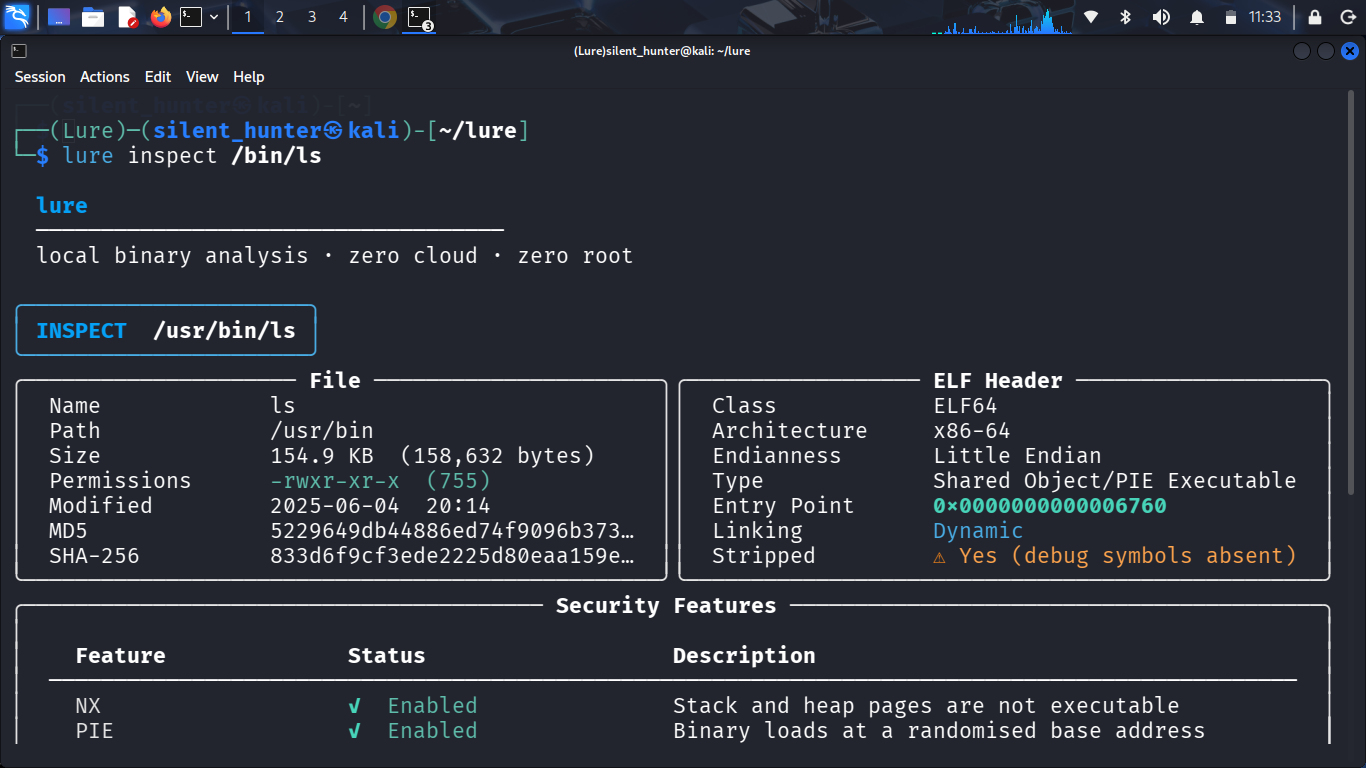 0xusmanismail/lure
Local Linux binary analysis tool that runs untrusted ELFs in an isolated sandbox (namespaces + strace) and produces structured behavioral reports…
 cahyod/react2shell
Alat ini mendeteksi potensi kerentanan React2Shell (CVE-2025-55182) dalam proyek React dengan memeriksa: - File `package.json` dan file lock untuk…
 lkimuk/reark
An intelligent reverse engineering analysis tool designed for multiple target platforms, currently supporting HarmonyOS (HAP/APP/ABC) and Android…