
truegaze
 nightwatchcybersecurity/truegaze
Static analysis tool for Android/iOS apps focusing on security issues outside the source code
android-securityios-securitymisconfiguration+3
133
nightwatchcybersecurity/truegazeStatic analysis tool for Android/iOS apps focusing on security issues outside the source code
 google/paranoid_crypto
Paranoid's library contains implementations of checks for well known weaknesses on cryptographic artifacts.
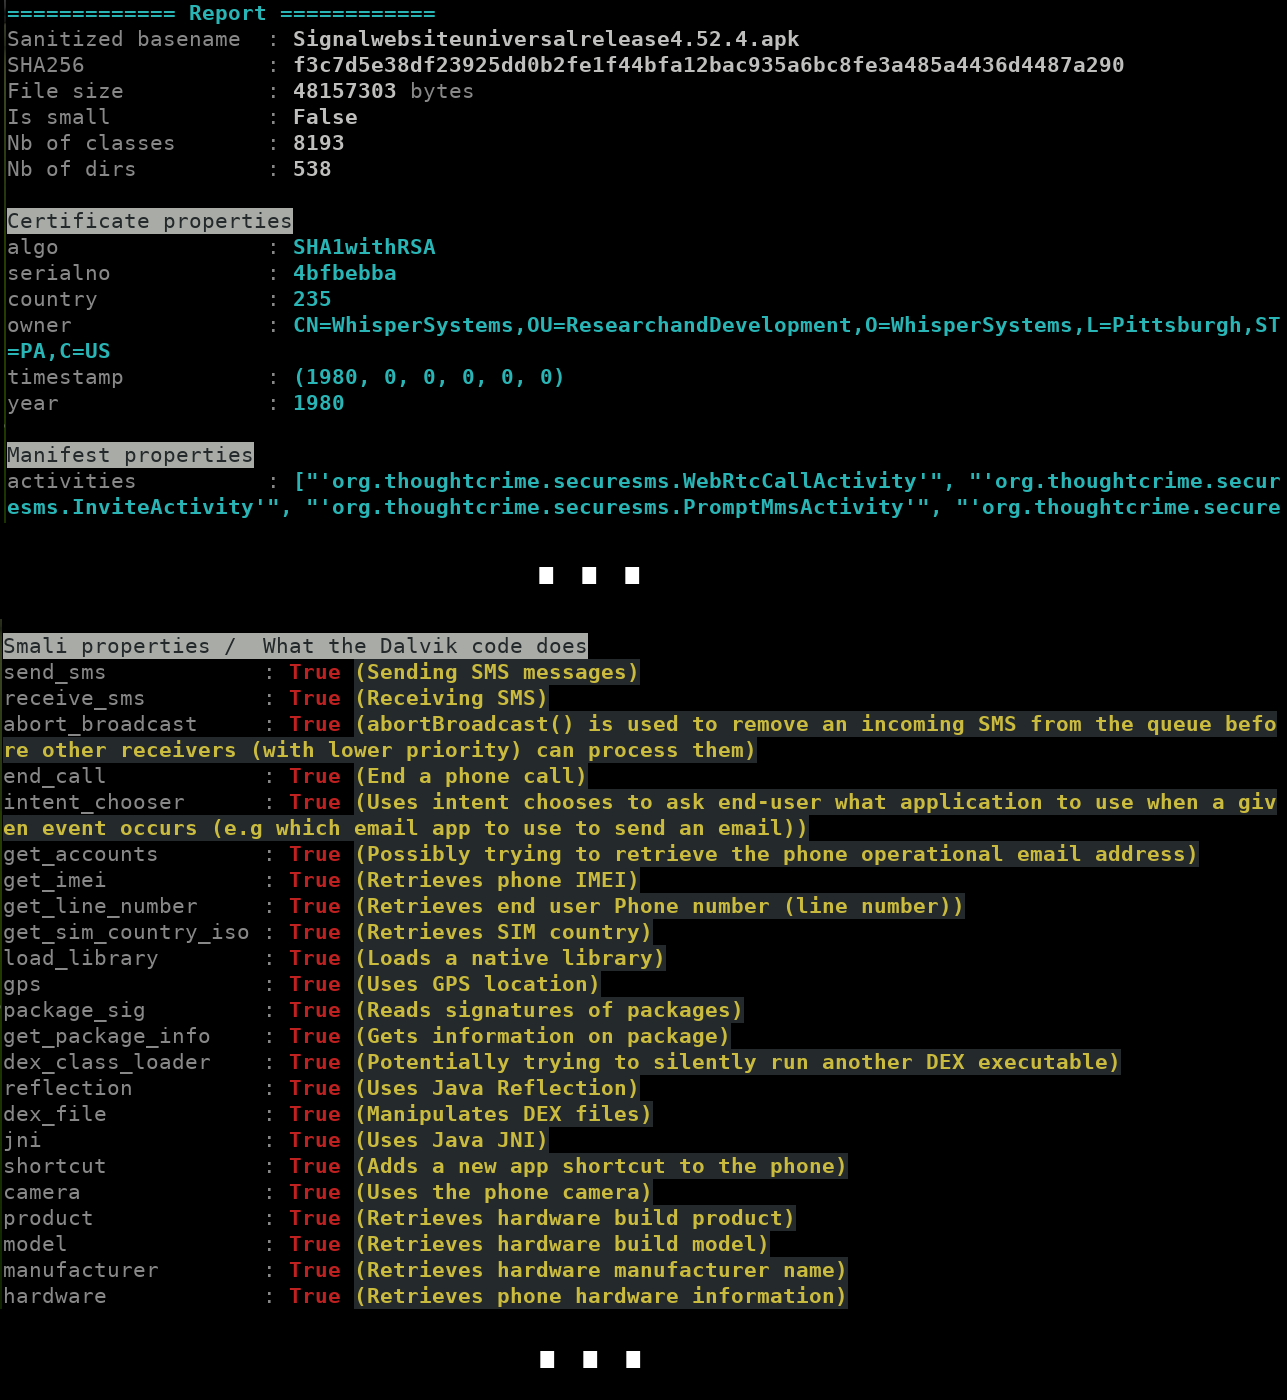 cryptax/droidlysis
Automated pre-analysis tool for Android apps that disassembles samples, extracts properties via configurable pattern matching, and organizes output…
 shoucheng3/jenkinsci__workflow-cps-plugin_cve-2022-25173_2646-v6ed3b5b01ff1
Exploit for CVE-2022-25173 targeting Jenkins Pipeline Groovy Plugin's CPS interpreter sandbox bypass, enabling arbitrary code execution within…
 ricardoquesada/regenerator2000
An interactive disassembler for the CPU 6502, focused on Commodore 8-bit computers. Features a TUI with modern features like x-ref, undo/redo, flow…
 rgielen/struts1filter
A request parameter filter solution for Struts 1 CVE-2014-0114 based on the work of Alvaro Munoz and the HP Fortify team
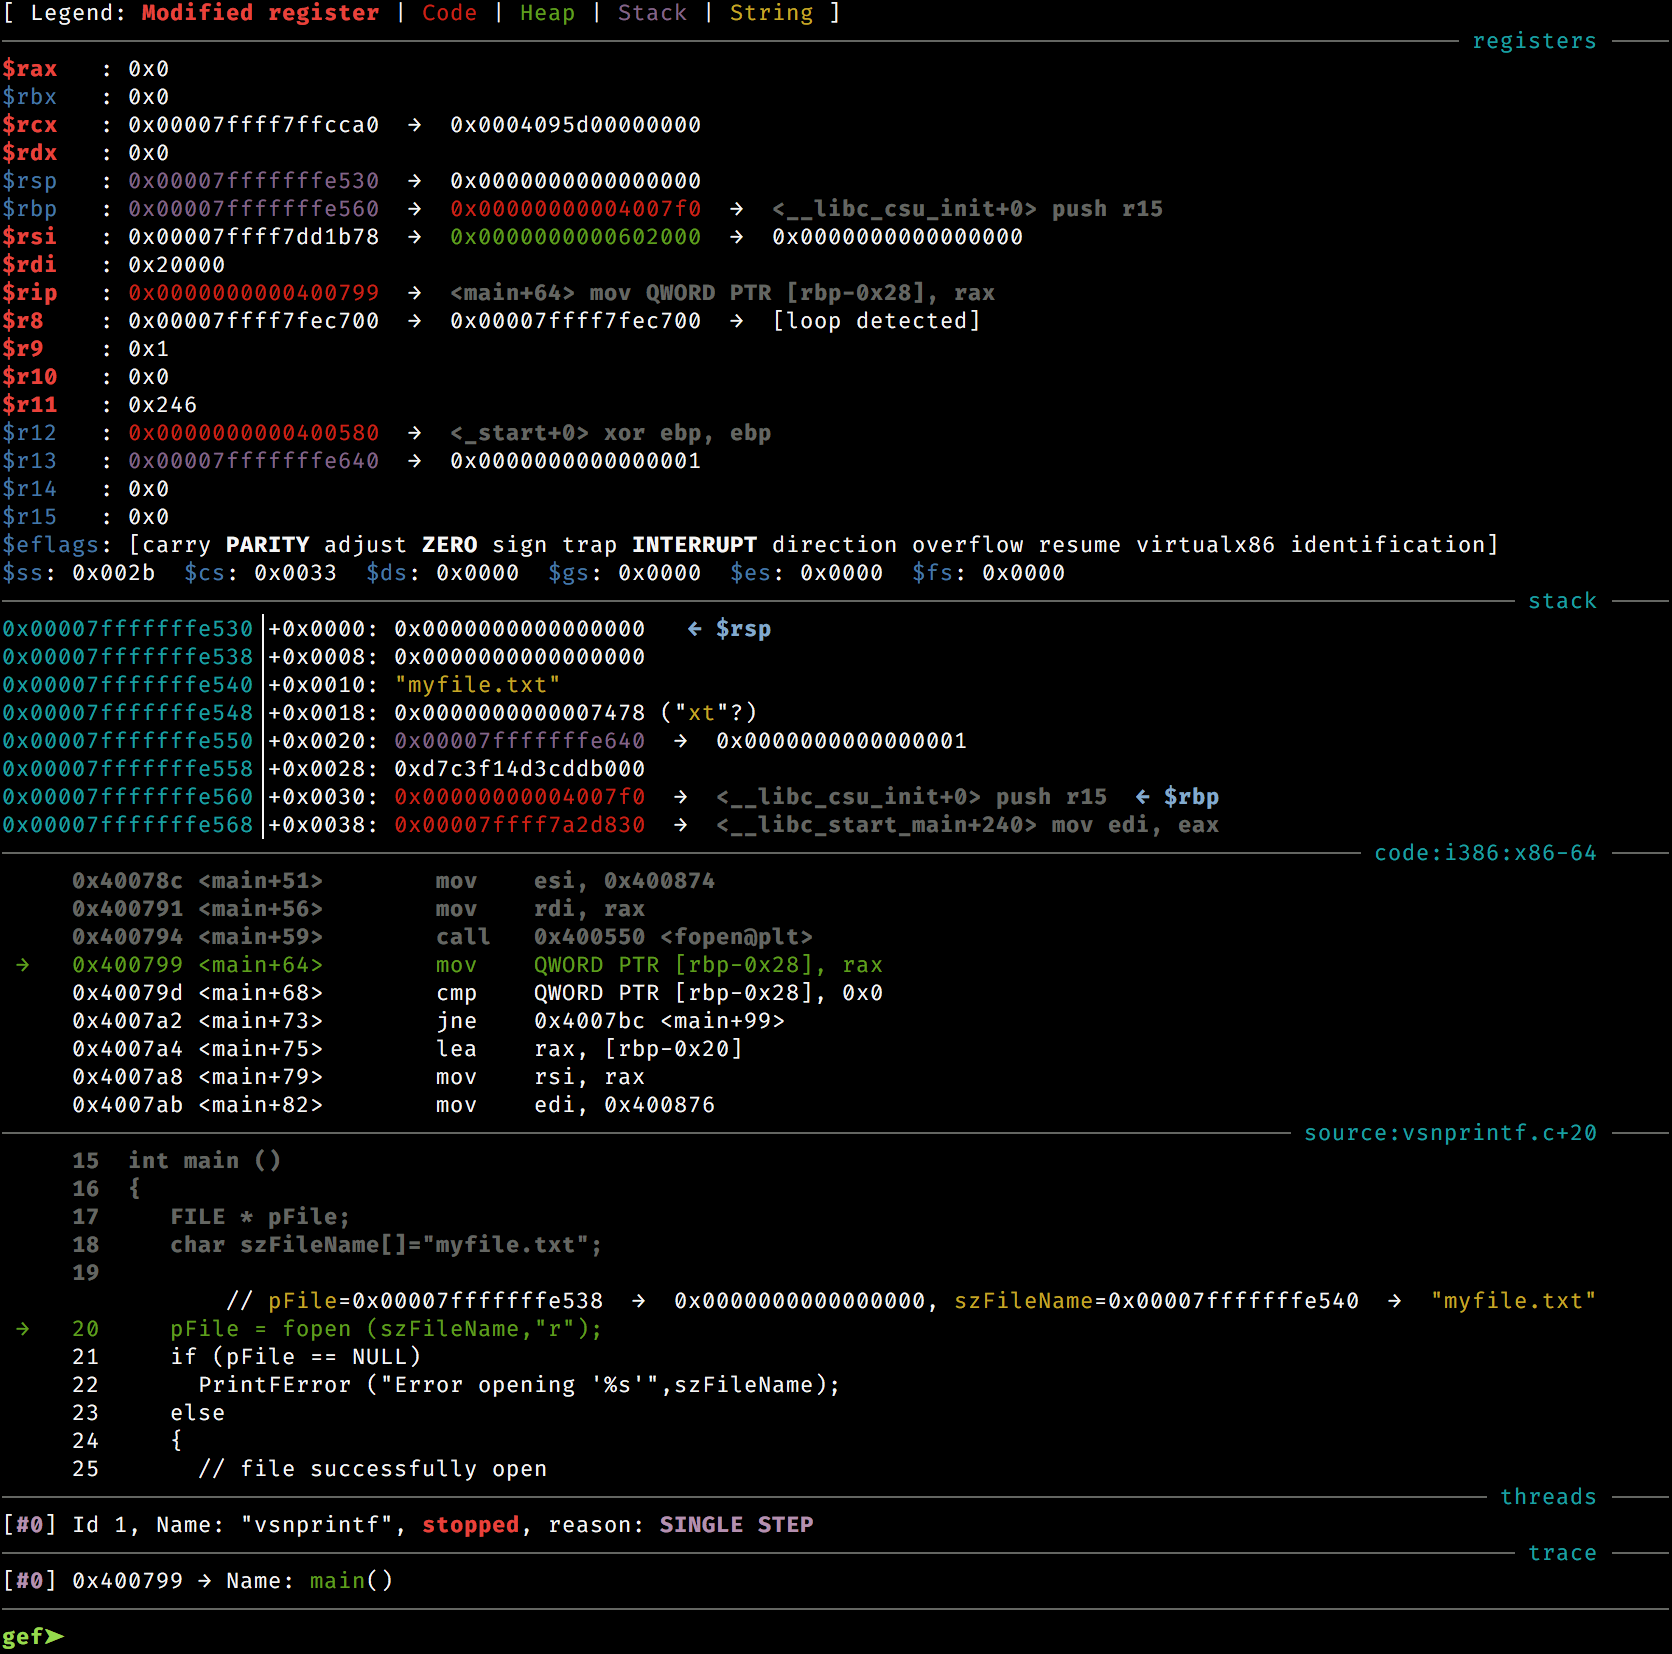 hugsy/gef
GEF (GDB Enhanced Features) - a modern experience for GDB with advanced debugging capabilities for exploit devs & reverse engineers on Linux
 scabench/fastjson-tp1fn1
a scenario based on CVE-2022-25845 yielding a TP for metadata based SCA but a FN if the callgraph is used
 x86byte/sbox
Compile-time AES string obfuscation for C++
 shoucheng3/jenkinsci__script-security-plugin_cve-2023-24422_1228.vd93135a_2fb_25
Jenkins plugin providing script approval workflows and Groovy sandboxing to enforce secure script execution, with ACL-aware permission checks and…
 trailofbits/testing-handbook
Trail of Bits Testing Handbook - appsec.guide
 we5ter/flerken
A Solution For Cross-Platform Obfuscated Commands Detection presented on CIS2019 China. 动静态Bash/CMD/PowerShell命令混淆检测框架 - CIS 2019大会
 chrischo-h/bithoven
Bithoven is a smart contract language for composing powerful and secure instruments on Bitcoin. LR(1) parser with static analysis for compile-time…
 shoucheng3/xwiki__xwiki-commons_cve-2023-31126_14-10-3
Java library providing technical commons for XWiki projects, with a focus on vulnerability analysis and static code inspection for security testing.
 hasherezade/jsc_deobfuscator
Static deobfuscation toolkit for compiled V8 JavaScript bytecode, focusing on JSCeal payloads. Provides pattern-driven filters, control-flow…
 owasp/appsec-agent
A TypeScript package that provides AI-powered agents for Application Security (AppSec) tasks, built on top of the frontier models.
 nidhihcl/external_expat_2.1.0_cve-2022-43680
C library for stream-oriented XML parsing with a focus on vulnerability analysis and exploitation of CVE-2022-43680, enabling fuzzing and…
 pazhanivelmani/webp_android10_r33_cve-2023-1999
Proof-of-concept exploit for CVE-2023-1999 targeting the WebP codec library on Android 10 (r33). Demonstrates a heap buffer overflow vulnerability in…