

sig_finder
 hasherezade/sig_finder
Signature finder (from PE-bear)
binary-analysismalware-analysisreverse-engineering+1
hasherezade/sig_finderSignature finder (from PE-bear)
 blacksnufkin/cheshire
Adaptix C2 service plugin that drives LitterBox payload analysis from the operator UI.
 ga1ois/blackhat-europe-2022
Select Bugs From Binary Where Pattern Like CVE-1337-Days
 rakosn1cek/oversight
A lightweight security auditor and sandbox for shell scripts. Oversight combines a Static Analysis engine (Rust) with Dynamic Enforcement (Linux…
 elevenpaths/pesto
Extracts and analyzes PE file security characteristics (ASLR, DEP, CFG, NO_SEH) from DLLs and EXEs across directories, storing results in a SQLite…
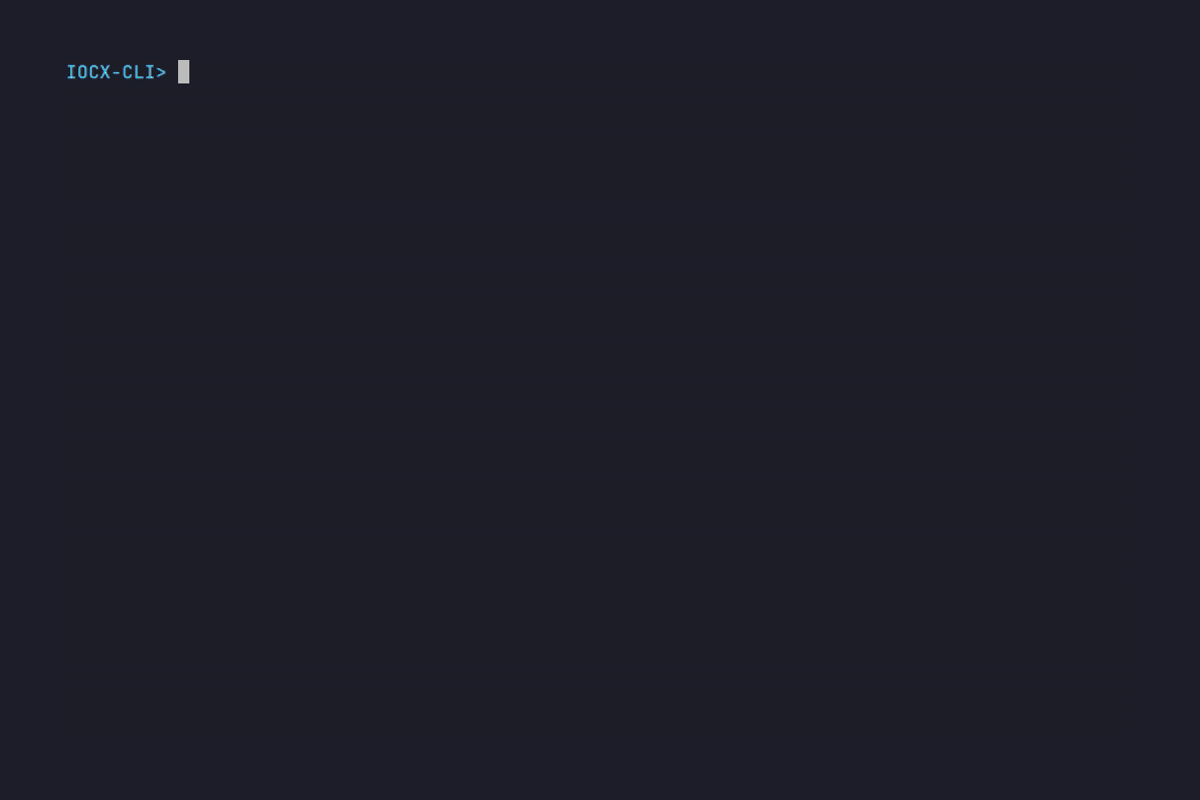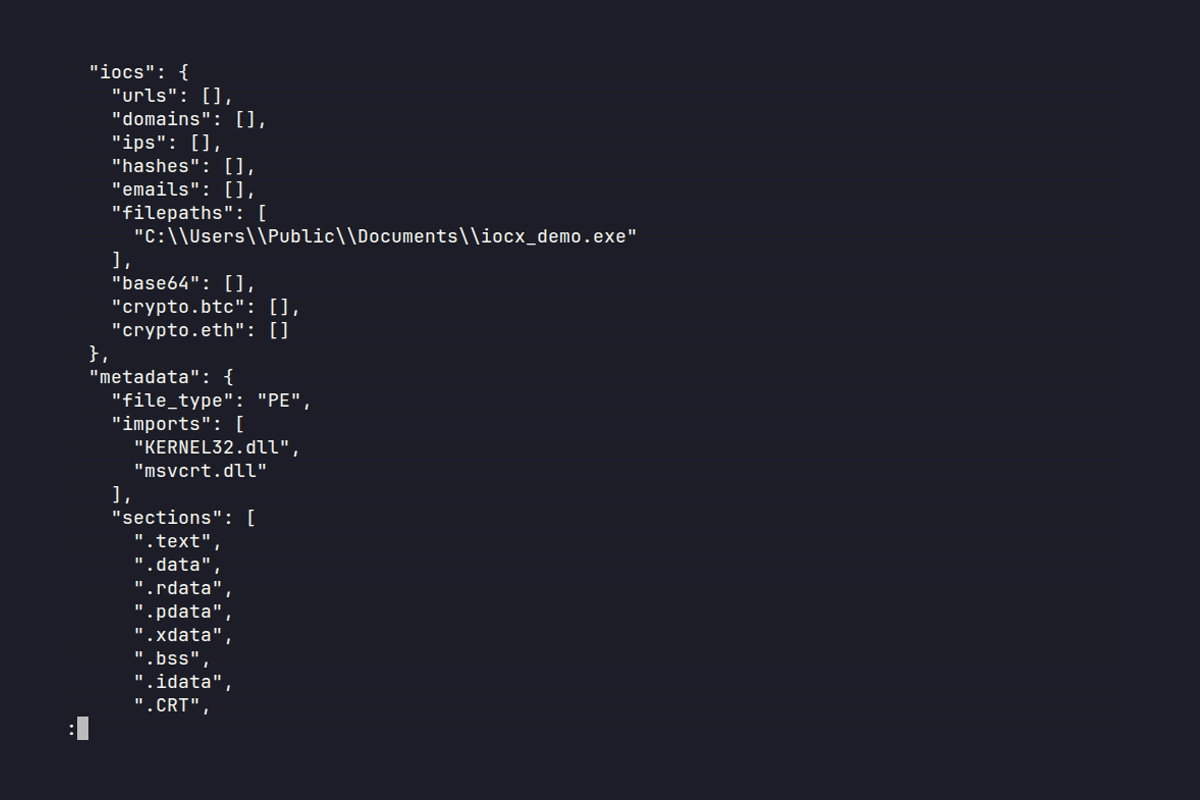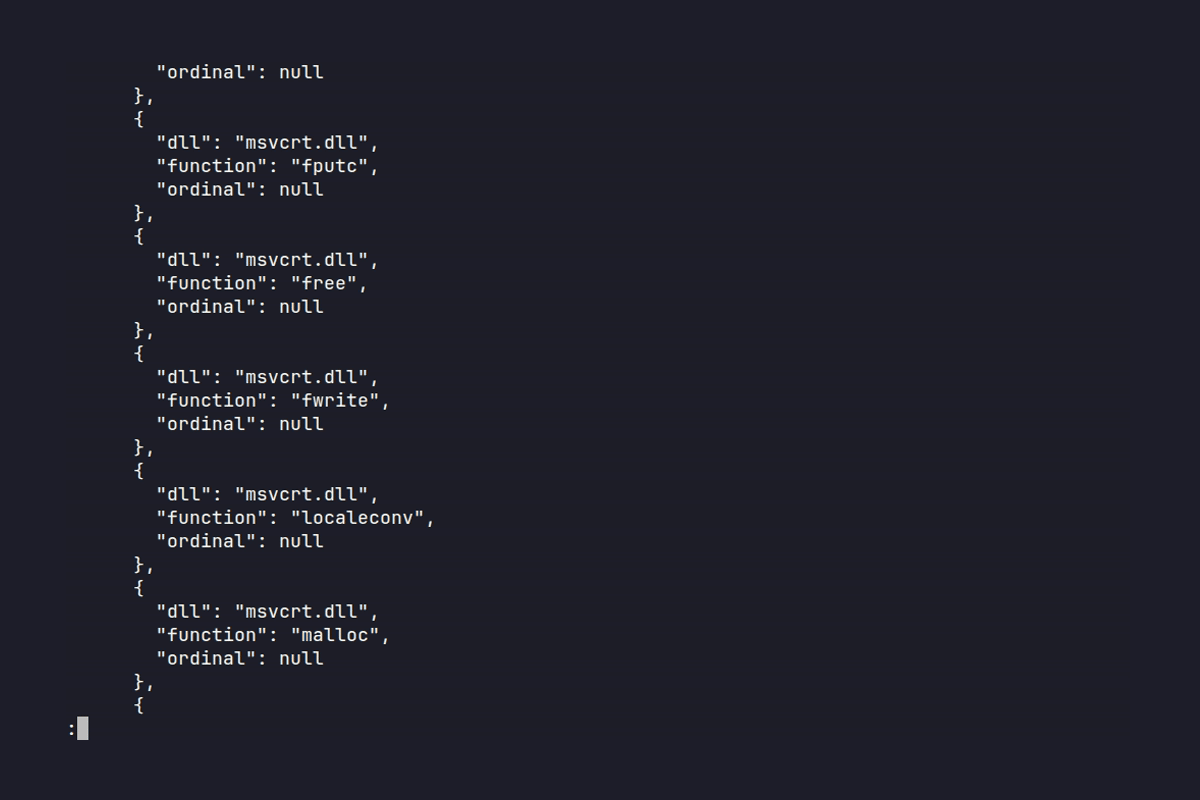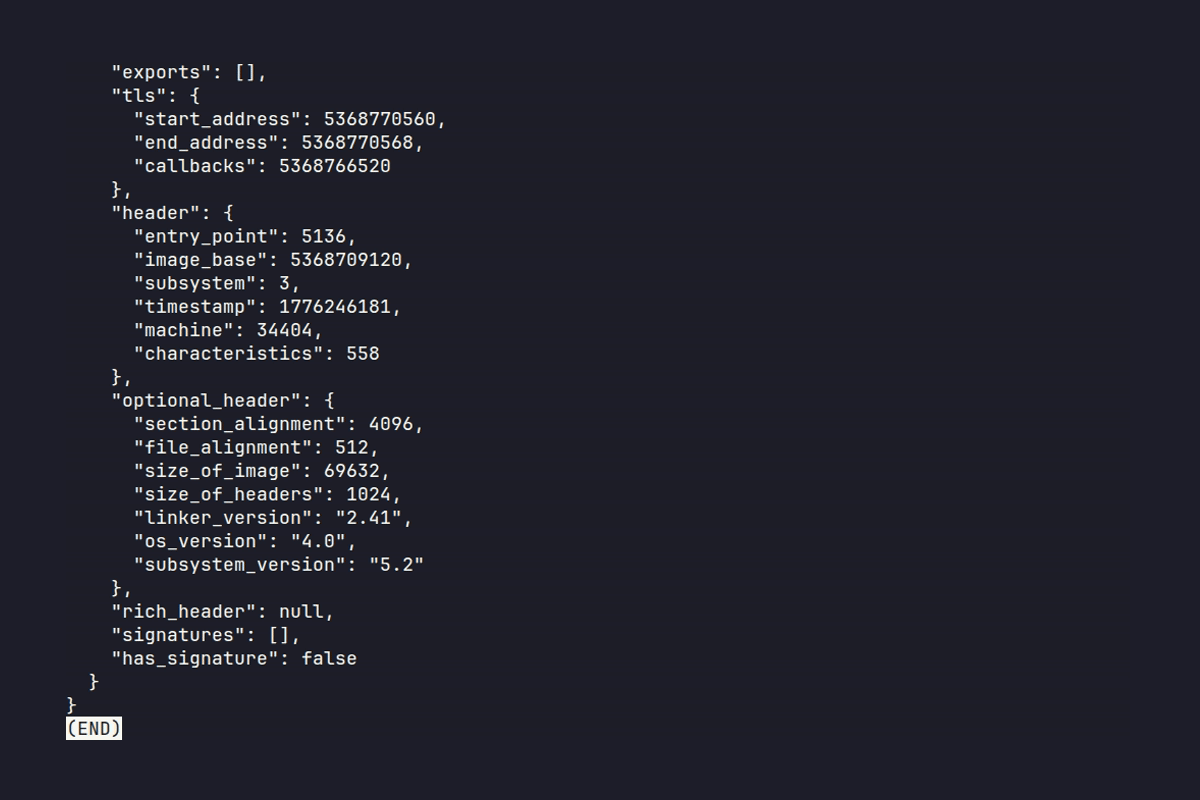 iocx-dev/iocx
An extensible, deterministic static‑analysis engine that extracts high‑signal IOCs from PE binaries and text, built for SOC automation and modern…
 brennhill/sloppy-joe
Shields against supply-chain, slopsquatting, and typosquatting attacks from dependencies and code.
 blakebratcher/wcw-cyberring-pav-decryptor
Cryptanalysis of a proprietary 1999 video DRM system. Recovers 61 encrypted wrestling videos from the WCW Internet Powerdisk CD-ROM through static…
 amenti-labs/openentropy
Open-source entropy harvesting from unconventional hardware sources. Rust + Python SDK.
 ambitsecurity/jshound
Find every API request a web app makes, from the JavaScript it ships: method, URL, body, headers and GraphQL operations. One command.
 nccgroup/yaml2yara
Generate bulk YARA rules from YAML input
 0x11dfe/file-unpumper
Tool that can be used to trim useless things from a PE file such as the things a file pumper would add.
 pr0me/xtride
N-gram-based type recovery tool for binaries, recovering structures and function signatures from decompiled code with high throughput and actionable…
 shellcromancer/daysofyara-2023
Rules Shared by the Community from 100 Days of YARA 2023 -
 xv4l3x/hermit
Inspects, decompiles and structurally patches Hermes bytecode (HBC) from React Native apps, with a GDB-style REPL, CFG, decompiler and re-serializing…
 forentfraps/pe-signgen
Universal signature generation for any system function from all Windows Builds using Winbindex
 aquasecurity/scan-cve-2018-8115
CLI tool that verifies Docker images for CVE-2018-8115 by checking layers for malicious files, helping ensure safe pulls from Docker Hub.
 prophetcraft/jarhunter
JAR analysis tool for exploring, searching, and extracting specific classes from large JAR files with bytecode search, multi-selection extraction,…