

pyOneNote
 dissectmalware/pyonenote
A python library to parse OneNote (.one) files
digital-forensicsmalware-analysisstatic-analysis
dissectmalware/pyonenoteA python library to parse OneNote (.one) files
 quosecgmbh/grap
Define and match user-defined graph patterns against binary control flow graphs using a Capstone-based disassembler, with CLI, Python bindings, and…
 idiom/pftriage
Python tool and library to help analyze files during malware triage and analysis.
 synacktiv/bip
Object-oriented Python API to simplify interaction with IDA for reverse engineering, enabling plugin development and automation of disassembly…
 pan-unit42/dotnetfile
Python library for parsing CLR/PE metadata in .NET assemblies, exposing streams and hash fingerprints to support malware analysis and threat hunting.
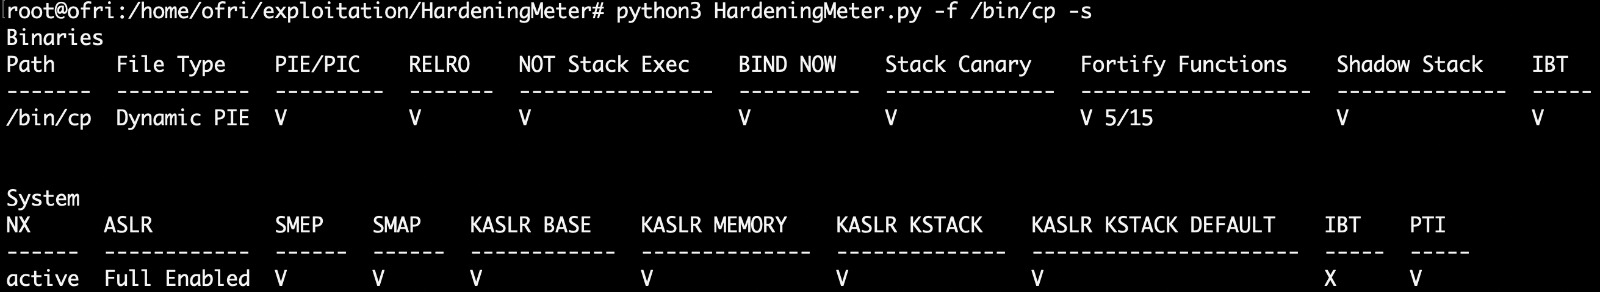 ofriouzan/hardeningmeter
HardeningMeter is an open-source Python tool carefully designed to comprehensively assess the security hardening of binaries and systems.
 s4dhulabs/vimana-framework
Vimana is a modular security framework for auditing Python APIs and Web applications. The plugin-based architecture enables security professionals to…
 seifreed/yaraast
A powerful Python library and CLI tool for parsing, analyzing, and manipulating YARA rules through Abstract Syntax Tree (AST) representation
 pstirparo/machofile
machofile is a module to parse Mach-O binary files
 munshi007/aura-state
Python framework for building LLM workflows as state machines with formal verification via Z3 theorem proving, CTL model checking, and conformal…
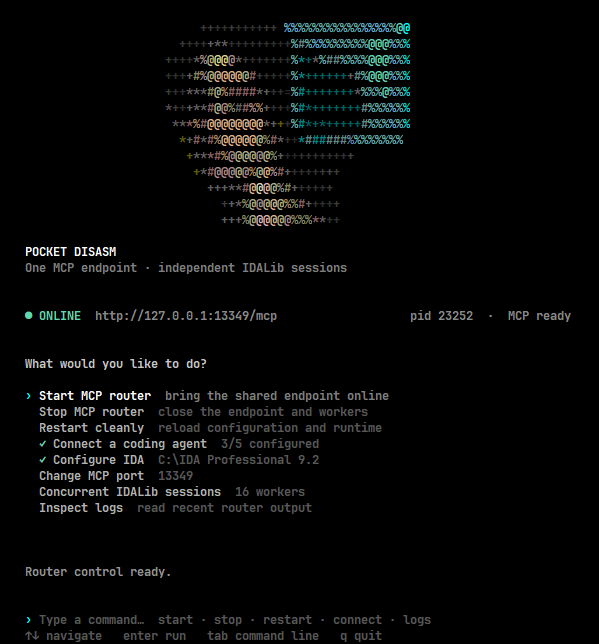 whoisqwerz/pocket_disasm
Multi-session IDALib MCP router for coding agents. Analyze multiple binaries in parallel with IDA-compatible reverse engineering tools.
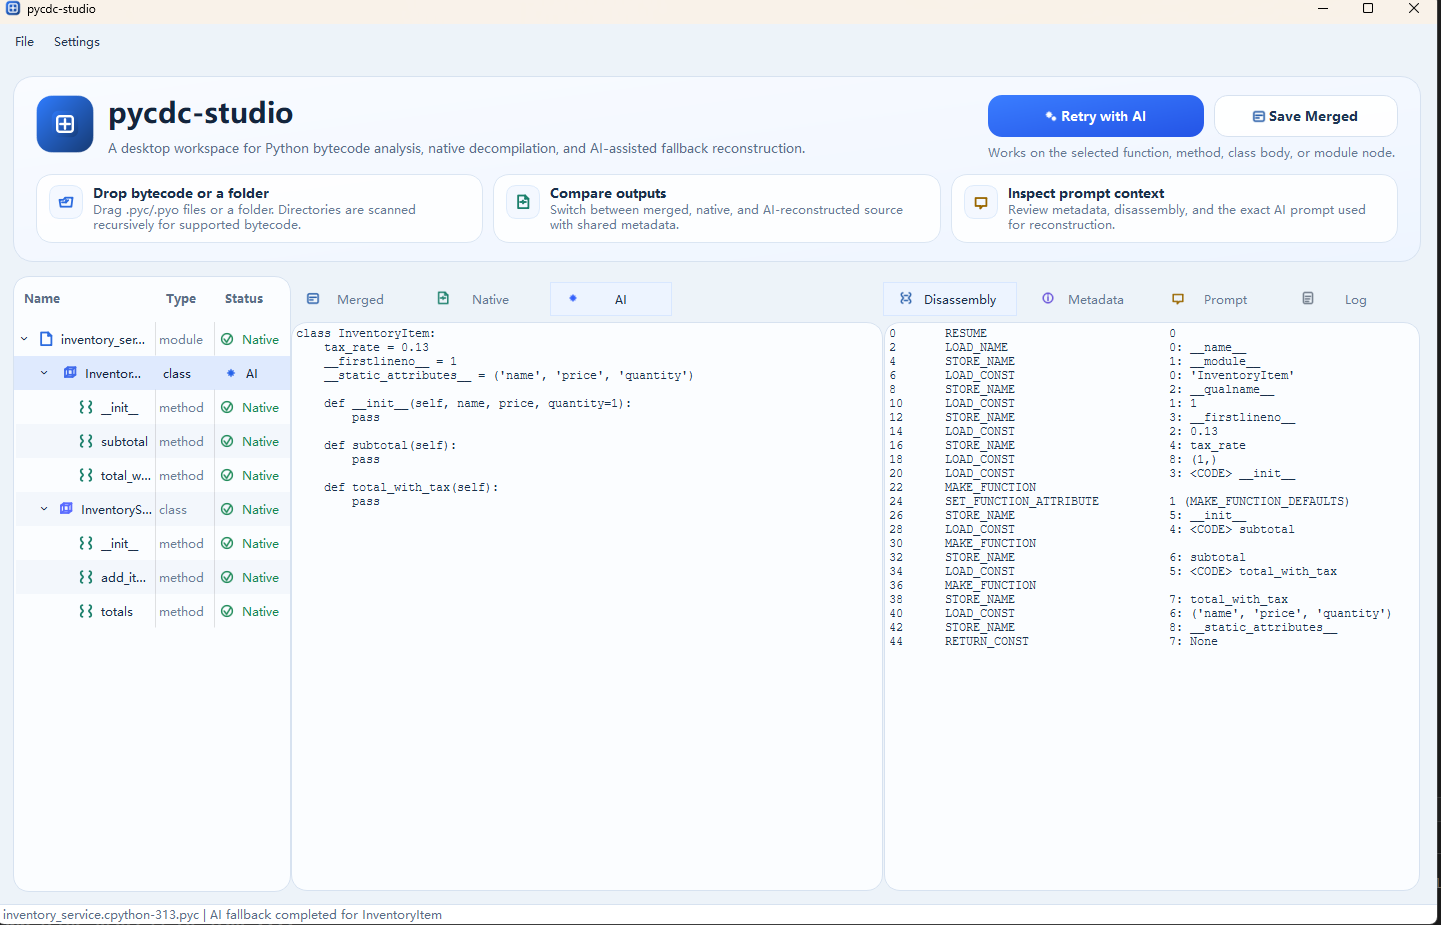 ddouworld/pycdc-studio
A Qt Widgets desktop UI for exploring Python bytecode with pycdc/pycdas, inspecting native decompilation, and using AI fallback for unsupported code…
 synacktiv/canon-mf644
Exploit and firmware analysis toolkit for Canon MF644 printer vulnerabilities, including Python exploits, ARM shellcode, and IDA Pro loader scripts…
 amenti-labs/openentropy
Open-source entropy harvesting from unconventional hardware sources. Rust + Python SDK.
 sylwia-budzynska/codeql-workshop
Take first steps in CodeQL for Python by writing a query to find CVE-2024-32022
 trailofbits/not-slithering-anywhere
The Python Version of our Not Go-ing Anywhere Vulnerable Application
 jordan922/cve-2025-8088
Python tool for safe archive handling, path traversal awareness, and secure extraction. Inspired by CVE-2025-8088.
 yonliud/cve-2026-0303
Checkov PoC: arbitrary code execution through auto-loaded configuration and unsigned external Python checks.