
wheelaudit
 kriskimmerle/wheelaudit
Python Wheel File Security Scanner — scan .whl files for security issues before installation. Detects path traversal (CVE-2026-24049), RECORD…
code-analysisconfiguration-auditingdevsecops+5
3
kriskimmerle/wheelauditPython Wheel File Security Scanner — scan .whl files for security issues before installation. Detects path traversal (CVE-2026-24049), RECORD…
 perufitlife/dotclaude-security
Scan a repo's .claude/ config (settings.json hooks, MCP servers, env, allowed-tools) for the RCE & API-key-exfiltration footguns (CVE-2025-59536,…
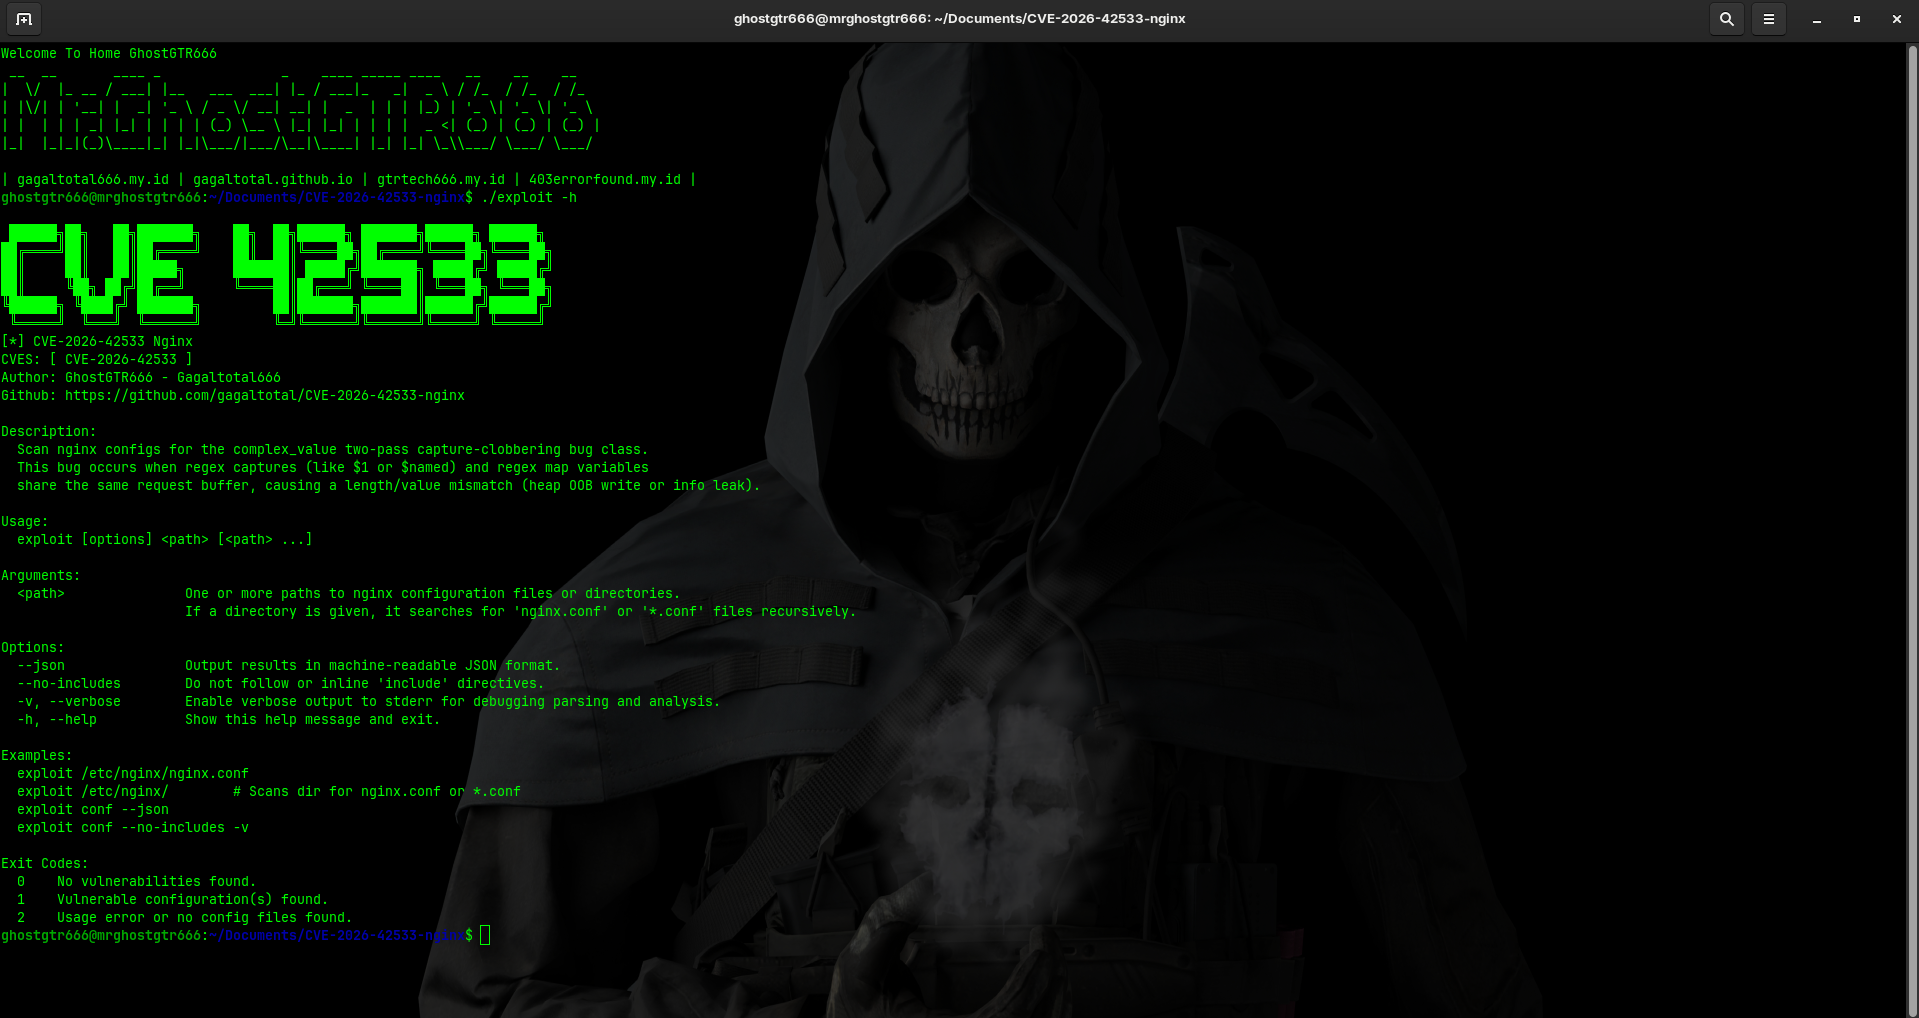 gagaltotal/cve-2026-42533-nginx
CVE-2026-42533 Nginx
 ekamsinghwalia/openssl-vulnerability-detection-script
This is an OpenSSL Vulnerability Detection Script for CVE-2022-2274
 anteater/anteater
Anteater - CI/CD Gate Check Framework
 kvesta/vesta
A static analysis of vulnerabilities, Docker and Kubernetes cluster configuration detect toolkit based on the real penetration of cloud computing
 makerchecker/makerchecker
Open-source security gateway & static scanner for AI agents. Enforce role-based access control (RBAC), human-in-the-loop approvals, segregation of…
 bridgecrewio/checkov
Static analysis tool for infrastructure as code that detects cloud misconfigurations, vulnerabilities, and secrets across Terraform, Kubernetes,…
 elttam/semgrep-rules
Static analysis security rules for vulnerability detection and audit-focused code review across Java, Go, Python, C#, Kotlin, PHP, Kubernetes, and…
 stackrox/kube-linter
KubeLinter is a static analysis tool that checks Kubernetes YAML files and Helm charts to ensure the applications represented in them adhere to best…
 mcp-shark/mcp-shark
Wireshark-like forensic analysis for Model Context Protocol communications Capture, inspect, and investigate all HTTP requests and responses between…
 rootsecdev/microburstsecretshunter
Scans exported Azure domain dumps for plaintext passwords, connection strings, storage keys, and other secrets; generates redacted CSV/HTML reports…
 vardhan0257/upb-any-recursion-audit
Audit harness testing whether the CVE-2026-0994 Any-unwrapping recursion bug class affects upb's C core in Ruby and PHP protobuf bindings, with…
 appvia/krane
Kubernetes RBAC static analysis & visualisation tool
 controlplaneio/kubesec
Security risk analysis for Kubernetes resources
 hashgraph-online/hol-guard
Open-source antivirus for AI agents: block risky tools, secret access, prompt injection, malicious packages, MCP servers, plugins, and skills at…
 skyscanner/cfripper
Library and CLI tool for analysing CloudFormation templates and check them for security compliance.
 tindersec/gh-workflow-auditor
Script to audit GitHub Action Workflow files for potential vulnerabilities.