
nuguard
 nuguardai/nuguard
opensource repo for validating agentic AI applications: redteam, behavior, supply-chain, static analysis
ai-securityapi-security-testingcode-analysis+8
508h 45m ago
nuguardai/nuguardopensource repo for validating agentic AI applications: redteam, behavior, supply-chain, static analysis
 shoucheng3/esapi__esapi-java-legacy_cve-2022-23457_2-2-3-1
Enterprise Security API library providing security controls for Java web applications, including authentication, access control, input validation,…
 mobsf/mobile-security-framework-mobsf
Automated mobile application security testing framework for Android, iOS, and Windows. Performs static and dynamic analysis, malware detection, and…
 amrudesh1/morf
Mobile Reconnaissance Framework is a powerful, lightweight and platform-independent offensive mobile security tool designed to help hackers and…
 owasp/cwe-tool
A command line CWE discovery tool based on OWASP / CAPSEC database of Common Weakness Enumeration.
 owasp/cwe-sdk-javascript
A Common Weakness Enumeration (CWE) Node.js SDK compliant with MITRE / CAPEC
 owasp-noir/noir
Hunt every Endpoint in your code, expose Shadow APIs, map the Attack Surface.
 security-prince/resources-for-application-security
Some good resources for getting started with application security
 owasp/secure-agent-playbook
OWASP Secure Agent Playbook Project
 owasp/ocsd
OWASP Certified Secure-Software Developer
 owasp/owasp-scs
OWASP Smart Contract Security (SCS) Project
 owasp/wrongsecrets-binaries
Source code for the Binaries of OWASP WrongSecrets
 owasp/benchmark
The OWASP Benchmark GitHub repo has moved to: https://github.com/OWASP-Benchmark/BenchmarkJava
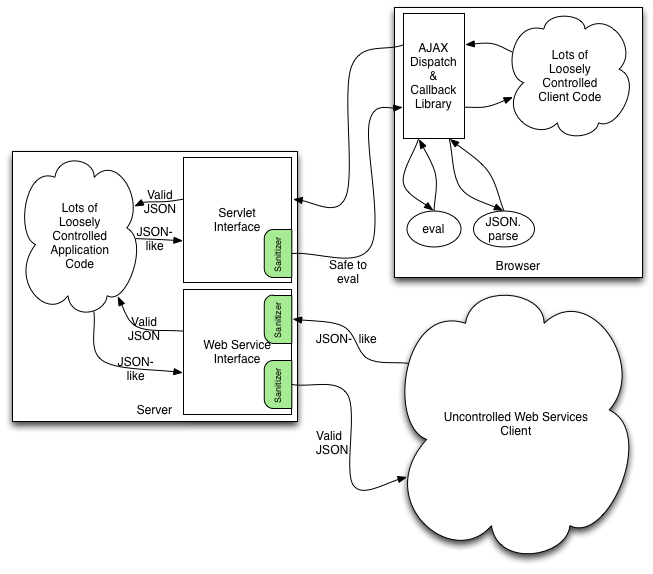 owasp/json-sanitizer
Given JSON-like content, The JSON Sanitizer converts it to valid JSON.
 bytepro-ai/bitcoder-v2-research
Research repository documenting LLM generalization ceilings in code security vulnerability detection, with cross-evaluation across synthetic and…
 shoucheng3/esapi__esapi-java-legacy_cve-2022-24891_2-2-3-1
OWASP Enterprise Security API library providing security controls for Java web applications, including authentication, access control, input…
 aws/http-desync-guardian
Analyze HTTP requests to minimize risks of HTTP Desync attacks (precursor for HTTP request smuggling/splitting).