
grap
 quosecgmbh/grap
Define and match user-defined graph patterns against binary control flow graphs using a Capstone-based disassembler, with CLI, Python bindings, and…
binary-analysisdebuggersmalware-analysis+2
155
quosecgmbh/grapDefine and match user-defined graph patterns against binary control flow graphs using a Capstone-based disassembler, with CLI, Python bindings, and…
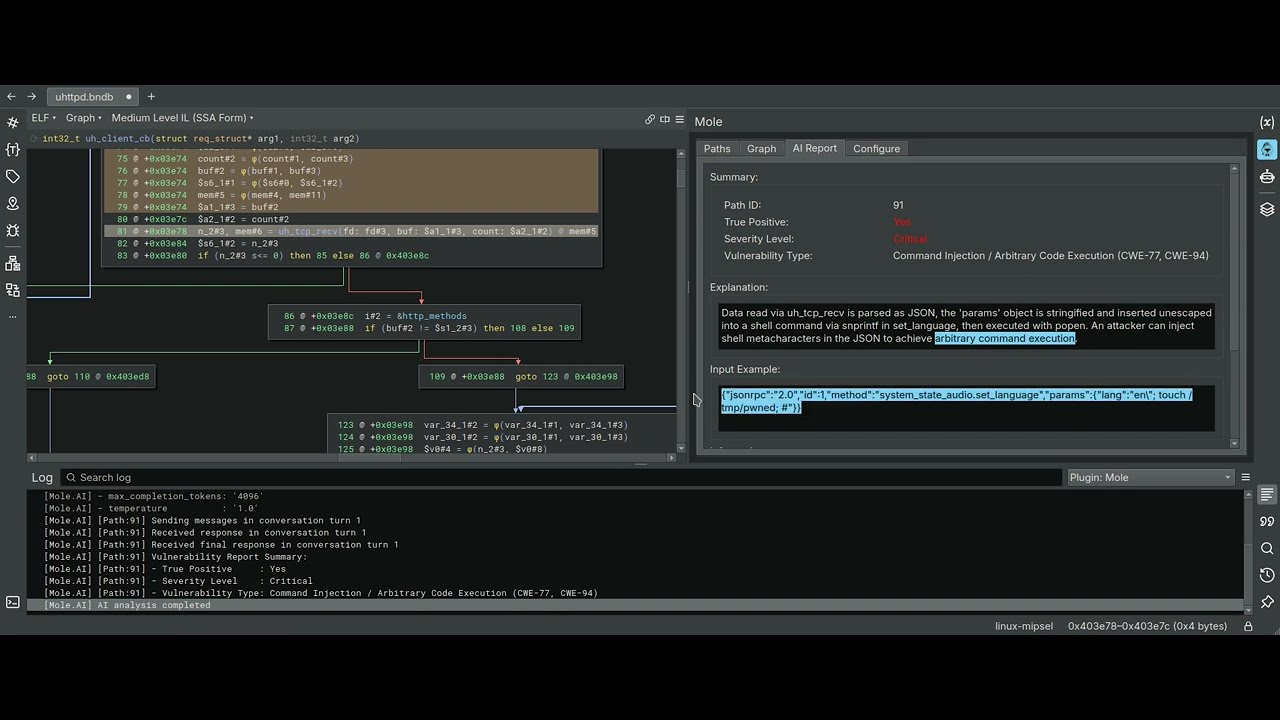 cyber-defence-campus/mole
A Binary Ninja plugin using backward slicing of variables as a driver for static taint analysis
 hiddenillusion/nomorexor
Tool to help guess a files 256 byte XOR key by using frequency analysis
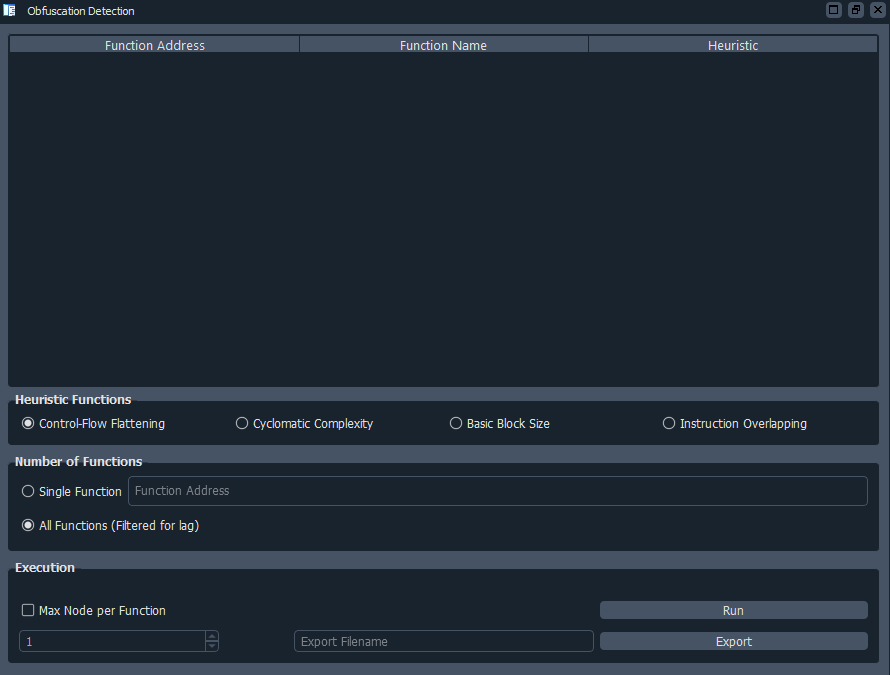 mcdulltii/obfdetect
IDA plugin for automated detection of obfuscated code and control-flow flattening in binaries using heuristic analysis and dominator tree…
 googleprojectzero/maccconc
Toolkit for exploring Linux kernel race conditions using KCOV traces: GUI and terminal viewers for concurrent execution and memory access, plus…
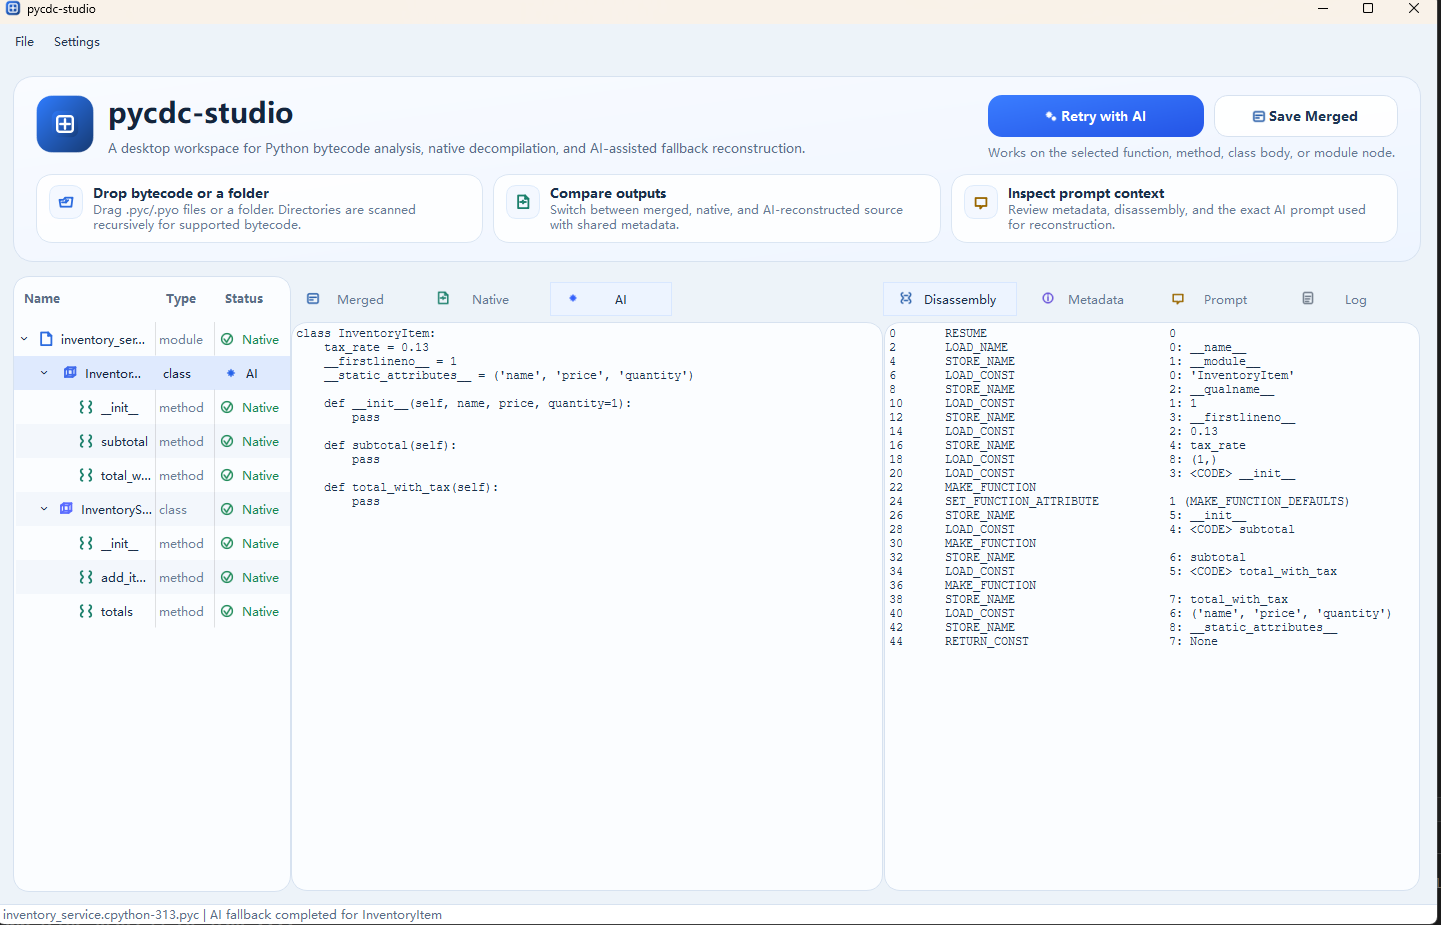 ddouworld/pycdc-studio
A Qt Widgets desktop UI for exploring Python bytecode with pycdc/pycdas, inspecting native decompilation, and using AI fallback for unsupported code…
 talha-nazeef-ahmed/rpc-triage
A zero-symbol static analysis engine that extracts and mathematically ranks the Windows RPC attack surface using an AHP-based risk model.
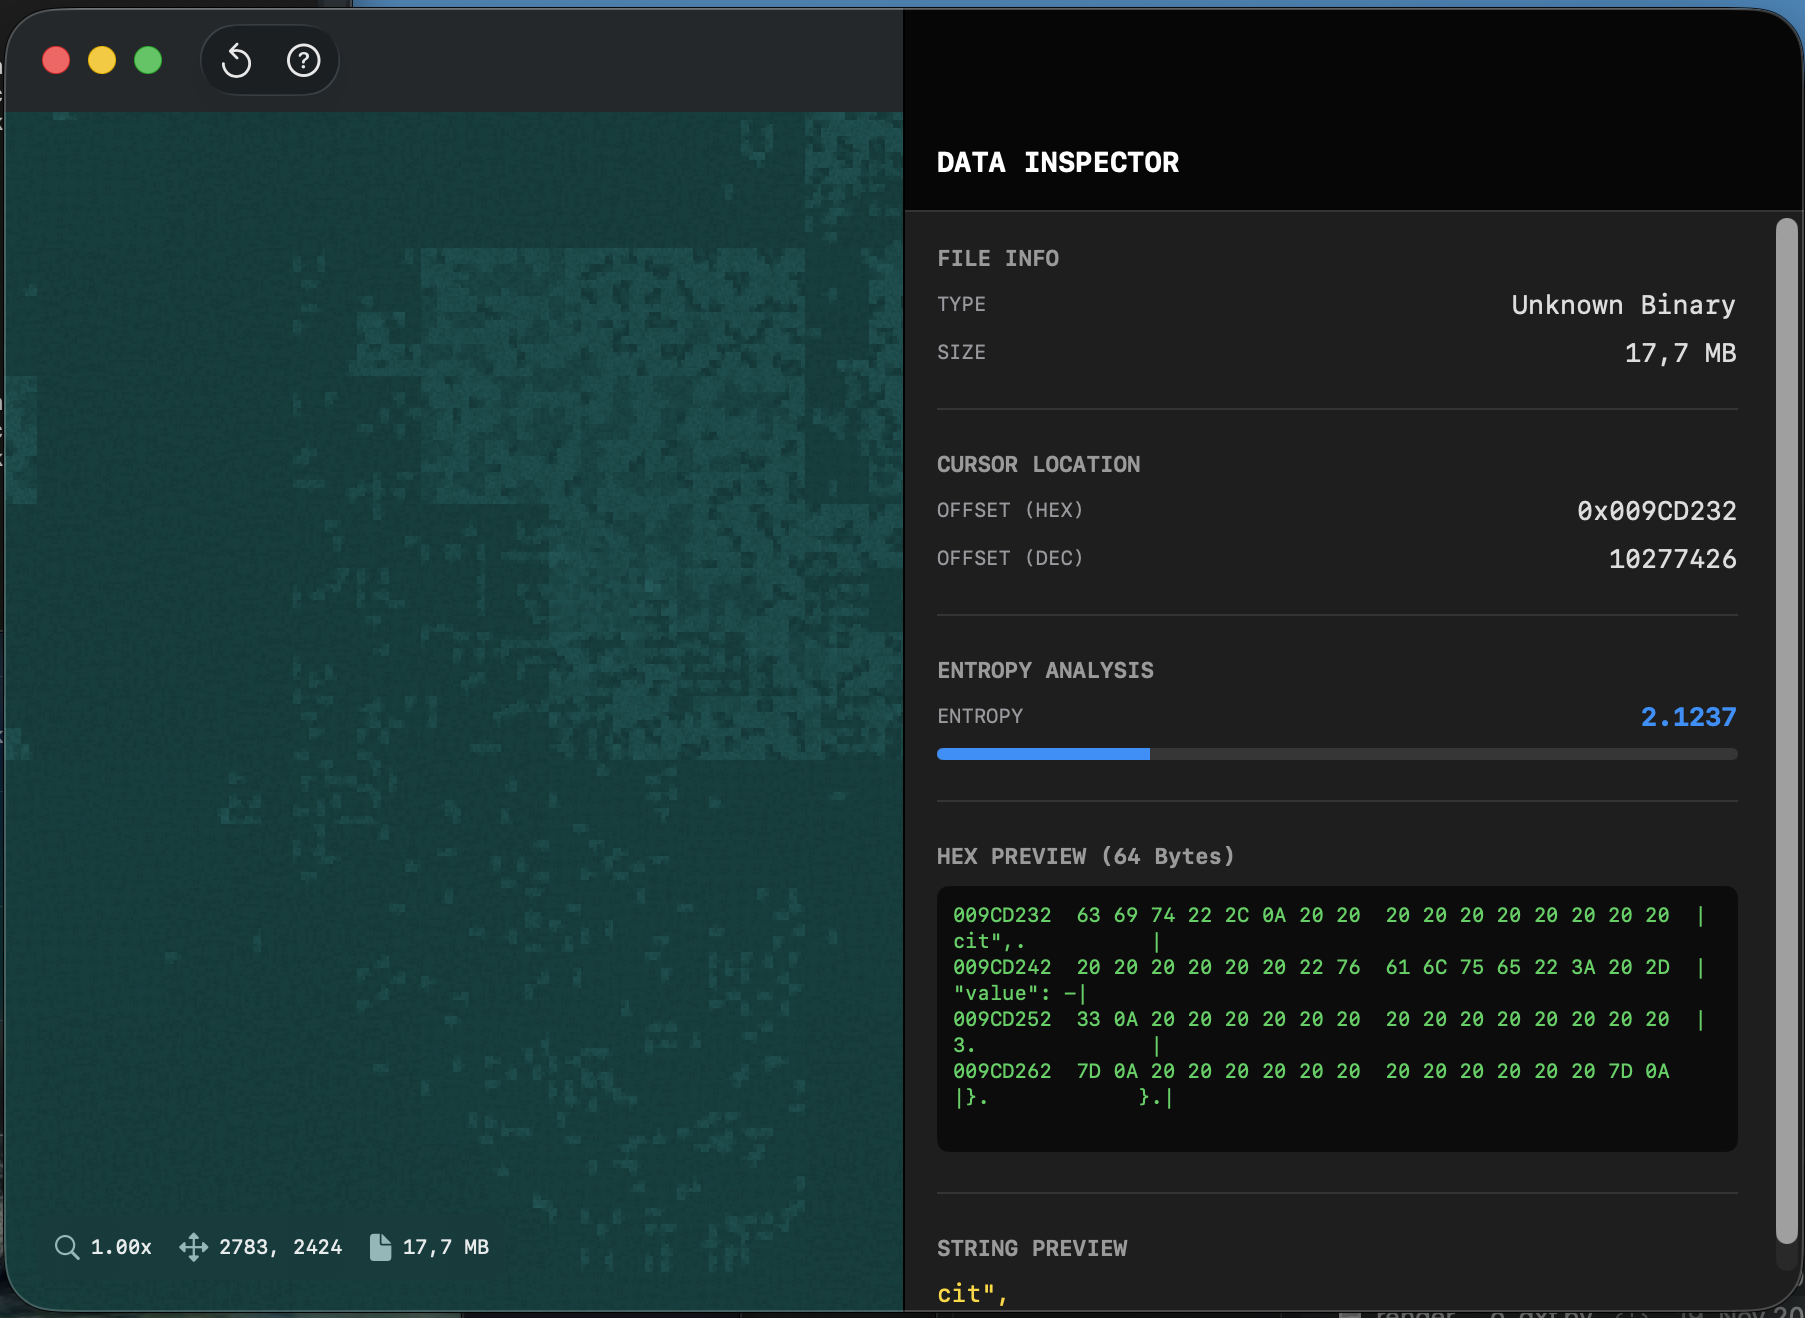 farukalpay/neurocore
NeuroCore is a native macOS application that visualizes the internal structure of binary files using a Hilbert Curve mapping and Shannon Entropy…
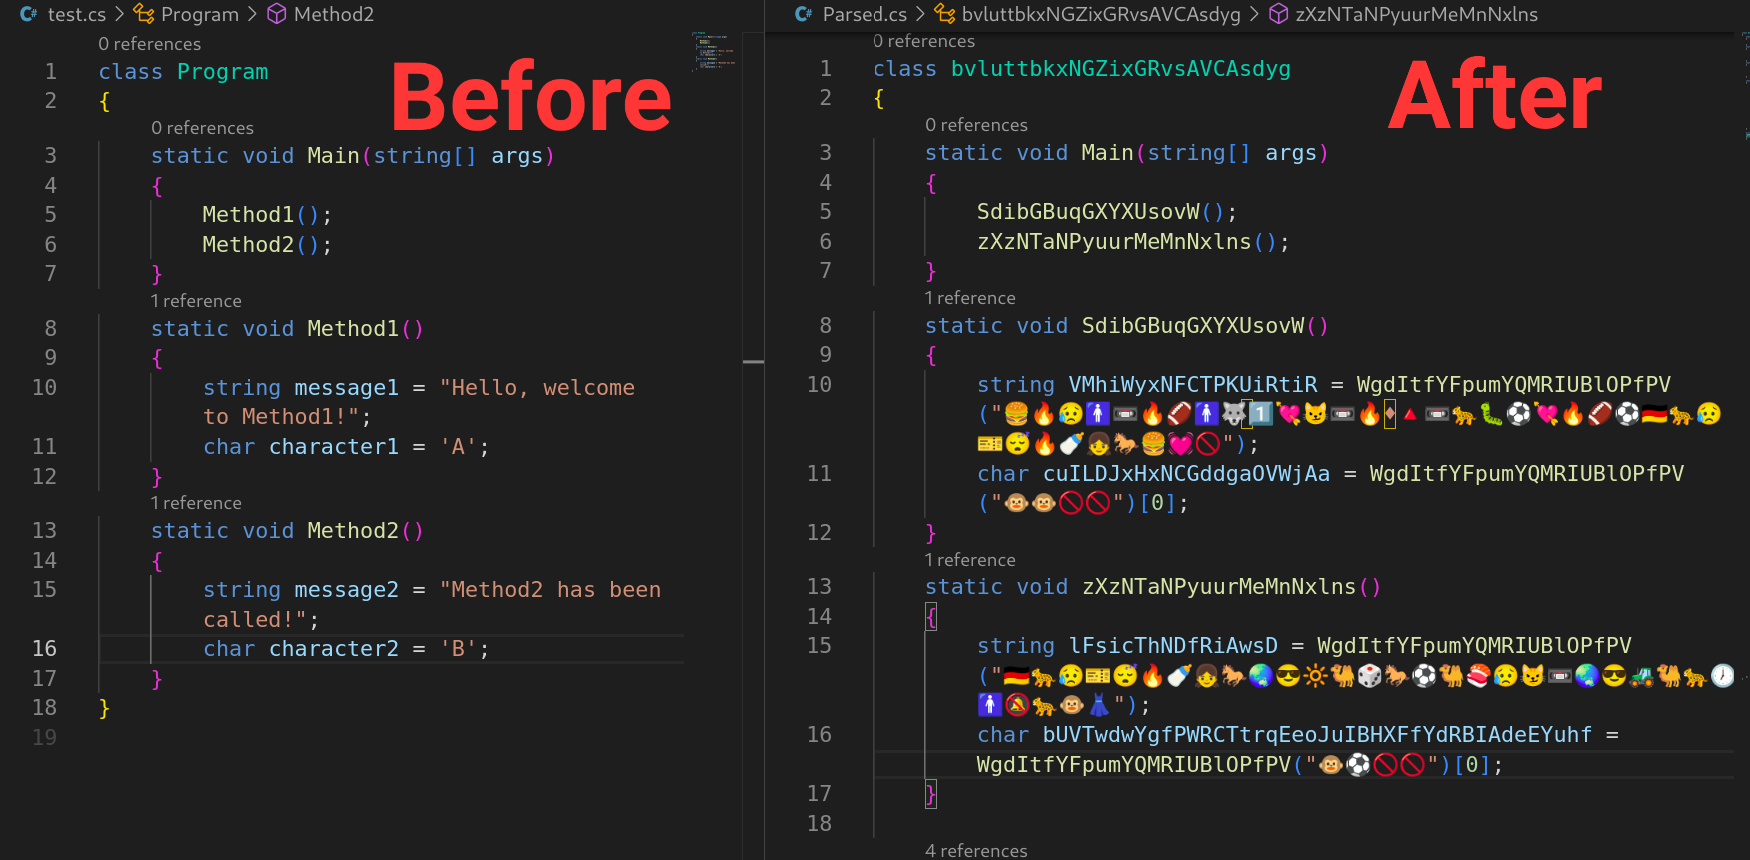 tomiwa-ot/emojify
C# source-code obfuscator that replaces character and string literals with emojis and randomizes class, interface, method, and variable names using…
 sdodson/cve-2026-46595-proof
Go proof-of-concept demonstrating CVE-2026-46595 in golang.org/x/crypto/ssh, using symbol inspection of stripped binaries and image scans to verify…
 polllogamer/sha-256-backdoor-discovery-engine
Detects potential backdoors in SHA-256 hashes using cryptographic analysis and pattern recognition. Designed for malware analysis and security…
 halahajyahia/cve-2022-2869-detector
CodeQL detector for CVE-2022-2869 root cause (CWE-191 unsigned underflow) using control-flow/range analysis to identify vulnerable patterns without…
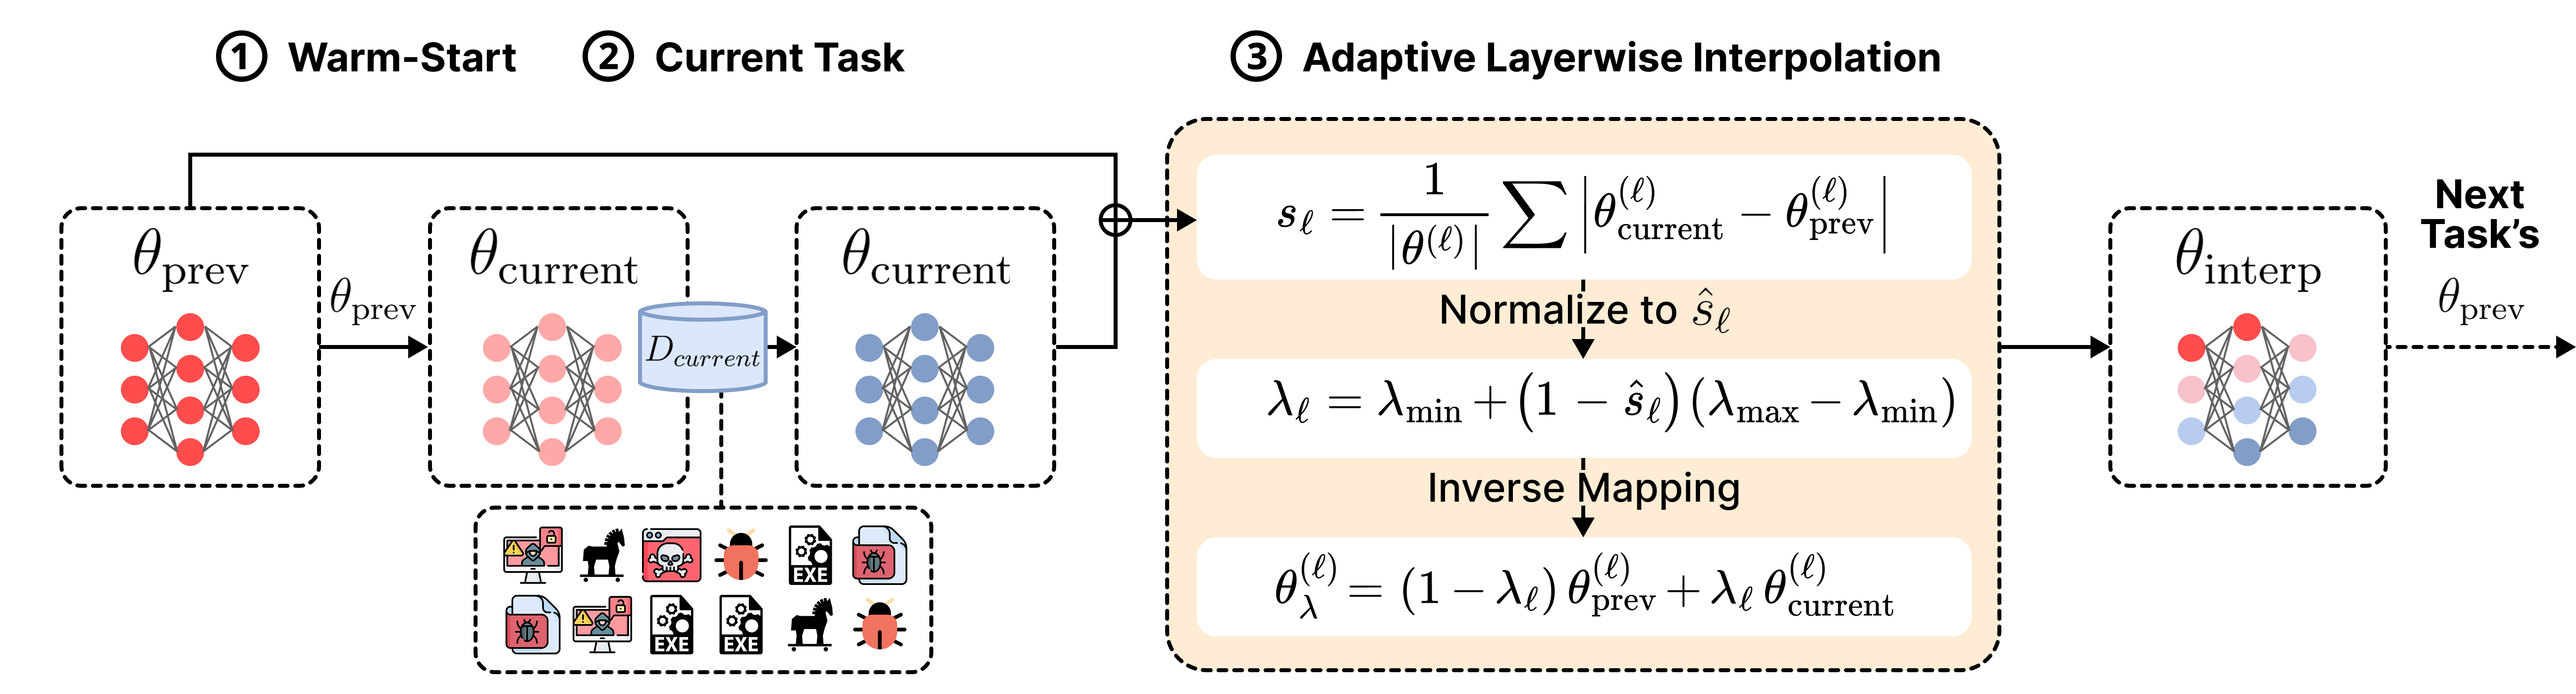 iqsec-lab/freemoca
Memory-free continual learning framework for malware classification using mode connectivity-based interpolation. Supports class-incremental and…
 idanshechter/cve-2017-13208-scanner
Python script using r2pipe to detect CVE-2017-13208 in Android libnetutils.so by checking for missing dhcp_size validation via static binary analysis.
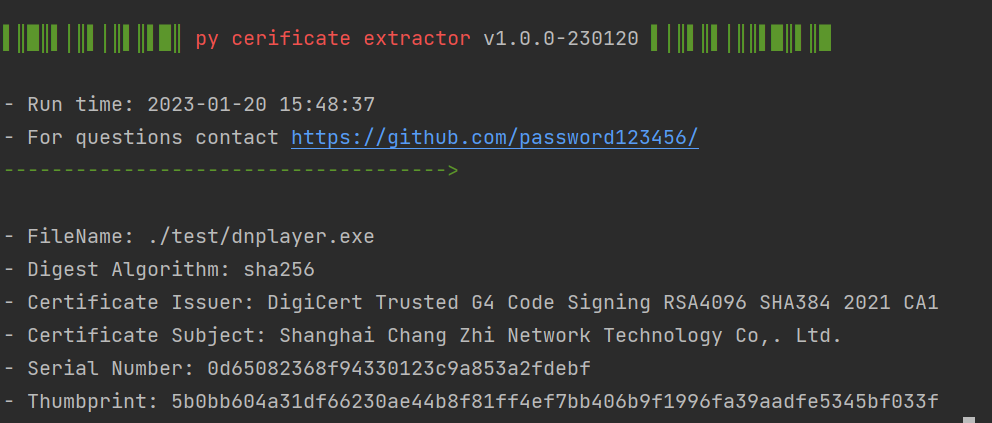 password123456/py_certificate_extractor
Extracts and exports certificate information from digitally signed PE files using Python and pefile, enabling forensic analysis of code-signing…
 anerruption/logic.net
A free and open-source .NET obfuscator using dnlib.

 nowsecure/r2frida
Radare2 and Frida better together.