
Skip to content
KitploitKITPLOIT
ToolsExploitsBlog
Log in
Submit
ToolsExploitsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

FeedsContactPrivacy© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories

Tools

AllAndroid SecurityAuthentication & AuthorizationCloud Infrastructure SecurityDefensive ToolsDisk ForensicsEmbedded Systems SecurityGeneral Purpose UtilitiesIndicator of Compromise (IOC) ManagementOSINT (Open Source Intelligence)Packet Sniffing & AnalysisPassword CrackingPenetration Testing FrameworksPhishing ToolsPrivilege EscalationReconnaissanceStatic AnalysisVulnerability ScannersWeb Vulnerability ScannersWi-Fi AuditingBluetooth SecurityContainer SecurityDynamic Analysis (Sandboxing)Encryption/Decryption ToolsExploit FrameworksIdentity ManagementiOS SecurityIoT SecurityMemory ForensicsNetwork MappingOSINT for Social EngineeringPassword AttacksPayload GenerationPersistence MechanismsPort ScanningStatic Code Analysis (SAST)Threat Feeds & AggregatorsVulnerability AnalysisWeb Proxies & InterceptionCode AnalysisDNS & Subdomain EnumerationDynamic Code Analysis (DAST)ExploitationHash AnalysisIDS/IPS EvasionImpersonation ToolsLateral MovementMobile App PentestingNetwork ForensicsReverse EngineeringRFID/NFC ToolsSCADA/ICS SecurityScripting & AutomationServerless SecurityShellcodeWeb Application ExploitationAPI Security TestingConfiguration AuditingData ExfiltrationDebuggersForensicsInformation GatheringMobile ForensicsNetwork Access ControlPost-ExploitationSecurity VirtualizationPhishingWAF BypassWeb SecurityFuzzingNetwork SecuritySteganographyWireless SecurityData RecoveryMalware AnalysisDigital ForensicsHardware HackingCryptographyCTFPenetration TestingCloud SecurityDevSecOpsMobile SecurityPrivacyCommand and ControlSocial EngineeringHardware SecurityUtilities & FrameworksHardware & IoT SecuritySecret DetectionBinary AnalysisThreat IntelligenceIdentity & Access Management (IAM)Supply Chain SecurityAuthenticationMachine LearningIntrusion DetectionPapers & ResearchMisconfigurationSubdomain EnumerationEmail HarvestingLearning & EducationAI-Assisted ReversingDNS FuzzingRed TeamingIncident ResponseCrawlerCurated ResourcesRemote Access ToolShellcode GenerationPayload DevelopmentRemote Access TrojanAPI SecurityAnti-BotFingerprint SpoofingCAPTCHA BypassEmail SecurityDNS AnalysisChaos EngineeringLearning Paths & CoursesContainer EscapeAI SecurityDatabase SecurityFirmware AnalysisAnomaly DetectionLog AnalysisAdversarial AttackBinary ExploitationLabs & Practice
NewestRelevanceMost popularRecently updated
53 results
shai-scan preview

shai-scan

GitHubdigi4care/shai-scan

Zero-dependency CLI scanner for npm/PyPI supply chain compromises. Detects compromised packages in lockfiles and system-level IOCs from attacks like…

code-analysisdevsecopsincident-response+6
5 months ago
malscore preview

malscore

GitHubraj3shp/malscore

Maliciousness scoring for Linux commands
anomaly-detectiondefensive-toolsincident-response+5
94 days ago
PortEx preview

PortEx

GitHubstruppigel/portex

Java library to analyse Portable Executable files with a special focus on malware analysis and PE malformation robustness
anomaly-detectionbinary-analysisforensics+3
5432 days ago
peframe preview

peframe

GitHubguelfoweb/peframe

PEframe is a open source tool to perform static analysis on Portable Executable malware and malicious MS Office documents.
forensicsmalware-analysisreverse-engineering+2
6285 years ago
PEpper preview

PEpper

GitHub0x0be/pepper

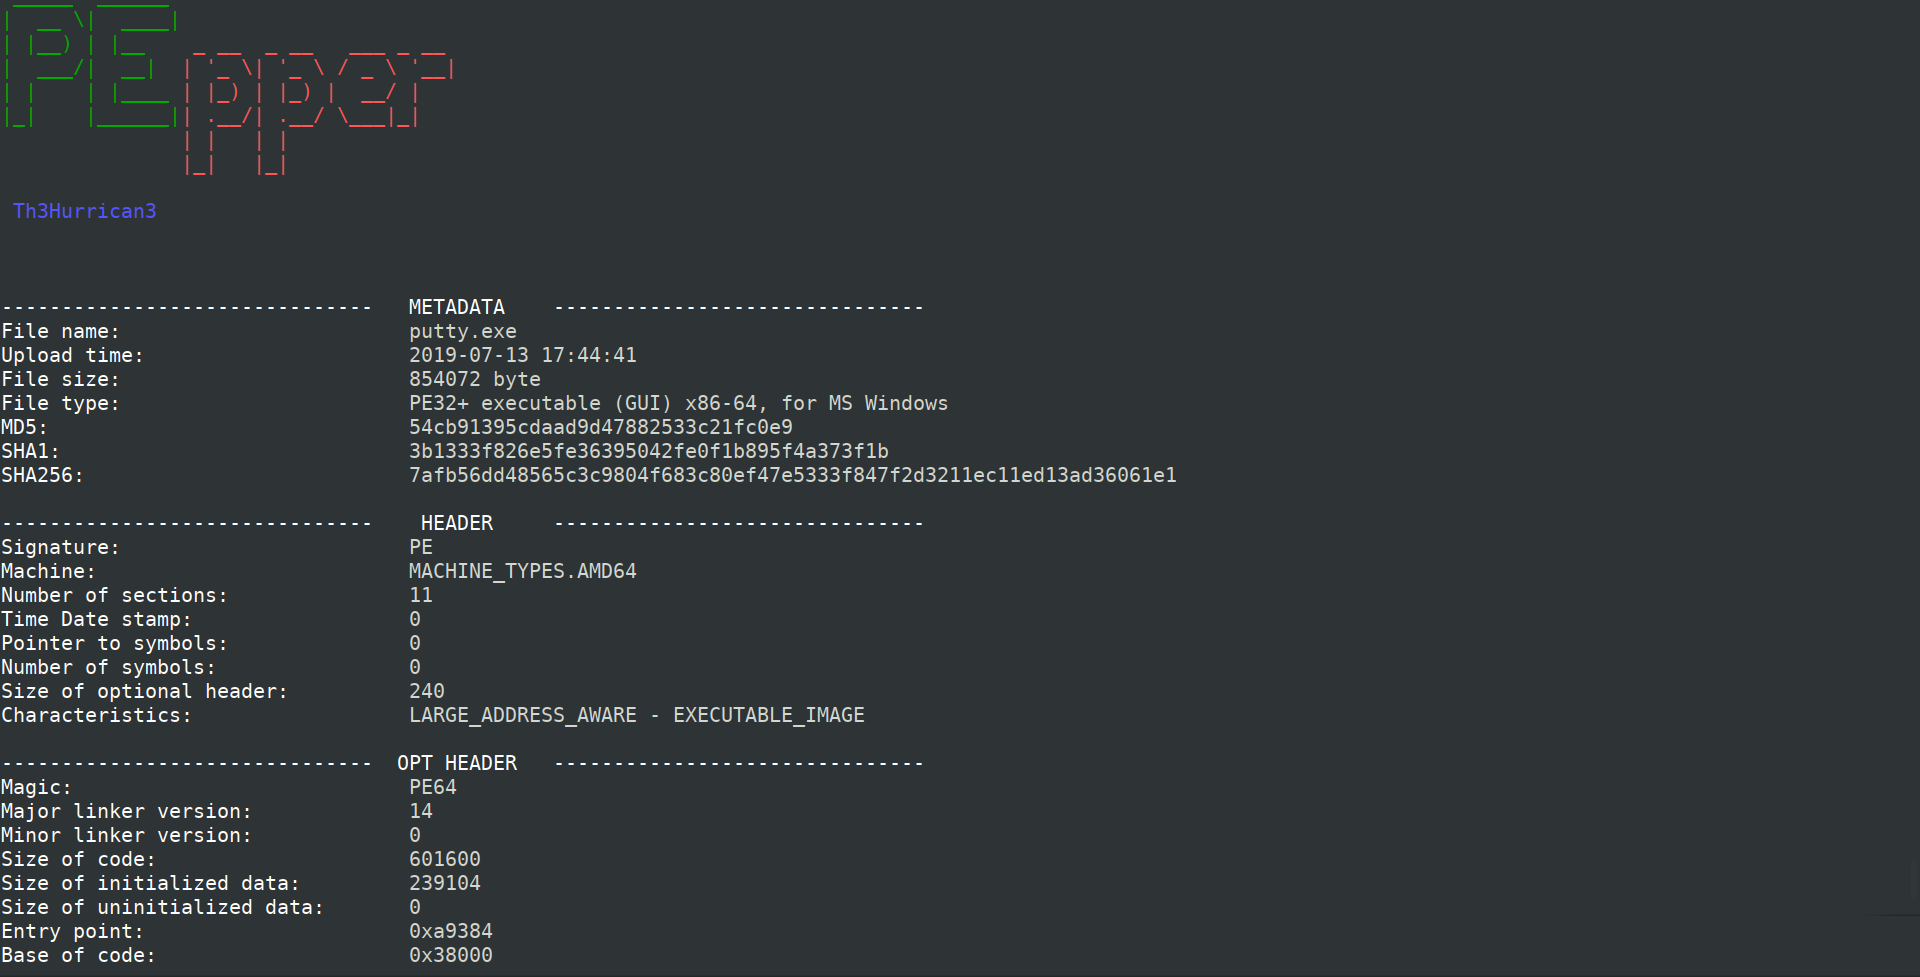
An open source script to perform malware static analysis on Portable Executable
binary-analysisforensicsmalware-analysis+1
3334 years ago
inhale preview

inhale

GitHubnetspooky/inhale

A malware analysis and classification tool.
binary-analysisforensicshash-analysis+3
1915 years ago
PortexAnalyzerGUI preview

PortexAnalyzerGUI

GitHubstruppigel/portexanalyzergui

Graphical interface for PortEx, a Portable Executable and Malware Analysis Library
binary-analysisforensicshash-analysis+3
1922 days ago
hacksguard preview

hacksguard

GitHubrhacknarok/hacksguard

A blazingly fast, multi-threaded TUI malware analysis tool built in Rust. Features deep PE parsing, YARA scanning, and heuristic risk scoring.
binary-analysisforensicsmalware-analysis+2
2151 month ago
nuitka-static-unpacker preview

nuitka-static-unpacker

GitHubdimareverse/nuitka-static-unpacker

Static-first research tool for unpacking Nuitka-compiled binaries: extracts constants, modules, recovers .pyc files, and generates analysis reports.
binary-analysisdata-recoveryforensics+3
1372 months ago
NoMoreXOR preview

NoMoreXOR

GitHubhiddenillusion/nomorexor

Tool to help guess a files 256 byte XOR key by using frequency analysis
binary-analysiscryptographyforensics+3
908 years ago
dotnetfile preview

dotnetfile

GitHubpan-unit42/dotnetfile

Python library for parsing CLR/PE metadata in .NET assemblies, exposing streams and hash fingerprints to support malware analysis and threat hunting.
binary-analysisforensicshash-analysis+4
1188 months ago
excelpeek preview

excelpeek

GitHubslaughterjames/excelpeek

Static analysis tool for investigating potentially malicious Microsoft Excel files, extracting metadata, macros, and embedded objects to aid digital…
digital-forensicsforensicsmalware-analysis+1
384 years ago
JarHunter preview

JarHunter

GitHubprophetcraft/jarhunter

JAR analysis tool for exploring, searching, and extracting specific classes from large JAR files with bytecode search, multi-selection extraction,…
binary-analysiscode-analysisdigital-forensics+5
87 months ago
qs_old preview

qs_old

GitHubtylabs/qs_old

Command line tool for scanning streams within office documents plus xor db attack
forensicsmalware-analysisstatic-analysis+1
1273 years ago
PETriage preview

PETriage

GitHubuky007/petriage

PETriage: A symbol-unified PE file reader for triage, built for multi-platform and multi-interface use.

anomaly-detectionbinary-analysisdigital-forensics+5
132 months ago
yara preview

yara

GitHubvirustotal/yara

The pattern matching swiss knife

forensicsmalware-analysisstatic-analysis+2
10.0k2 days ago
pe-bear preview

pe-bear

GitHubhasherezade/pe-bear

Portable Executable reversing tool with a friendly GUI

binary-analysisforensicsmalware-analysis+3
3.9k8 days ago
pefile preview

pefile

GitHuberocarrera/pefile

pefile is a Python module to read and work with PE (Portable Executable) files

binary-analysisforensicsmalware-analysis+3
2.1k11 days ago
Previous123Next