hexcymatix
 xoreaxeaxeax/hexcymatix
Visualizes repeated byte sequences in binary files to reveal hidden structure, supporting reverse engineering and pattern discovery without…
binary-analysisreverse-engineeringstatic-analysis
xoreaxeaxeax/hexcymatixVisualizes repeated byte sequences in binary files to reveal hidden structure, supporting reverse engineering and pattern discovery without…
 wolfssl/wolfcose
A fast, portable, and lightweight COSE + CBOR implementation for embedded systems. Supports PQC, FIPS 140-3, DO-178, and MISRA C. Powered by wolfSSL.
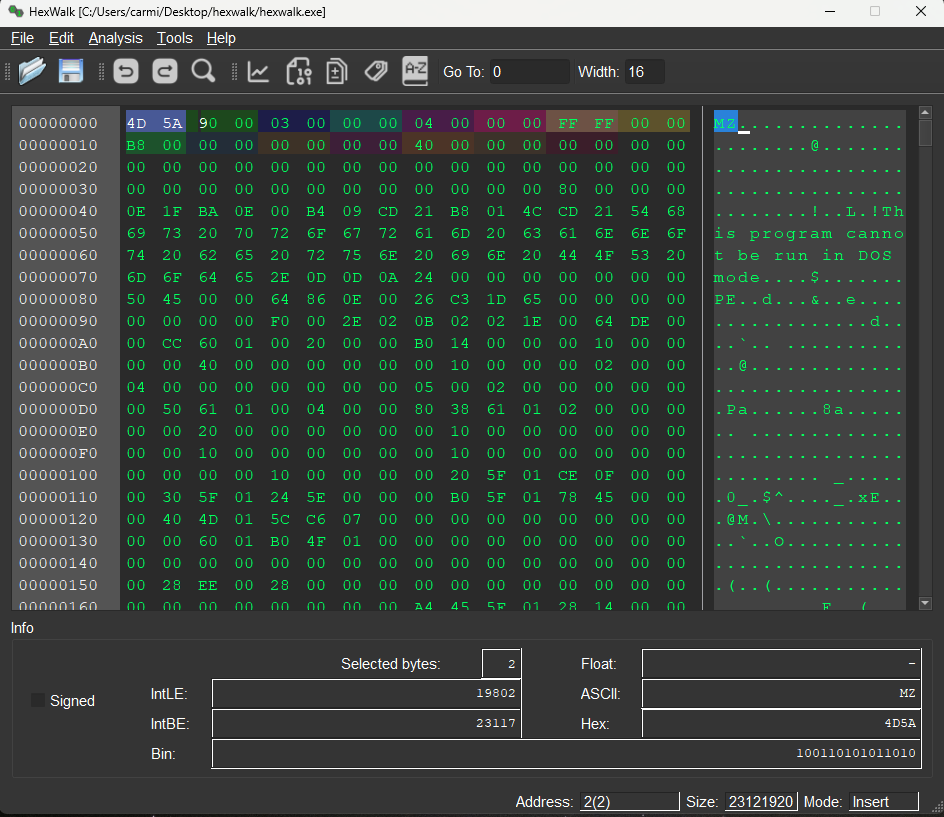 gcarmix/hexwalk
Hex Viewer/Editor/Analyzer compatible with Linux/Windows/MacOS
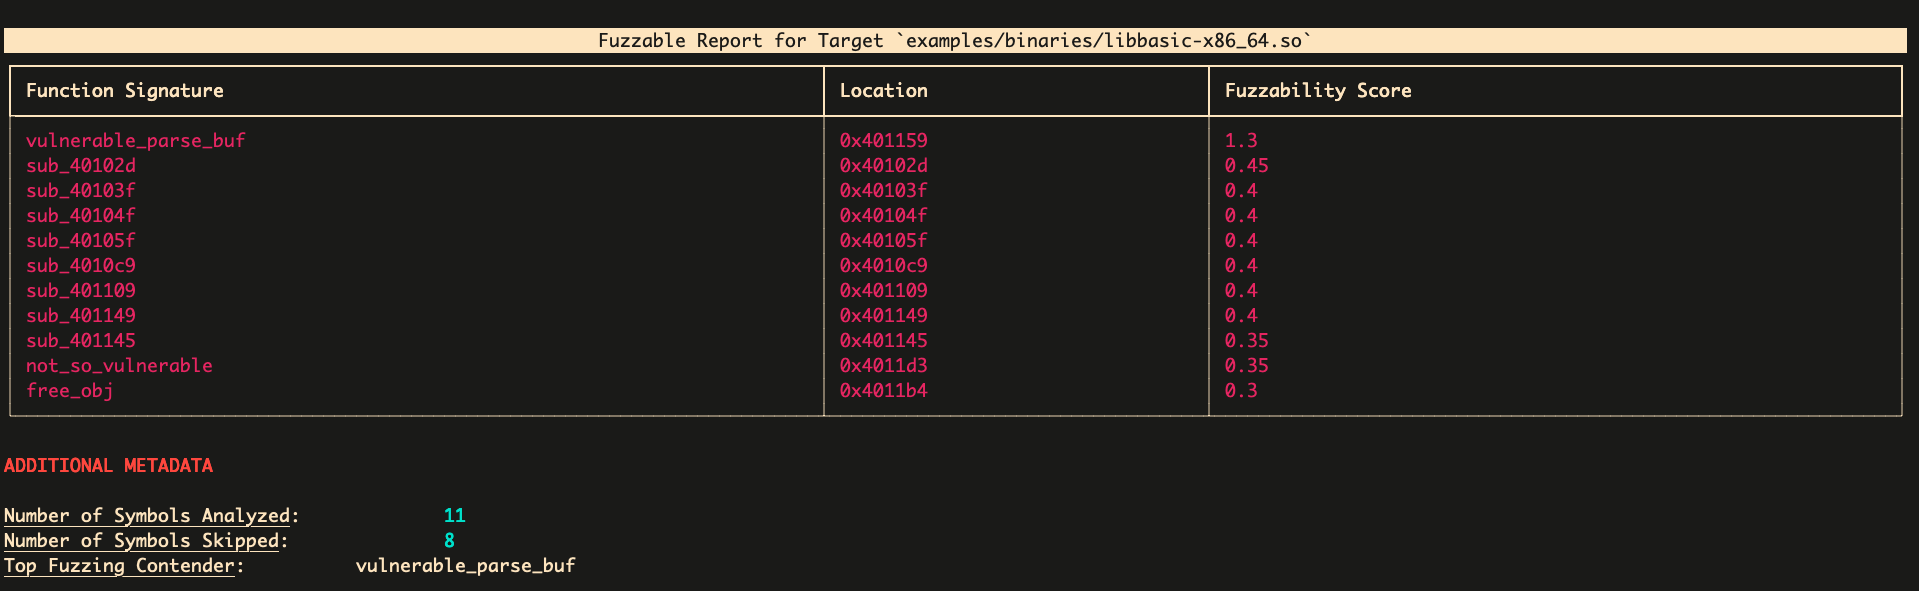 ex0dus-0x/fuzzable
Static analysis framework that identifies fuzzable function targets in source code and binaries, generates harness templates, and integrates with…
 synacktiv/dotniet
IDA Pro plugin that imports runtime-resolved symbols in .NET Native binaries, parsing SharedLibrary.dll and its PDB to restore missing imports for…
 jetbrains/fernflower
Decompiler from Java bytecode to Java, used in IntelliJ IDEA.
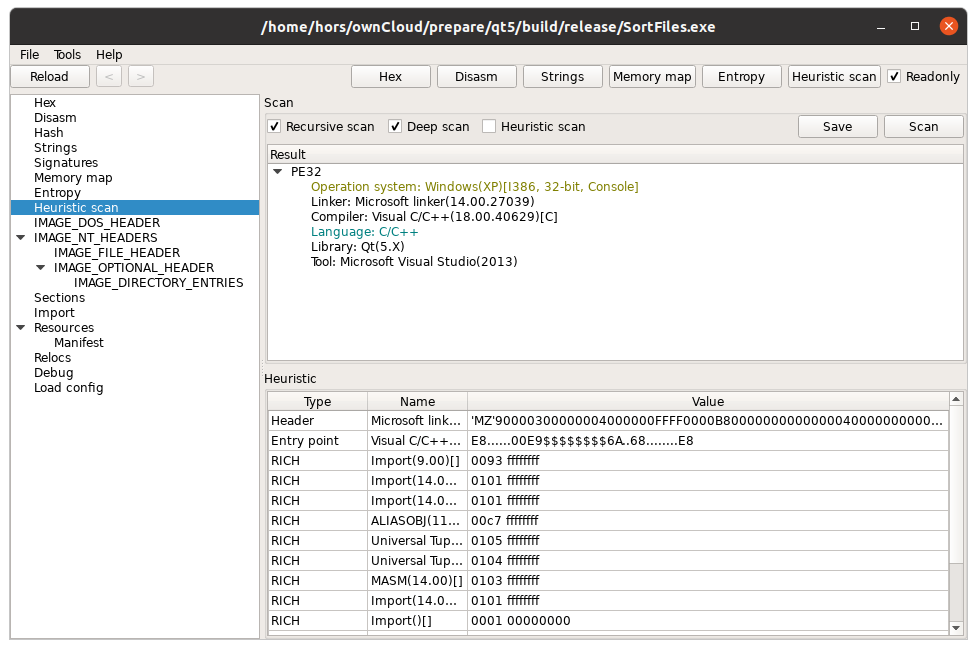 horsicq/xpeviewer
PE file viewer/editor for Windows, Linux and MacOS.
 rizinorg/rz-ghidra
Deep ghidra decompiler and sleigh disassembler integration for rizin
 keensecuritylab/binabsinspector
Static binary vulnerability scanner using abstract interpretation on Ghidra Pcode. Detects CWE classes like buffer overflows, use-after-free, and…
 nccgroup/susanrtti
Another RTTI Parsing IDA plugin
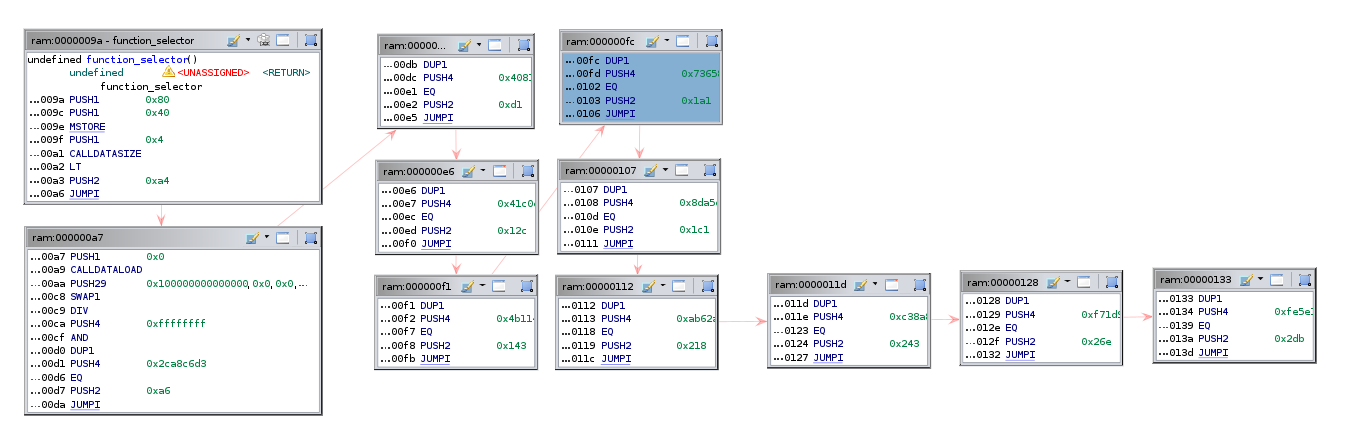 adelapie/ghidra-evm
Ghidra module for disassembling, decompiling, and analyzing Ethereum smart contract bytecode. Detects insecure instructions, extracts hidden methods,…
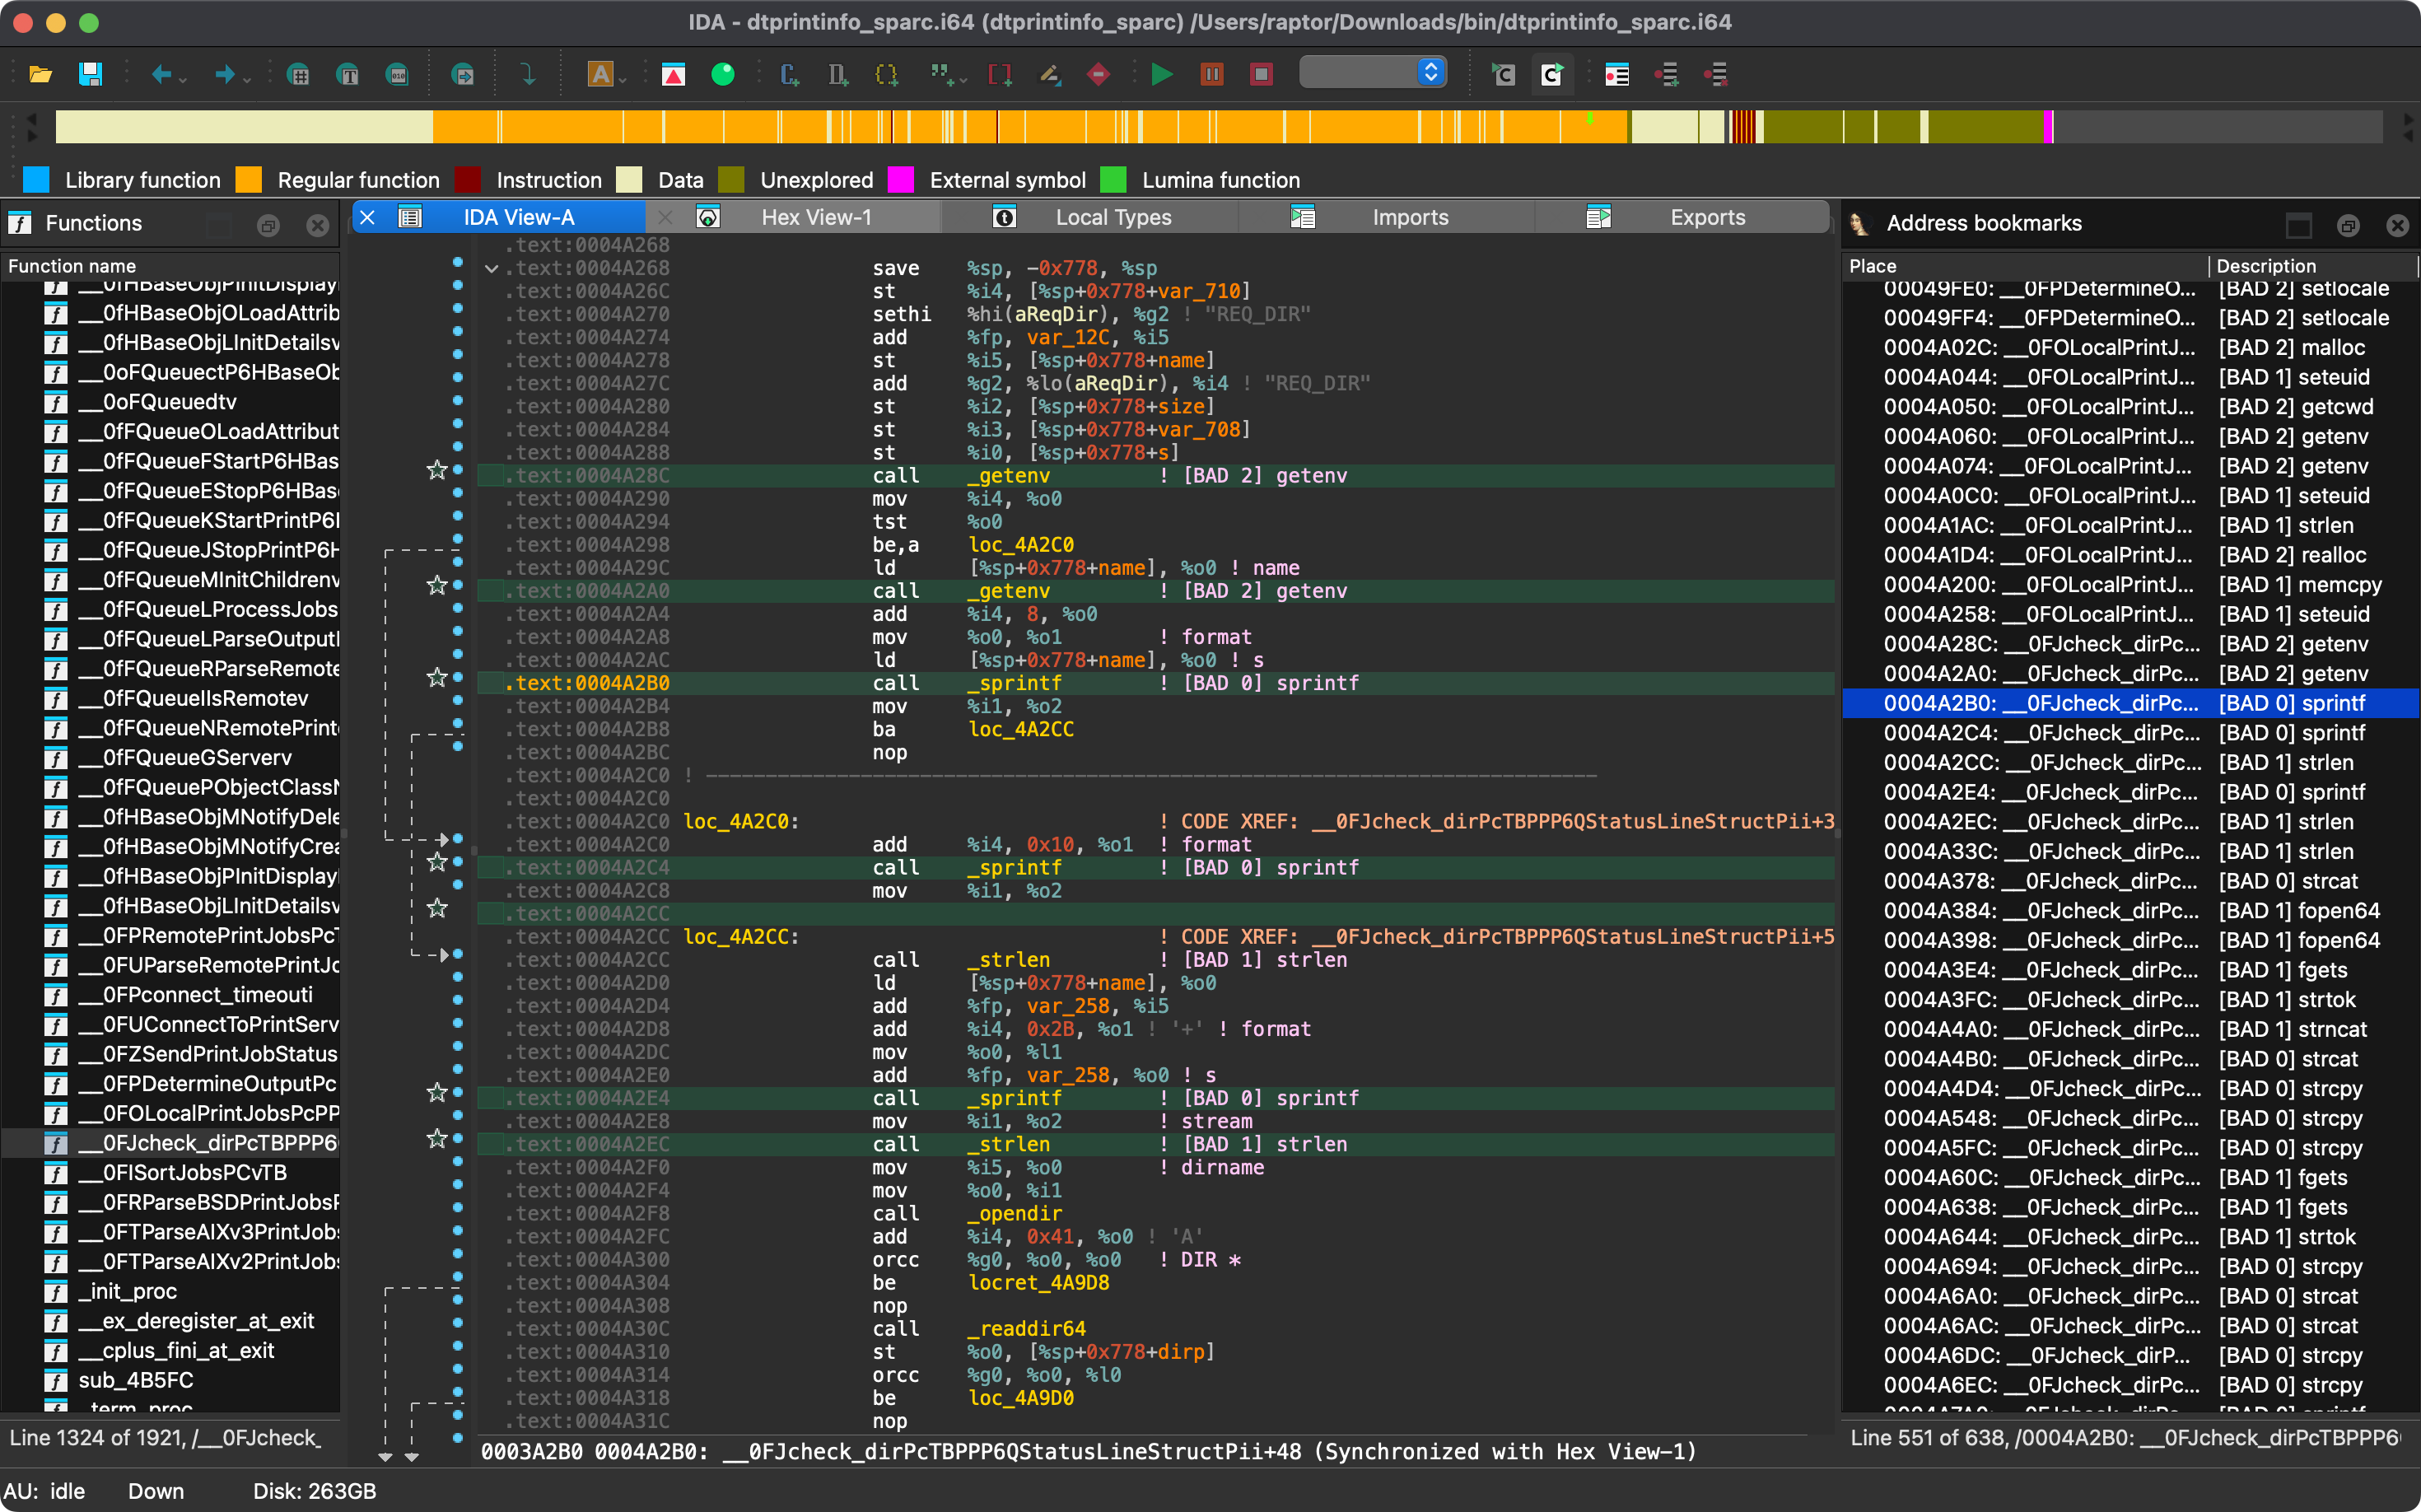 0xdea/rhabdomancer
Vulnerability research assistant that locates calls to potentially insecure API functions in a binary file.
 ea/xfg_analyzer
A Binary Ninja plugin that uses bruteforced XFG hashes to recover precise function prototypes
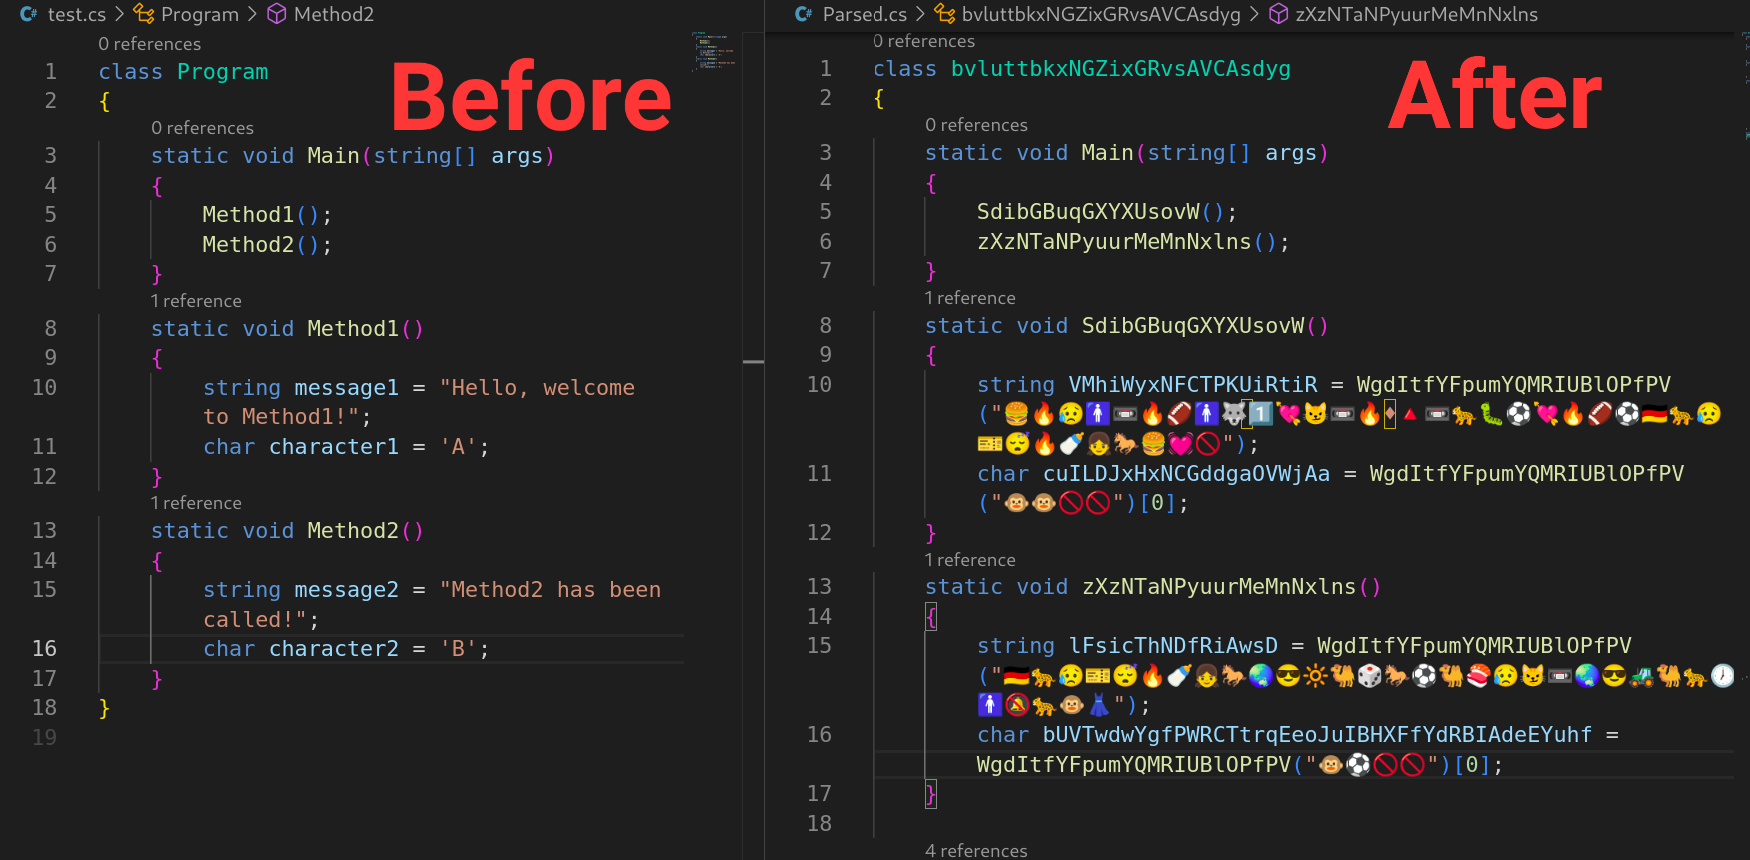 tomiwa-ot/emojify
C# source-code obfuscator that replaces character and string literals with emojis and randomizes class, interface, method, and variable names using…