
masq
 wattocyber/masq
Live recon and posture auditing for AI agent infrastructure: scans MCP configs, session logs, and APIs for secrets, poisoned catalogs, and CoT leaks.
ai-securityapi-security-testingconfiguration-auditing+6
wattocyber/masqLive recon and posture auditing for AI agent infrastructure: scans MCP configs, session logs, and APIs for secrets, poisoned catalogs, and CoT leaks.
 enriquenegri-cyberlaw/boa-cve-2009-4496-analysis
Defensive analysis of CVE-2009-4496 in Boa 0.94.14rc21, including source-code review, patch analysis, severity assessment, and ethical scope.
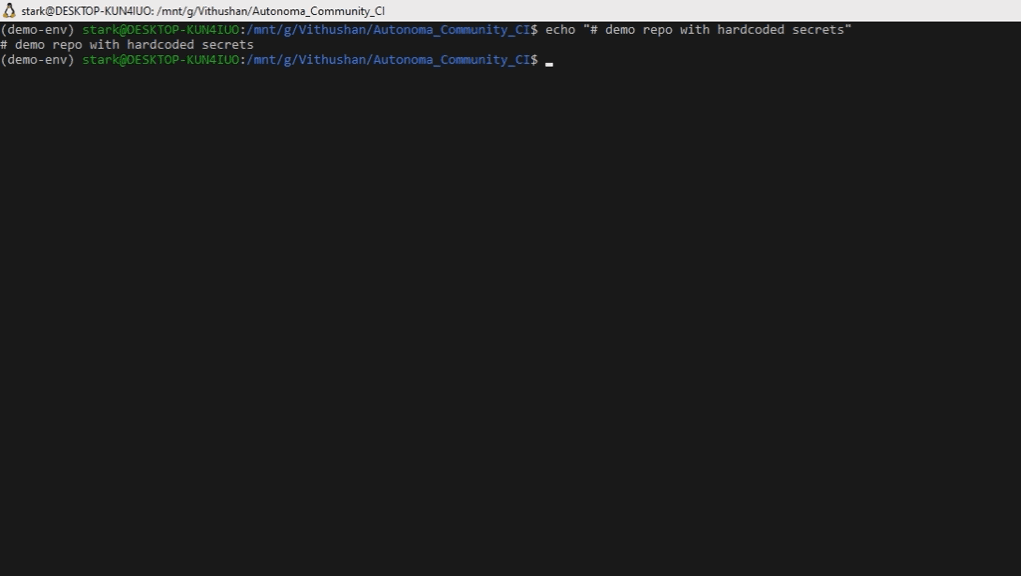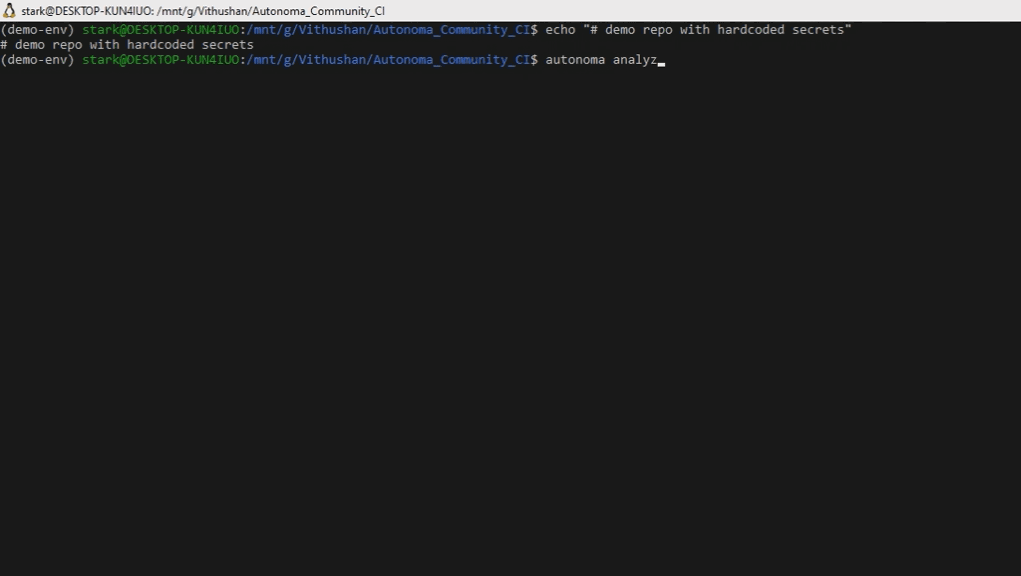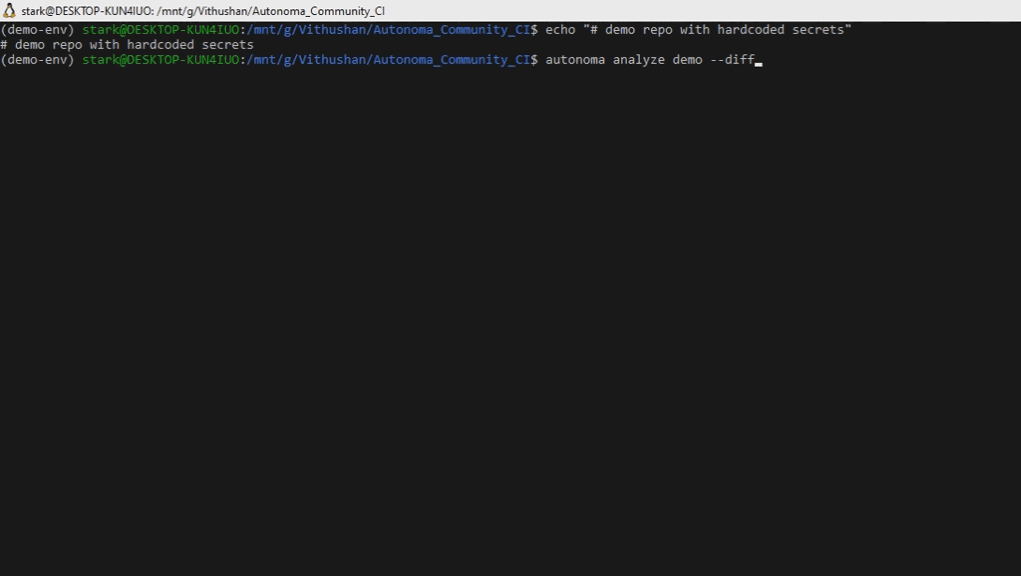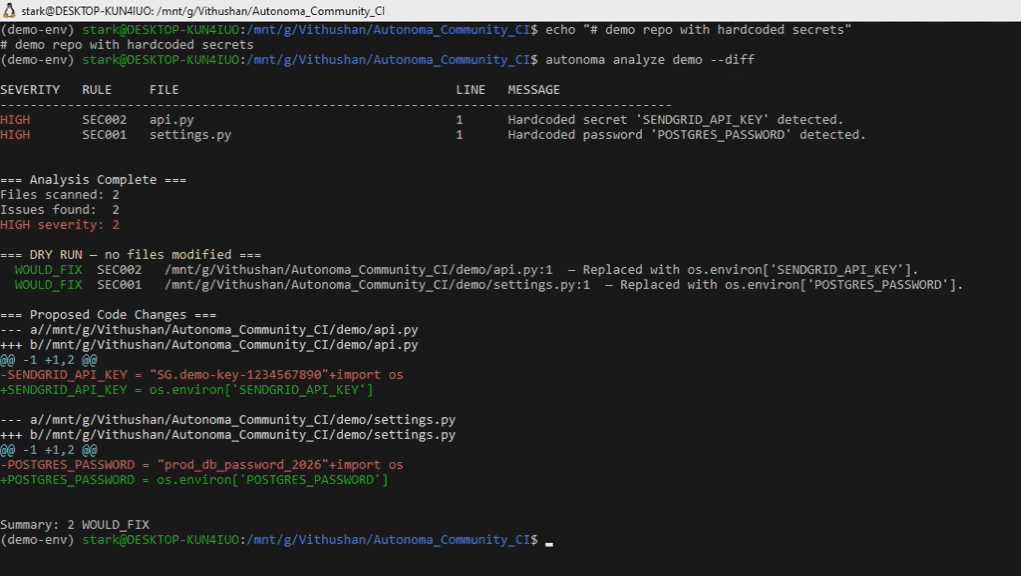 vihaaninnovations/autonoma
Detects and auto-fixes hardcoded secrets in Python repos — refuses when the fix could break your code
 divyanshukumar0014/shipproof
Automated SOC 2 change management for GitLab CI.
 nccgroup/formal_np1sec
Formalizing np1sec using Tamarin and other FM (see https://github.com/equalitie/np1sec)
 shivang0/guardmodel
GitHub Action that scans ML model files for malicious code and security vulnerabilities
 realityone/cve-2026-42945-scan
Scan your NGINX configuration to determine whether it is affected by CVE-2026-42945.
 jacklosingheart/cve-2024-51132-poc
Proof-of-concept exploit for CVE-2024-51132, an XML External Entity (XXE) injection vulnerability in HAPI FHIR core libraries, enabling SSRF and…
 gagaltotal/cve-2026-42533-nginx
CVE-2026-42533 Nginx
 sonarsource/sonarcloud-scan
A Bitbucket Pipe to trigger SonarCloud analysis
 abubakar-shahid/cve-2024-36886
Academic research on N-Day Linux kernel vulnerabilities, analyzing CVE-2024-36886 in the TIPC networking subsystem, lifecycle, impact, and mitigation…
 fysac/cve-2019-20326
Heap buffer overflow in GNOME gThumb and Linux Mint Pix
 mohammadnassiri/yaasa
Yet Another APK Static Analyzer
 trerb/ai-ide-config-guard
Scan a repo for AI-IDE config files that can trigger RCE via Claude Code hooks, Cursor rules, MCP auto-registration. Detects CVE-2025-59536,…
 scabench/fastjson-tp1fn1
a scenario based on CVE-2022-25845 yielding a TP for metadata based SCA but a FN if the callgraph is used
 trailofbits/manticore
Symbolic execution tool
 anchore/anchore-engine
A service that analyzes docker images and scans for vulnerabilities
 endrazine/rocq-cve-poc-12155
CVE-2020-37268 — Rocq/Coq Print Assumptions Omits Unsafe Universe Checking via Parameter Inline