external_libavc_AOSP10_r33_CVE-2021-0325

C-based vulnerability analysis and exploitation toolkit targeting AOSP libavc heap overflow (CVE-2021-0325) with static code analysis capabilities.

C-based vulnerability analysis and exploitation toolkit targeting AOSP libavc heap overflow (CVE-2021-0325) with static code analysis capabilities.

Educational proof-of-concept demonstrating SQL injection via dynamic aliases in Django's annotate() and alias() methods (CVE-2025-57833). Includes…

Detailed technical analysis of CVE-2026-47777, a high-severity authorization bypass in Mastodon's Featured Collections federation pipeline, including…

Detect-only scanner for CVE-2026-42945 (NGINX Rift), a heap overflow in ngx_http_rewrite_module. Version detection + nginx.conf pattern analysis.…

cabin partial analysis

This repo stores necessary files for the analysis blog which will come soon

Technical analysis of CVE-2025-66628, an integer overflow in ImageMagick's TIM parser leading to out-of-bounds reads, with root cause, exploitation…

Educational lab demonstrating JavaScript expression sandbox escape techniques and patch evolution through multiple vulnerable sandbox versions, with…

Security research and reproduction of CVE-2025-5548: A stack-based buffer overflow in FreeFloat FTP Server 1.0. Includes binary analysis, crash…

Static Malware Analysis of Follina (CVE-2022-30190) from Blue Team Labs Online

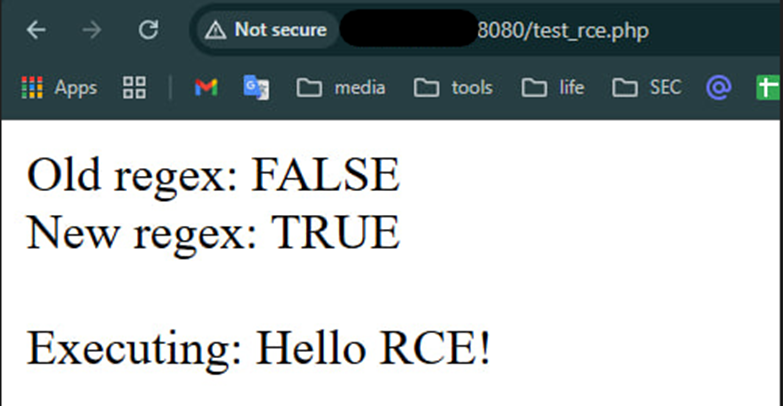
Educational CVE-2024-12877 exploit demo for PHP Object Injection in GiveWP WordPress plugin. Includes root cause analysis, regex bypass techniques,…

CodeQL-based analysis of CVE-2025-55182 prototype pollution vulnerability in React Server Components, with exploit POC and static detection queries…

Detailed analysis of CVE-2025-61686, a path traversal vulnerability in React Router's file session storage, including root cause, attack scenarios,…

Technical deep dive into Apache Log4j2 JNDI injection vulnerability. Features static code analysis, patch comparison, attack vectors (LDAP/RMI/DNS),…

Step-by-step static malware analysis of a Follina (CVE-2022-30190) exploit document, covering file extraction, VirusTotal correlation, MITRE ATT&CK…

AI powered security analysis extension for Mobile Security Framework MobSF

Java XML serialization library with a focus on the CVE-2013-7285 deserialization vulnerability, providing source code, binaries, and documentation…

Public advisory and technical analysis for CVE-2026-36590, a NanoMQ v0.24.9 denial-of-service vulnerability.