

work1-secure-api
 ght657/work1-secure-api
HDU IS Work 1 - Secure REST API (Flask) with CI/CD (pytest + bandit + pip-audit) and CVE-2018-17246 analysis
api-securityauthentication-authorizationdevsecops+7
ght657/work1-secure-apiHDU IS Work 1 - Secure REST API (Flask) with CI/CD (pytest + bandit + pip-audit) and CVE-2018-17246 analysis
 c2sp/wycheproof
Project Wycheproof tests crypto libraries against known attacks.
 open-policy-agent/conftest
Write tests against structured configuration data using the Open Policy Agent Rego query language
 tc4dy/cve-2026-57821-poc-exploit
🔐 CVE-2026-57821 - Apache Fineract SQL Injection Toolkit 📚 Two Python scripts for authorized security testing: verifier.py (safe detection, no…
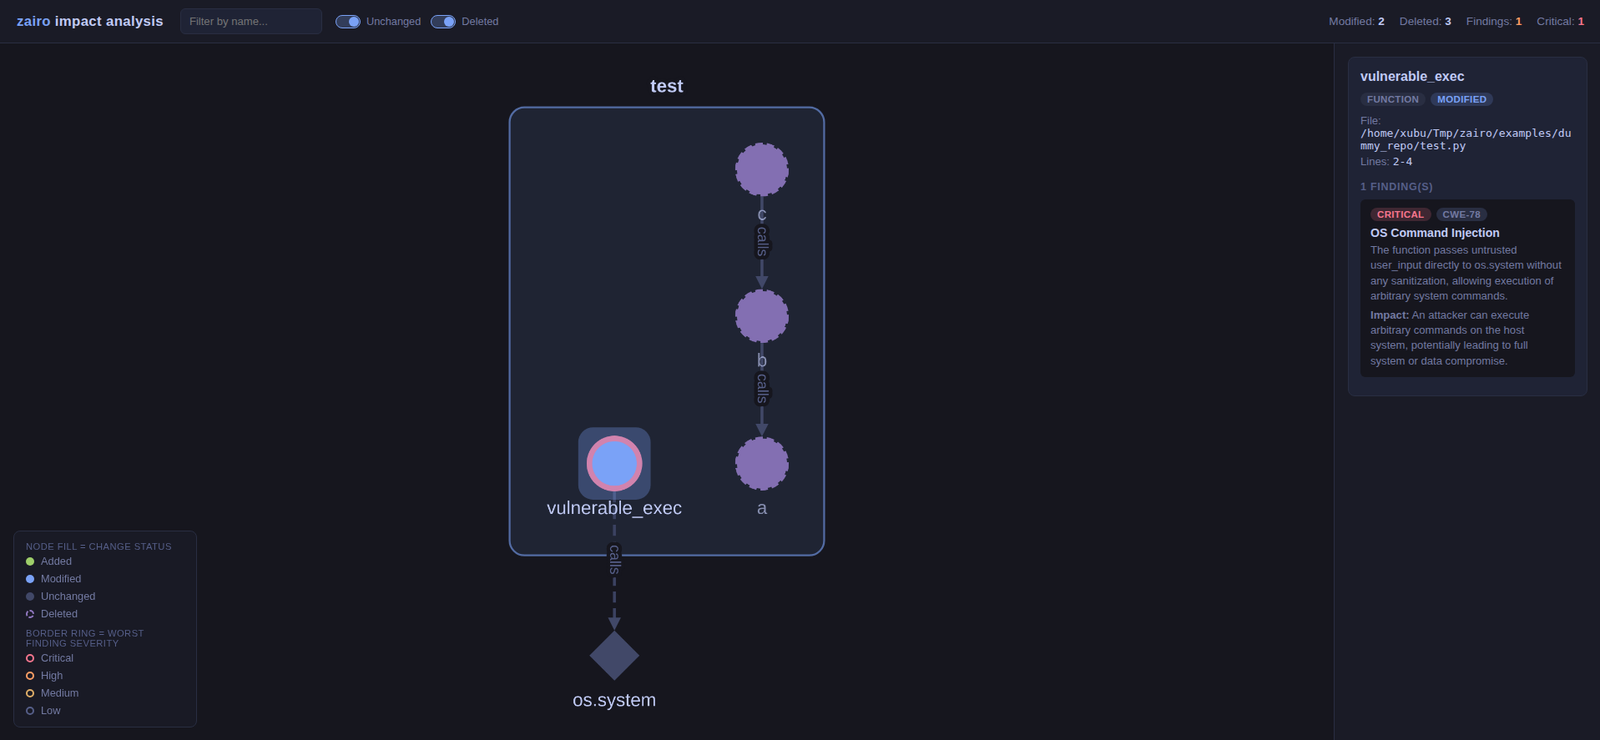 iamavu/zairo
Scans code diffs with context to build an impact graph and uses LLMs to find vulnerabilities, supporting multi-repo scans and CI gating with SARIF…
 seqra/cve-2026-58138
Reproduction kit for CVE-2026-58138, an unauthenticated RCE in Conductor. Includes OpenTaint static analysis rules, isolated tests, SARIF results,…
 hiteshgorana/susvibes-jupyter-server-cve-2026-35397
Benchmark task for reimplementing a masked path-resolution fix in Jupyter Server, with functional and hidden security tests to evaluate…
 l33tdawg/aether
AI Smart Contract Security Analysis and PoC Generation Framework
 dani33339/tough-cookie-v2.5.0-patched
Patched tough-cookie v2.5.0 fixing CVE-2023-26136 prototype pollution vulnerability with Object.create(null) in MemoryCookieStore, including exploit…
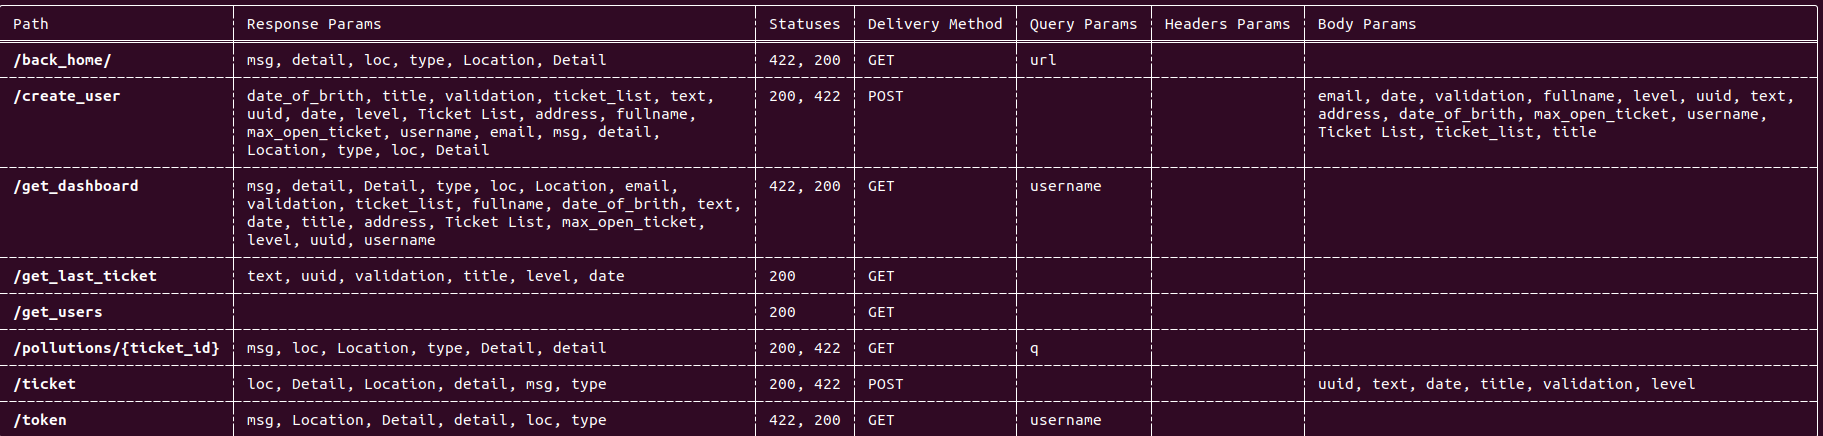 blst-security/cherrybomb
CLI tool that audits OpenAPI specifications, validates them against best practices, and runs automated security tests to detect vulnerabilities and…
 globocom/huskyci
Performing security tests inside your CI
 filipsedivy/cve-2020-15227
Python-based checker for CVE-2020-15227 that tests Nette applications for remote code execution vulnerabilities via file_put_contents and shell_exec…
 aquasecurity/scan-cve-2018-8115
CLI tool that verifies Docker images for CVE-2018-8115 by checking layers for malicious files, helping ensure safe pulls from Docker Hub.