

grype
 anchore/grype
A vulnerability scanner for container images and filesystems
container-escapecontainer-securitydevsecops+4
anchore/grypeA vulnerability scanner for container images and filesystems
 anchore/syft
CLI tool and library for generating a Software Bill of Materials from container images and filesystems

 horsicq/detect-it-easy
Program for determining types of files for Windows, Linux and MacOS.
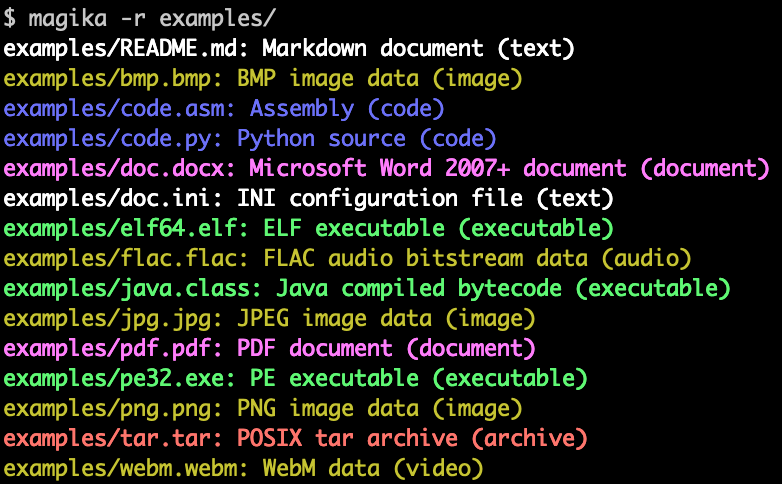 google/magika
Fast and accurate AI powered file content types detection
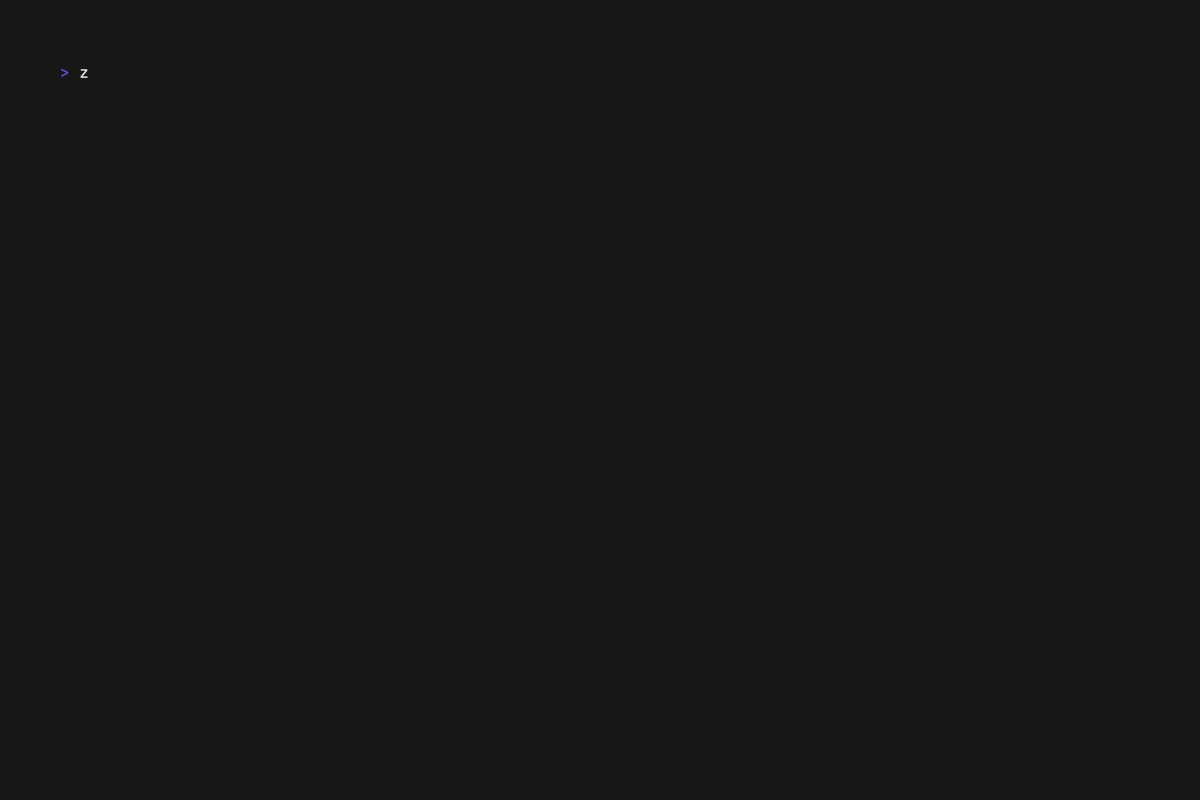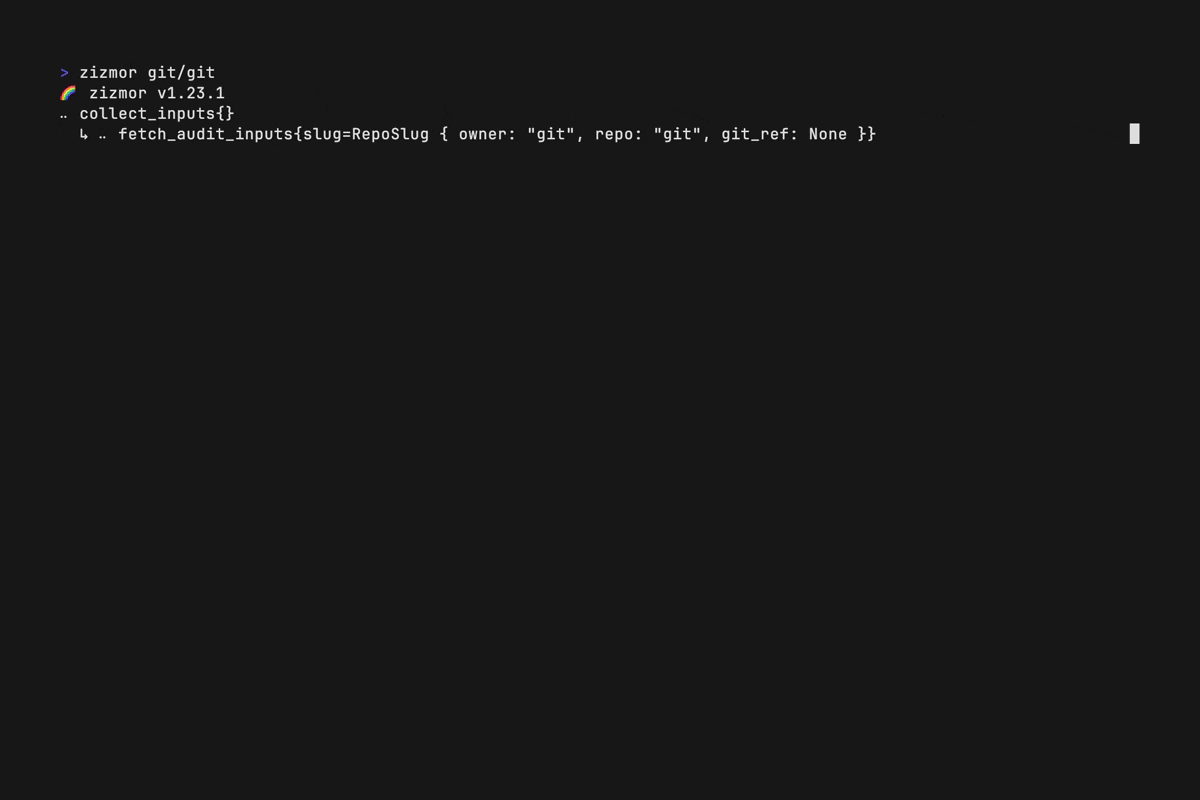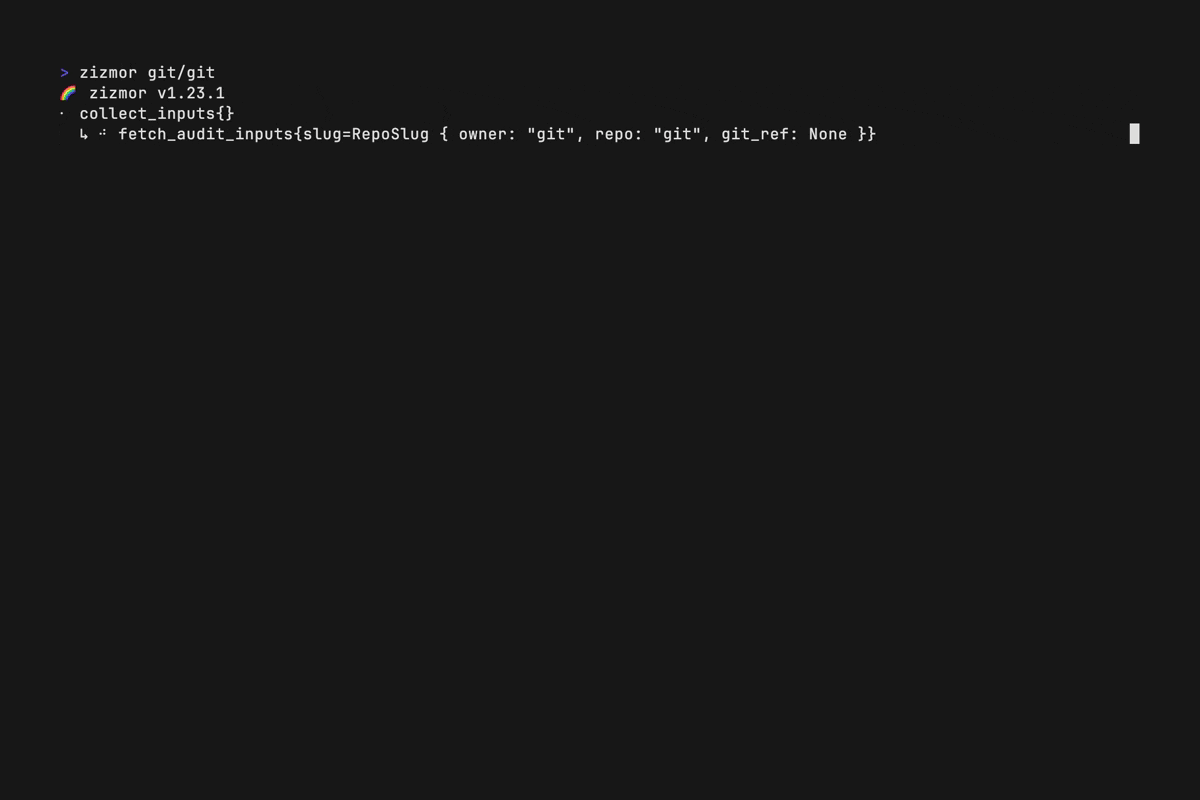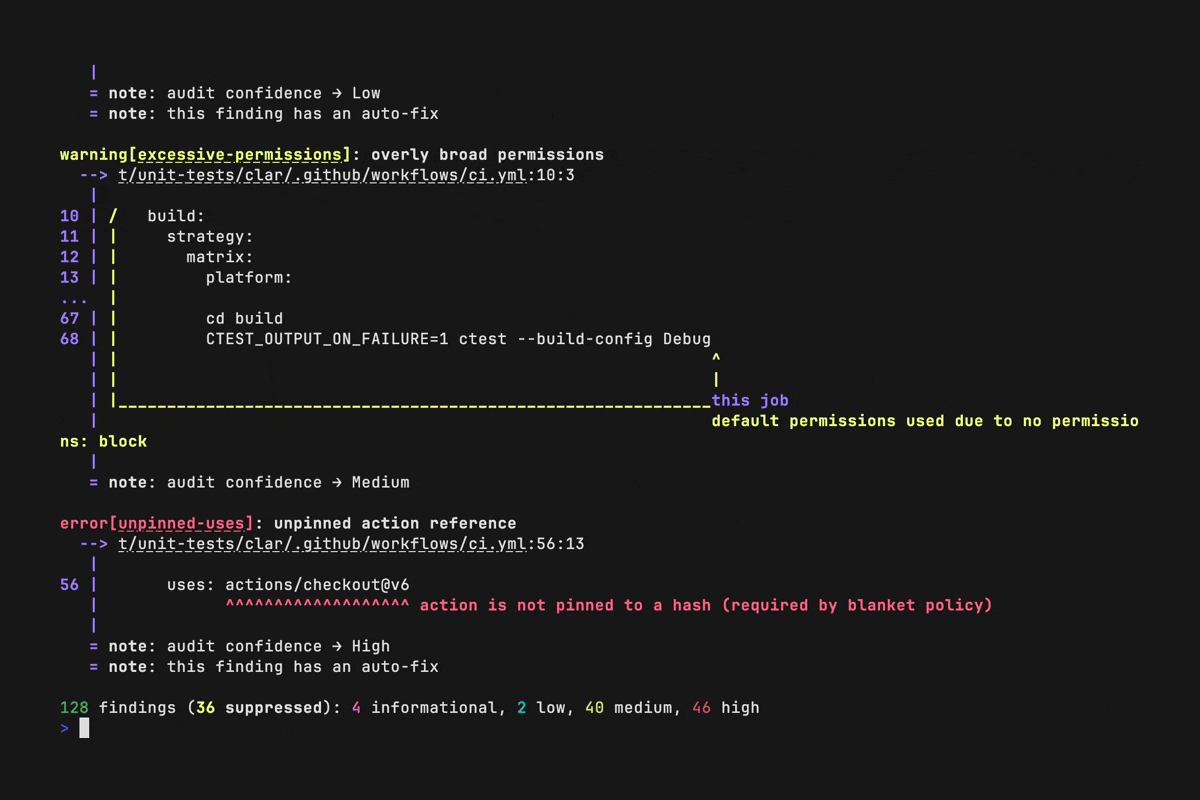 zizmorcore/zizmor
Static analysis tool for CI/CD systems that detects and fixes security issues in GitHub Actions, Dependabot, and pre-commit configurations, including…
 mongodb/kingfisher
Detect secrets + live validation. Map blast radius. Revoke fast. Use the CLI or embed in Rust and Python.
 secretlint/secretlint
Pluggable linting tool to prevent committing credential.
 hiepler/euconform
EU AI Act Compliance Tool - Risk classification and bias testing
 youkyi/pki-toolbox
Client-side PKI toolbox that decodes X.509, CSR, chain, CRL, PKCS#7 and PKCS#12 artifacts, views ASN.1, converts formats, and generates self-signed…
 facebook/infer
A static analyzer for Java, C, C++, and Objective-C
 loadingalias/rscrypto
Rust cryptography w/ zero required deps: hashes, checksums, MACs, KDFs, password hashing, AEADs, signatures, RSA, key exchange, ML-KEM, and ML-DSA.…
 skylot/jadx
Command-line and GUI tool for decompiling Android Dex and APK files into readable Java source code, with resource decoding, deobfuscation, and Smali…
 bridgecrewio/checkov
Static analysis tool for infrastructure as code that detects cloud misconfigurations, vulnerabilities, and secrets across Terraform, Kubernetes,…
 abraxas/sqlite-fj-using-auth
SQLite 3.53.4 - High - Local - Privilege leftover - FULL JOIN USING skips sqlite3AuthRead
 stackrox/kube-linter
KubeLinter is a static analysis tool that checks Kubernetes YAML files and Helm charts to ensure the applications represented in them adhere to best…
 tamarin-prover/tamarin-prover
Symbolic verification tool for security protocols using multiset rewriting and constraint solving to prove secrecy, authentication, and equivalence…
 openbreach/canop
Static analysis CLI that scans AI-generated code for vulnerabilities like SQL injection, unsafe reflection, and hardcoded secrets, with SARIF export…