
wycheproof
 c2sp/wycheproof
Project Wycheproof tests crypto libraries against known attacks.
code-analysiscryptographyeducation+3
c2sp/wycheproofProject Wycheproof tests crypto libraries against known attacks.
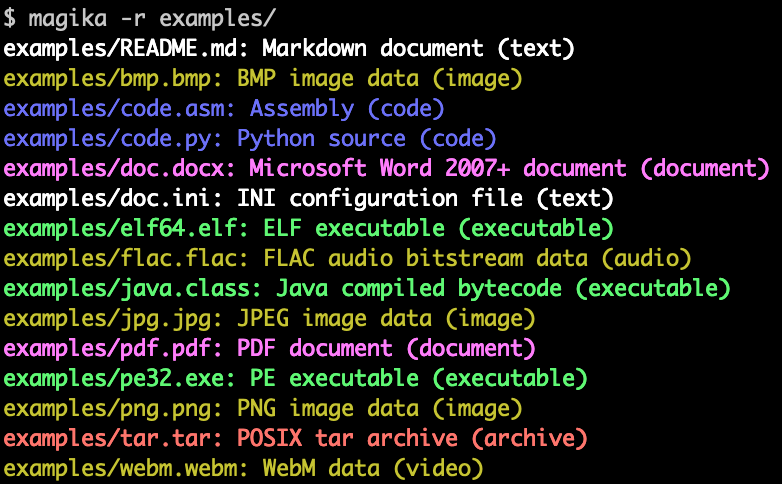 google/magika
Fast and accurate AI powered file content types detection
 vighnesh91/omnisec-hex
Browser-local security monorepo with six modules for mobile APK/IPA triage, client-side DAST fuzzing, OSINT directories, offline AI threat scoring,…
 mandiant/flare-floss
FLARE Obfuscated String Solver - Automatically extract obfuscated strings from malware.
 jsonpath-plus/jsonpath
A fork of JSONPath from http://goessner.net/articles/JsonPath/
 ambitsecurity/jshound
Find every API request a web app makes, from the JavaScript it ships: method, URL, body, headers and GraphQL operations. One command.
 affolter-engineering/xssearch
Rust-based XSS scanner with context-aware payload selection, WAF detection and bypass, crawling, blind XSS callbacks, and static DOM sink analysis.
 eset/malware-research
Code written as part of our various malware investigations
 ejfkdev/dj
Extracts dynamically loaded JavaScript files by statically analyzing website HTML and JS, detecting webpack chunks, import() lazy loading, and source…
 shinthink/blitzstrike
MCP server packaging a three-tier penetration-testing methodology: attack-surface reconnaissance, source-to-sink static analysis, and live finding…
 squeeze440/gortex-poc
PoC — symlink following to out-of-repo content disclosure via search_text in Gortex (GHSA-6vhf-4wcm-2r83, CVE-2026-87003, CVSS 5.5).
 bio/vue-template-compiler-patched
Patched Vue 2.7.16 template compiler with fixes for CVE‑2024‑6783 and CVE-2024-9506
 zeze-zeze/ioctlance
A tool that is used to hunt vulnerabilities in x64 WDM drivers
 sassoftware/jackson
This repository provides a comprehensive security remediation of denial-of-service and allocation of resources without limits or throttling security…
 teycir/diffcatcher
A Rust CLI tool that recursively discovers Git repositories, captures state changes, generates diffs, extracts code elements with full snippets, and…
 shoucheng3/jenkinsci__script-security-plugin_cve-2023-24422_1228.vd93135a_2fb_25
Jenkins plugin providing script approval workflows and Groovy sandboxing to enforce secure script execution, with ACL-aware permission checks and…
 jenish-sojitra/jsanalyzer
Burp Suite extension for JavaScript static analysis: extracts API endpoints, URLs, secrets, and emails with noise filtering for web security testing.
 heiheishushu/rsc_detect_cve-2025-55182
Detects whether a website uses React Server Components (RSC) or Next.js, aiding in vulnerability assessment for CVEs like CVE-2025-55182.