
DOMPurify
 cure53/dompurify
DOMPurify - a DOM-only, super-fast, uber-tolerant XSS sanitizer for HTML, MathML and SVG. DOMPurify works with a secure default, but offers a lot of…
api-securitycode-analysisdefensive-tools+3
17.4k
cure53/dompurifyDOMPurify - a DOM-only, super-fast, uber-tolerant XSS sanitizer for HTML, MathML and SVG. DOMPurify works with a secure default, but offers a lot of…
 studiomeyer-io/mcp-stdio-shellguard
Defense-in-depth bundle for MCP stdio servers: drop-in guardExec/guardSpawn wrappers, AST audit CLI, reference MCP server. Closes the Ox-Security…
 peterlinccl/vulnerability-dlink-cve-2025-14659
Static analysis (Ghidra) and custom packet-crafting (Scapy) demonstrating a root-level DHCP command injection vulnerability (CVE-2025-14659) in…
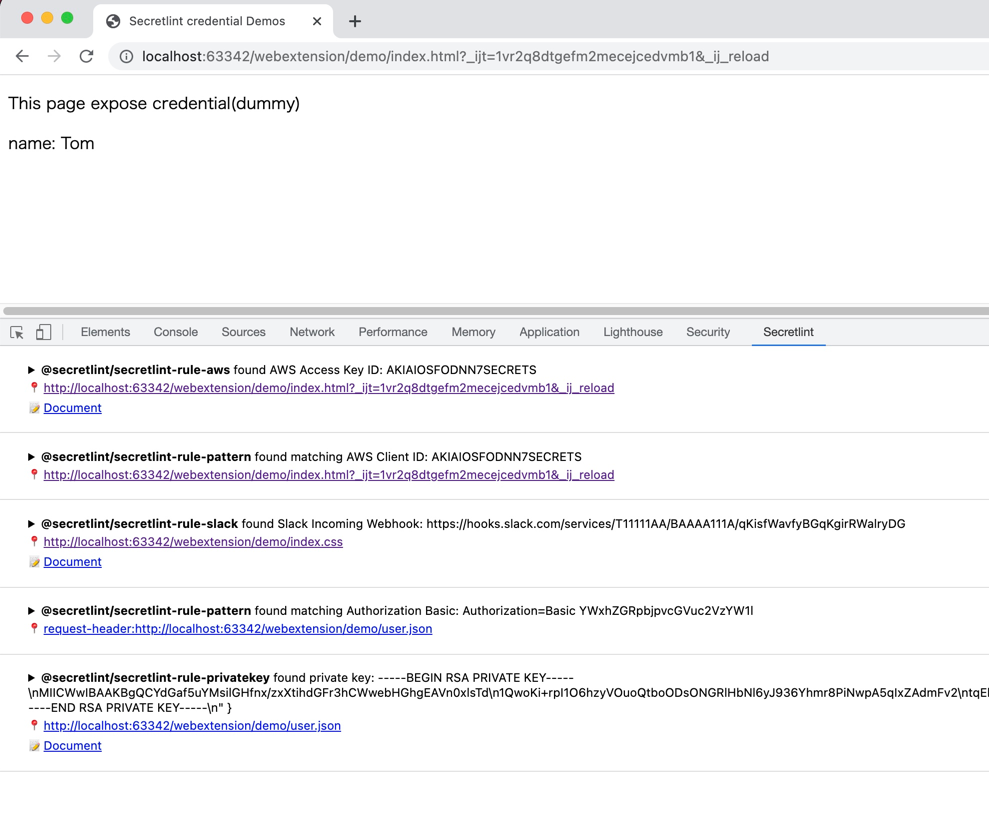 secretlint/secretlint
Pluggable linting tool to prevent committing credential.
 seifreed/yaraast
A powerful Python library and CLI tool for parsing, analyzing, and manipulating YARA rules through Abstract Syntax Tree (AST) representation

 niclas-zone/ci/gitleaks
CI component for Gitleaks SAST tool that scans git repositories for hardcoded secrets, API keys, and tokens with custom and remote configuration…
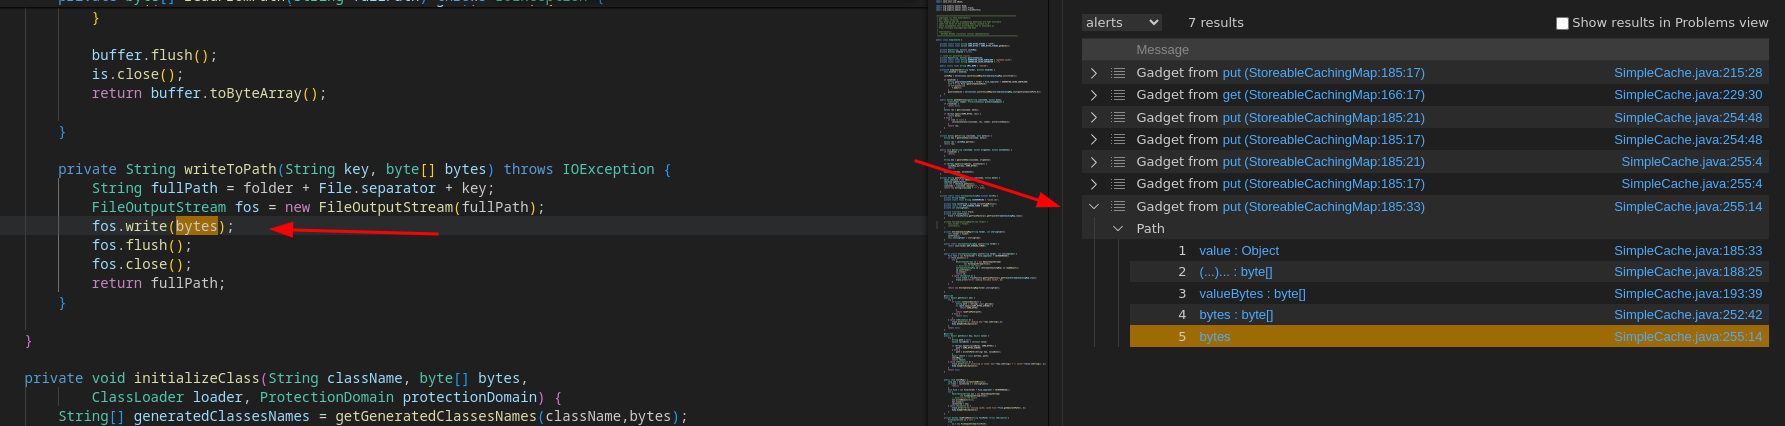 synacktiv/qlinspector
Finding Java/C# gadget chains with CodeQL
 boratanrikulu/gobee
Write your BPF programs in Go, not C. gobee transpiles a Go subset to BPF C and generates typed cilium/ebpf bindings.
 shoucheng3/jenkinsci__workflow-cps-plugin_cve-2022-25173_2646-v6ed3b5b01ff1
Exploit for CVE-2022-25173 targeting Jenkins Pipeline Groovy Plugin's CPS interpreter sandbox bypass, enabling arbitrary code execution within…
 poppopjmp/vmdragonslayer
Multi-engine framework for unpacking and analyzing VM-protected binaries using dynamic taint tracking, symbolic execution, pattern classification,…
 runreveal/sigmalite
Go library for parsing and executing Sigma detection rules against log entries, supporting field modifiers, CIDR matching, and custom field resolvers…
 shoucheng3/jenkinsci__script-security-plugin_cve-2023-24422_1228.vd93135a_2fb_25
Jenkins plugin providing script approval workflows and Groovy sandboxing to enforce secure script execution, with ACL-aware permission checks and…
 gitlab-da/tutorials/security-and-governance/custom-scanner-integration/fern-pattern-scanner
Scans selected files for patterns stated in rules. This is used in order to find secrets you may have accidentally written to a file. This scanner is…
 spamscanner/url-regex-safe
Regular expression matching for URL's. Maintained, safe, and browser-friendly version of url-regex. Resolves CVE-2020-7661 for Node.js servers.
 simplylu/cve-2021-42574
Generate malicious files using recently published bidi-attack (CVE-2021-42574)
 pietroborrello/customprocessingunit
The first analysis framework for CPU microcode
 iilegacyyii/exportdumper
A small tool I made to dump the export table of PE files. The primary use case was intended for use within DLL proxying.
 trinadh465/external_lib_aosp10_r33_cve-2021-45960_cve-2021-46143-
C library for stream-oriented XML parsing, providing a fast and configurable parser with support for custom handlers and encoding options.