
ASC
 mg1937/asc
Fast Android APK decompiler front-end that queries compiled DEX artifacts directly, extracting classes and cross-references in milliseconds without…
android-securitybinary-analysiscode-analysis+6
2.1k
mg1937/ascFast Android APK decompiler front-end that queries compiled DEX artifacts directly, extracting classes and cross-references in milliseconds without…
 vighnesh91/securiscan
Standard-library Python security triage engine that scans web apps, APIs, LLMs, and mobile packages via passive header inspection, active canary…
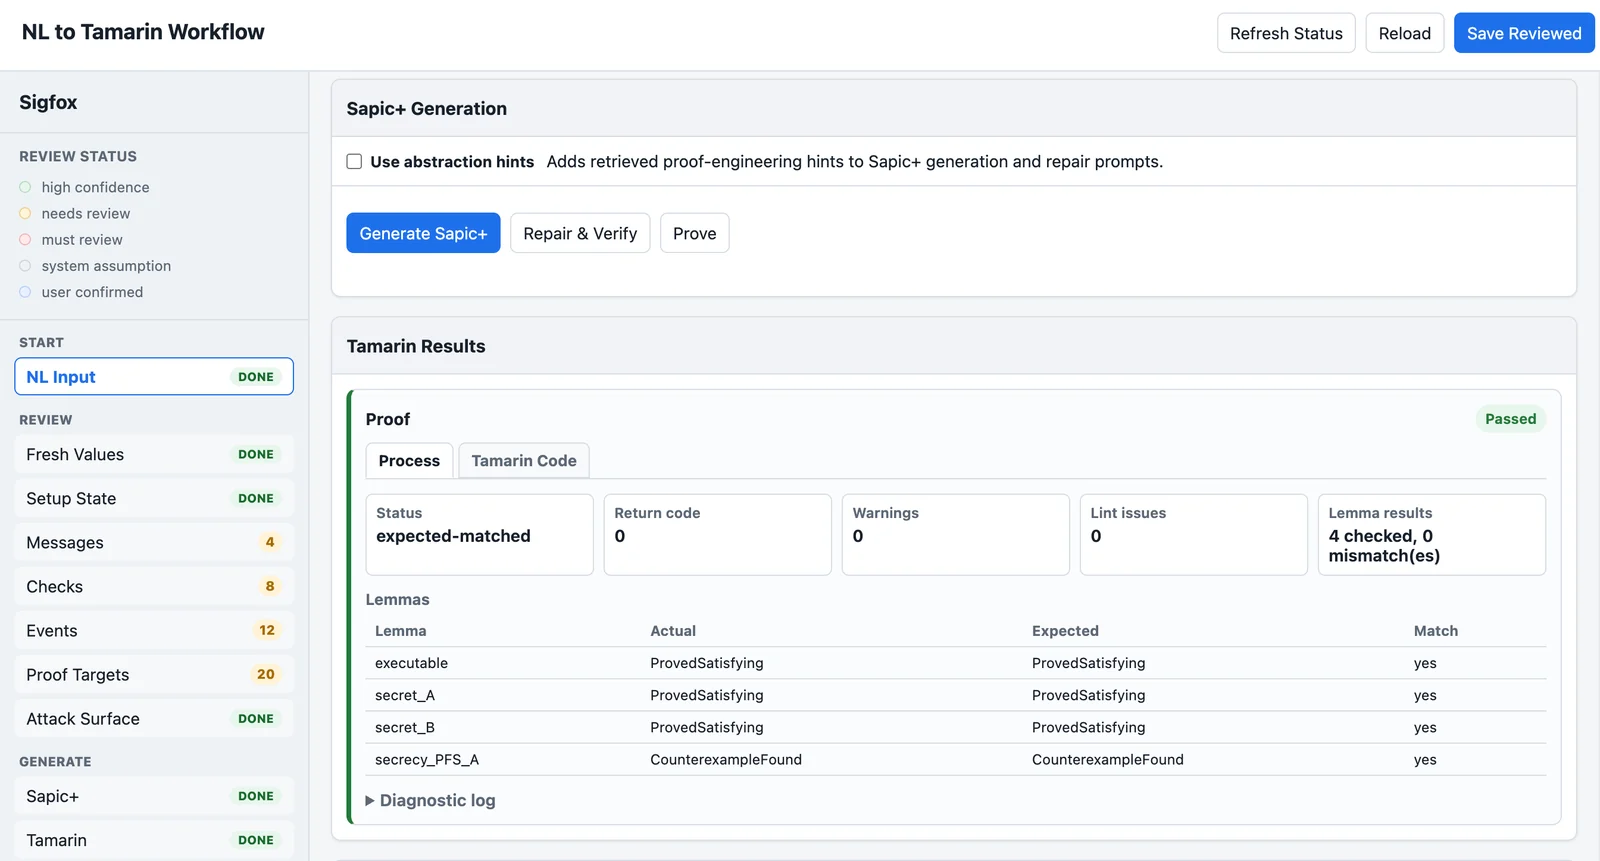 laplace1002/tamarinagent
Human-in-the-loop UI that converts natural-language or C/C++ protocol descriptions into a reviewable Protocol IR, then generates Sapic+/Tamarin…
 gmh5225/ida-claude-code-plugins
Plugins integrating Claude Code with IDA Pro to assist reverse engineering and binary analysis workflows through AI-driven disassembly and code…
 ejfkdev/ddc
DEX → Java decompiler in Rust — fast, progressive analysis, bilingual CLI
 ejfkdev/dj
Extracts dynamically loaded JavaScript files by statically analyzing website HTML and JS, detecting webpack chunks, import() lazy loading, and source…
 ssh-pur66/cve-replay
Independent offline regression of CVE-2026-44431 across pinned urllib3 releases, with original reporter attribution.
 dmdhrumilmistry/security-harness
Multi-agent static application-security review harness for AI coding agents: maps codebases, hunts vulnerability classes, chains and verifies…
 sdodson/cve-2026-46595-proof
Go proof-of-concept demonstrating CVE-2026-46595 in golang.org/x/crypto/ssh, using symbol inspection of stripped binaries and image scans to verify…
 svtagan/wp-cve-2026-87902
Read-only PHP diagnostic script that checks WordPress version, core checksums, extra PHP files, and known plugin paths for CVE-2026-87902 exposure…
 atomdrift-project/scan
0-day malware detection for binaries, source & scripts (that doesn't suck)
 ch0pin/rdx
A native APK and DEX decompiler written in Rust
 bishopfox/mauidll
Extract the managed (.NET) assemblies out of a MAUI Android assembly store.
 gmh5225/gmh5225
LLVM-based security research toolchain: NeverC, a C23 cross-compiler, and NeverD, a binary analysis and decompilation engine that lifts PE, ELF,…
 vpierre/ndaal_public_sbom_auditor
Offline single-binary web app that ingests CycloneDX, SPDX and syft SBOMs, runs an ensemble of CVE scanners, enriches findings with EPSS, CISA-KEV…
 xiaoqimikko/async-http-client-check
Self-hosted AI workspace with agents, skills, and tools (Gmail, Calendar) that runs entirely on your own provider API keys (BYOK). Bring your own…
 gmh5225/evmbench-certora-agent-harness
Iterative agent harness that uses LLMs and Certora Prover to generate and refine smart-contract CVL specs, feeding verifier output back until success…
 fauxrougee/smartscanner-source
Web vulnerability scanner built with C++17 and Qt 6, featuring a GUI, CLI, configurable crawling, and JSON reports. Reconstructed for educational…