

FlutterGuard
 anasfik/flutterguard
Offline security audits for Flutter APKs on Android. Inspect permissions, SDKs, endpoints and potential secrets. No root, account, ads or analytics.
android-securitydefensive-toolsfingerprint-spoofing+7
30
anasfik/flutterguardOffline security audits for Flutter APKs on Android. Inspect permissions, SDKs, endpoints and potential secrets. No root, account, ads or analytics.
 fare9/dragon-tales
Binary analysis library built on LLVM for disassembling, lifting, and symbolically executing machine code across x86, ARM, and RISC-V, with CFG…
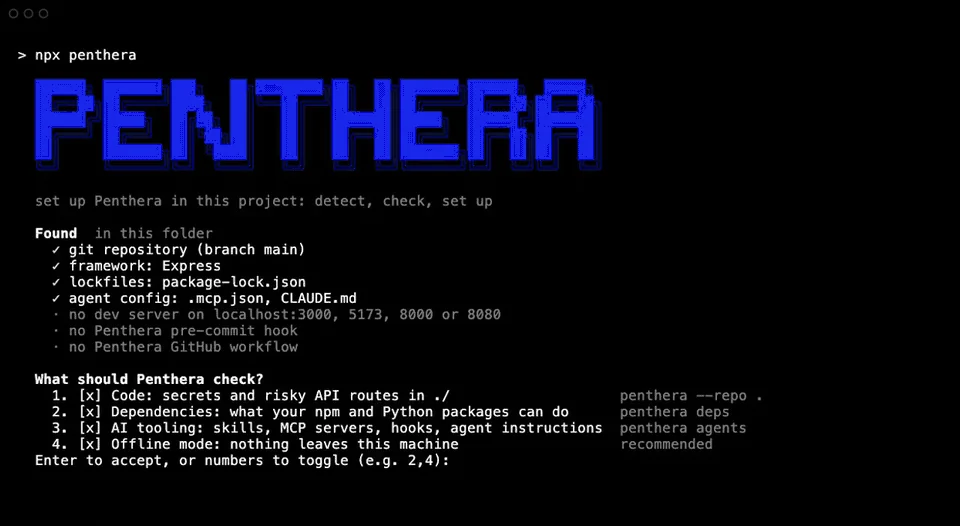 danoszz/penthera
Offline cyber security agent for your apps and AI coding tools. Open R&D: measured in public, improved every release.
 nighthawkk/jnisleuth-mcp
Automated Android JNI RegisterNatives recovery, stripped ARM64 .so type reconstruction, OLLVM BR X8 deobfuscator, and universal LLM/MCP bridge for…
 cloudflare/svg-hush
Make it safe to serve untrusted SVG files
 darylldoyle/svg-sanitizer
PHP library that sanitizes untrusted SVG/XML by filtering tags, attributes, and remote references to prevent XSS and script injection in uploaded or…
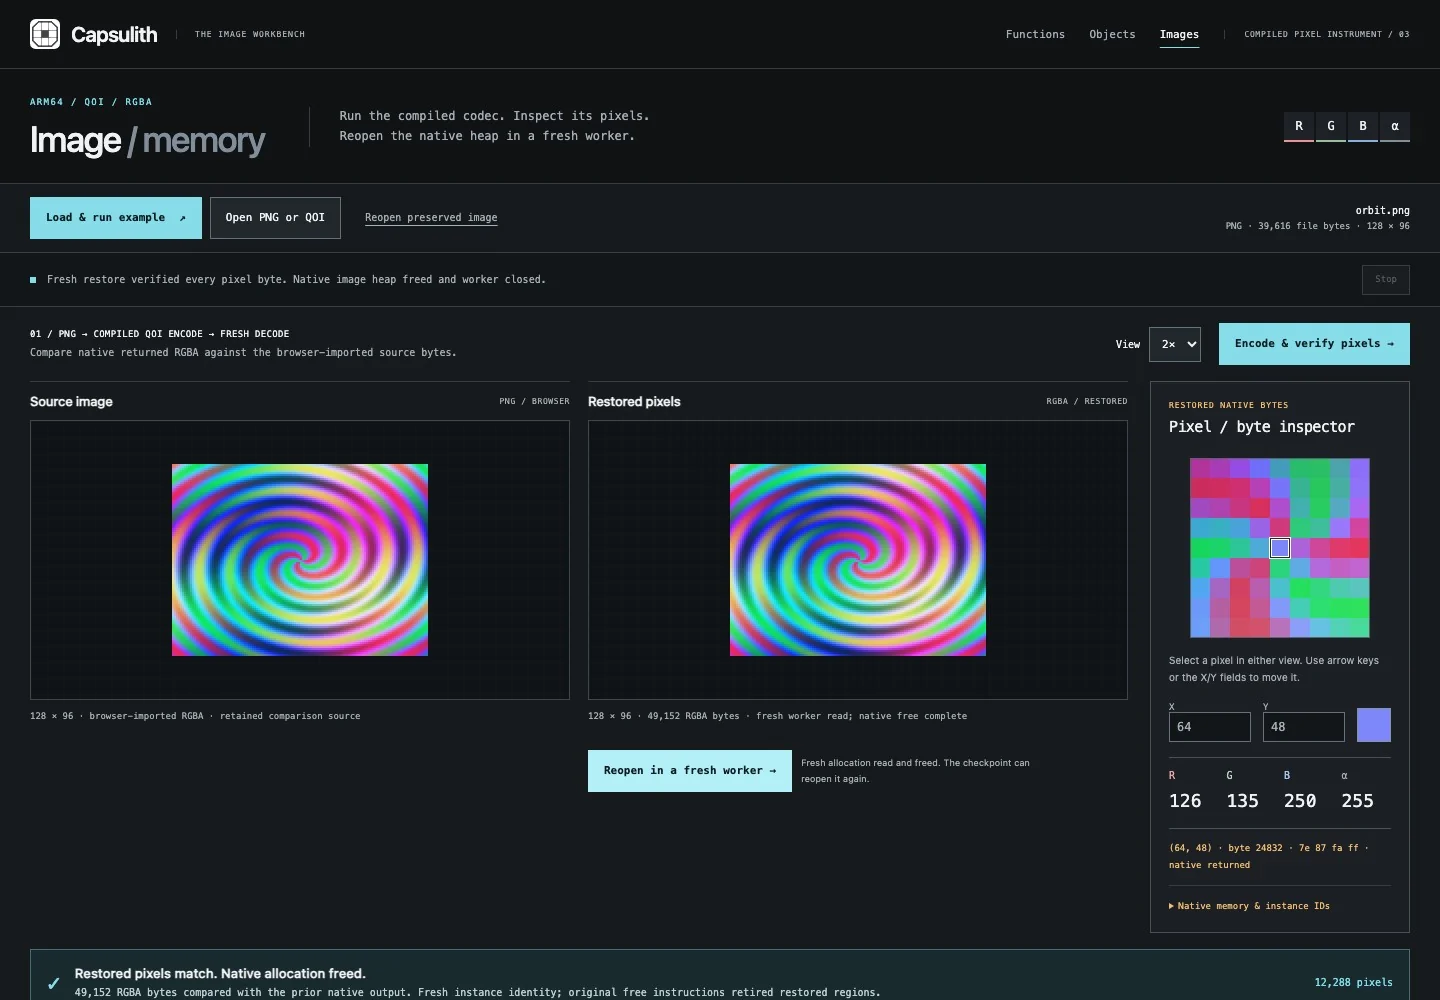 nazeeh111/capsulith
Run preserved ARM64 code in Node or a browser; inspect decoded image pixels and initialized memory.
 secprbench/secprbench
Benchmark of 265 real vulnerability-introducing code changes across nine C, C++, and Rust projects, with paired review tasks, Docker sandbox, judge,…
 0xajstrike/emsign-trust-scan
Offline scanner for the October 2026 eMudhra/emSign CA key compromise, finds affected certificates across OS trust stores, CA bundles, Java cacerts,…
 lzh0082-cloud/code-detection
Replication package studying how LLM vulnerability auditors defer to static-analysis evidence, with a tree-sitter C/C++ front end, controlled…
 endrazine/rocq-cve-poc-12155
CVE-2020-37268 — Rocq/Coq Print Assumptions Omits Unsafe Universe Checking via Parameter Inline
 endrazine/rocq-cve-poc-21682
CVE-2026-72703 — Rocq Guard Checker Accepts Non-Terminating Fixpoint via Unchecked Cross-Calls
 nanashili/rea-rust
Rust port of REA, a local-only reverse-engineering tool with CLI/MCP workflows and a native Ghidra worker
 apaonum/brotli-cve-check
Agent skill + script to scan projects for CVE-2026-111497 (Brotli), rate criticality and suggest fixes
 jondean213-pixel/quietos-sentinel
Sentinel — DeanWay Labs' inbound governor. Guards what an AI agent hears: world content is data, never orders. The mirror of QuietOS.
 trailofbits/brotli-checker
Claude Code and Codex skill for finding potentially vulnerable Brotli copies and guiding updates for CVE-2026-111497.
 yuatemycat/superghidra
Python toolkit accelerating Ghidra with a cached daemon, ARM64 P-code lifting, Z3 equivalence proofs, GPU-accelerated scanning, binary diffing, and…
 edoardottt/openhands-disclosure
Multiple Command Injection vulnerabilities in openhands <0.62.0 allow an attacker to run arbitrary system commands.