

quipu
 corelight/quipu
A desktop workbench for writing, validating, compiling, and testing YARA rules.
code-analysisdefensive-toolsdigital-forensics+6
corelight/quipuA desktop workbench for writing, validating, compiling, and testing YARA rules.
 svdwi/bluebox
Open-source threat intelligence platform for malware and observable analysis. Enriches IPs, domains, URLs, and hashes with external sources, performs…
 idamcp/idamcp
MCP server integrating IDA Pro with AI agents, featuring a stateless gateway for multi-session management, a relational SQL query engine for binary…
 zaydmulani09/sentrymcp
A static + runtime security scanner for MCP (Model Context Protocol) servers
 threatlabz/iocs
This repository is for Indicators of Compromise (IOCs) from Zscaler ThreatLabz public reports
 pandare9x/configuration_extractors
Configuration Extractors for Malware
 embee-research/agenttesla-config-extractor
Config extractor for AgentTesla - Discord/Telegram Variant
 nccgroup/yaml2yara
Generate bulk YARA rules from YAML input
 synacktiv/krustyloader-analysis
KrustyLoader Analysis
 bytespulse-oe/wp2shell-hestia-scanner
Read-only WordPress security scanner for HestiaCP servers. Detects wp2shell compromise indicators (CVE-2026-63030 / CVE-2026-60137) across all hosted…
 chpratik/cve-2026-9830
Threat intelligence report repository for CVE-2026-9830, an authentication bypass vulnerability in BookingPress Pro WordPress plugin, with detailed…
 adamsjack711-ux/pkgxray
Pre-install security for AI agents, npm packages, and MCP servers. Zero-dep local static analysis; normal scans never execute package code.
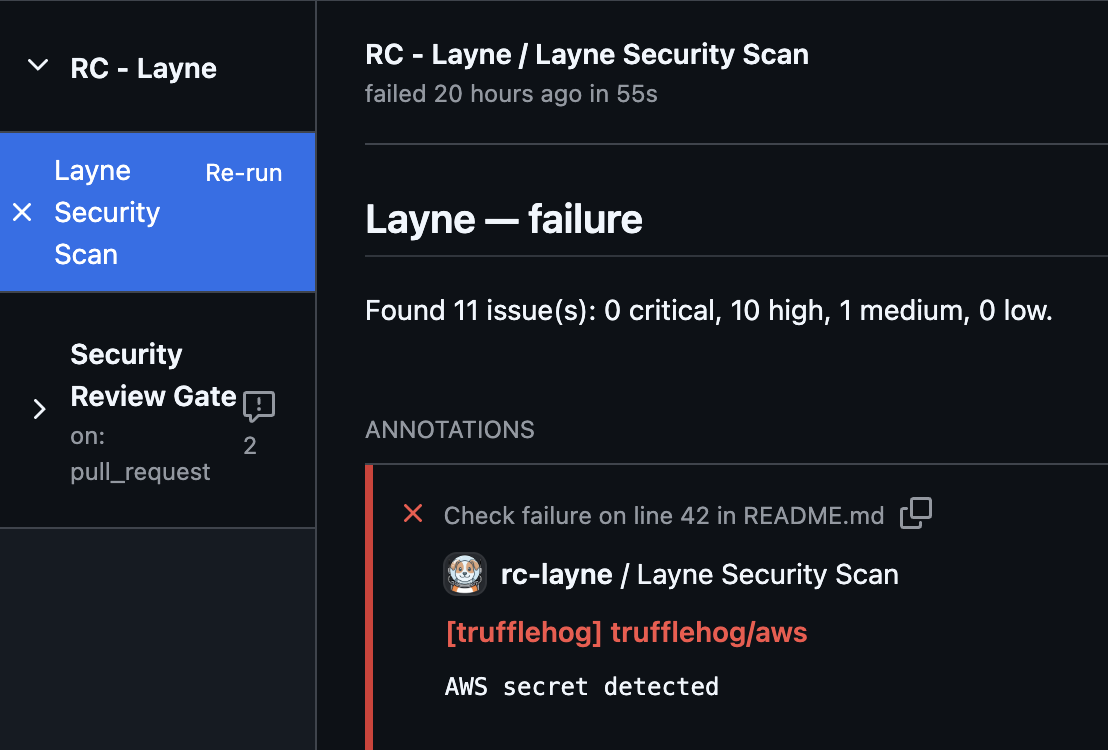 rocketchat/layne
A doggo that helps look for security issues in your repositories.
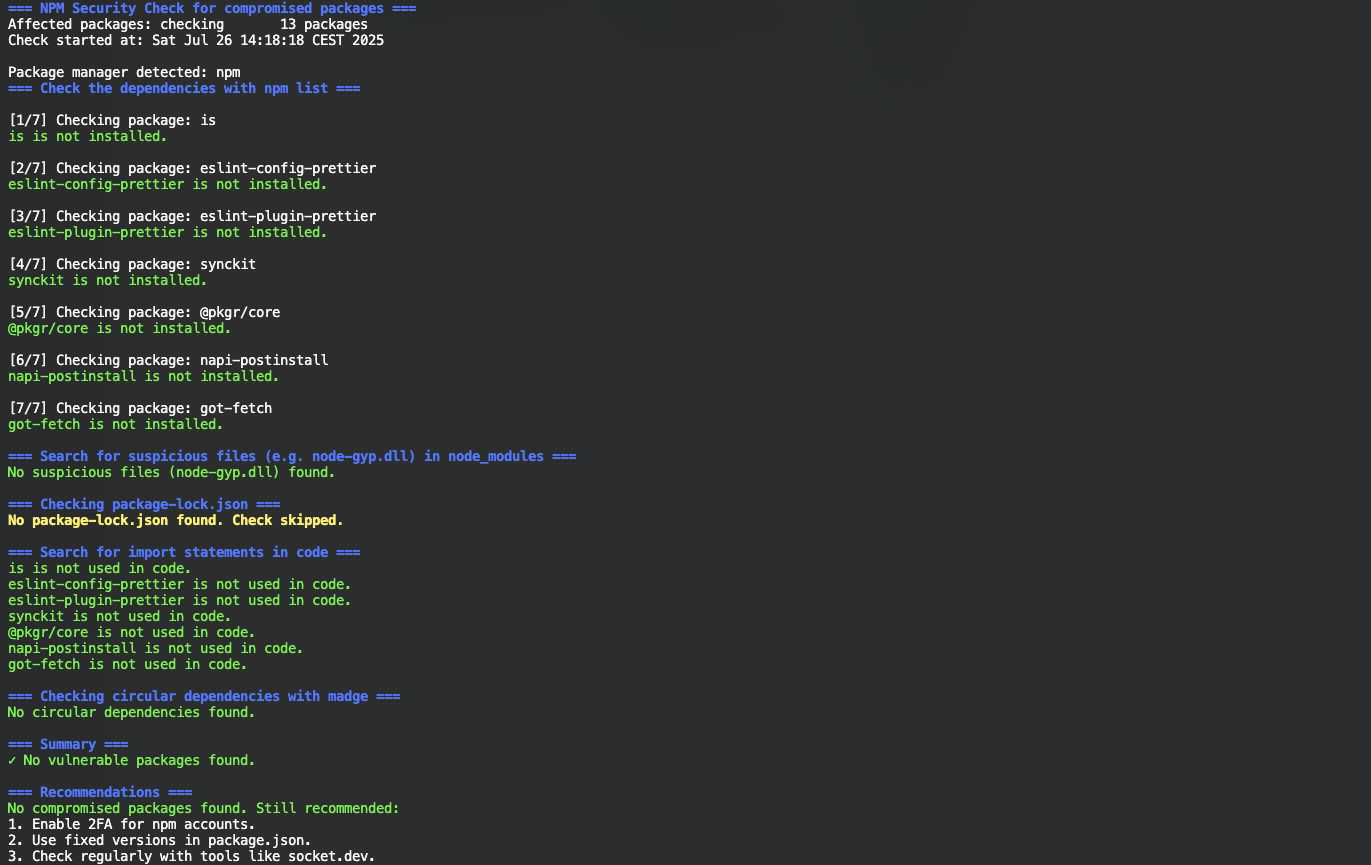 nihilor/cve-2025-54313
Checks projects for compromised packages, suspicious files, and import statements.
 shoucheng3/jenkinsci__script-security-plugin_cve-2023-24422_1228.vd93135a_2fb_25
Jenkins plugin providing script approval workflows and Groovy sandboxing to enforce secure script execution, with ACL-aware permission checks and…
 xsultan/log4jshield
Log4j Shield - fast ⚡, scalable and easy to use Log4j vulnerability CVE-2021-44228 finder and patcher
 codeshield-security/log4jshell-bytecode-detector
Local Bytecode Scanner for the Log4JShell Vulnerability (CVE-2021-44228)
 shoucheng3/joniles__mpxj_cve-2020-35460_8-3-4
Exploit for CVE-2020-35460 targeting MPXJ project management library, enabling arbitrary code execution via crafted project files in Java, .Net, and…