
pftriage
 idiom/pftriage
Python tool and library to help analyze files during malware triage and analysis.
binary-analysisdigital-forensicsdynamic-analysis-sandboxing+4
796 years ago
idiom/pftriagePython tool and library to help analyze files during malware triage and analysis.
 dimareverse/nuitka-static-unpacker
Static-first research tool for unpacking Nuitka-compiled binaries: extracts constants, modules, recovers .pyc files, and generates analysis reports.
 skylot/jadx
Command-line and GUI tool for decompiling Android Dex and APK files into readable Java source code, with resource decoding, deobfuscation, and Smali…
 gitleaks/gitleaks
Fast, open-source static analysis tool for detecting hardcoded secrets like passwords, API keys, and tokens in git repositories, files, and stdin…
 analysis-tools-dev/static-analysis
Curated directory of static analysis (SAST) tools and linters for programming languages, configs, build tools, and CI, focused on improving code…
 ejfkdev/dj
Extracts dynamically loaded JavaScript files by statically analyzing website HTML and JS, detecting webpack chunks, import() lazy loading, and source…
 mandiant/capa
Rule-based static and dynamic analysis tool that identifies capabilities in PE, ELF, .NET, and shellcode files, mapping them to MITRE ATT&CK…
 seekbytes/ipa
GUI analyzer for deep-diving into PDF files. Detect malicious payloads, understand object relationships, and extract key information for threat…
 intelowlproject/intelowl
Scalable threat intelligence platform that enriches observables and files using 200+ analyzers, with built-in GUI, REST API, and automated workflows…
 wadingporque/apkprobe
APK decompiler & secrets scanner for Android security research! Extract leaked API keys, hardcoded credentials, endpoints from APK files. apk2url,…
 vpierre/ndaal_public_sbom_auditor
Offline single-binary web app that ingests CycloneDX, SPDX and syft SBOMs, runs an ensemble of CVE scanners, enriches findings with EPSS, CISA-KEV…
 suleram/view8
Decompiles serialized V8 bytecode (JSC files) into high-level readable JavaScript-like code, with support for multiple V8 versions, tree output, and…
 google/bindiff
Quickly find differences and similarities in disassembled code
 stackrox/kube-linter
KubeLinter is a static analysis tool that checks Kubernetes YAML files and Helm charts to ensure the applications represented in them adhere to best…
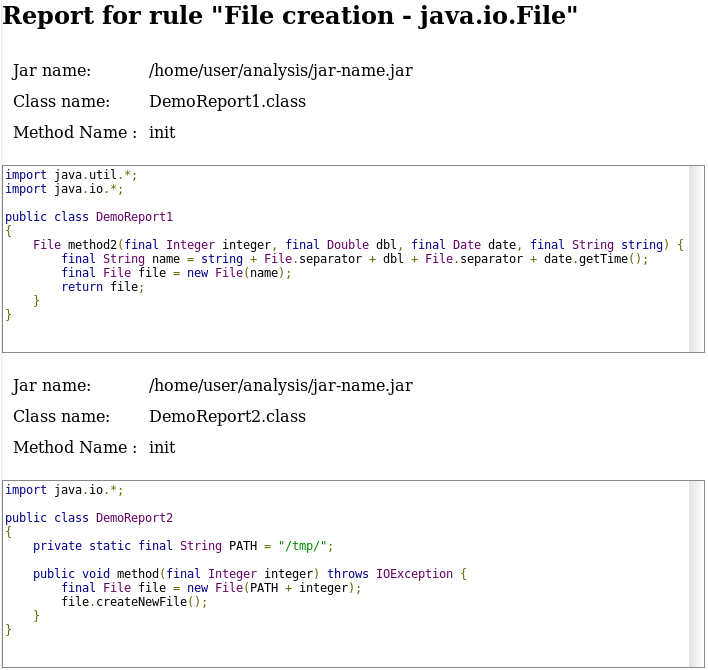 fergarrui/custom-bytecode-analyzer
Java bytecode analyzer customizable via JSON rules
 inettgmbh/checkmk-log4j-scanner
Checkmk extension that scans JAR, WAR, EAR, and AAR files for Log4j versions vulnerable to CVE-2021-44228 by inspecting META-INF pom.properties…
 volexity/donut-decryptor
Extracts and decrypts inner payloads from Donut obfuscator samples by detecting loader shellcode signatures, parsing the DONUT_INSTANCE structure,…
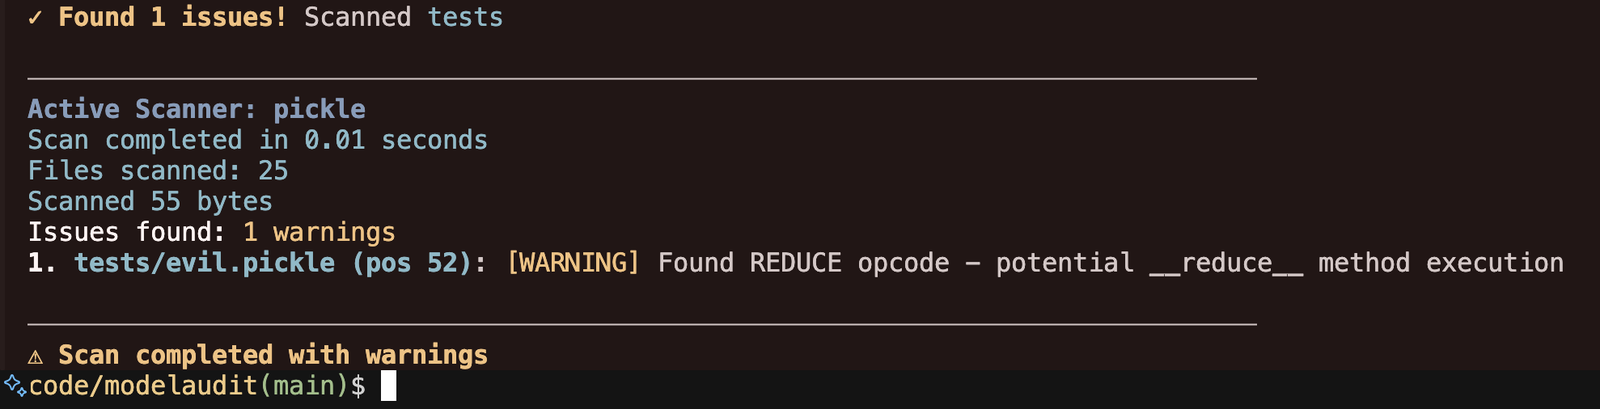 promptfoo/modelaudit
Security scanner for AI/ML model files. Detects malicious code, backdoors, and vulnerabilities before deployment