

recurse
 recurse-labs/recurse
Agentic reverse engineering IDE with a pure-Rust multi-architecture disassembler, native decompiler, debugger, and LLM agent for binary analysis and…
ai-assisted-reversingai-securitybinary-analysis+7
284
recurse-labs/recurseAgentic reverse engineering IDE with a pure-Rust multi-architecture disassembler, native decompiler, debugger, and LLM agent for binary analysis and…
 z3prover/z3
High-performance SMT solver for automated theorem proving, constraint solving, and program verification. Supports multiple theories and language…
 security-prince/resources-for-application-security
Some good resources for getting started with application security
 x64dbg/x64dbg
An open-source user mode debugger for Windows. Optimized for reverse engineering and malware analysis.
 ggfuchsi-oss/spectrida-reverse_engineering_stack
Parallel IDA Pro binary analysis with AI-powered function naming, Neo4j knowledge graph, and phantomrt emulation/hooking/fuzzing engine for automated…
 coffeeandsecurity/dakshscra
Framework-aware static code analysis tool for automated source code review with platform-specific rules, taint analysis, effort estimation, and…
 hasherezade/jsc_deobfuscator
Static deobfuscation toolkit for compiled V8 JavaScript bytecode, focusing on JSCeal payloads. Provides pattern-driven filters, control-flow…
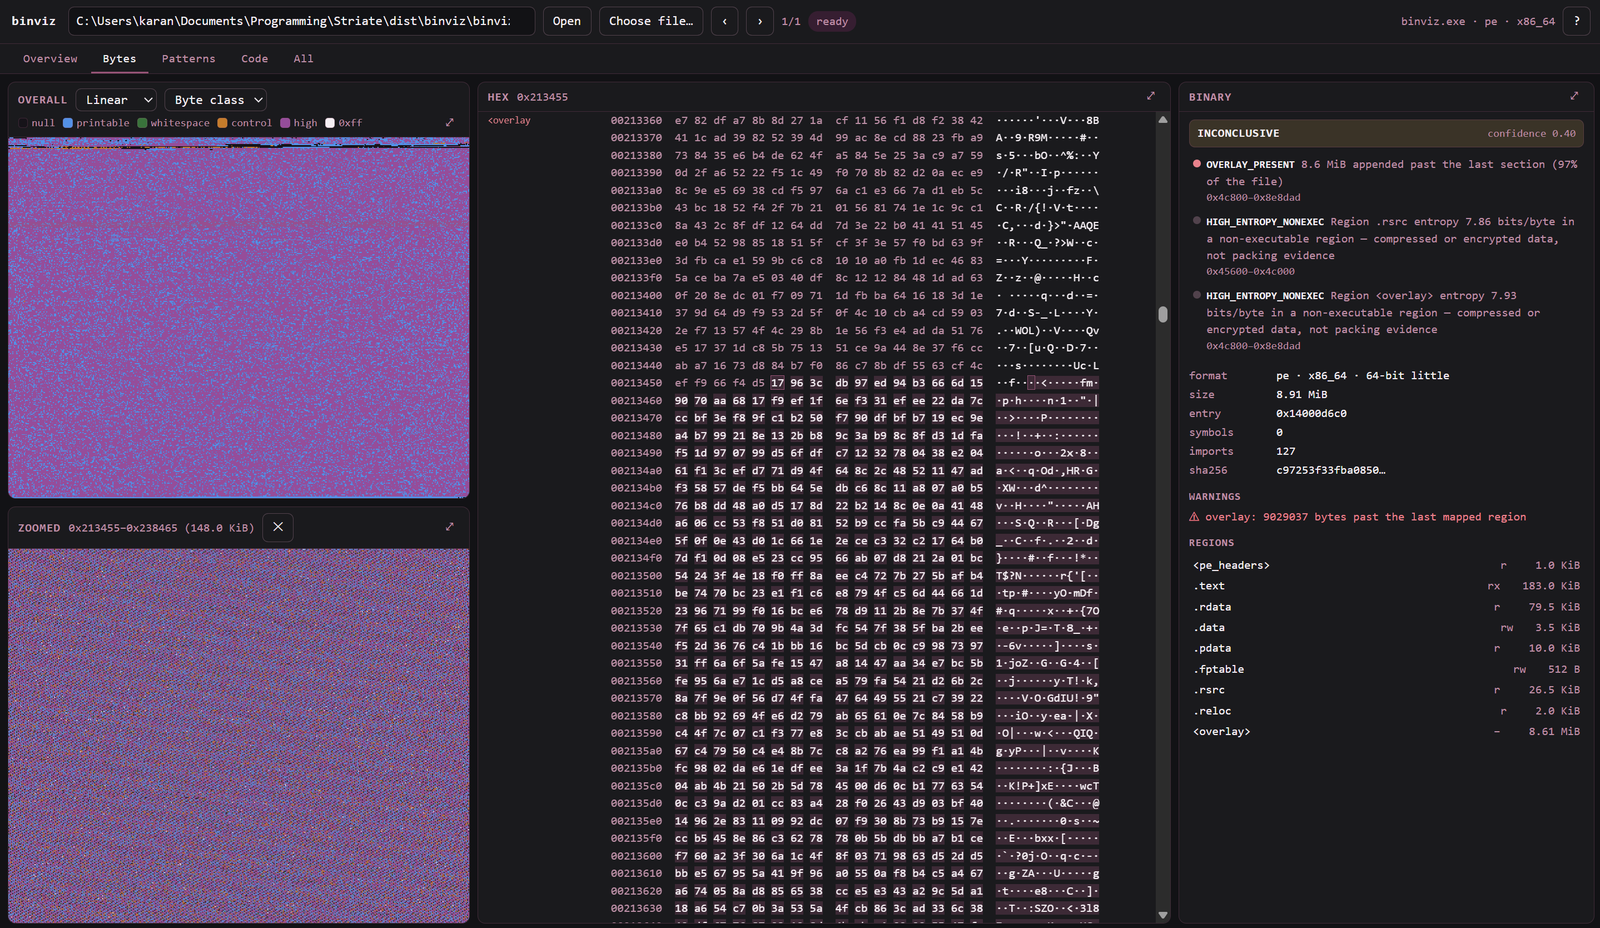 karankantaria/binviz
Binary visualiser and triage tool — entropy, byte-class and Hilbert surfaces, dot plots and control-flow graphs over one shared address-space model.
 owasp/wrongsecrets-binaries
Source code for the Binaries of OWASP WrongSecrets
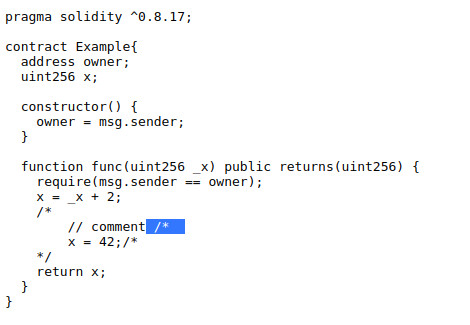 tin-z/solidity_cve-2021-42574-poc
POC of CVE-2021-42574 for solidity and solc compiler
 google/bindiff
Quickly find differences and similarities in disassembled code
 cmu-sei/pharos
Automated static analysis tools for binary programs
 danielbohannon/revoke-obfuscation
PowerShell Obfuscation Detection Framework
 chris1sflaggin/lcsajdump
An ML powered Graph-Based Multi-Architecture Approach for ROP Gadget Detection
 owasp/railsgoat
A vulnerable version of Rails that follows the OWASP Top 10
 tamarin-prover/tamarin-prover
Symbolic verification tool for security protocols using multiset rewriting and constraint solving to prove secrecy, authentication, and equivalence…
 runtimeverification/kernel-c-to-rust-spike
Hardening kernel C parsers via Rust rewrite + differential fuzzing + formal verification. First target: UVC (CVE-2024-53104).
 wrongbaud/hackaday-u
Course materials for hackaday.io Ghidra training