
Skip to content
KitploitKITPLOIT
ToolsBlog
Log in
Submit
ToolsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

FeedsContactPrivacy© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories

Tools

AllAndroid SecurityAuthentication & AuthorizationCloud Infrastructure SecurityDefensive ToolsDisk ForensicsEmbedded Systems SecurityGeneral Purpose UtilitiesIndicator of Compromise (IOC) ManagementOSINT (Open Source Intelligence)Packet Sniffing & AnalysisPassword CrackingPenetration Testing FrameworksPhishing ToolsPrivilege EscalationReconnaissanceStatic AnalysisVulnerability ScannersWeb Vulnerability ScannersWi-Fi AuditingBluetooth SecurityContainer SecurityDynamic Analysis (Sandboxing)Encryption/Decryption ToolsExploit FrameworksIdentity ManagementiOS SecurityIoT SecurityMemory ForensicsNetwork MappingOSINT for Social EngineeringPassword AttacksPayload GenerationPersistence MechanismsPort ScanningStatic Code Analysis (SAST)Threat Feeds & AggregatorsVulnerability AnalysisWeb Proxies & InterceptionCode AnalysisDNS & Subdomain EnumerationDynamic Code Analysis (DAST)ExploitationHash AnalysisIDS/IPS EvasionImpersonation ToolsLateral MovementMobile App PentestingNetwork ForensicsReverse EngineeringRFID/NFC ToolsSCADA/ICS SecurityScripting & AutomationServerless SecurityShellcodeWeb Application ExploitationAPI Security TestingConfiguration AuditingData ExfiltrationDebuggersForensicsInformation GatheringMobile ForensicsNetwork Access ControlPost-ExploitationSecurity VirtualizationPhishingWAF BypassWeb SecurityFuzzingNetwork SecuritySteganographyWireless SecurityData RecoveryMalware AnalysisDigital ForensicsHardware HackingCryptographyCTFPenetration TestingCloud SecurityDevSecOpsMobile SecurityPrivacyCommand and ControlSocial EngineeringHardware SecurityUtilities & FrameworksHardware & IoT SecuritySecret DetectionBinary AnalysisThreat IntelligenceIdentity & Access Management (IAM)Supply Chain SecurityAuthenticationMachine LearningIntrusion DetectionPapers & ResearchMisconfigurationSubdomain EnumerationEmail HarvestingLearning & EducationAI-Assisted ReversingDNS FuzzingRed TeamingIncident ResponseCrawlerCurated ResourcesRemote Access ToolShellcode GenerationPayload DevelopmentRemote Access TrojanAPI SecurityAnti-BotFingerprint SpoofingCAPTCHA BypassEmail SecurityDNS AnalysisChaos EngineeringLearning Paths & CoursesContainer EscapeAI SecurityDatabase SecurityFirmware AnalysisAnomaly DetectionLog AnalysisAdversarial AttackBinary ExploitationLabs & Practice
NewestRelevanceMost popularRecently updated
16 results
CVE-2021-28079 preview

CVE-2021-28079

GitHubg33xter/cve-2021-28079

Proof-of-concept exploit for XSS vulnerability in Jamovi <=1.6.18. Demonstrates crafting malicious .omv documents with JavaScript payloads to achieve…
command-and-controlexploitationpayload-development+3
4
4 years ago
CVE-2019-13633 preview

CVE-2019-13633

GitHubsecurity-avs/cve-2019-13633

Proof of concept for a blind/persistent XSS vulnerability in Blinger.io helpdesk, demonstrating remote code execution in admin panels via crafted…
information-gatheringpenetration-testingphishing+3
6 years ago
CVE-2025-69606-GSVoIP-XSS preview

CVE-2025-69606-GSVoIP-XSS

GitHubrazielx64/cve-2025-69606-gsvoip-xss

Proof-of-concept for a reflected XSS vulnerability (CVE-2025-69606) in GSVoIP Web Panel v2.0.90, demonstrating unauthenticated arbitrary JavaScript…
educationphishingsocial-engineering+3
6 months ago
CVE-2024-30956 preview

CVE-2024-30956

GitHubleocottret/cve-2024-30956

(DOM-based XSS) HTML Injection vulnerability in TOWeb v.12.05 and before allows an attacker to inject HTML/JS code via the _message.html component.
exploitationphishing-toolssocial-engineering+2
2 years ago
CVE-2023-38831-Exploit preview

CVE-2023-38831-Exploit

GitHubtechnicalcorp0/cve-2023-38831-exploit

This project contains a Python script that exploits **CVE-2023-38831**, a vulnerability in **WinRAR** versions prior to 6.23. The exploit generates a…
educationexploitationpayload-generation+4
12 years ago
CVE-2022-48429_poc preview

CVE-2022-48429_poc

GitHubecho-devim/cve-2022-48429_poc

Proof-of-concept exploit for CVE-2022-48429, a stored cross-site scripting vulnerability in JetBrains YouTrack dashboards enabling low-privileged…
exploitationpenetration-testingphishing+3
3 years ago
CVE-2024-6529 preview

CVE-2024-6529

GitHubabdurahmon3236/cve-2024-6529

Proof-of-concept scripts demonstrating reflected XSS in the Ultimate Classified Listings WordPress plugin and admin cookie theft via crafted payloads…
exploitationpenetration-testingphishing+3
2 years ago
CVE-2025-25101 preview

CVE-2025-25101

GitHubnxploited/cve-2025-25101

WordPress Munk Sites plugin <= 1.0.7 - CSRF to Arbitrary Plugin Installation vulnerability
educationexploitationphishing+3
11 year ago
PoC-for-CVE-2024-7014-Exploit preview

PoC-for-CVE-2024-7014-Exploit

GitHubabsholi7ly/poc-for-cve-2024-7014-exploit

Proof of Concept (PoC) for CVE-2024-7014 (EvilVideo) Exploit
android-securityexploitationmobile-security+3
121 year ago
WEAPONIZING-CVE-2024-4367 preview

WEAPONIZING-CVE-2024-4367

GitHubexfil0/weaponizing-cve-2024-4367

CVE-2024-4367 is a critical vulnerability (CVSS 9.8) in PDF.js, allowing arbitrary JavaScript code execution due to insufficient type checks on the…
educationexploitationpayload-generation+3
31 year ago
CVE-2025-3568 preview

CVE-2025-3568

GitHubshellkraft/cve-2025-3568

A security vulnerability has been identified in Krayin CRM <=2.1.0 that allows a low-privileged user to escalate privileges by tricking an admin into…
exploitationphishingprivilege-escalation+3
1 year ago
CVE-2021-46366 preview

CVE-2021-46366

GitHubmbadanoiu/cve-2021-46366

CVE-2021-46366: Credential Bruteforce Attack via CSRF + Open Redirect in Magnolia CMS

exploitationinformation-gatheringpassword-attacks+3
2 years ago
PoC-CVE-2026-20841 preview

PoC-CVE-2026-20841

GitHubelenichristopoulou/poc-cve-2026-20841

Proof-of-concept exploit for CVE-2026-20841, a Windows Notepad remote code execution vulnerability, using a crafted .md file and social engineering…
exploitationphishingsocial-engineering+1
8 months ago
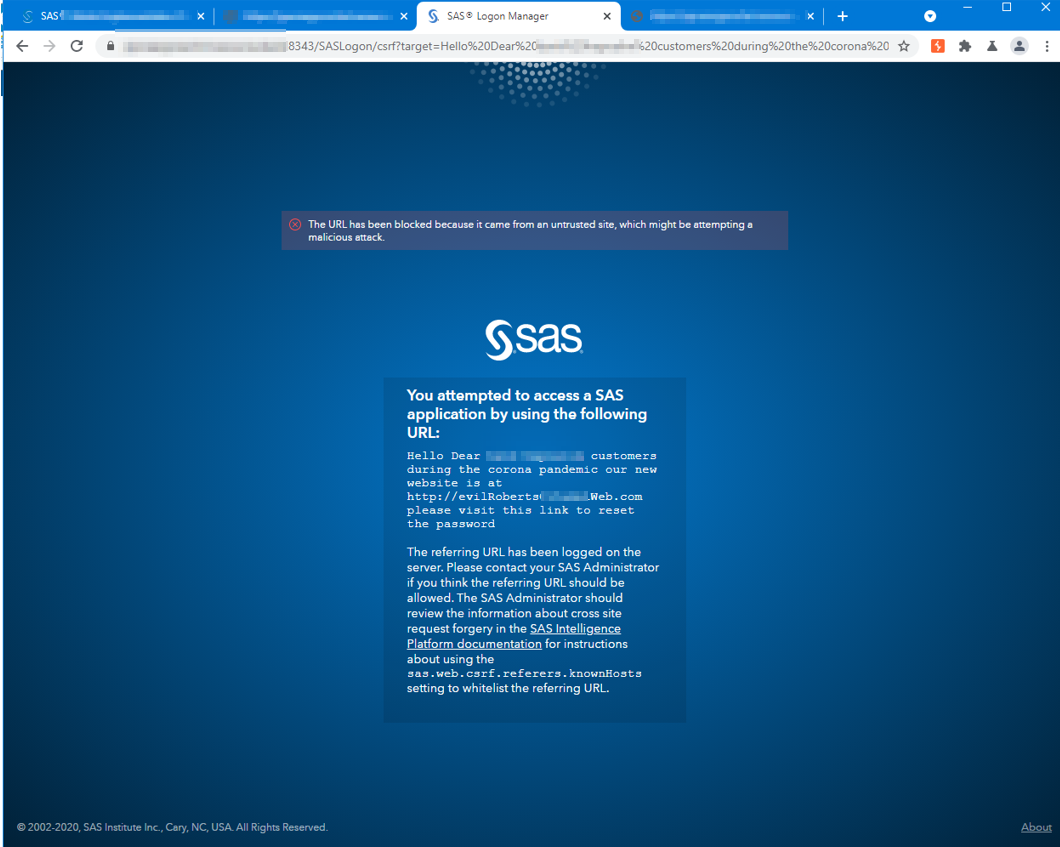
CVE-2022-25257 preview

CVE-2022-25257

GitHubpolling-repo-continua/cve-2022-25257

Proof-of-concept exploit for CVE-2022-25257: CSRF parameter injection in SAS Logon 9.4 enabling warning-message spoofing for phishing attacks.
exploitationphishingsocial-engineering+2
4 years ago
CVE-2022-46087 preview

CVE-2022-46087

GitHubg37sys73m/cve-2022-46087

CloudSchool v3.0.1 is vulnerable to Cross Site Scripting (XSS). A normal user can steal session cookies of the admin users through notification…
phishingsocial-engineeringvulnerability-analysis+2
3 years ago
CVE-2022-47132 preview

CVE-2022-47132

GitHubopenxp-research/cve-2022-47132

Academy LMS <= 5.10 CSRF

exploitationpenetration-testingsocial-engineering+2
2 years ago