All-CEHv13-Module-wise-PDF-Reports

Practical labs, notes, and reports for CEH v13 modules — covering web hacking, network pentesting, malware analysis, social engineering, and security…

Practical labs, notes, and reports for CEH v13 modules — covering web hacking, network pentesting, malware analysis, social engineering, and security…

RedRoot is a Python-based, CLI-driven offensive security framework that brings essential red teaming tools into one unified terminal environment.…

Penetration testing lab demonstrating CVE-2024-21413 moniker link exploitation for NTLM credential theft, including attack execution, hash cracking,…

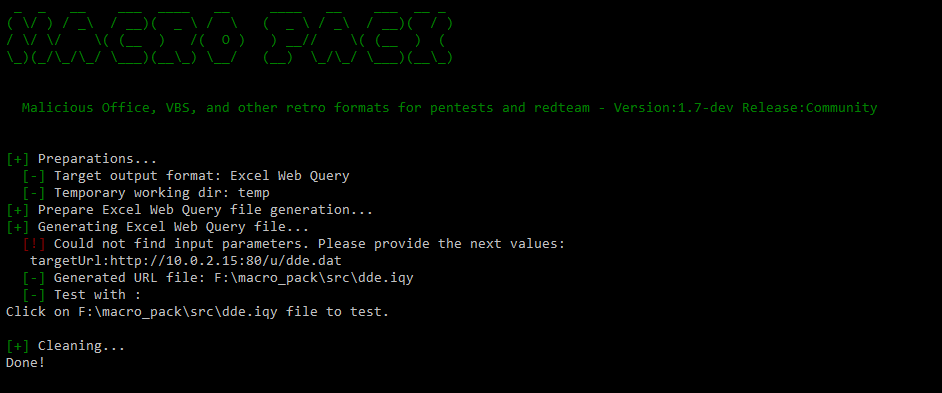
macro_pack is a tool by @EmericNasi used to automatize obfuscation and generation of Office documents, VB scripts, shortcuts, and other formats for…

Contains evilginx phislets, gophish templates, burp suite extensions etc.

Remote Administration Tool for Android devices

evilginx3 + gophish

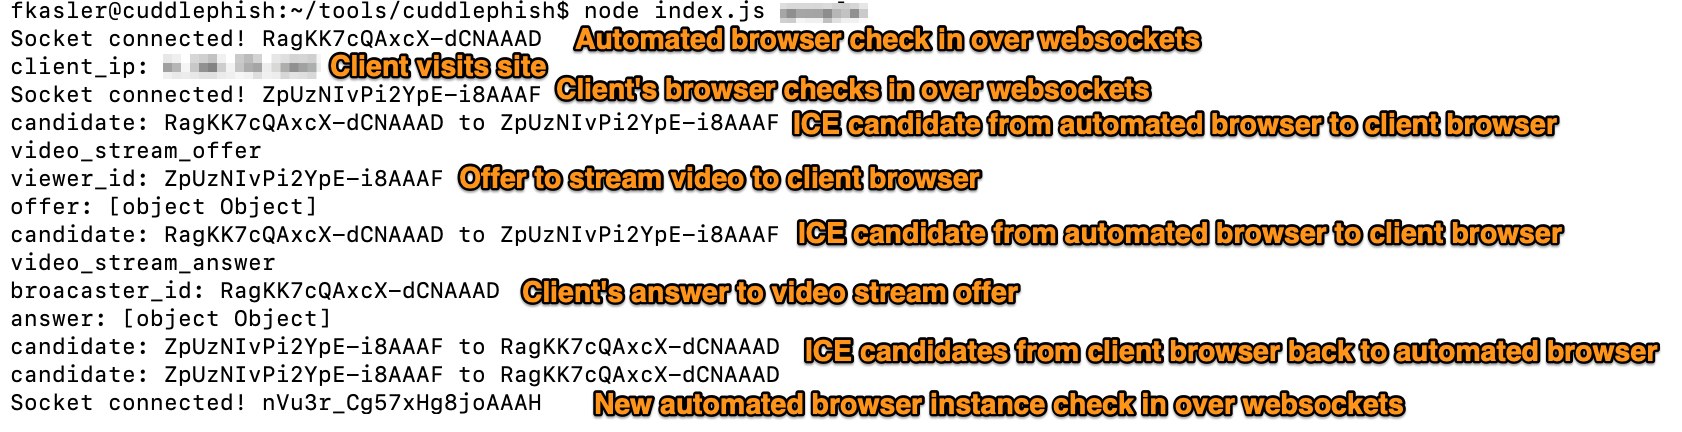
Weaponized Browser-in-the-Middle (BitM) for Penetration Testers

PLEASE USE NEW VERSION: https://github.com/kgretzky/evilginx2

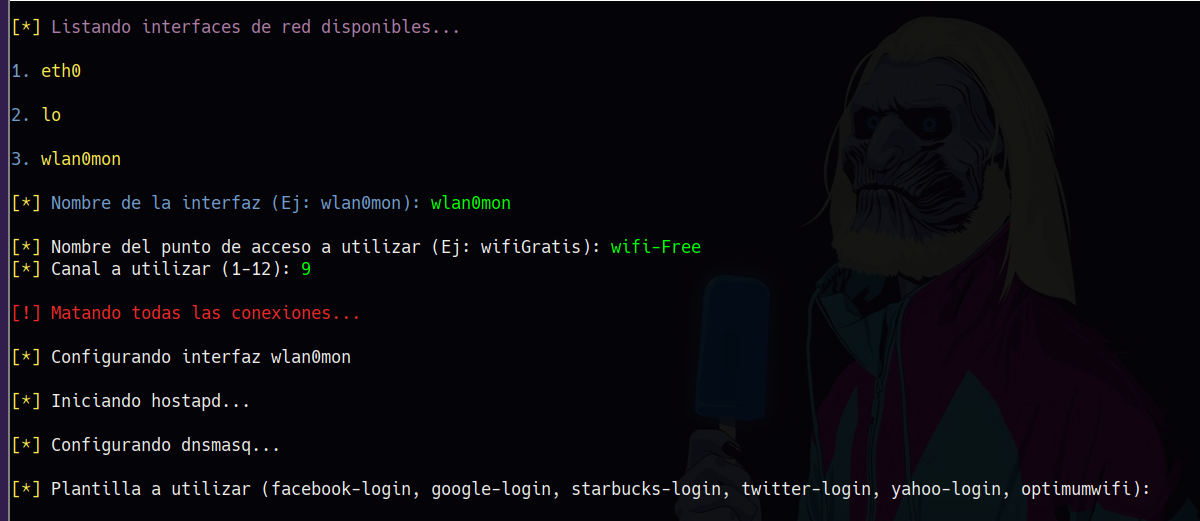
Herramienta ideal para el despliegue automatizado de un Rogue AP con capacidad de selección de plantilla + 2FA. No requiere de conexión cableada.

Automated network asset, email, and social media profile discovery and cataloguing.

Proof-of-concept to demonstrate dynamic QR swap phishing attacks in practice.

Automated phishing campaign toolset that spawns dedicated AWS EC2 instances with integrated PhishingFrenzy and BeEF, plus subdomain discovery and…

PwnSTAR (Pwn SofT-Ap scRipt) - for all your fake-AP needs!

Serverless AITM Simulation Framework for Entra ID and M365

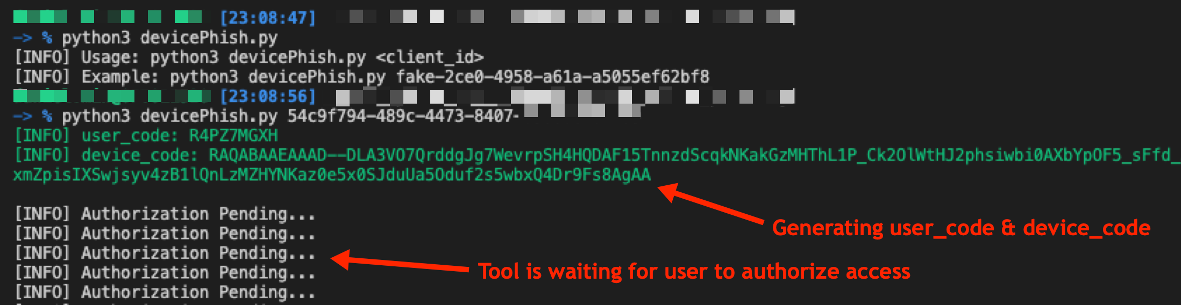
A proof-of-concept script to conduct a phishing attack abusing Microsoft 365 OAuth Authorization Flow

A malicious OAuth application that can be leveraged for both internal and external phishing attacks targeting Microsoft Azure and Office365 users.

This script can be used to gain access to a victim's Samsung Account if they have a specific version of Samsung Members installed on their Samsung…