

SysWhispers3
 klezvirus/syswhispers3
SysWhispers on Steroids - AV/EDR evasion via direct system calls.
defensive-toolsexploitationids-ips-evasion+5
1.7k
klezvirus/syswhispers3SysWhispers on Steroids - AV/EDR evasion via direct system calls.
 cybereason/siofra
Simulates the Windows PE loader to identify DLL hijacking vulnerabilities, generates weaponized DLLs with shellcode payloads, and detects UAC…
 shutdownrepo/shellerator
Simple CLI tool for the generation of bind and reverse shells in multiple languages
 tanc7/exocet-av-evasion
EXOCET - AV-evading, undetectable, payload delivery tool
 rburrito/payloadgenerator
A wrapper for MSFvenom that allows for easy generation of payloads
 runik/harmonic
Suite for reverse shell handling geared toward working within the native shell
 9emin1/charlotte
c++ fully undetected shellcode launcher ;)
 0xsha/cve-2026-6307
Google Chrome CVE-2026-6307 PoC
 monoxgas/srdi
Shellcode implementation of Reflective DLL Injection. Convert DLLs to position independent shellcode
 m4sc3r4n0/astroid
ASTROID v 1.2 bypass most A.V softwares
 davidbuchanan314/monomorph
MD5-Monomorphic Shellcode Packer - all payloads have the same MD5 hash
 l-urk/cve-2024-6387
Proof of concept python script for regreSSHion exploit.
 that-guy-steve/cve-2022-28368-handler
This repository contains a python script that will handle the majority of the dompdf cached font exploit (CVE-2022-28368), all you need to do is…
 alienwithin/owasp-mth3l3m3nt-framework
OWASP Mth3l3m3nt Framework is a penetration testing aiding tool and exploitation framework. It fosters a principle of attack the web using the web as…
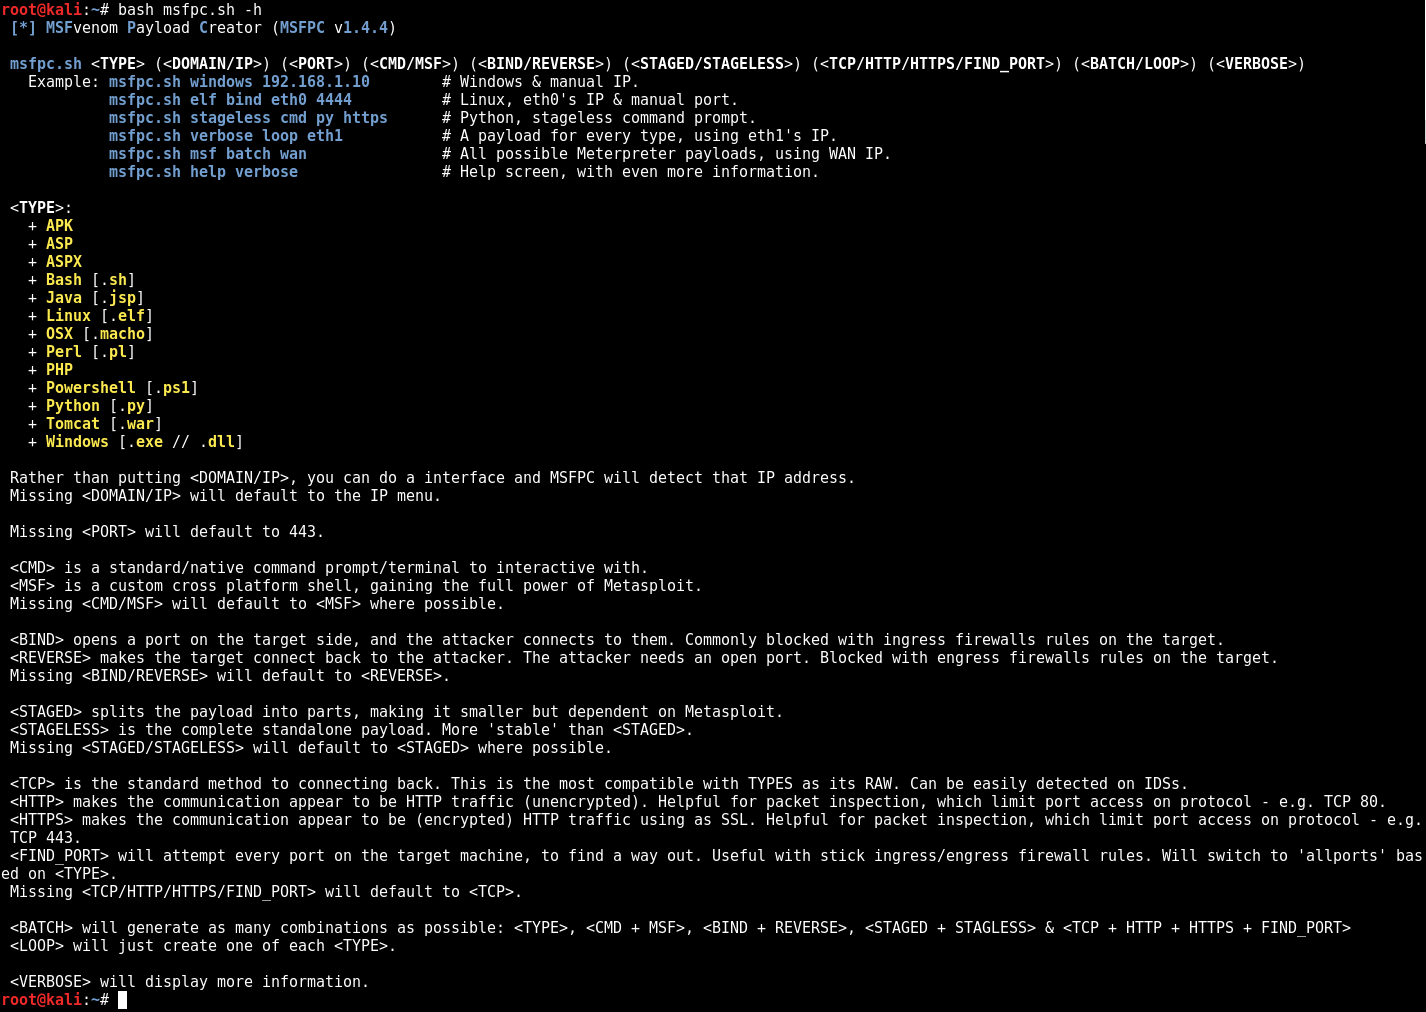 g0tmi1k/msfpc
MSFvenom Payload Creator (MSFPC)
 saerxcit/libtp_gadget
Crystal Palace library for proxying Nt API calls via the Threadpool. Updated for call gadgets.
 getrektboy724/meterpwrshell
Automated Tool That Generates The Perfect Meterpreter Powershell Payload