powershell-backdoor-generator

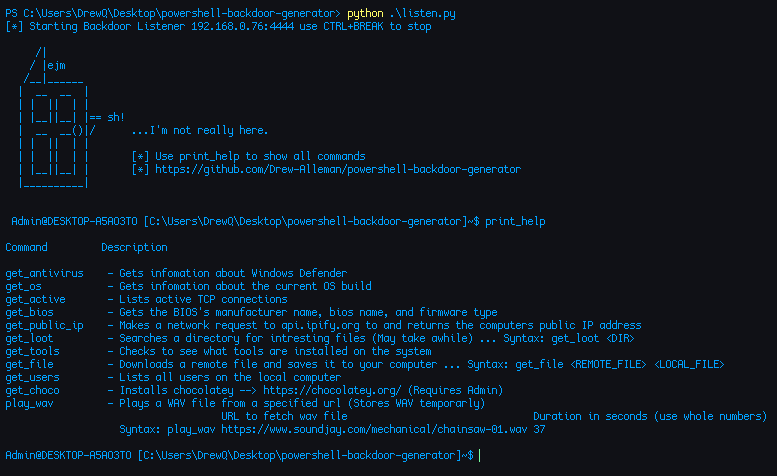
Reverse backdoor written in PowerShell and obfuscated with Python. It generates payloads for popular hacking devices like Flipper Zero and Hak5 USB…

Reverse backdoor written in PowerShell and obfuscated with Python. It generates payloads for popular hacking devices like Flipper Zero and Hak5 USB…


Linux ELF x32/x64 ASLR DEP/NX bypass exploit with stack-spraying

An application to test windows and linux shellcodes

Linux Shared Library to Shellcode Loader

Shellcode Compiler

OWASP ZSC - Shellcode/Obfuscate Code Generator https://www.secologist.com/

Terminator metasploit payload generator

Deploy payloads to *Nix systems en masse

C-shellcode to hex converter, handy tool for paste & execute shellcodes in IDA PRO, gdb, windbg, radare2, ollydbg, x64dbg, immunity debugger & 010…

Open-source exploitation framework with modular payload, encoder, and auxiliary system for penetration testing, vulnerability validation, and…

Adversary Emulation Framework

Multi-architecture assembler framework that converts assembly source into machine code for Arm, x86, MIPS, PowerPC, RISC-V, and more, with a…

Chimera is a PowerShell obfuscation script designed to bypass AMSI and commercial antivirus solutions.

c++ fully undetected shellcode launcher ;)

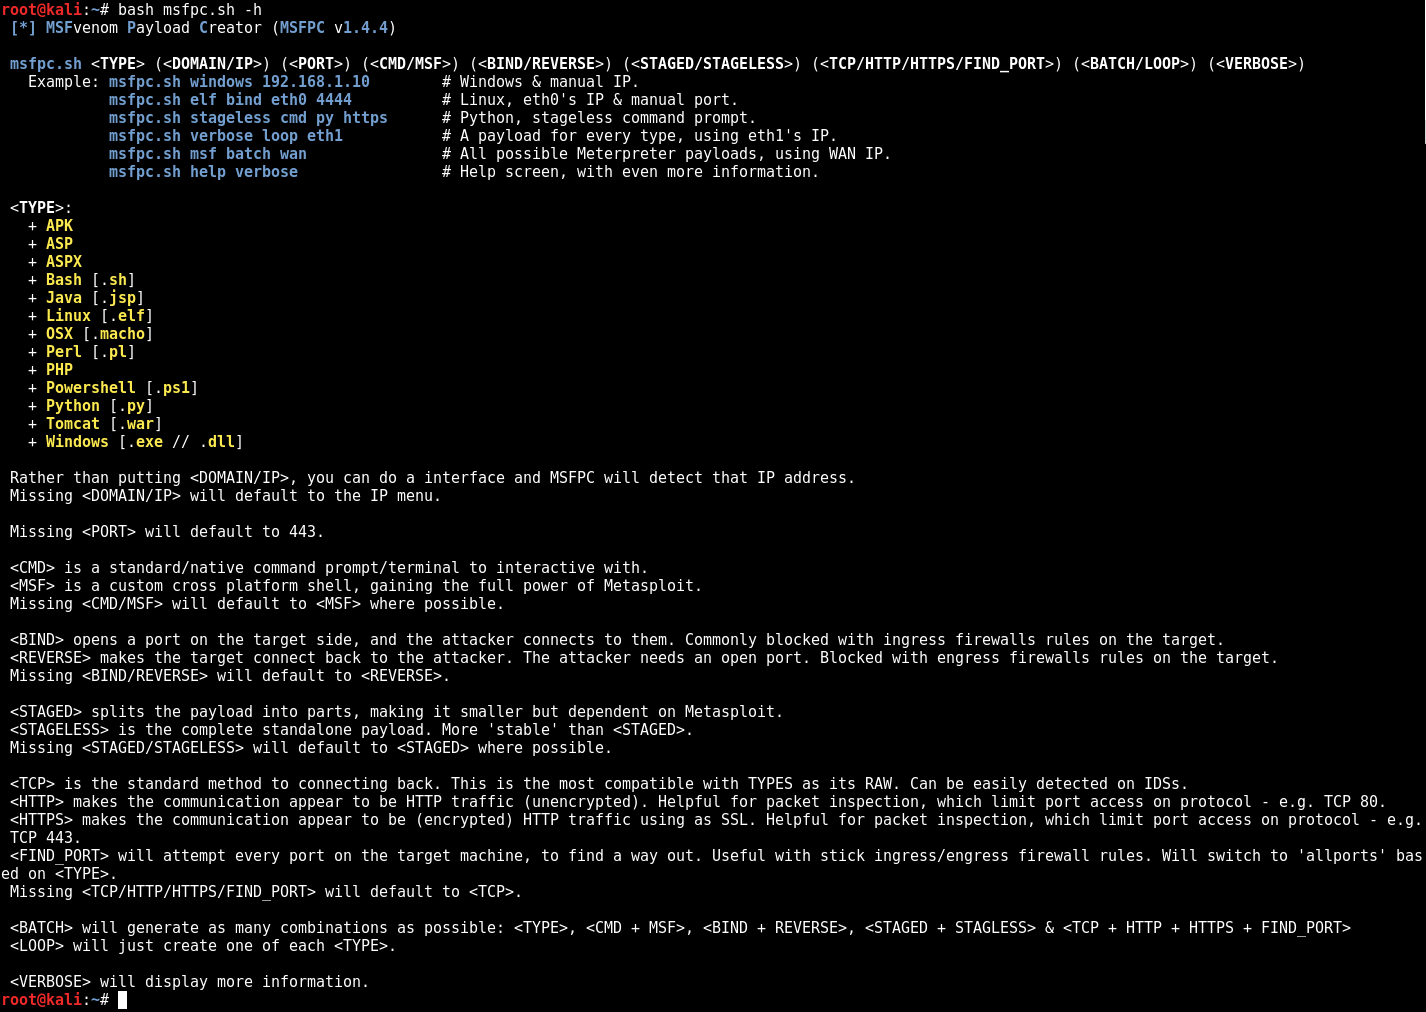
MSFvenom Payload Creator (MSFPC)

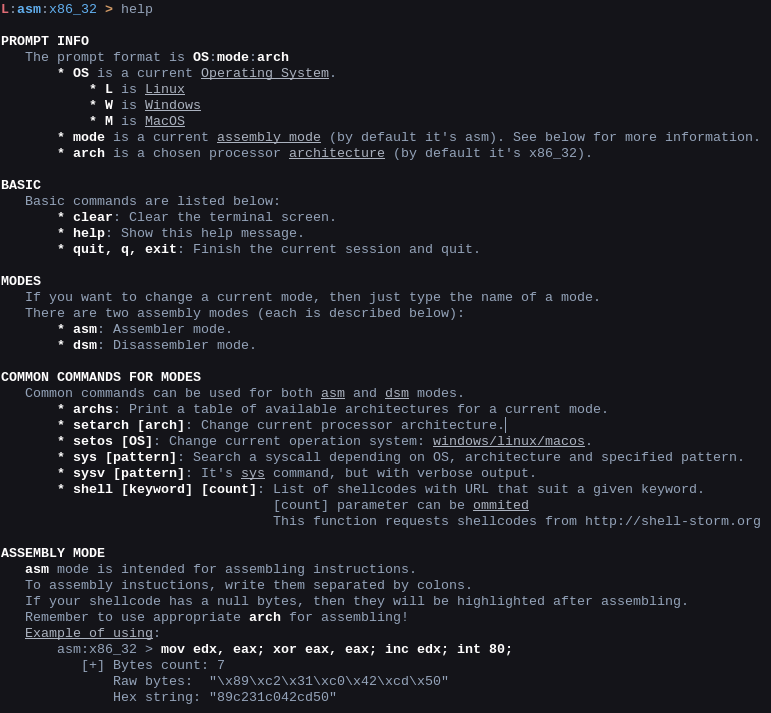
:cherry_blossom: Interactive shellcoding environment to easily craft shellcodes

EXOCET - AV-evading, undetectable, payload delivery tool