

SysWhispers3
 klezvirus/syswhispers3
SysWhispers on Steroids - AV/EDR evasion via direct system calls.
defensive-toolsexploitationids-ips-evasion+5
1.6k2 years ago
klezvirus/syswhispers3SysWhispers on Steroids - AV/EDR evasion via direct system calls.
 saerxcit/libtp_gadget
Crystal Palace library for proxying Nt API calls via the Threadpool. Updated for call gadgets.
 monoxgas/srdi
Shellcode implementation of Reflective DLL Injection. Convert DLLs to position independent shellcode
 thewover/donut
Generates x86, x64, or AMD64+x86 position-independent shellcode that loads .NET Assemblies, PE files, and other Windows payloads from memory and runs…
 cybereason/siofra
Simulates the Windows PE loader to identify DLL hijacking vulnerabilities, generates weaponized DLLs with shellcode payloads, and detects UAC…
 davidbuchanan314/monomorph
MD5-Monomorphic Shellcode Packer - all payloads have the same MD5 hash
 runik/harmonic
Suite for reverse shell handling geared toward working within the native shell
 bishopfox/sliver
Adversary Emulation Framework
 9emin1/charlotte
c++ fully undetected shellcode launcher ;)
 tanc7/exocet-av-evasion
EXOCET - AV-evading, undetectable, payload delivery tool
 0xsha/cve-2026-6307
Google Chrome CVE-2026-6307 PoC
 s0lst1c3/dropengine
DropEngine provides a malleable framework for creating shellcode runners, allowing operators to choose from a selection of components and combine…
 optiv/mangle
Mangle is a tool that manipulates aspects of compiled executables (.exe or DLL) to avoid detection from EDRs
 petitoto/chromium-exploit-dev
Toolkit to weaponize Chromium vulnerabilities into reliable, cross-platform, full-chain exploits
 l-urk/cve-2024-6387
Proof of concept python script for regreSSHion exploit.
 rburrito/payloadgenerator
A wrapper for MSFvenom that allows for easy generation of payloads
 g0tmi1k/msfpc
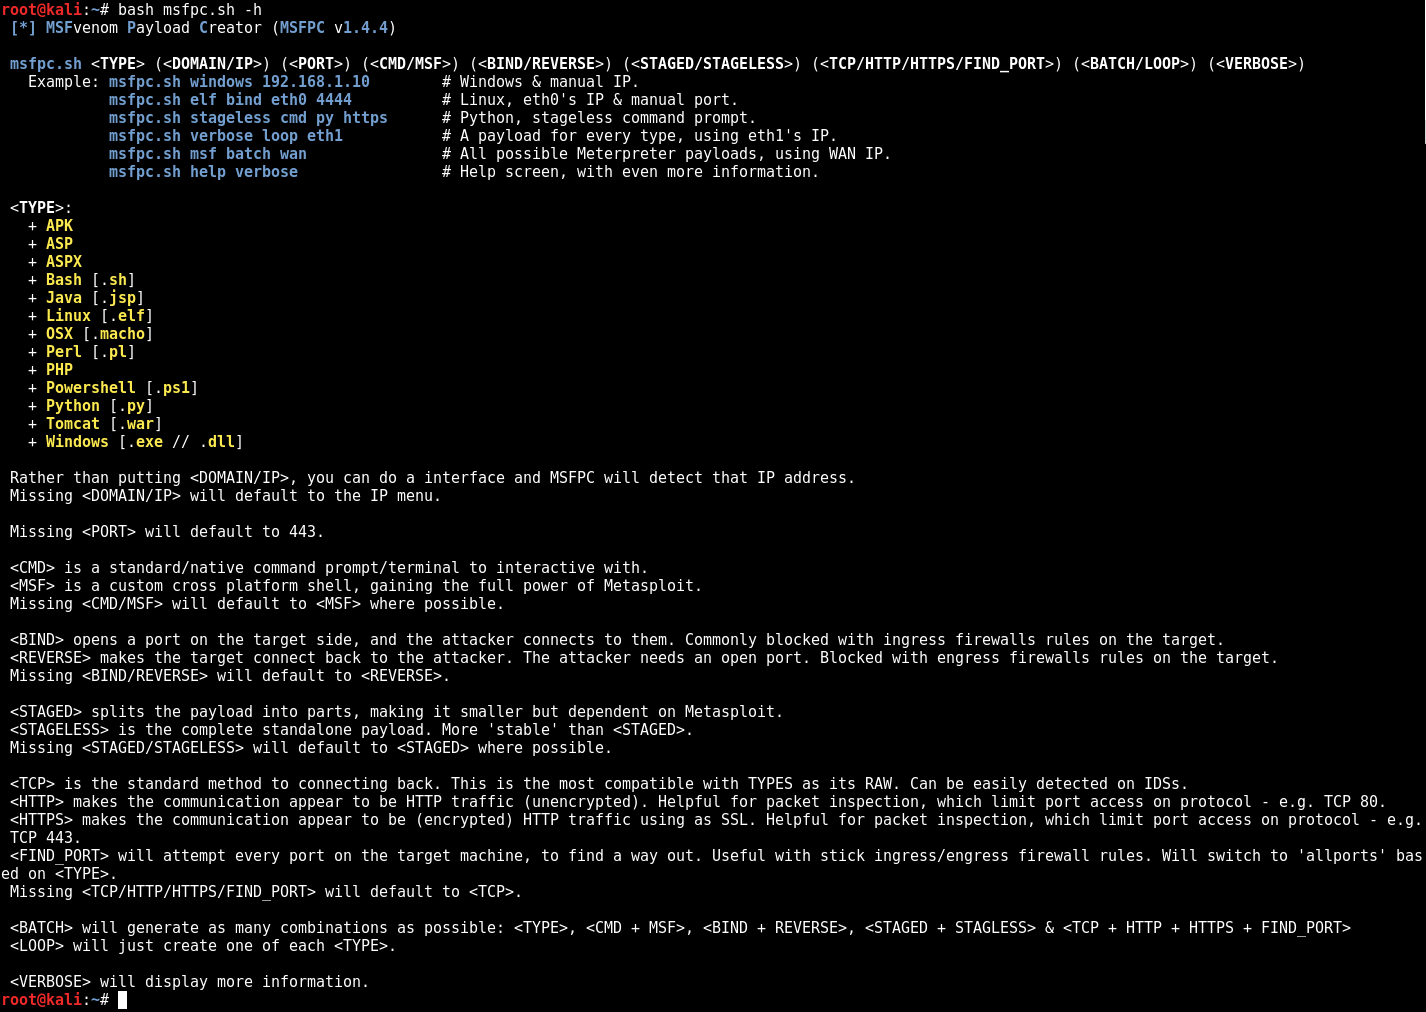
MSFvenom Payload Creator (MSFPC)
 that-guy-steve/cve-2022-28368-handler
This repository contains a python script that will handle the majority of the dompdf cached font exploit (CVE-2022-28368), all you need to do is…