powershell-backdoor-generator

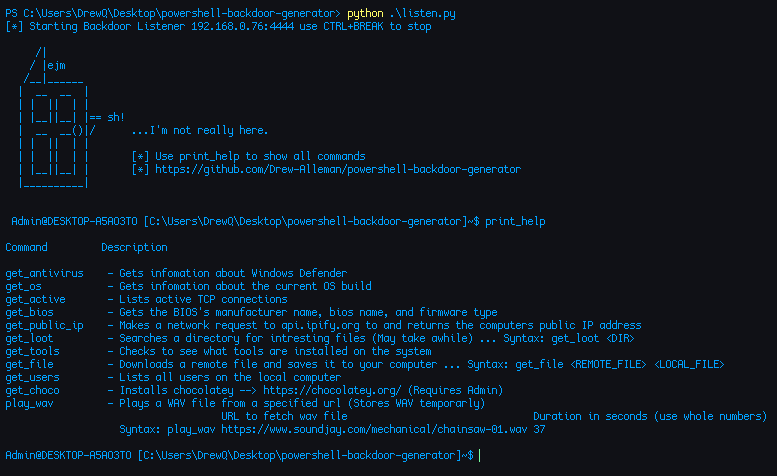
Reverse backdoor written in PowerShell and obfuscated with Python. It generates payloads for popular hacking devices like Flipper Zero and Hak5 USB…

Reverse backdoor written in PowerShell and obfuscated with Python. It generates payloads for popular hacking devices like Flipper Zero and Hak5 USB…

Windows memory hacking library

Previously-0day exploit from the Hacking Team leak, written by Eugene Ching/Qavar.

Undetectable Windows Payload Generation

SSH-based reverse shell management tool with native SCP/SFTP support, multiple transport protocols, Windows DLL generation, and fileless execution…

This is a proof-of-concept Metasploit module exploit for CVE-2015-1578, a buffer overflow vulnerability in Achat 0.150 beta7 on Windows. Exploitation…

Automated Tool That Generates The Perfect Meterpreter Powershell Payload

An efficent Script To Generate FUD Persistent Reverse Shell For Red Teaming. Don't Upload Generated Stub On Virustotal

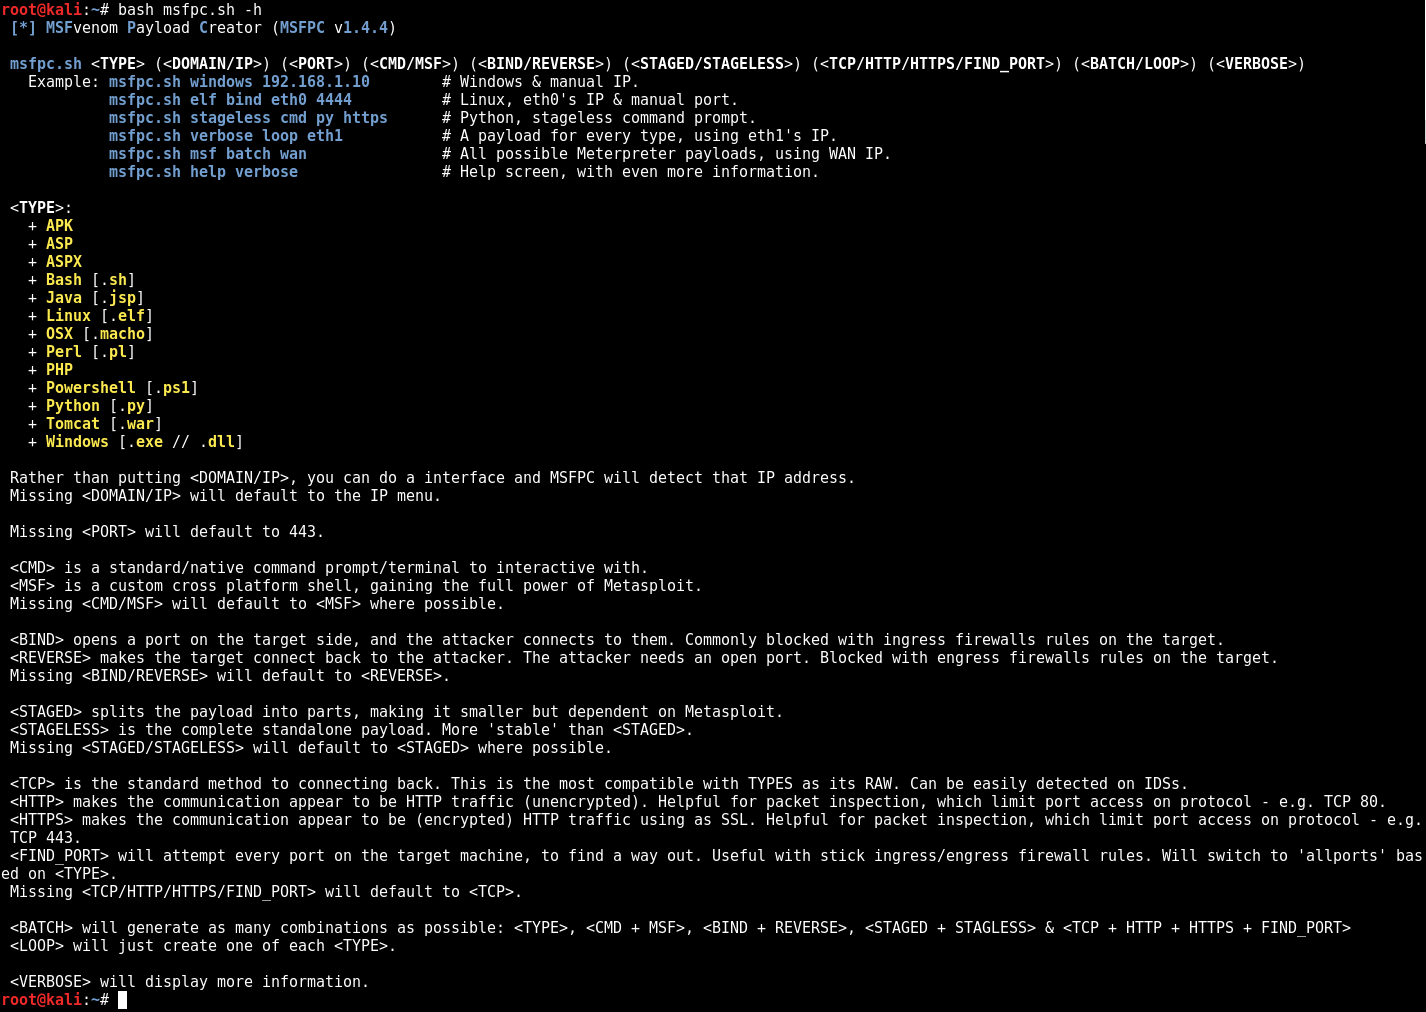
MSFvenom Payload Creator (MSFPC)

Cross-platform C2 agent for Mythic with dynamic function loading, SOCKS5 proxy, file operations, shellcode injection, and macOS/Windows…


WasmForge — compile Go and C# programs to single-binary, WASM-sandboxed native executables with polymorphic output.

Crystal Palace Evasion kit for Sliver

Python exploit for Serv-U SSH vulnerability (CVE-2021-35211) with multiple payload modes: stage, exec, and download-execute, enabling shellcode…

A wrapper for MSFvenom that allows for easy generation of payloads

Freeze is a payload toolkit for bypassing EDRs using suspended processes, direct syscalls, and alternative execution methods

Veil 3.1.X (Check version info in Veil at runtime)

Veil Evasion is no longer supported, use Veil 3.0!