
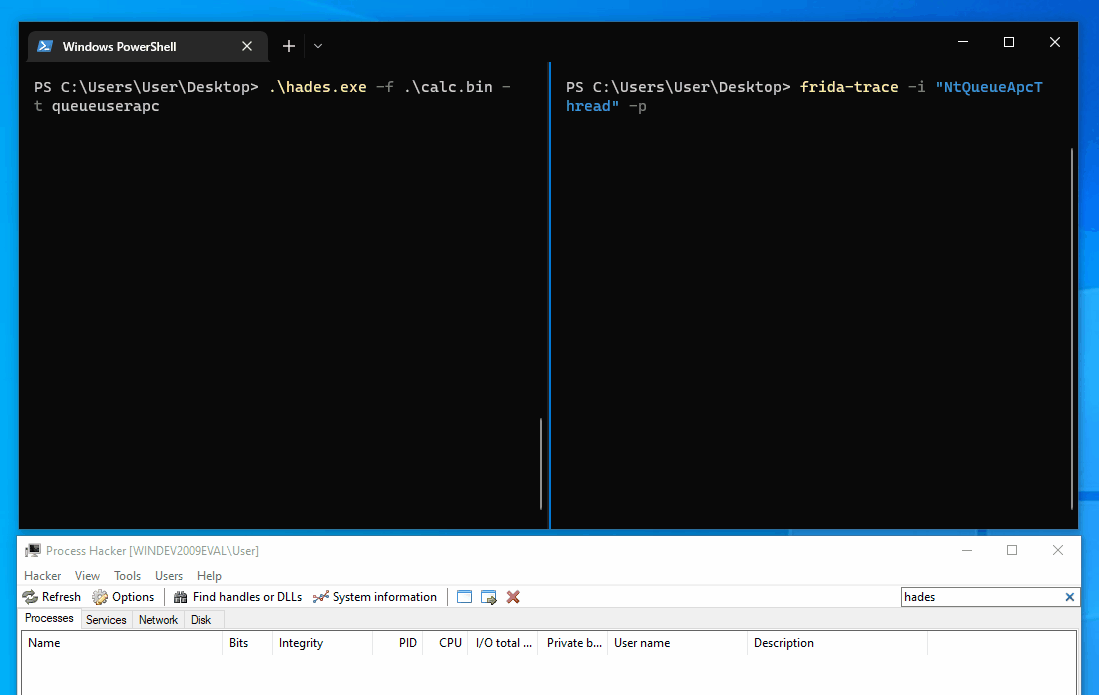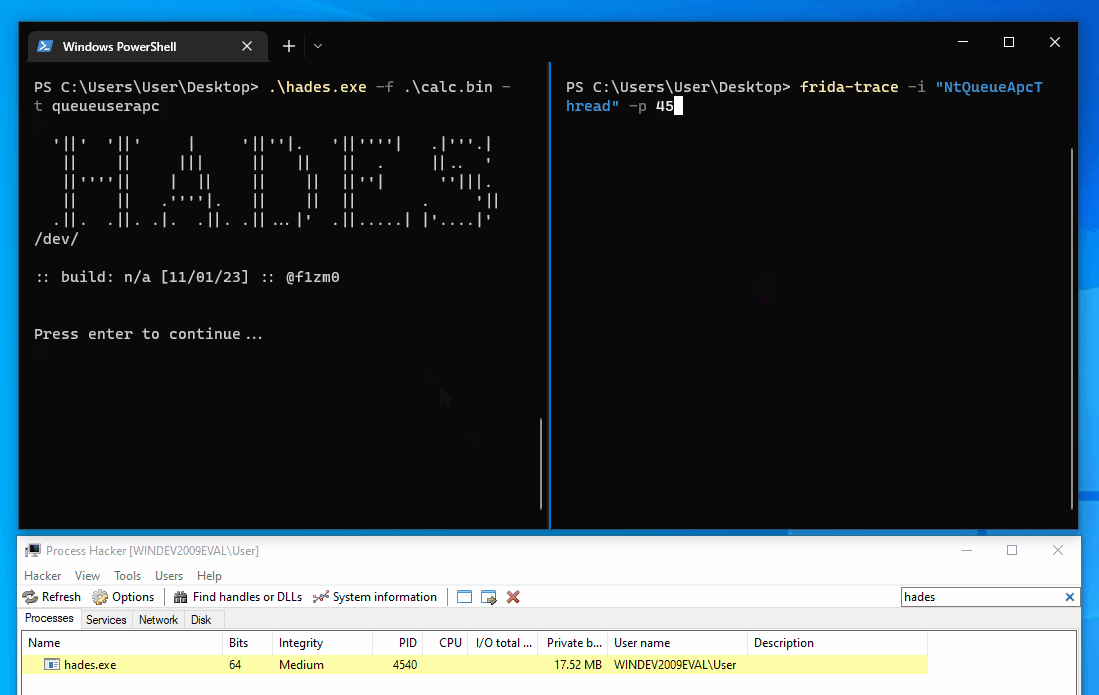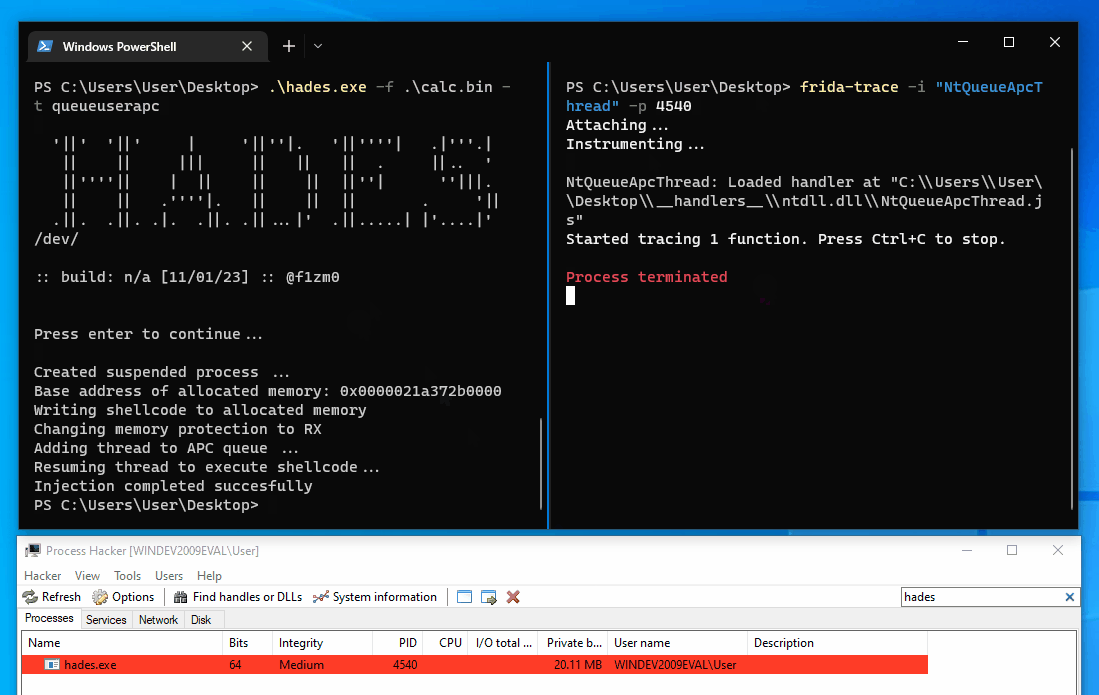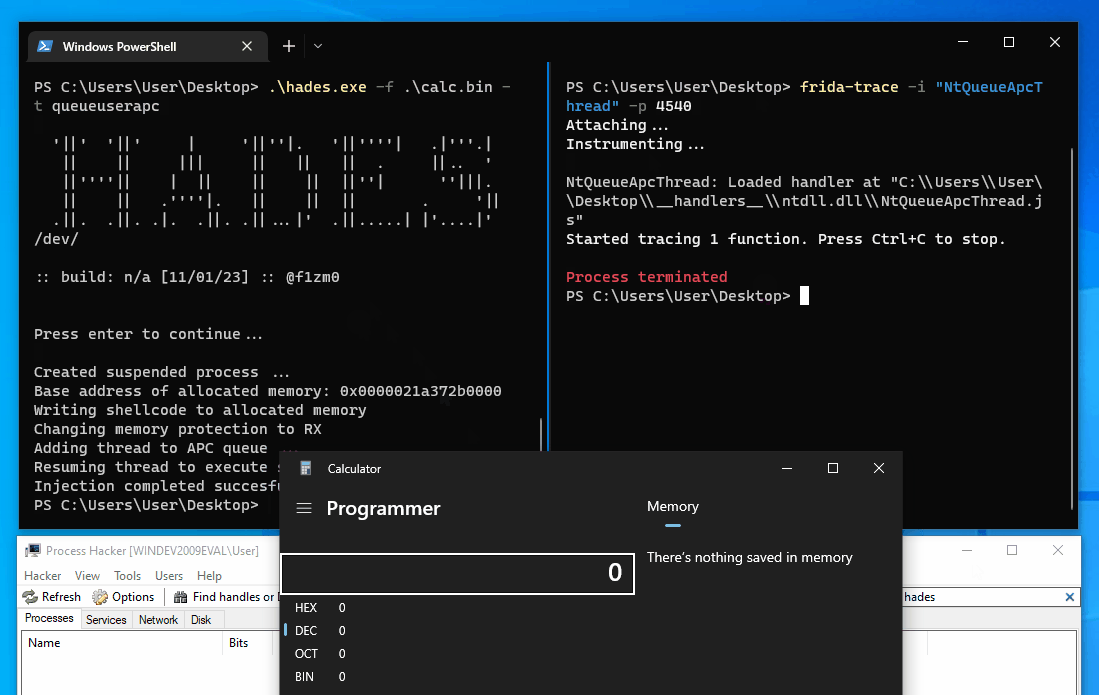
hades
 f1zm0/hades
Go shellcode loader that combines multiple evasion techniques
ids-ips-evasionshellcodeshellcode-generation
f1zm0/hadesGo shellcode loader that combines multiple evasion techniques
 d3lb3/keefarcereborn
A standalone DLL that exports databases in cleartext once injected in the KeePass process.
 connormcgarr/littlecorporal
LittleCorporal: A C# Automated Maldoc Generator
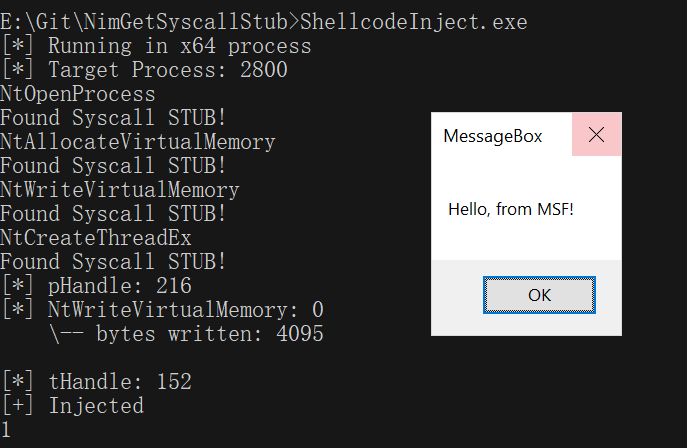 s3cur3th1ssh1t/nimgetsyscallstub
Dynamically extracts fresh syscall stubs from ntdll.dll to evade signature-based detection, with a shellcode execution template for Nim-based…
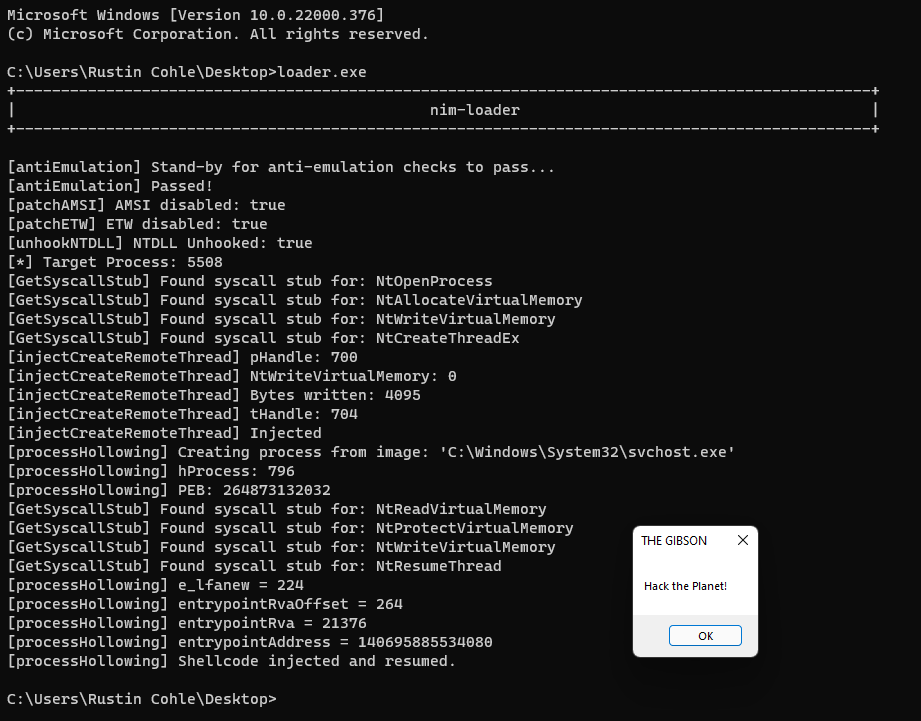 adamsvoboda/nim-loader
WIP shellcode loader in nim with EDR evasion techniques
 winterknife/silverpick
Windows User-Mode Shellcode Development Framework (WUMSDF)
 blacknbunny/mcreator
Encoded Reverse Shell Generator With Techniques To Bypass AV's
 ohjeongwook/shellcodeemulator
Shellcode emulator written with Unicorn Framework With Process Dump Emulation Environment
 hasherezade/masm_shc
A helper utility for creating shellcodes. Cleans MASM file generated by MSVC, gives refactoring hints.
 devploit/put2win
Script to automate PUT HTTP method exploitation to get shell
 machine1337/fudshell
An efficent Script To Generate FUD Persistent Reverse Shell For Red Teaming. Don't Upload Generated Stub On Virustotal
 watchtowrlabs/watchtowr-vs-citrix-netscaler-preauth-rce-cve-2026-8452
CVE-2026-8452 PreAuth RCE
 kasturixbm5/staged-dll-injection-smb-
Staged DLL injection proof-of-concept built in C using Win32 APIs — developed in an isolated lab environment for red team certification study (CRTO).
 elweth-sec/cve-2023-2255
CVE-2023-2255 Libre Office
 mahmoudimus/static_asm
Header-only C++2x compile-time assembler for x86/x86-64 instruction encoding
 saerxcit/libtp_gadget
Crystal Palace library for proxying Nt API calls via the Threadpool. Updated for call gadgets.